
Nmap-API
 morpheuslord/nmap-api
RESTful API wrapping Nmap for automated network scanning, port detection, service enumeration, and vulnerability analysis with optional AI-powered…
api-security-testingnetwork-mappingosint+2
morpheuslord/nmap-apiRESTful API wrapping Nmap for automated network scanning, port detection, service enumeration, and vulnerability analysis with optional AI-powered…
 elevenpaths/siemframework
Modular Python3 attack framework for automating exploitation of SIEM platforms (Splunk, Graylog, OSSIM, QRadar, McAfee) via credential theft, payload…
 an00brektn/gopher47
A third-party Gopher Assassin for the Havoc Framework.
 zcyberseclab/zscan
A fast, customizable service detection tool powered by a flexible fingerprint system. It helps you identify services, APIs, and network…
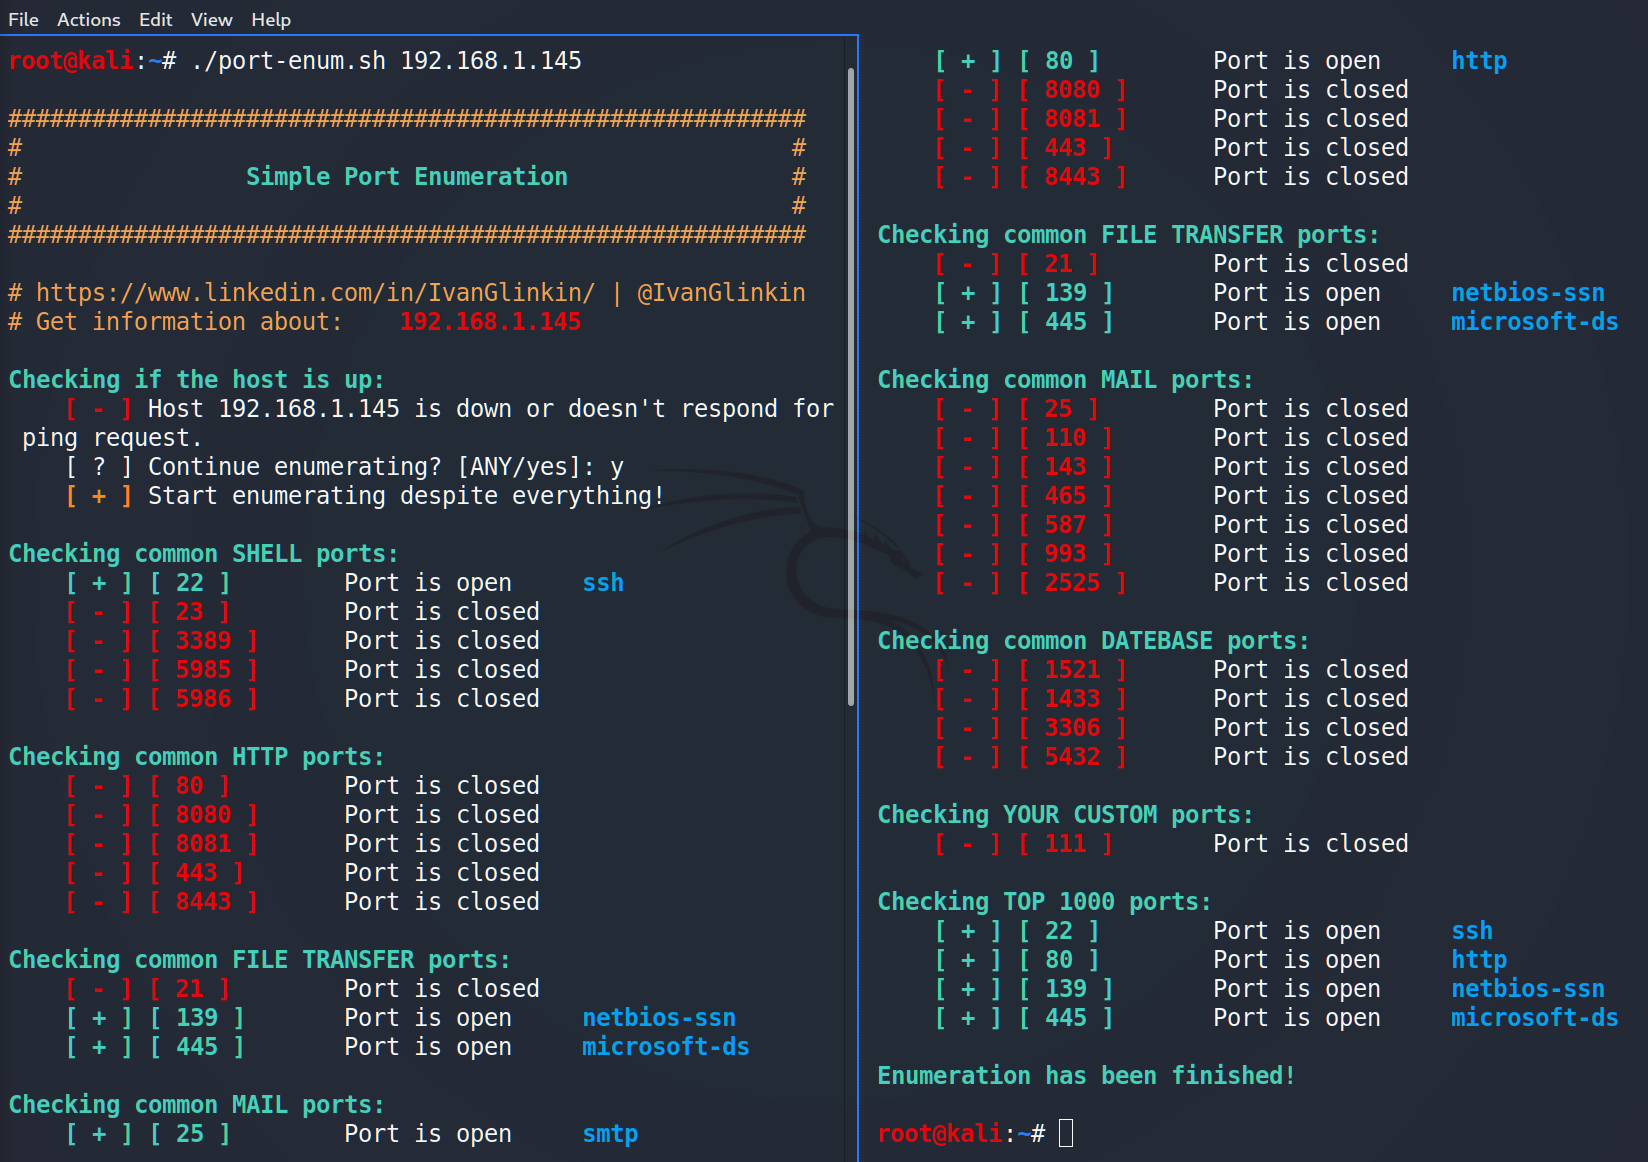 ivanglinkin/port-enumeration
Have you ever faced with the lack of possibility of using NMap? For instance if you have reverse shell as an unprivileged user and there are no…
 thegenetic/cve-2024-6387-exploit
CVE-2024-6387 exploit
 samh4cks/cve-2023-27163-internalprober
A tool to perform port scanning using vulnerable Request-Baskets
 baimaobg/sunflower_exp
Sunflower CVE-2022-10270 vulnerability exploitation tool
 bitplugg/kitsune
🦊 nine-tailed pentest framework — nmap + msf + aircrack + sqlmap в одном CLI · 25 модулей · SQLite-сессия · TUI · REST API · pipx install
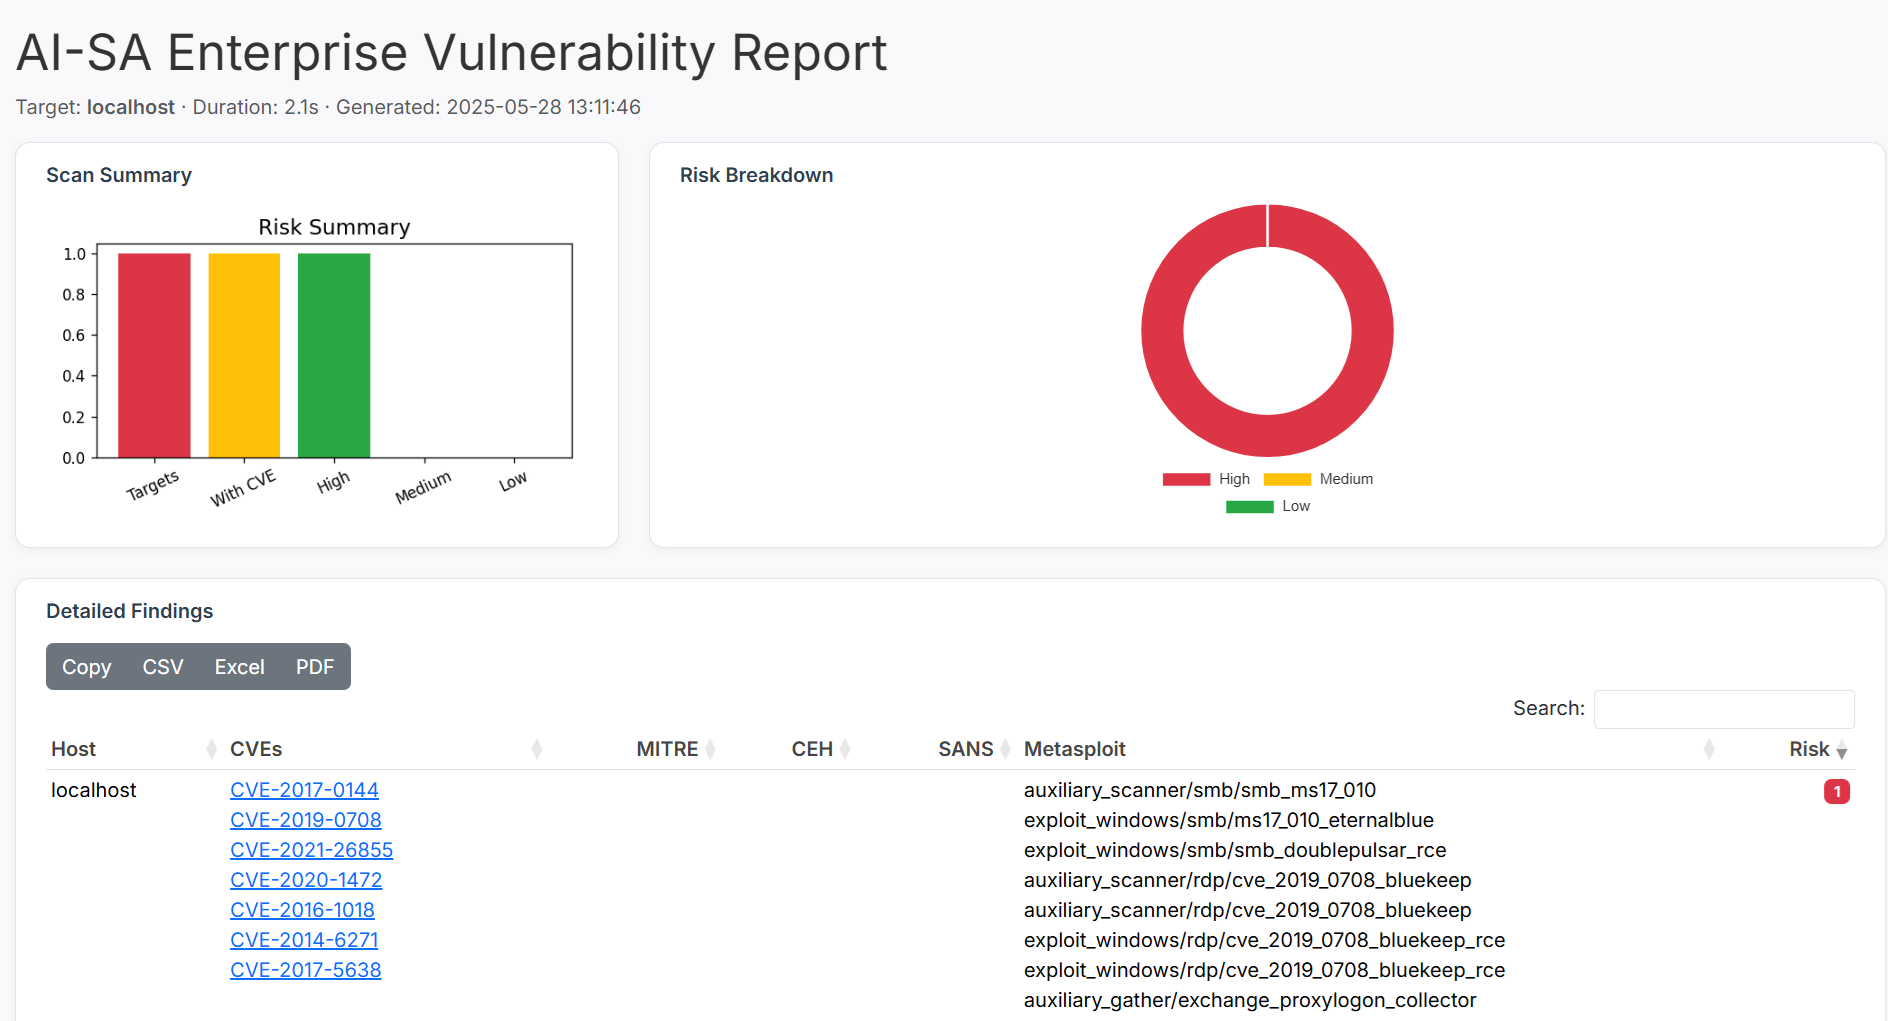 gmh5225/aisa-scanner
AISA-Scanner is an AI-powered autonomous vulnerability scanner that maps CVEs to metasploit exploits, MITRE, CEH, and SANS, delivering intelligent,…
 achux21/checker-cve-2024-6387
Python scanner that checks hosts for the OpenSSH regreSSHion vulnerability (CVE-2024-6387)
 udpsycho/moodle-cve-2018-1042
Script to exploit CVE-2018-1042 in order to do internal port scans.
 rek2/goenumerator
A personal tool in GO for my usual first enumeration steps on a target
 cyberdudebivash/cyberdudebivash-fortisiem-cve-2025-64155-scanner
Authorized high-impact tool from CYBERDUDEBIVASH ECOSYSTEM to detect CVE-2025-64155 (FortiSIEM phMonitor Command Injection). Scans for open ports and…
 j0ey17/exploit_cve-2023-27163
Proof of Concept exploit for Server Side Request Forgery vulnerability in Requests Basket v1.2.1 and before.
 reanimat0r/bpnd-libssh
Multi-threaded, reliable scanner for CVE-2018-10933.
 rishabh-kumar-cyber-sec/cve-2023-27163-ssrf-to-port-scanning
It is a simple script to automate internal port scanning dueto SSRF in requests-baskets v 1.2.1. this script can also assisst in solving 'SAU'…
 mttaggart/offensivenotion
Notion as a platform for offensive operations