
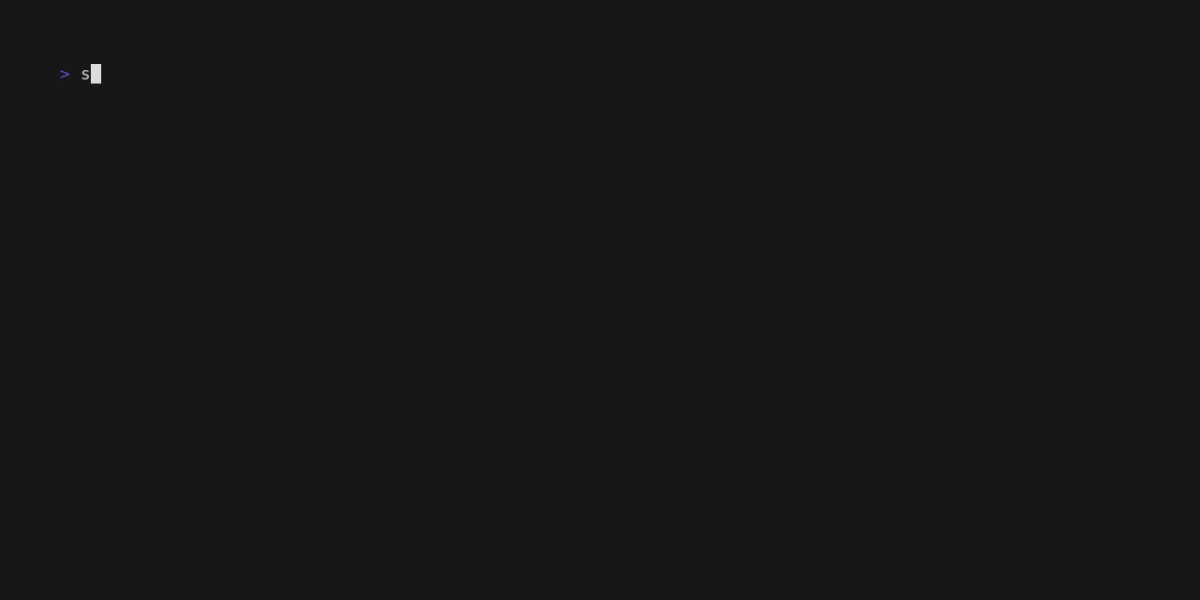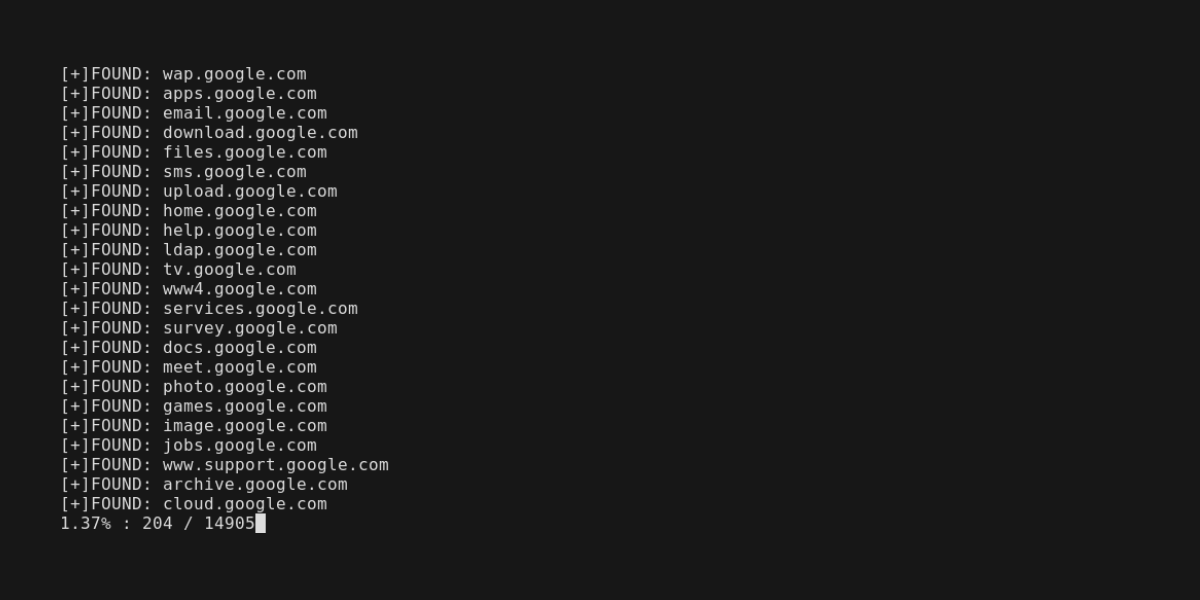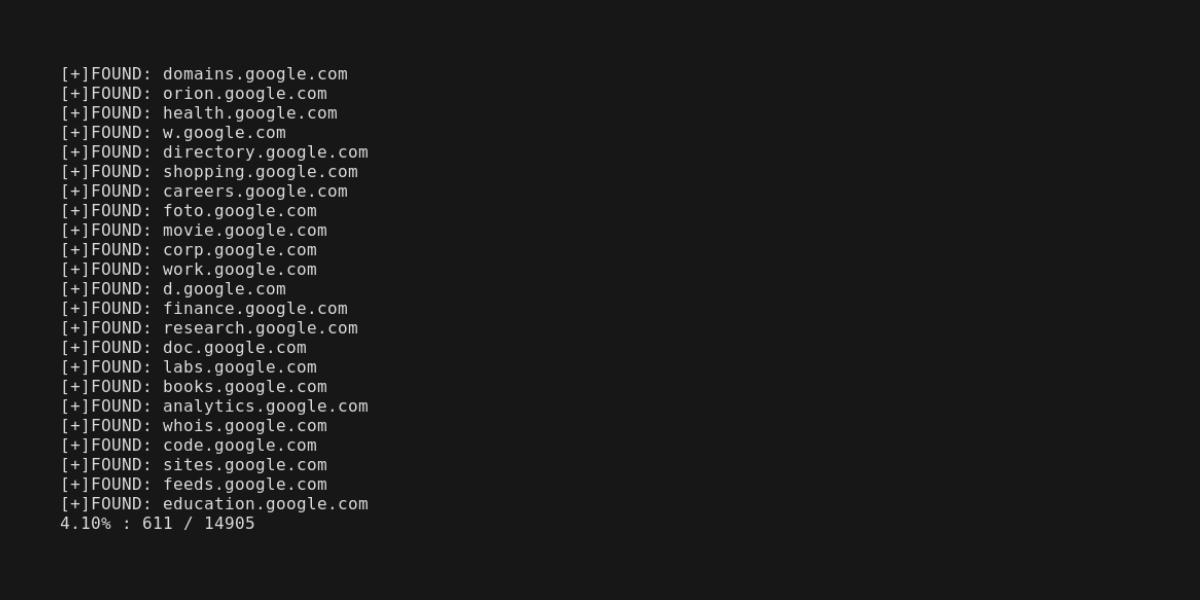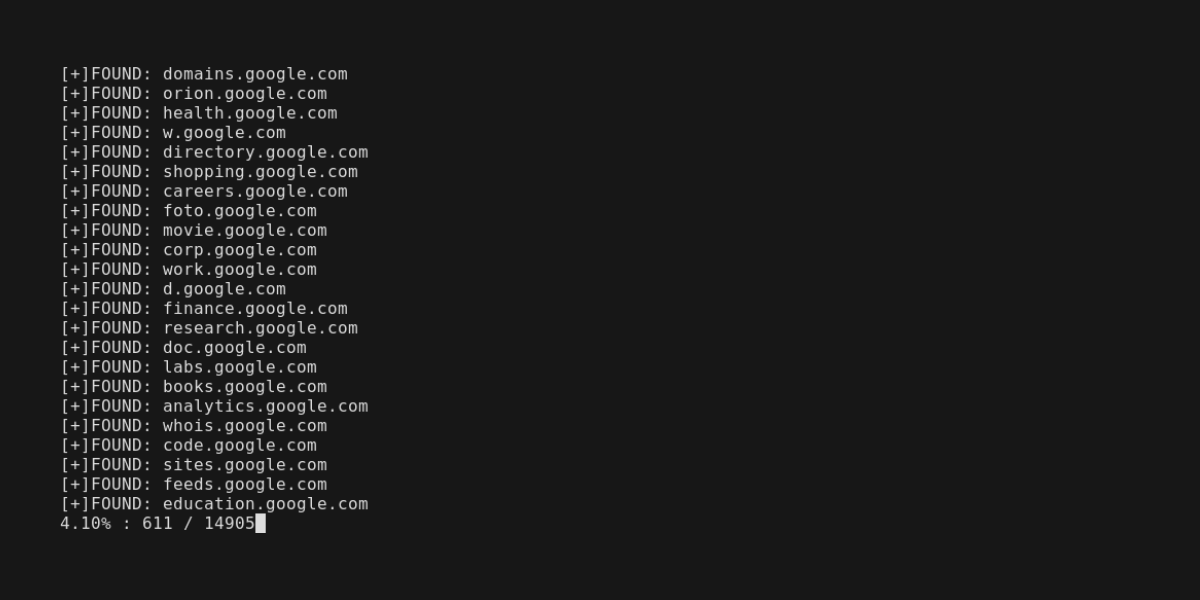
scilla
 edoardottt/scilla
Information Gathering tool - DNS / Subdomains / Ports / Directories enumeration
dns-analysisdns-subdomain-enumerationinformation-gathering+4
1.3k6 days ago
edoardottt/scillaInformation Gathering tool - DNS / Subdomains / Ports / Directories enumeration

 v-byte-cpu/sx
:vulcan_salute: Fast, modern, easy-to-use network scanner
 solomonsklash/chomp-scan
A scripted pipeline of tools to streamline the bug bounty/penetration test reconnaissance phase, so you can focus on chomping bugs.
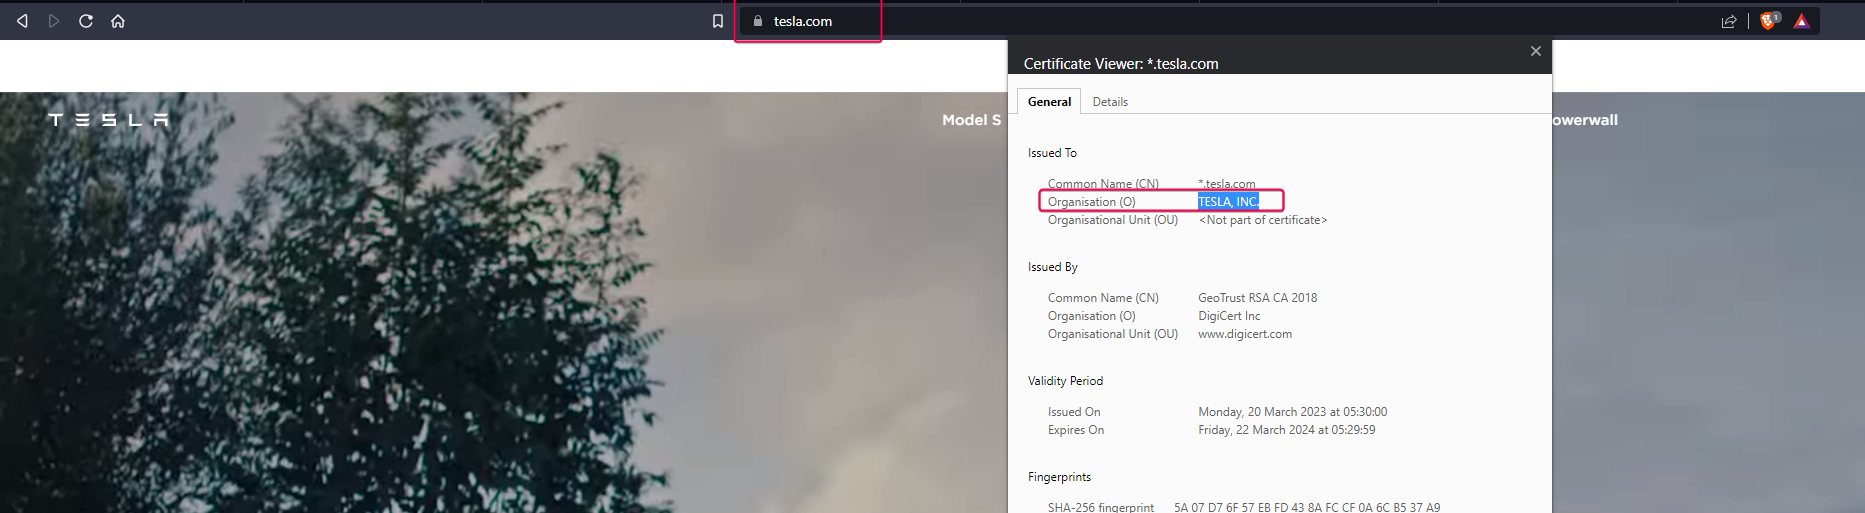 mr-rizwan-syed/chomtesh
CHOMTE.SH is a powerful shell script designed to automate reconnaissance tasks during penetration testing. It utilizes various Go-based tools to…
 offxec/pavelow
PAVELOW Exploit Toolbox is a BASH script that corresponds with your KALI distro to better help your vulnerability hunting and exploiting proccess…
 zcyberseclab/zscan
A fast, customizable service detection tool powered by a flexible fingerprint system. It helps you identify services, APIs, and network…
 yukselberkay/asnap
Automates reconnaissance by mapping IPv4/IPv6 addresses to organizations using GeoLite2 databases, with integrated nmap port scanning and batch…
 znakar/sharktooth
Port Scanner with Docker & Prometheus + Grafana integration. A tool for network auditing with multithreading support and real-time monitoring.
 c00ln3t/log4shellauditor
An autonomous reflective Go agent for full-cycle security auditing, WAF evasion, OOB LDAP verification, self-remediation (auto-patching), and…

 netbox-community/netbox
Open-source IPAM and DCIM platform providing a centralized source of truth for modeling, documenting, and automating network infrastructure with…
 ghosttroops/scan4all
Official repository vuls Scan: 15000+PoCs; 23 kinds of application password crack; 7000+Web fingerprints; 146 protocols and 90000+ rules Port…
 milesrichardson/docker-onion-nmap
Scan .onion hidden services with nmap using Tor, proxychains and dnsmasq in a minimal alpine Docker container.
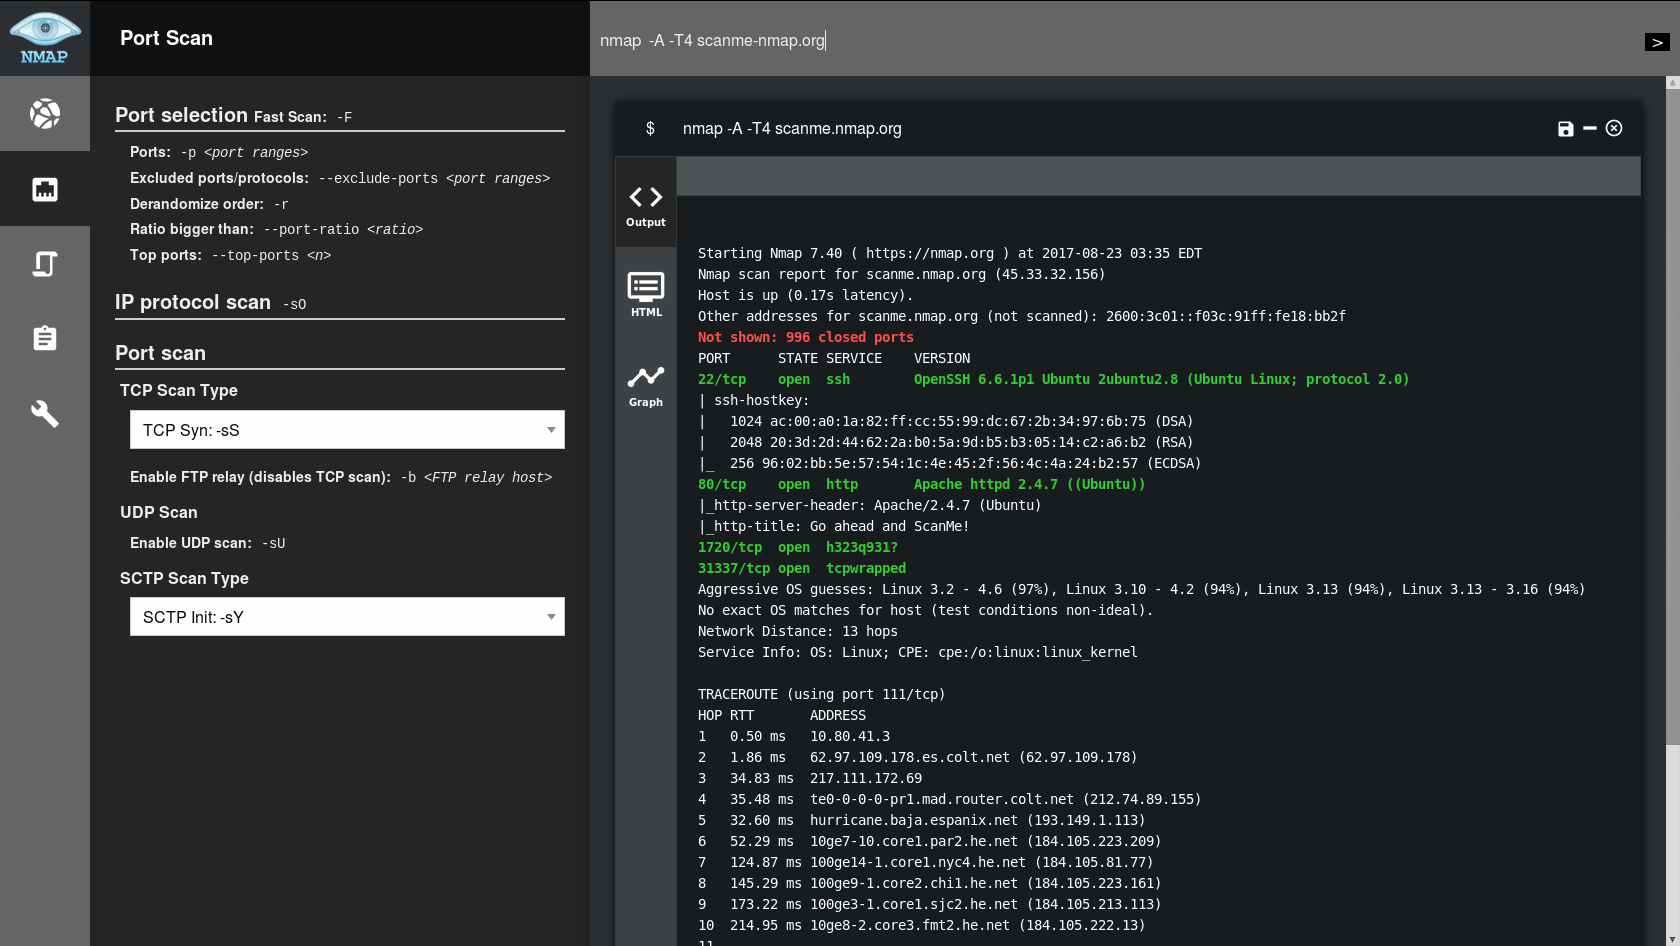 daniel-cues/nmapgui
Advanced Graphical User Interface for NMap
 dmontgomery40/pentest-mcp
NOT for educational purposes: An MCP server for professional penetration testers including STDIO/HTTP/SSE support, nmap, go/dirbuster, nikto, JtR,…
 skr0x1c0/blind-ssrf-cve-2020-15002
https://hackerone.com/reports/865652
 vavkamil/awesome-bugbounty-tools
Curated directory of bug bounty tools organized by category: reconnaissance, subdomain enumeration, port scanning, content discovery, exploitation,…