

 gwen001/pentest-tools
A collection of custom security tools for quick needs.
 ntop/ntopng
Web-based Traffic and Cybersecurity Network Traffic Monitoring
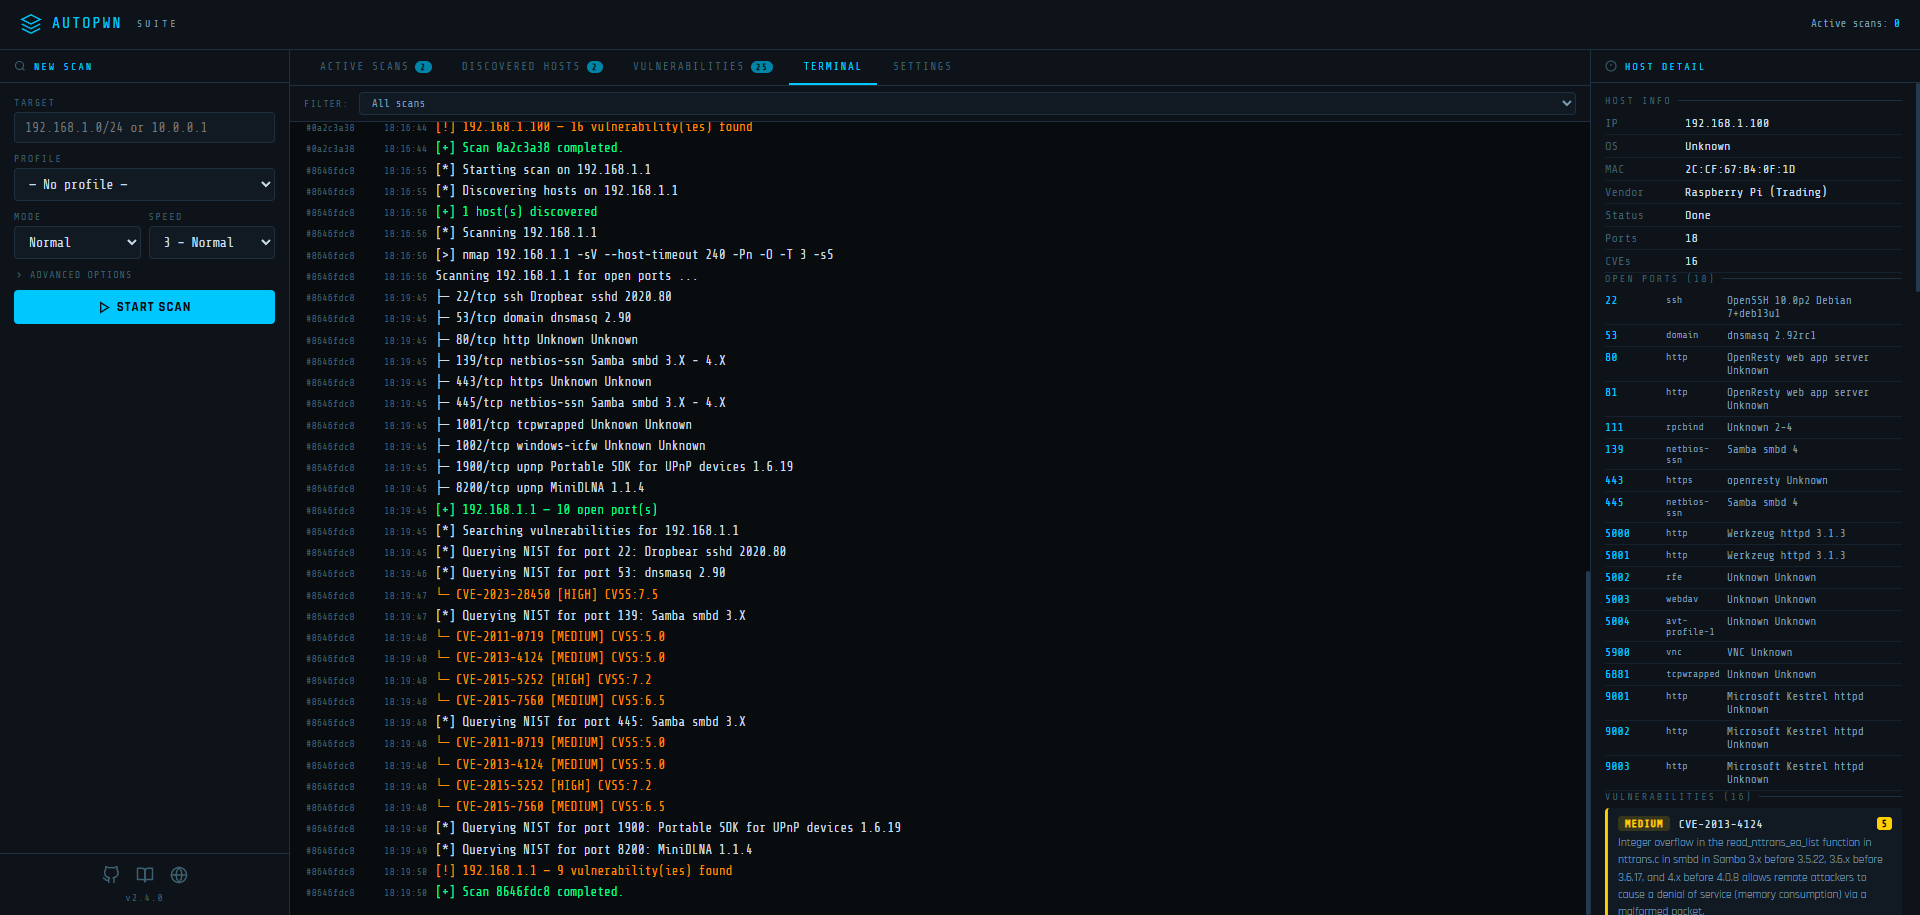 gamehunterkaan/autopwn-suite
AutoPWN Suite is a project for scanning vulnerabilities and exploiting systems automatically.
 vavkamil/awesome-bugbounty-tools
Curated directory of bug bounty tools organized by category: reconnaissance, subdomain enumeration, port scanning, content discovery, exploitation,…
 robertdavidgraham/masscan
TCP port scanner, spews SYN packets asynchronously, scanning entire Internet in under 5 minutes.
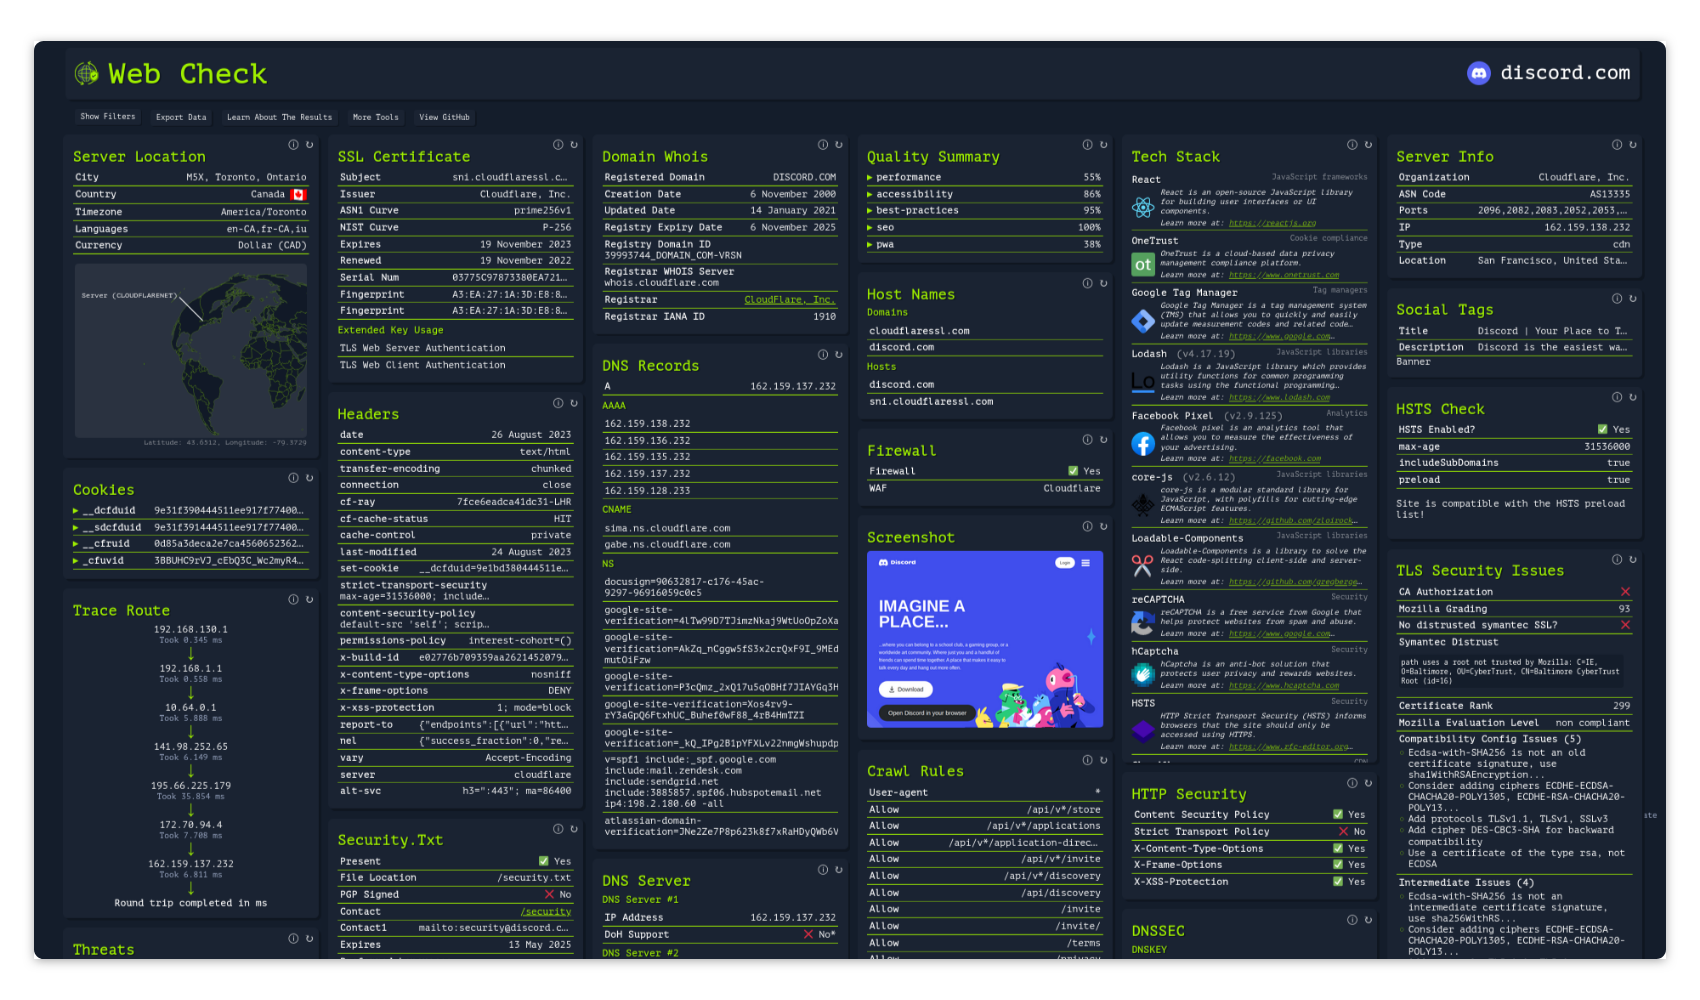 lissy93/web-check
🕵️♂️ All-in-one OSINT tool for analysing any website

 vqkro/ultrasploiter
A single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…
 nmap/nmap
High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
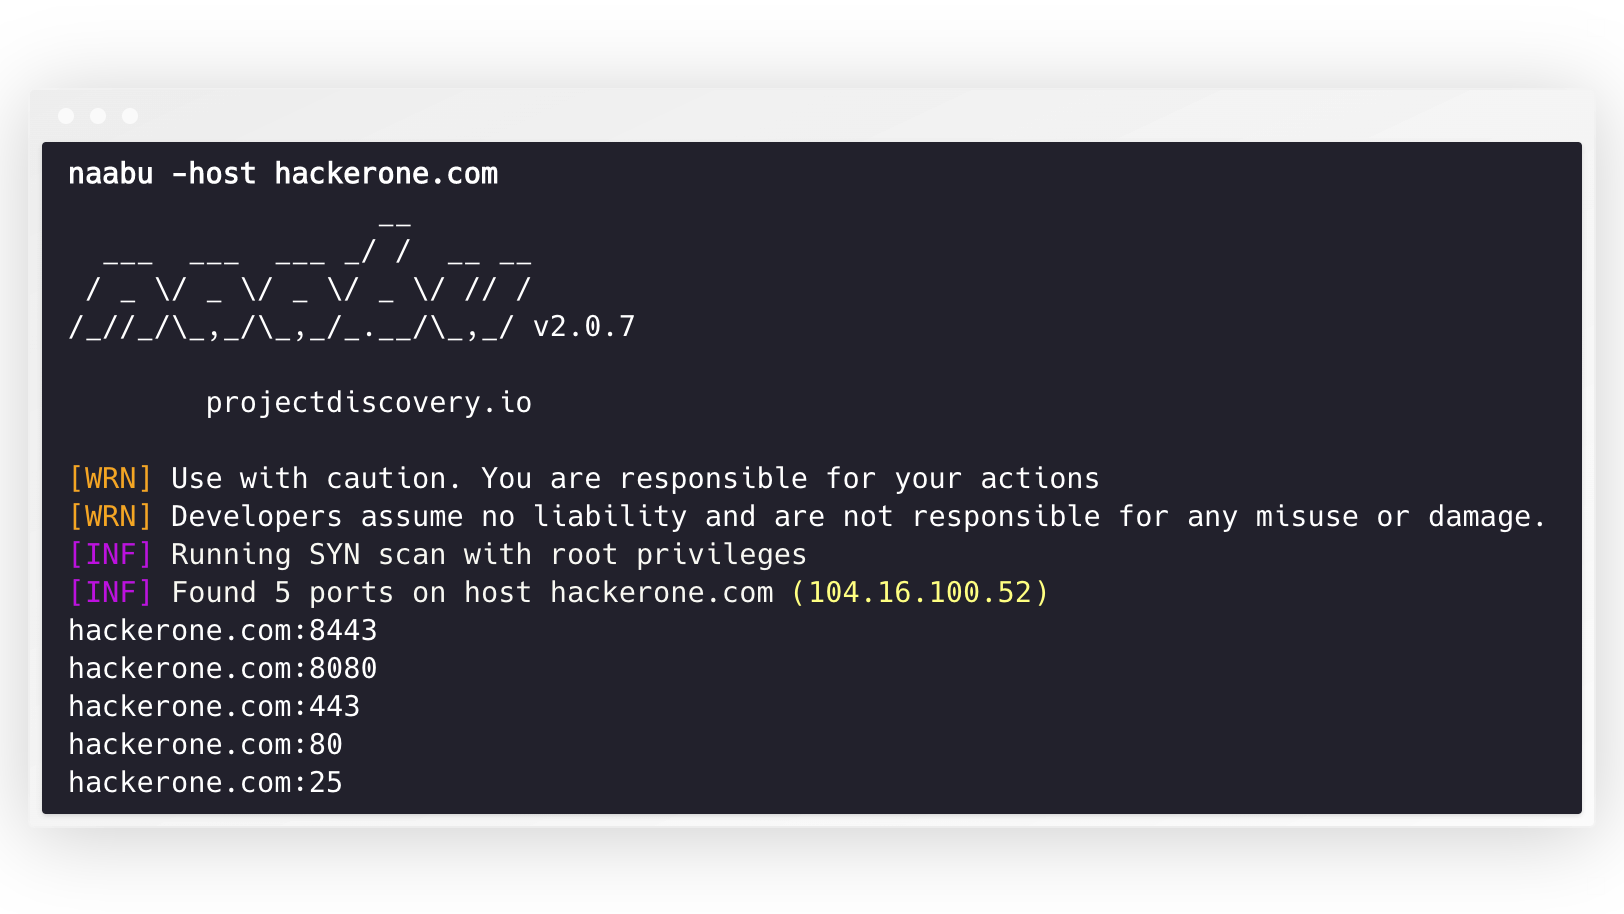 projectdiscovery/naabu
A fast port scanner written in go with a focus on reliability and simplicity. Designed to be used in combination with other tools for attack surface…
 darkrx1/rxscan
Rust CLI for bounded network reconnaissance: TCP/UDP port discovery, service identification, DNS/TLS/HTTP evidence collection, and public-source…
 simplifaisoul/osiris
Open Source Global Intelligence Platform - Real-Time OSINT Dashboard - A Palantir Alternative - …
 praetorian-inc/nerva
Fast service fingerprinting CLI for 170+ protocols (TCP/UDP/SCTP) - built by Praetorian
 vqkro/higernes
a passive OSINT toolkit in python usernames, emails, domains, ips, phones, hashes. no keys, no logins.
 jankoboy88/higernes
a passive OSINT toolkit in python - usernames, emails, domains, ips, phones, hashes. no keys, no logins.
 karim852/kumo-domain-recon-tool
Domain OSINT and security reconnaissance framework running 26 parallel modules for DNS, ports, subdomains, leaked credentials, exposed endpoints,…
 ankhcorp/nuke.sh
Bash-based passive reconnaissance + attack surface mapping script using only public APIs + stock Linux tools (curl, dig, openssl, nmap, python3).