
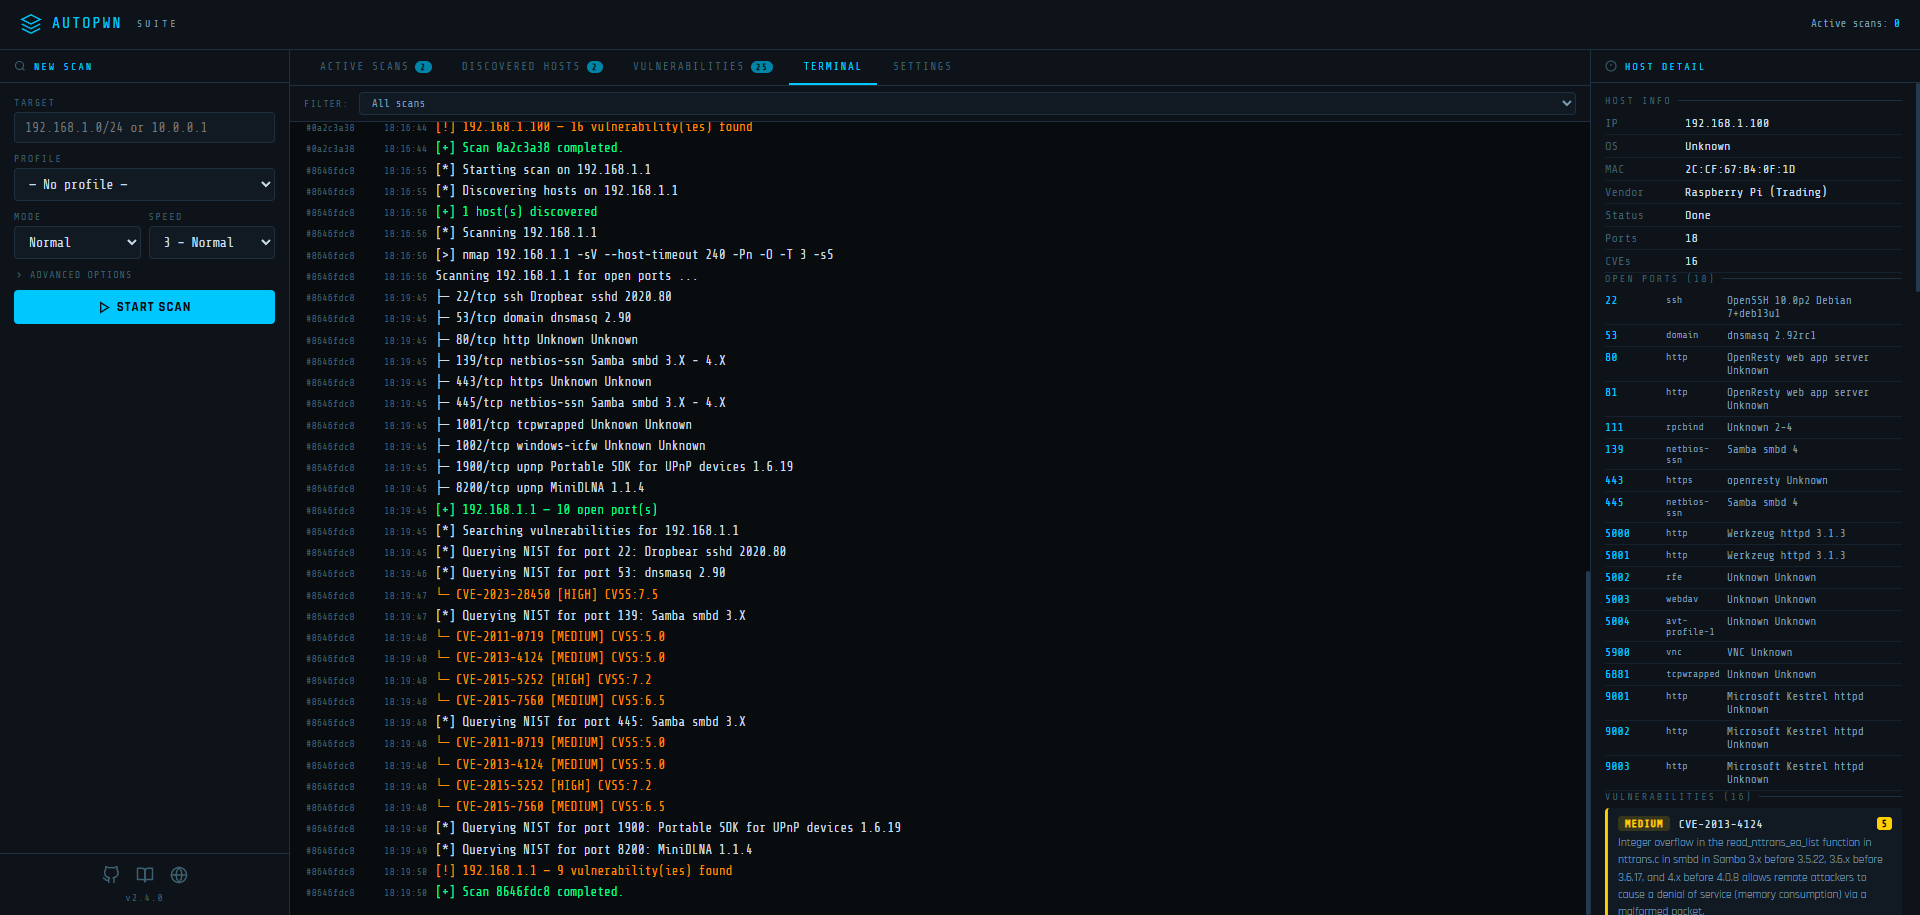
AutoPWN-Suite
 gamehunterkaan/autopwn-suite
AutoPWN Suite is a project for scanning vulnerabilities and exploiting systems automatically.
exploitationinformation-gatheringnetwork-security+5
1.1k
gamehunterkaan/autopwn-suiteAutoPWN Suite is a project for scanning vulnerabilities and exploiting systems automatically.

 vqkro/ultrasploiter
A single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…
 edu4rdshl/unimap
Scan only once by IP address and reduce scan times with Nmap for large amounts of data.
 angryip/ipscan
Angry IP Scanner - fast and friendly network scanner
 irsaattiquecyber/systemvulnerabilitychecklist_project4_decodelabs
System Vulnerability Checklist & Network Security Hardening project featuring reconnaissance, vsFTPd backdoor analysis (CVE-2011-2523), and active…
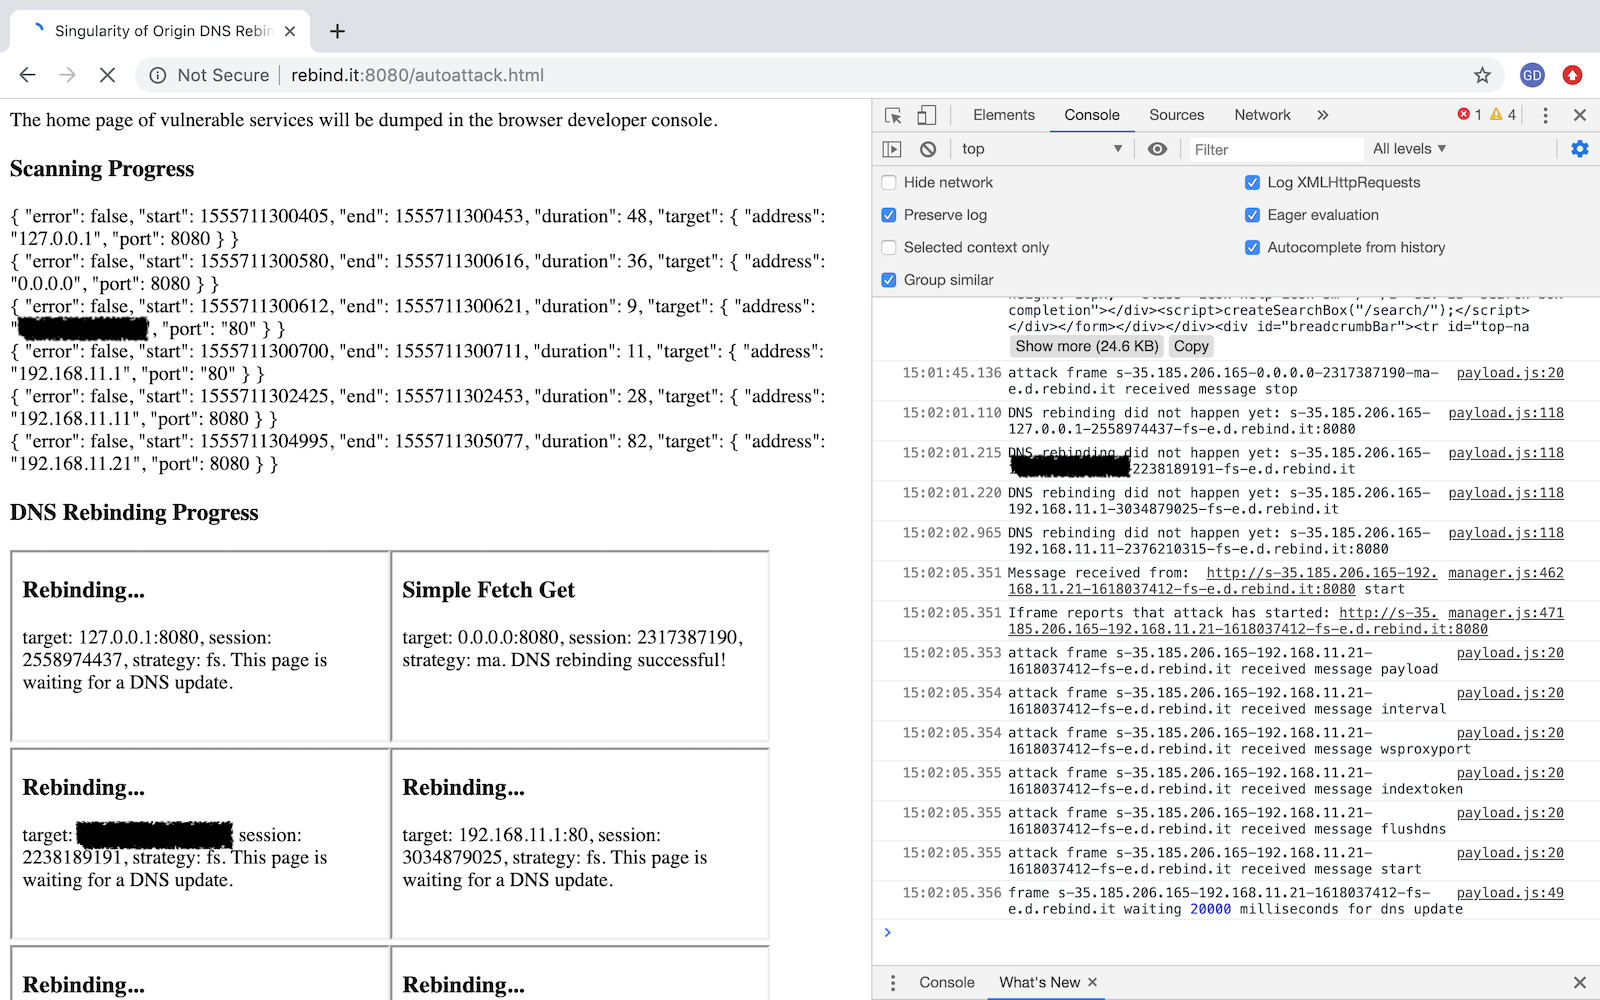 nccgroup/singularity
A DNS rebinding attack framework.
 amirrezamarzban/portscan-cve-2026-41940
IP CIDRs (presumably as input, maybe command line or file) and checks ports 2083 and 2087 for openness
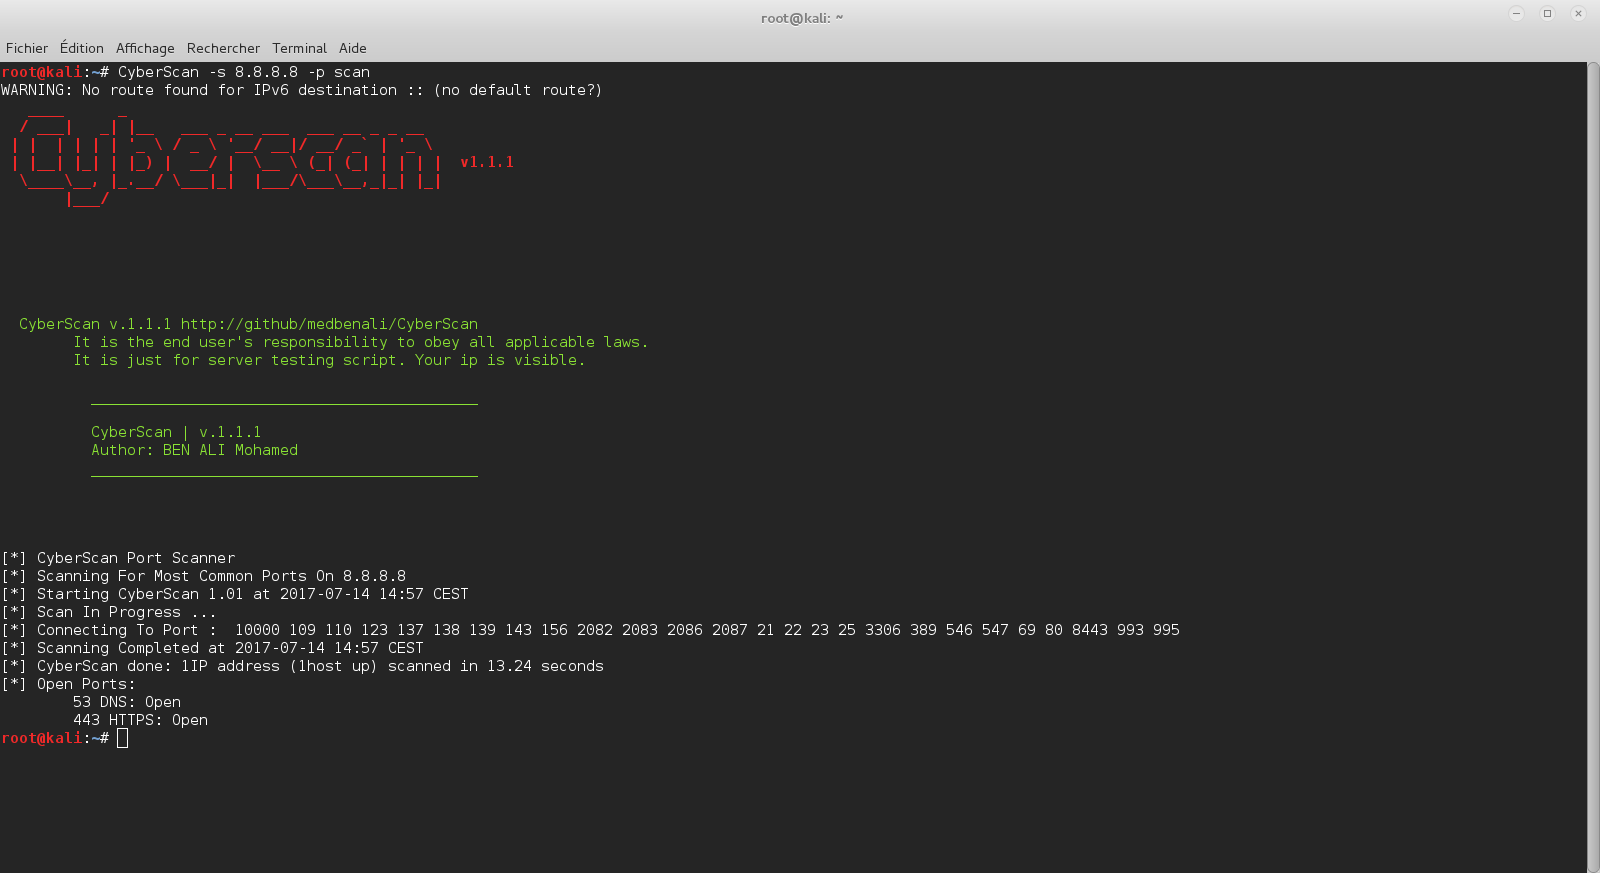 medbenali/cyberscan
Open-source network forensics toolkit for packet analysis, port scanning, host discovery, and IP geolocation. Supports ARP, ICMP, TCP, UDP pings and…
 neutralwarrior/c-port-scanner
A port scanner that scans a target IP for open ports and displays the results, built with C
 mmarting/unwaf
Go tool that passively discovers the real origin IP behind a WAF/CDN using multiple OSINT sources, then verifies candidates via HTML similarity, SSL…
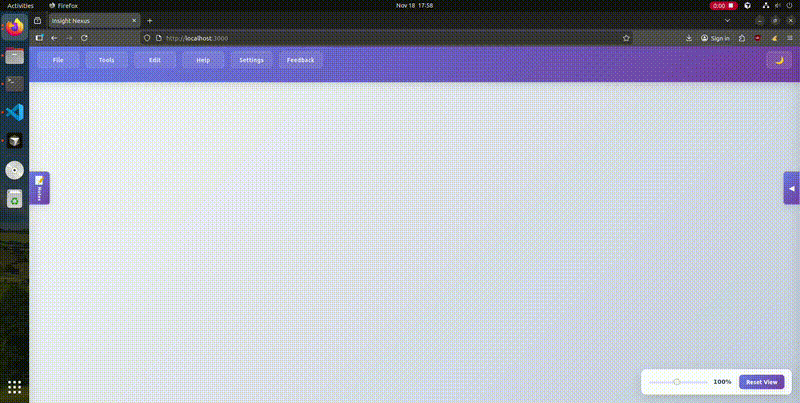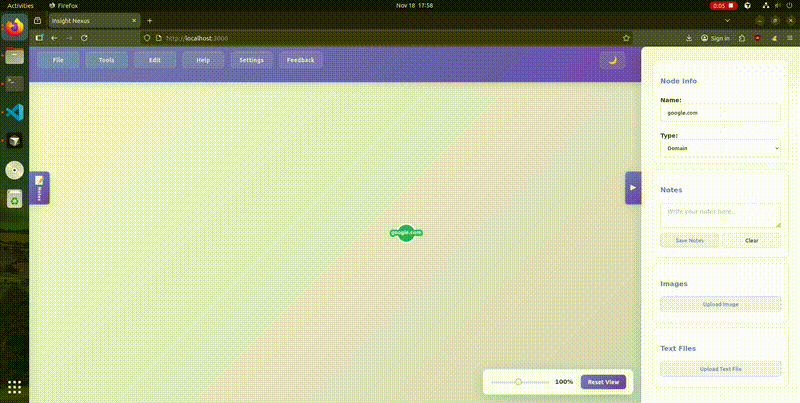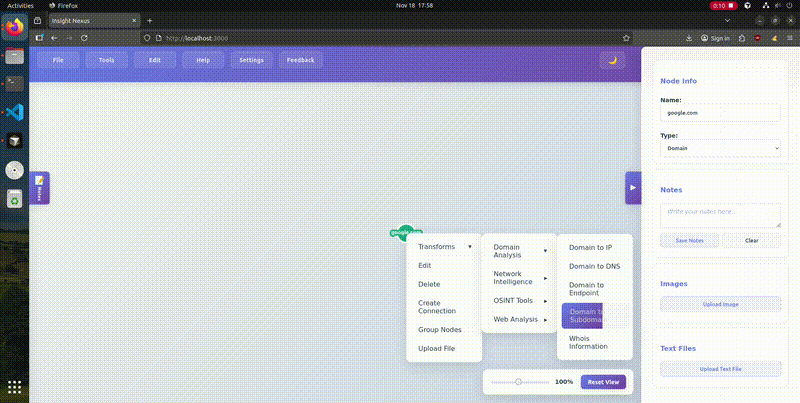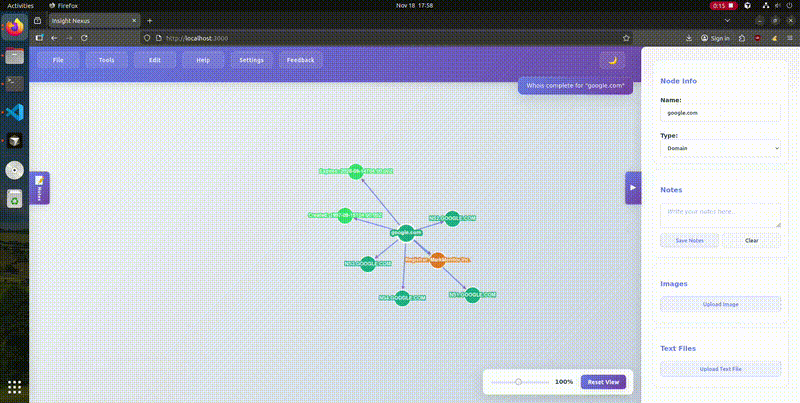 cyberintel-labs/insightsnexus
OSINT Graph Investigation Application
 m0usem0use/erl_mouse
python script to find vulnerable targets of CVE-2025-32433
 achux21/checker-cve-2024-6387
Python scanner that checks hosts for the OpenSSH regreSSHion vulnerability (CVE-2024-6387)
 r4tw1z/cve-2024-6387
This script, created by R4Tw1z, is designed to scan IP addresses to check if they are running a potentially vulnerable version of OpenSSH. The tool…
 betancour/openssh-vulnerability-test
OpenSSH CVE-2024-6387 Vulnerability Checker
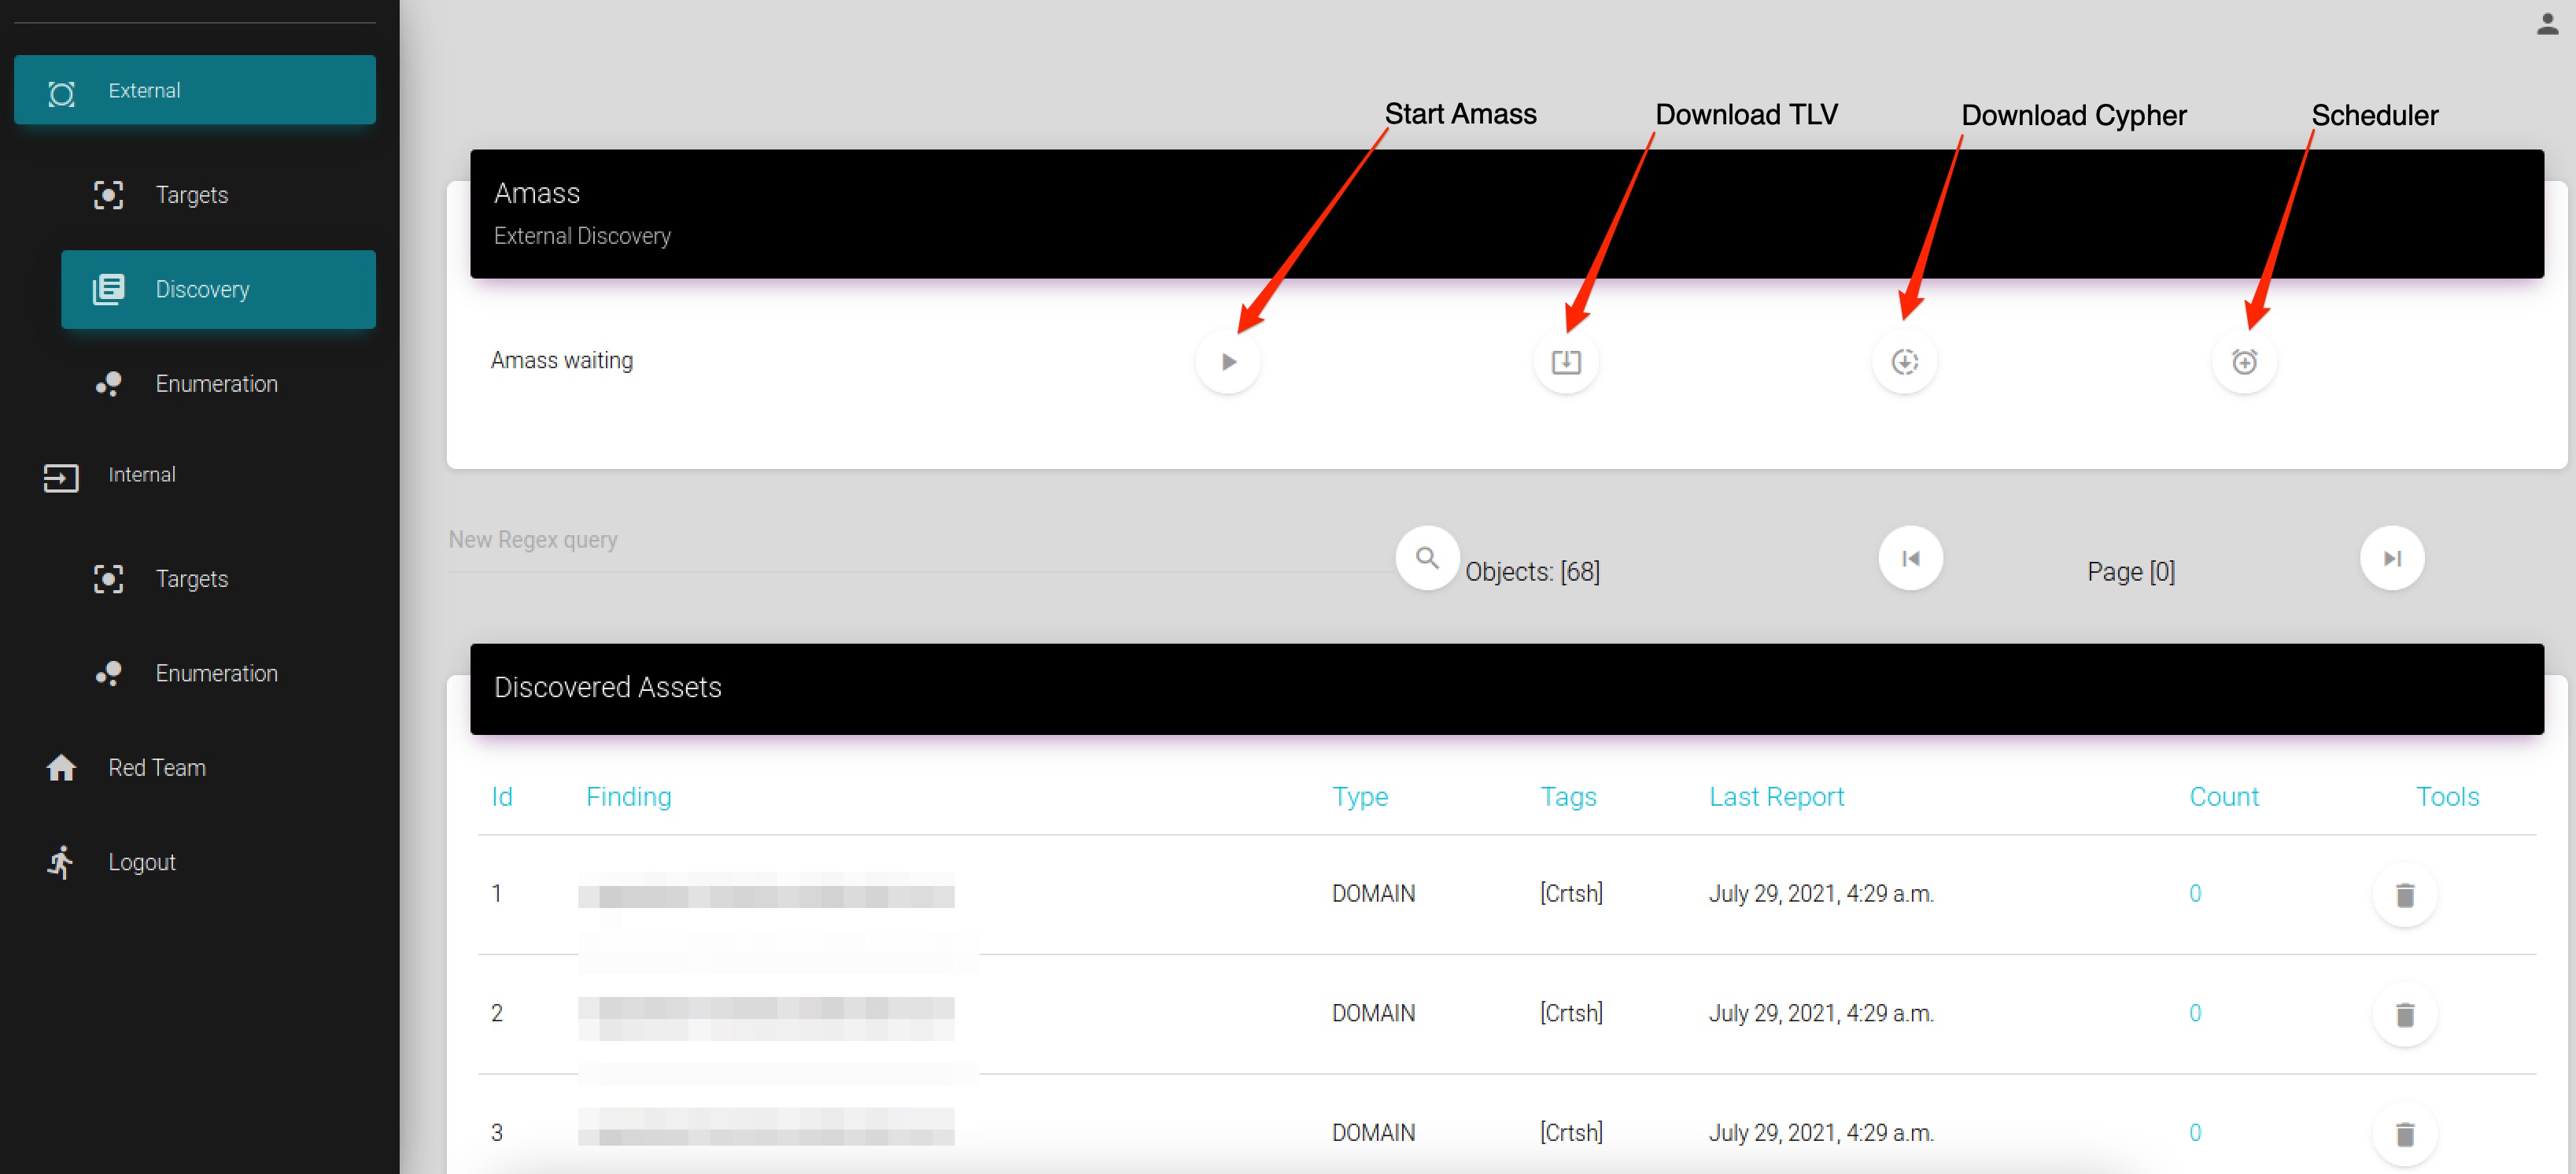 vmware-labs/attack-surface-framework
Tool to discover external and internal network attack surface
 baimaobg/sunflower_exp
Sunflower CVE-2022-10270 vulnerability exploitation tool
 anouarbensaad/vulnx
vulnx 🕷️ an intelligent Bot, Shell can achieve automatic injection, and help researchers detect security vulnerabilities CMS system. It can perform…