
awesome-bugbounty-tools
 vavkamil/awesome-bugbounty-tools
Curated directory of bug bounty tools organized by category: reconnaissance, subdomain enumeration, port scanning, content discovery, exploitation,…
curated-resourcesexploitationfuzzing+5
6.2k
vavkamil/awesome-bugbounty-toolsCurated directory of bug bounty tools organized by category: reconnaissance, subdomain enumeration, port scanning, content discovery, exploitation,…
 sinfulz/justtryharder
Comprehensive penetration testing cheat sheet for PWK/OSCP exam preparation, covering privilege escalation, password cracking, payload generation,…
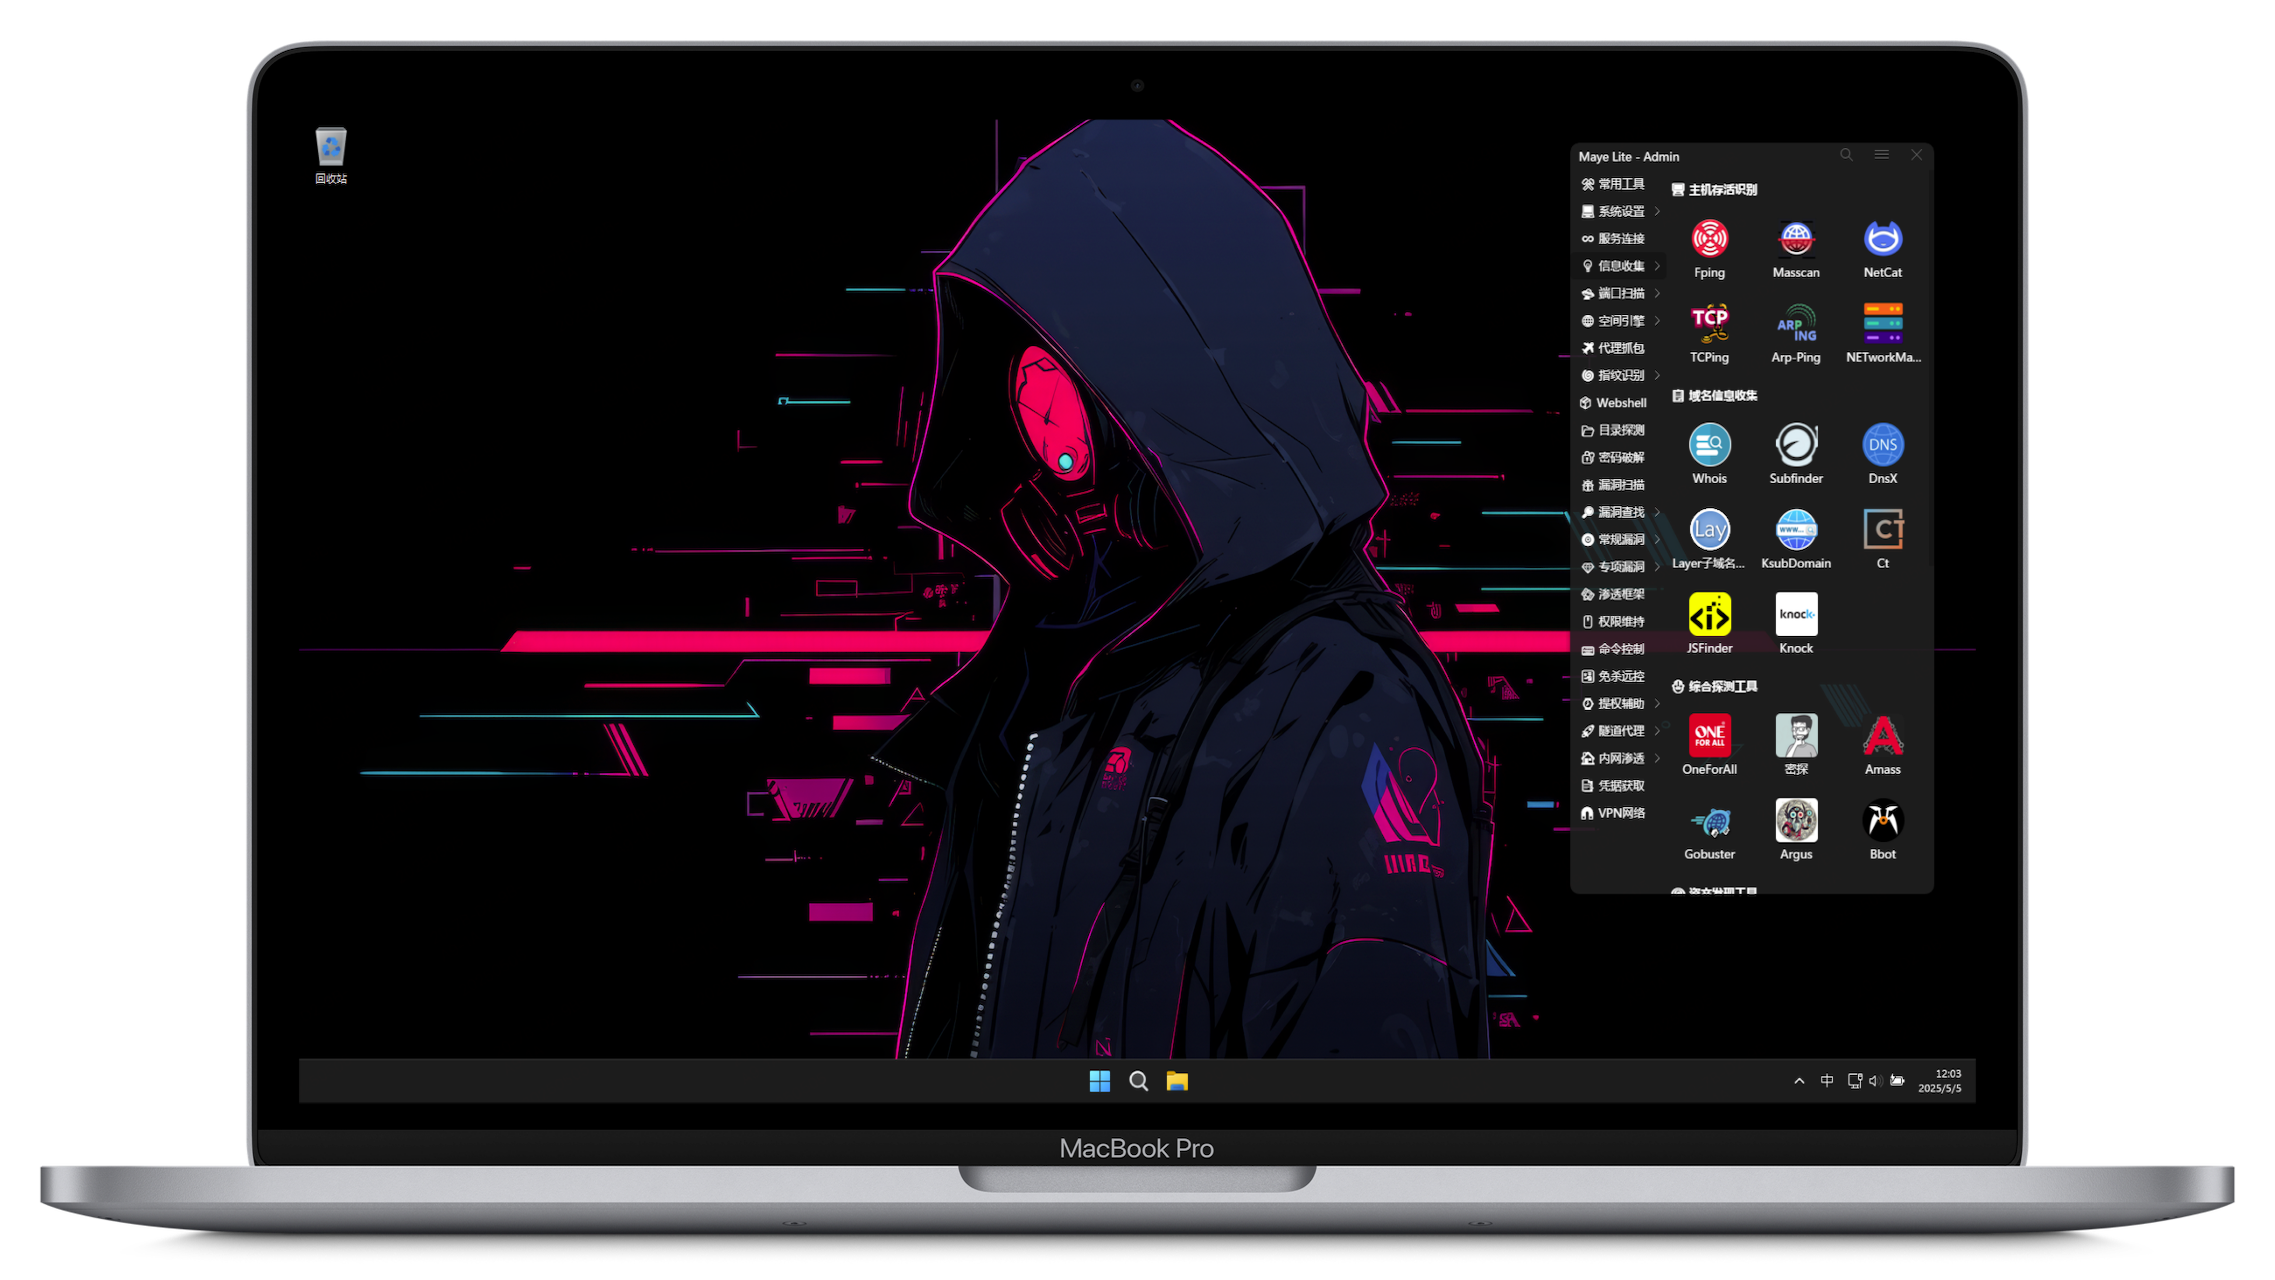 arch3rpro/pentest-windows
⚔️Windows11 Penetration Suite Toolkit 🔰 The First Windows Penetration Testing Environment on Mac M Chips
 rpranshu/eternalview
EternalView is an all in one basic information gathering and vulnerability assessment tool
 redhuntlabs/awesome-asset-discovery
Curated list of asset discovery and attack surface reconnaissance resources covering subdomain enumeration, IP discovery, port scanning, email…
 ritvikb99/dark-fantasy-hack-tool
DDOS Tool: To take down small websites with HTTP FLOOD. Port scanner: To know the open ports of a site. FTP Password Cracker: To hack file system of…
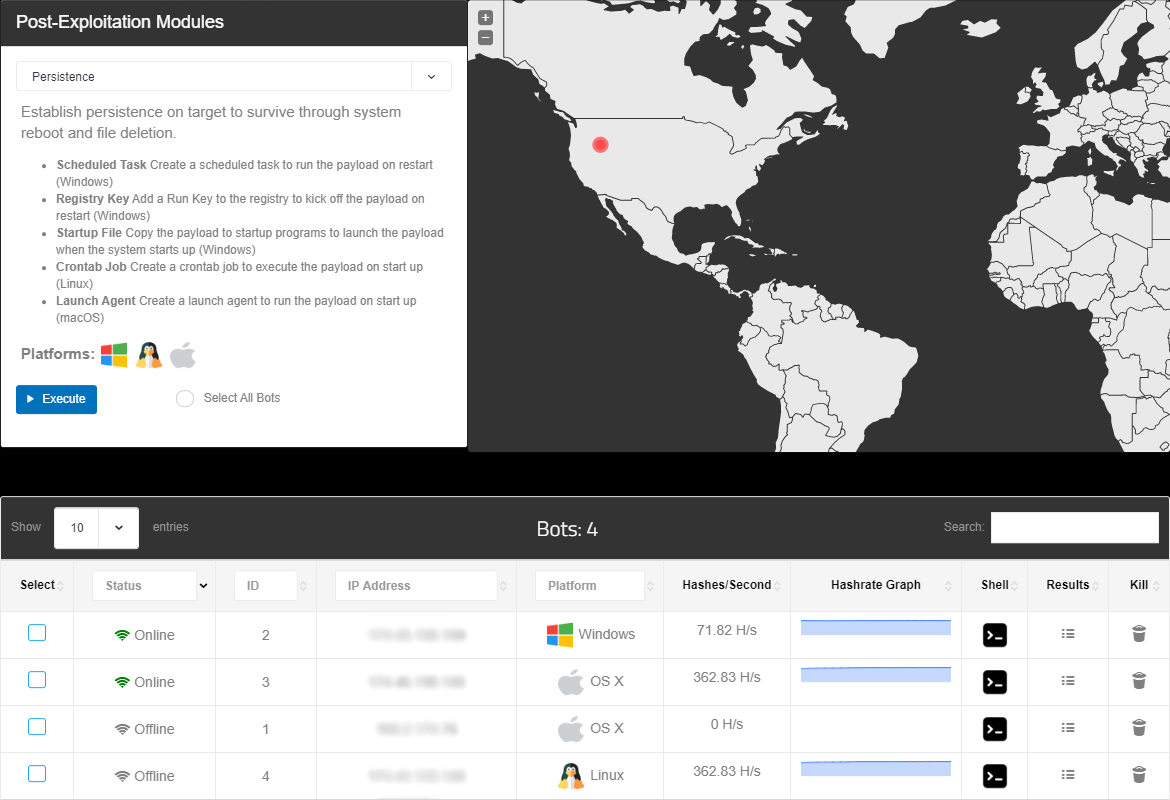 malwaredllc/byob
An open-source post-exploitation framework for students, researchers and developers.
 sakispat/simple-pentesting
An educational Python toolkit for authorized penetration testing: threaded port scanner, subdomain & directory enumeration, banner grabber and host…
 rhimavanth32-max/metasploitable2-reconnaissance-and-unrealircd-backdoor-exploitation
End-to-end recon and exploitation of a known backdoor (CVE-2010-2075) on Metasploitable2 using Nmap and Metasploit.
 prapul1/vulnhub-dc1-writeup
VulnHub DC-1 boot-to-root — exploiting CVE-2018-7600 (Drupalgeddon2) for RCE, extracting DB credentials from settings.php, forging admin password…
 nu11secur1ty/nmap-cheat-sheet
Curated cheat sheet for Nmap, covering target selection, port scanning, service/OS detection, NSE scripts, and output formats for network…
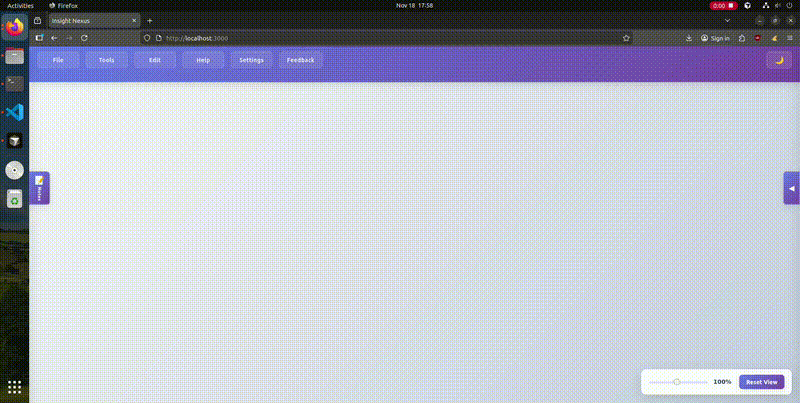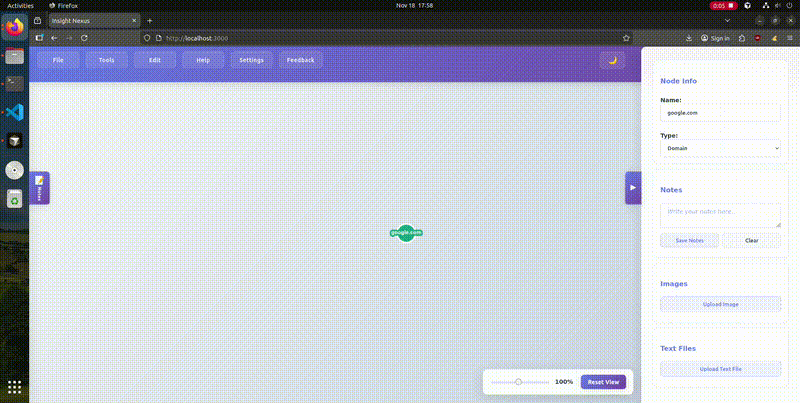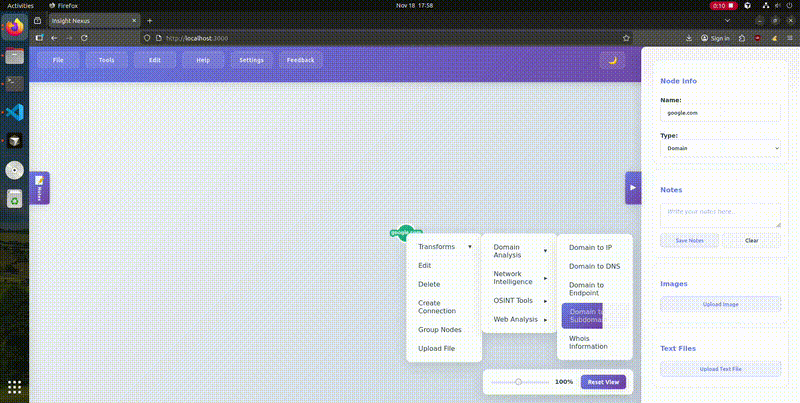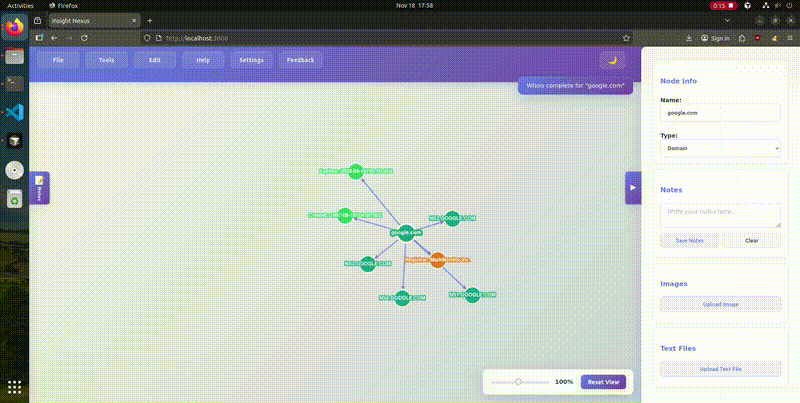 cyberintel-labs/insightsnexus
OSINT Graph Investigation Application
 dviros/excalibur
Excalibur is an Eternalblue exploit payload based "Powershell" for the Bashbunny project.
 mngunibanda1-prog/jozini-network-scanner
Python-based network scanner with port scanning, banner grabbing, and RouterOS CVE mapping for vulnerability identification and reporting.
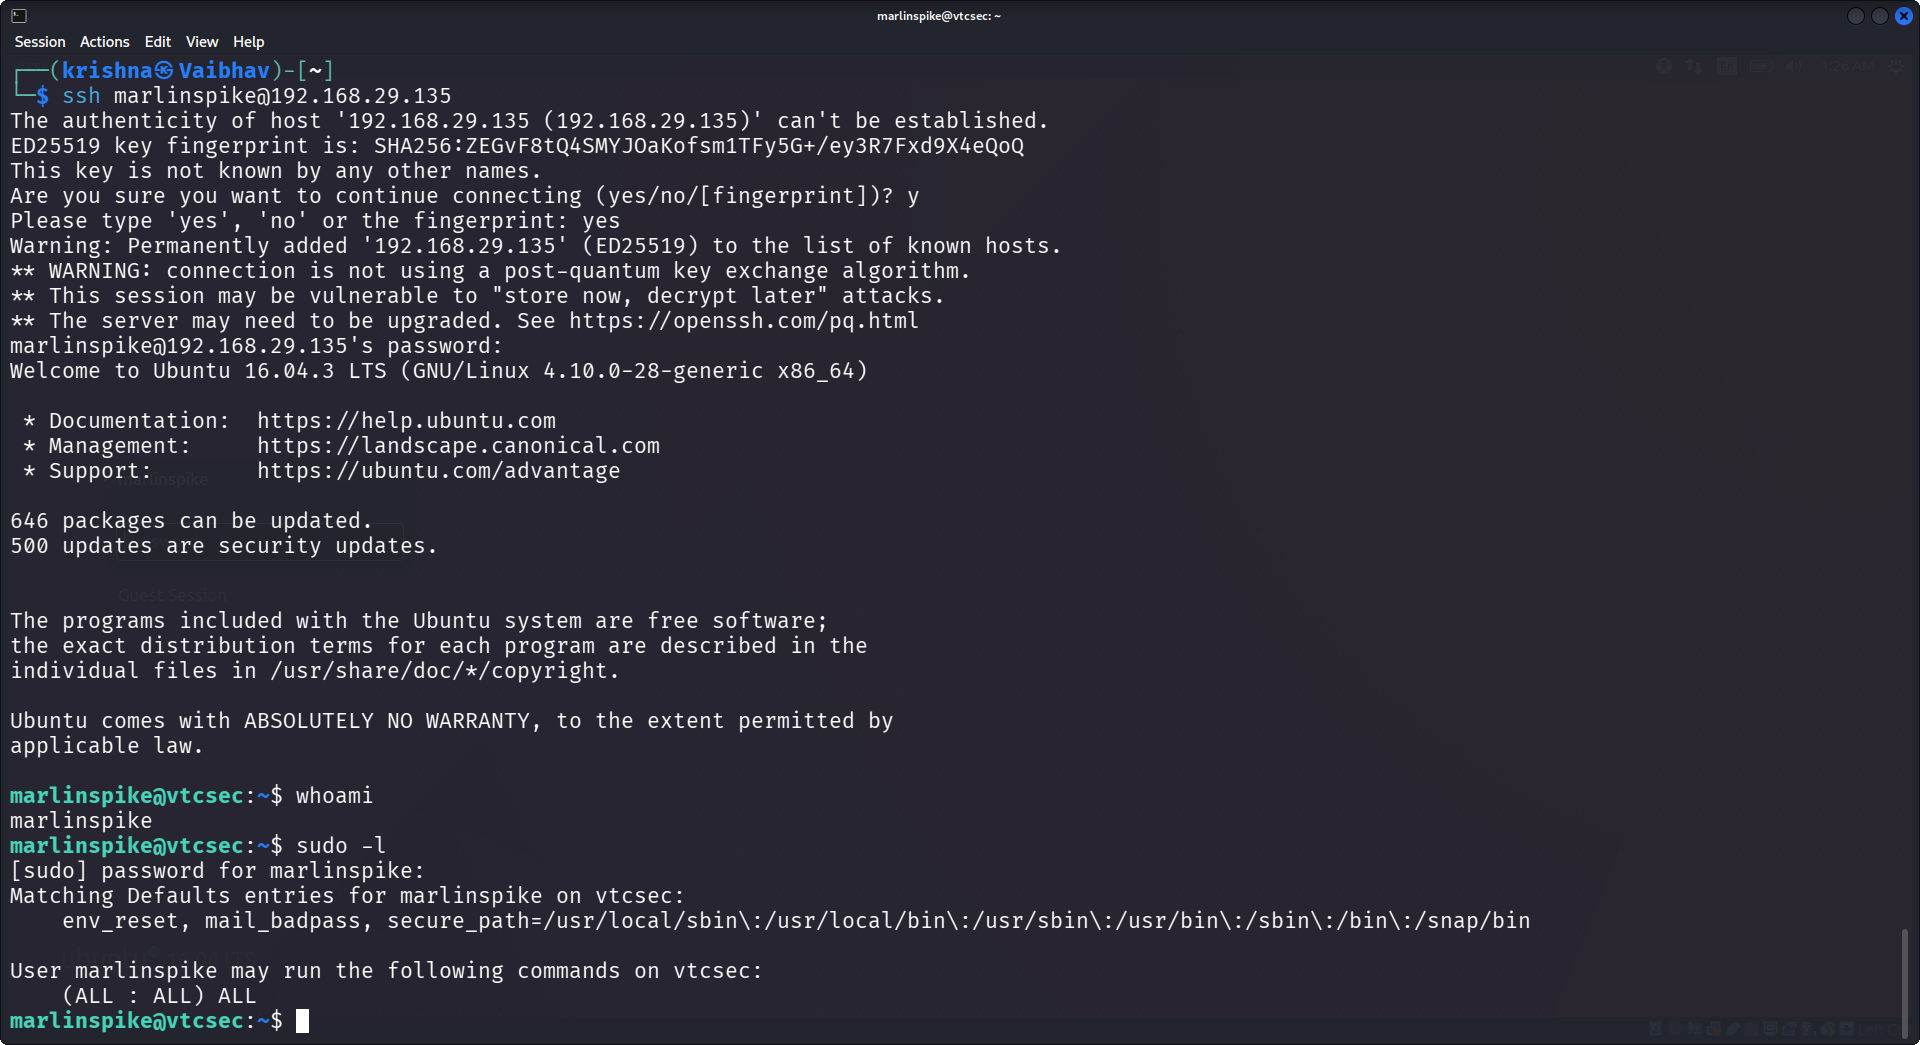 vaibhavkrishna12004/ubuntu-privesc-lab
Full penetration testing workflow: credential brute force, SSH access and privilege escalation (CVE-2021-4034)
 mafiosohack/offensive-lab-2
Penetration test walkthrough on a vulnerable Ubuntu VM. Exploited the ProFTPD 1.3.3c backdoor (CVE-2010-4221) to gain root access and capture the…
 ivoalbacete/kali-metasploitable
Escaneo de vulnerabilidades, análisis de tráfico con Wireshark y explotación controlada del CVE-2011-2523 (vsftpd 2.3.4) en entorno de red segura.
 cumakurt/tscan
Python-based scanner that detects and exploits CVE-2026-24061 telnetd authentication bypass, enabling root shell access on vulnerable GNU Inetutils…