

spoonmap
 trustedsec/spoonmap
Python wrapper around masscan and nmap for large-scale port discovery, host discovery, banner grabbing, and NSE-based vulnerability scanning across…
defensive-toolsinformation-gatheringnetwork-mapping+7
214
trustedsec/spoonmapPython wrapper around masscan and nmap for large-scale port discovery, host discovery, banner grabbing, and NSE-based vulnerability scanning across…
 mad-robot/spartan
Automated reconnaissance framework integrating subdomain enumeration, live host probing, port scanning, CMS detection, and directory brute-forcing…
 ullaakut/nmap
Idiomatic Go library for invoking a network scanner binary, enabling host discovery, port scanning, service/OS detection, and scripted vulnerability…
 sakispat/simple-pentesting
An educational Python toolkit for authorized penetration testing: threaded port scanner, subdomain & directory enumeration, banner grabber and host…
 rhimavanth32-max/metasploitable2-reconnaissance-and-unrealircd-backdoor-exploitation
End-to-end recon and exploitation of a known backdoor (CVE-2010-2075) on Metasploitable2 using Nmap and Metasploit.
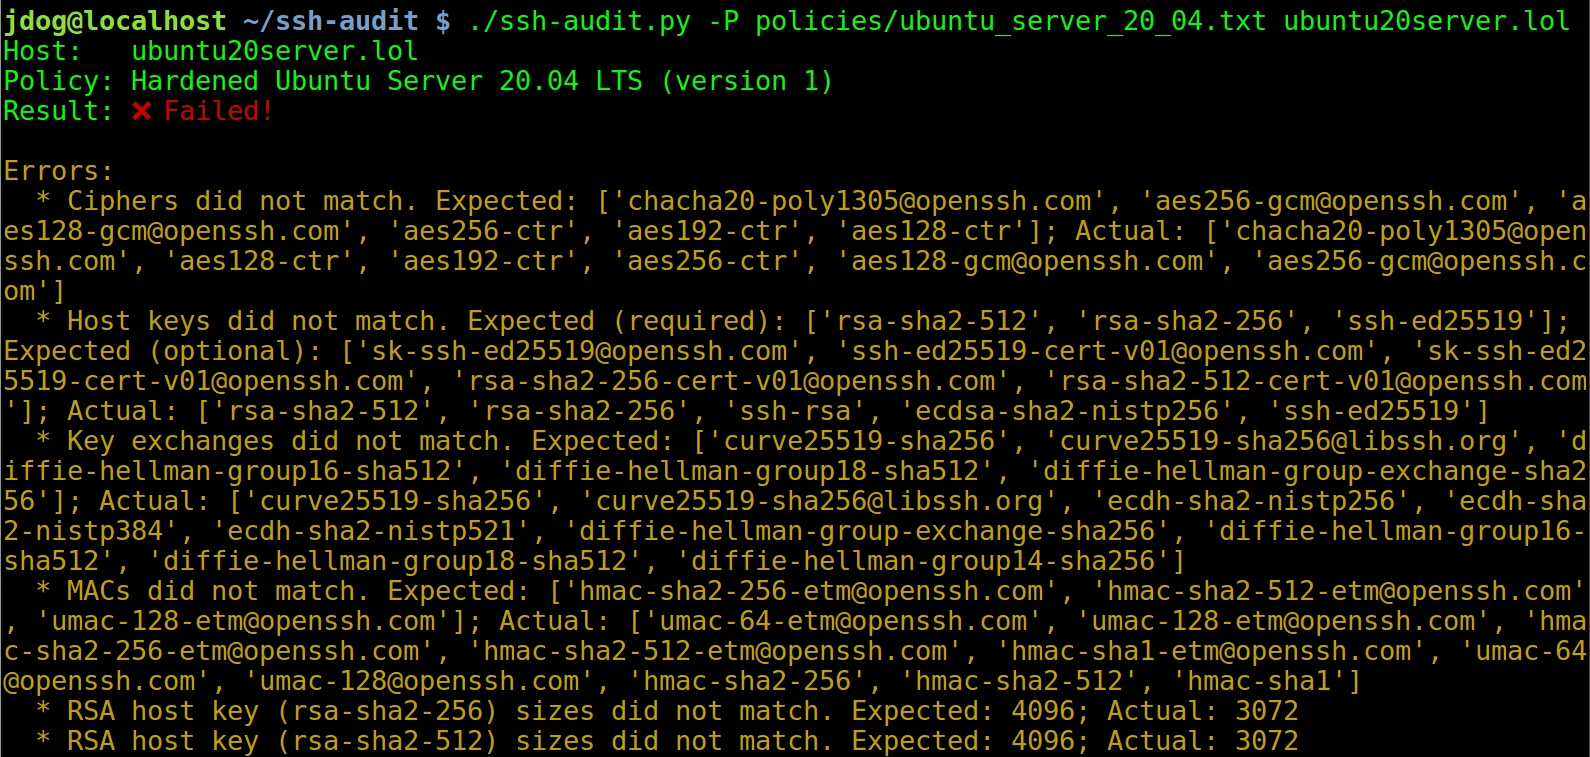 jtesta/ssh-audit
SSH server & client security auditing (banner, key exchange, encryption, mac, compression, compatibility, security, etc)
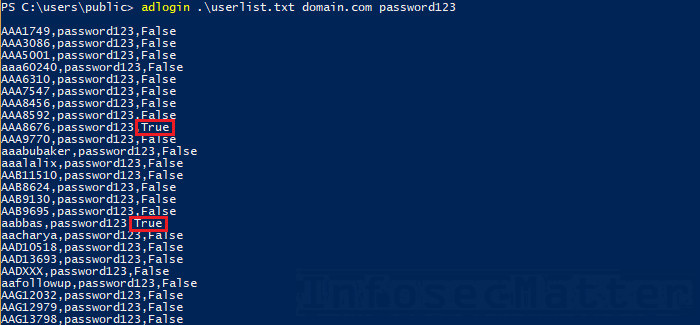 infosecmatter/minimalistic-offensive-security-tools
A repository of tools for pentesting of restricted and isolated environments.
 haishanzheng/cve-2019-0708-generate-hosts
CIDR-based host discovery tool that uses nmap to identify Windows machines with open port 3389 (RDP), reducing target IPs for CVE-2019-0708…
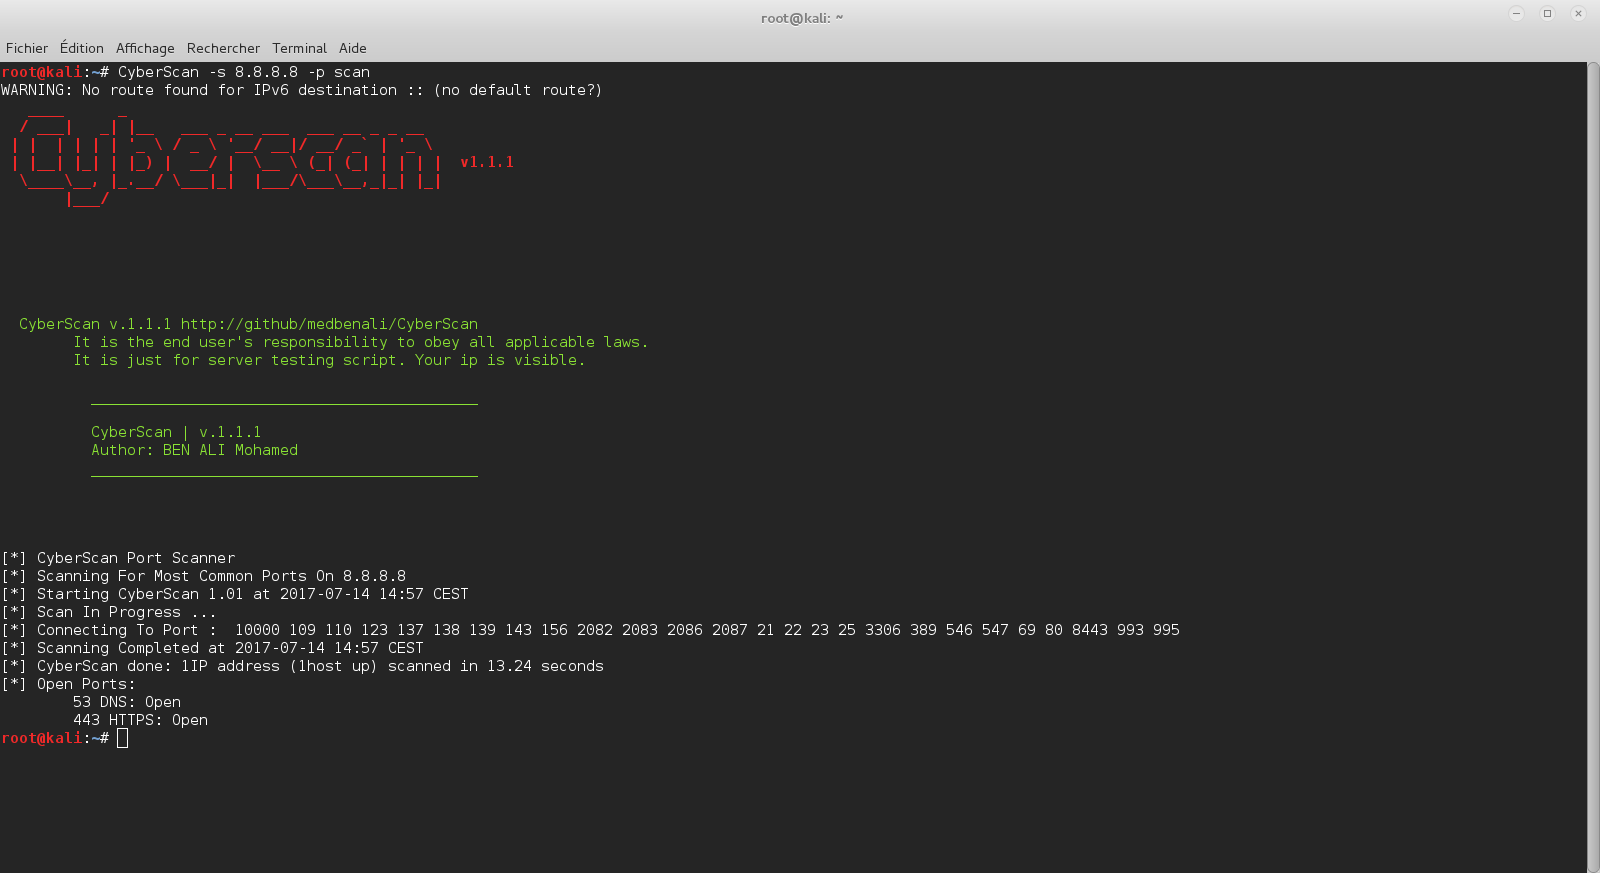 medbenali/cyberscan
Open-source network forensics toolkit for packet analysis, port scanning, host discovery, and IP geolocation. Supports ARP, ICMP, TCP, UDP pings and…
 isnic/prober
Automated, reproducible network security testing framework using Ansible and BATS to verify DNS, host availability, open ports, and TLS configuration…
 kabiri-labs/sshfinder
Parallel SSH service discovery and security auditor that scans any port, validates SSH banners, and audits authentication methods, weak cryptography,…
 nurdilin/cve-2018-16706
Or how I turn off my TV via a cronjob
 serain/netmap.js
Fast browser-based network discovery module