
toxssin
 t3l3machus/toxssin
An XSS exploitation command-line interface and payload generator.
exploitationinformation-gatheringpayload-generation+4
t3l3machus/toxssinAn XSS exploitation command-line interface and payload generator.
 redsiege/excelntdonut
Excel 4.0 (XLM) Macro Generator for injecting DLLs and EXEs into memory.
 d00mfist/mystikal
macOS Initial Access Payload Generator
 bardlaudian/cve-2025-24071
Dependency-free Python PoC generator for CVE-2025-24071 that crafts a malicious .library-ms file in a ZIP to trigger Windows Explorer NTLM hash…
 s0md3v/jshell
JShell - Get a JavaScript shell with XSS.
 arno0x/embedinhtml
Embed and hide any file in an HTML file
 stmcyber/boobsnail
Generate obfuscated Excel 4.0 XLM macros for red team operations and blue team analysis, with support for multiple infection techniques, formula…
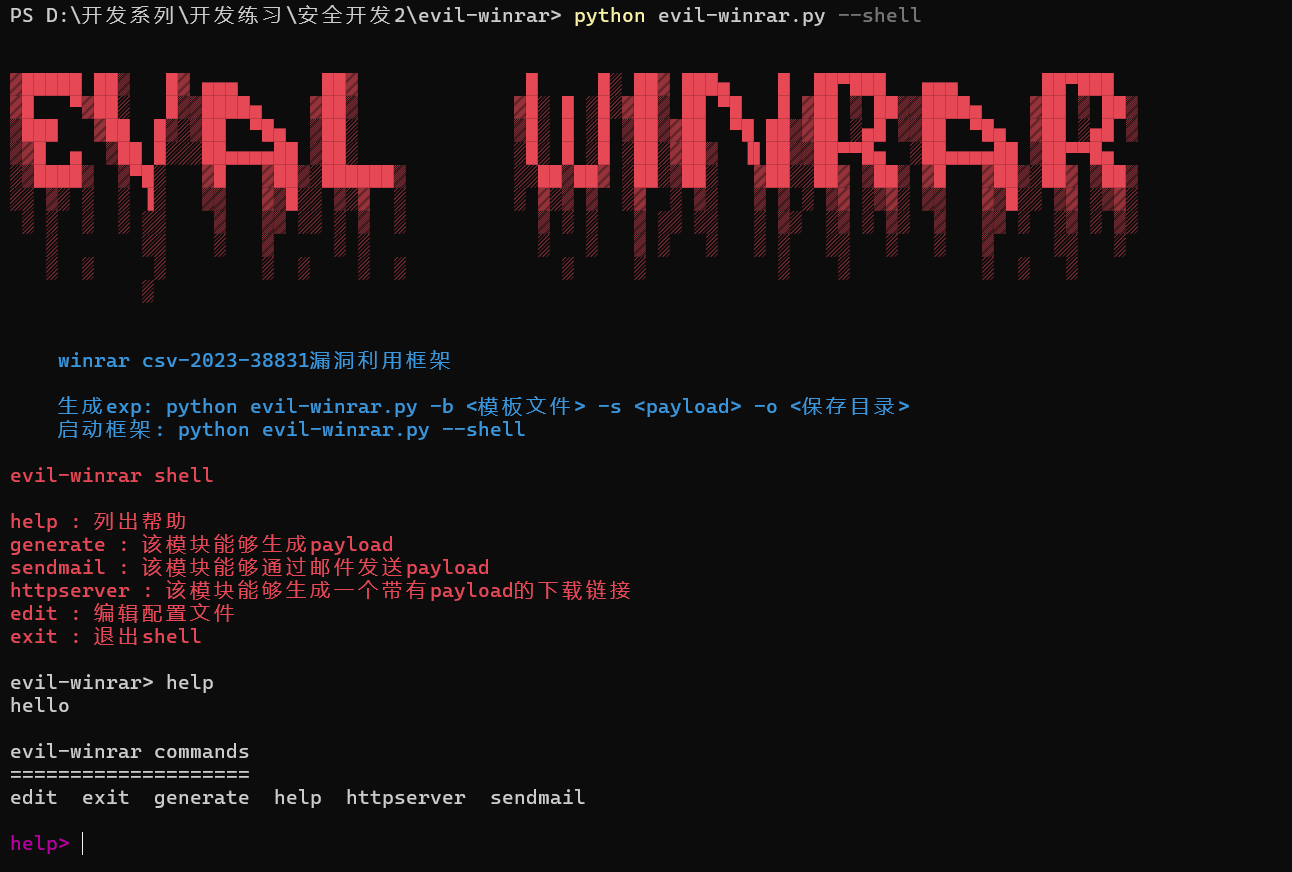 youmulijiang/evil-winrar
evil-winrar,CVE-2023-38831漏洞利用和社会工程学攻击框架 (evil-winrar, CVE-2023-38831 Vulnerability Exploitation and Social Engineering Attack Framework)
 mohwahyudi/poc-cve-2026-64638-
PoC exploit chain for WordPress pre-auth XSS to RCE via DOM clobbering, REST JSONP/SOME, and plugin upload, with Docker lab verification and…
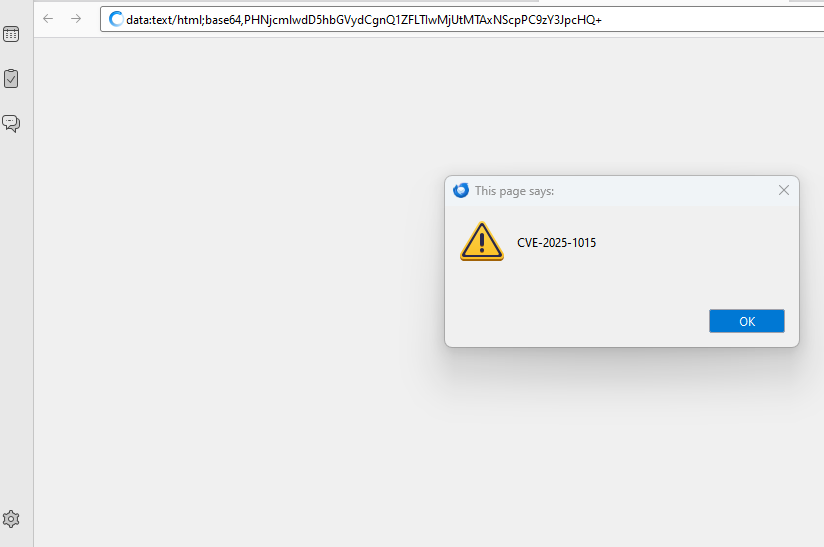 r3m0t3nu11/cve-2025-1015
an attacker to create and export an address book containing a malicious payload in a field. For example, in the “Other” field of the Instant…
 raffli-dev/cve-2023-41425
Exploit for Wonder CMS XSS to RCE (CVE-2023-41425) with theme upload and reverse shell payloads.
 zzn1nj4/cve-2025-22131-poc
PoC for CVE-2025-22131
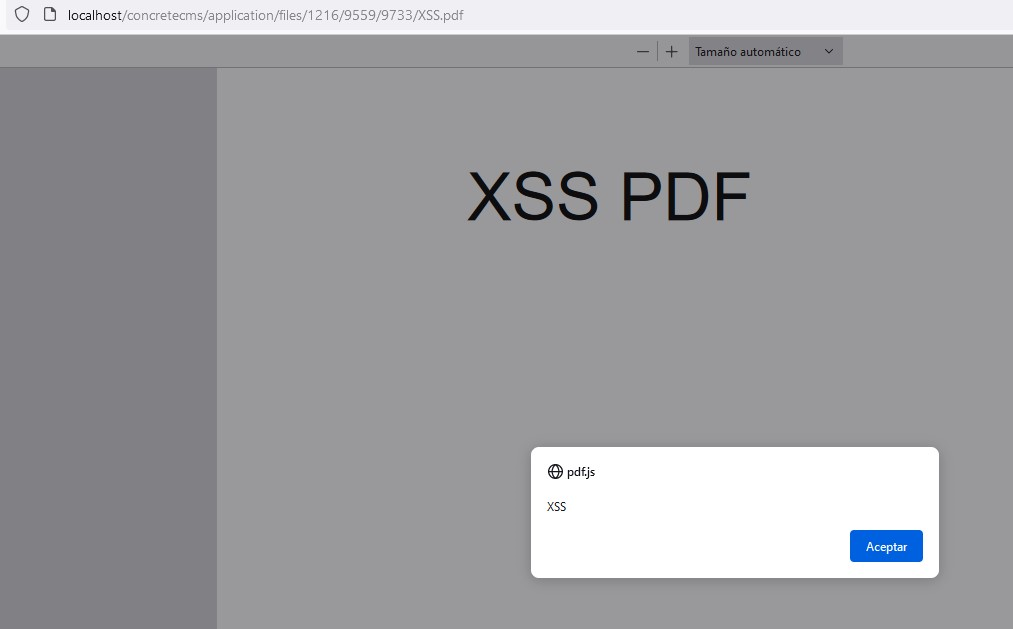 sromanhu/cve-2023-44763_concretecms-arbitrary-file-upload-thumbnail
ConcreteCMS v.9.2.1 is affected by Arbitrary File Upload vulnerability that allows Cross-Site Scriting (XSS) Stored.
 hunt-benito/cve-2026-41200-stig-manager-oidc-reflected-xss
Proof-of-concept exploit generator for reflected XSS in STIG Manager OIDC authentication, enabling session token theft via crafted callback URLs and…
 secsys-fdu/cve-2025-51863
Proof-of-concept for a Self-XSS vulnerability in ChatGPTUtil, demonstrating cookie theft and account hijacking via crafted SVG payloads pasted into…