
 trustedsec/unicorn
Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…
 komomon/cve-2022-30190-follina-office-msdt-fixed
Modified CVE-2022-30190 exploit tool for MS-MSDT Office RCE with custom docx template support, binary/command execution modes, and embedded HTTP…
 retr0-code/signhere
SignHere is implementation of CVE-2017-11882. SignHere is builder of malicious rtf document and VBScript payloads.
 ash1996x/cve-2025-50154-aggressor-script
Cobalt Strike Aggressor script that weaponizes LNK and Library-MS files to trigger SMB NTLMv2 hash disclosure, including CVE-2025-24054 bypass, for…
 cisc0-gif/kitt-lite
Python-Based Pentesting CLI Tool
 rmikehodges/hidensneak
a CLI for ephemeral penetration testing
 beefproject/beef
The Browser Exploitation Framework Project
 r00t-3xp10it/fakeimageexploiter
Use a Fake image.jpg to exploit targets (hide known file extensions)
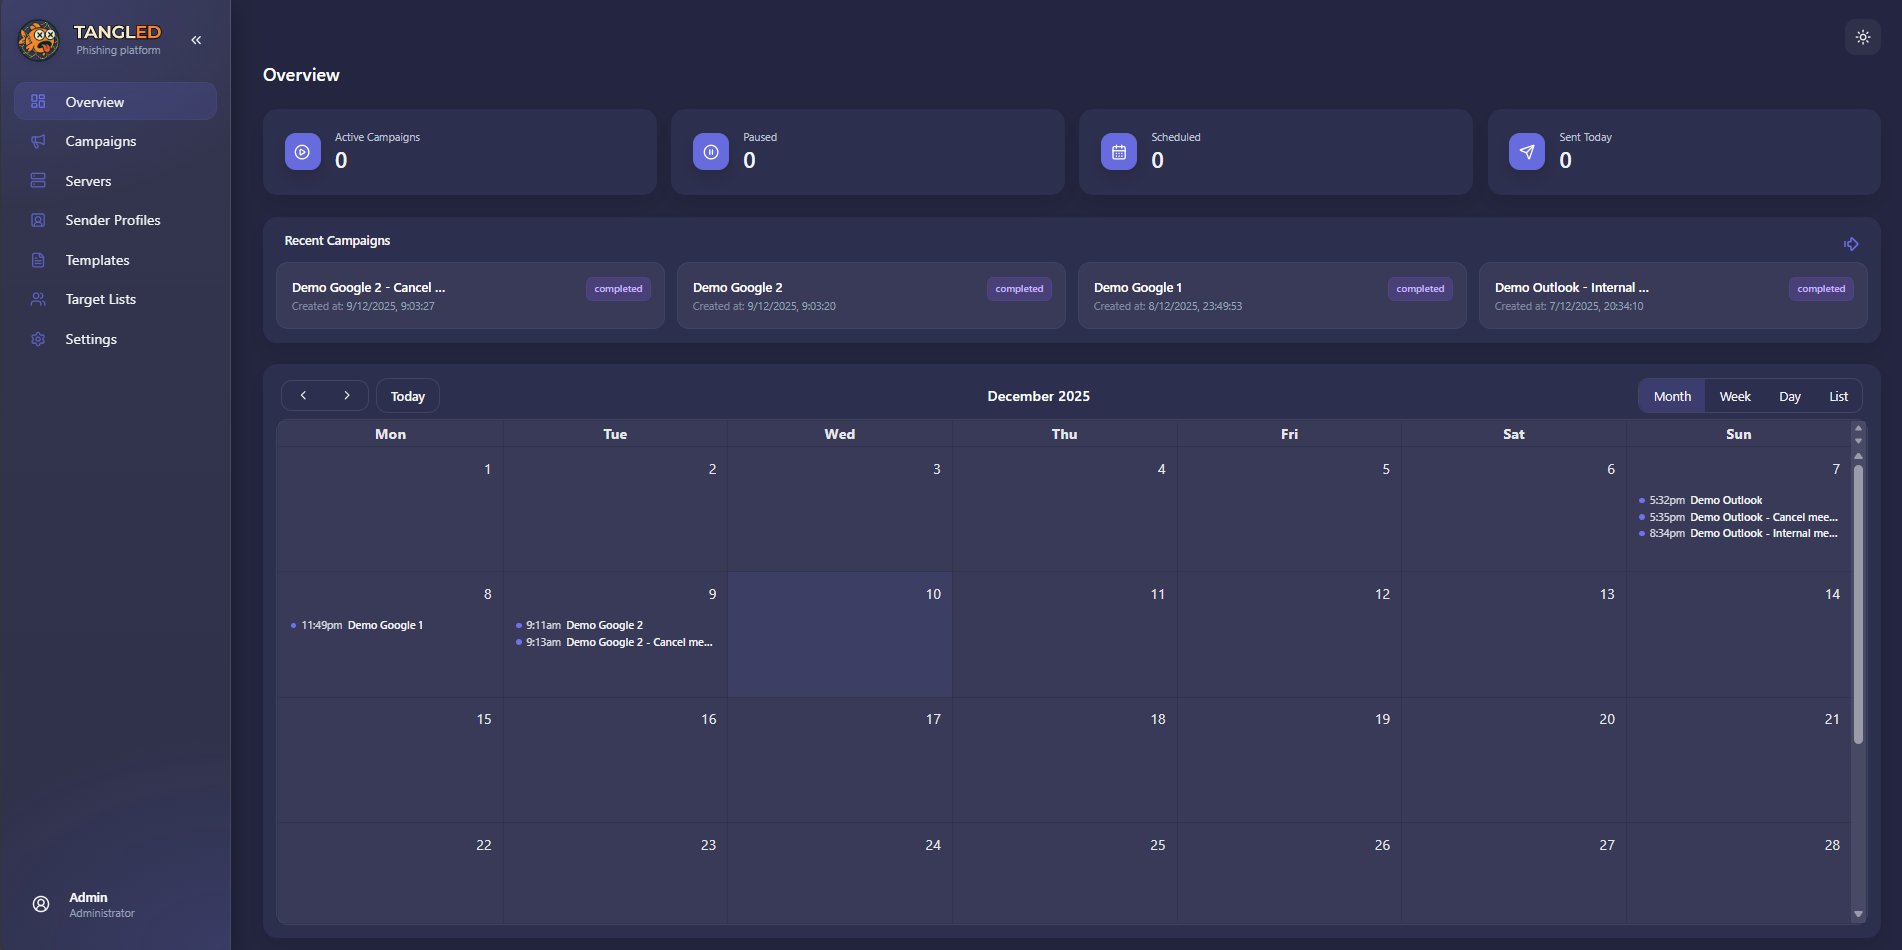 ineesdv/tangled
Open-source offensive security platform for conducting phishing campaigns that weaponizes iCalendar automatic event processing.
 jmousqueton/poc-cve-2022-30190
POC CVE-2022-30190 : CVE 0-day MS Offic RCE aka msdt follina
 cedowens/mythic-macro-generator
Python3 script to generate a macro to launch a Mythic payload. Author: Cedric Owens
 rootup/git-fsmonitor
This is a proof-of-work for abusing "fsmonitor" against IDE.
 operatorequals/smbrat
A Windows Remote Administration Tool in Visual Basic with UNC paths
 0xflagplz/ms-msdt-office-rce-follina
CVE-2022-30190 | MS-MSDT Follina One Click