
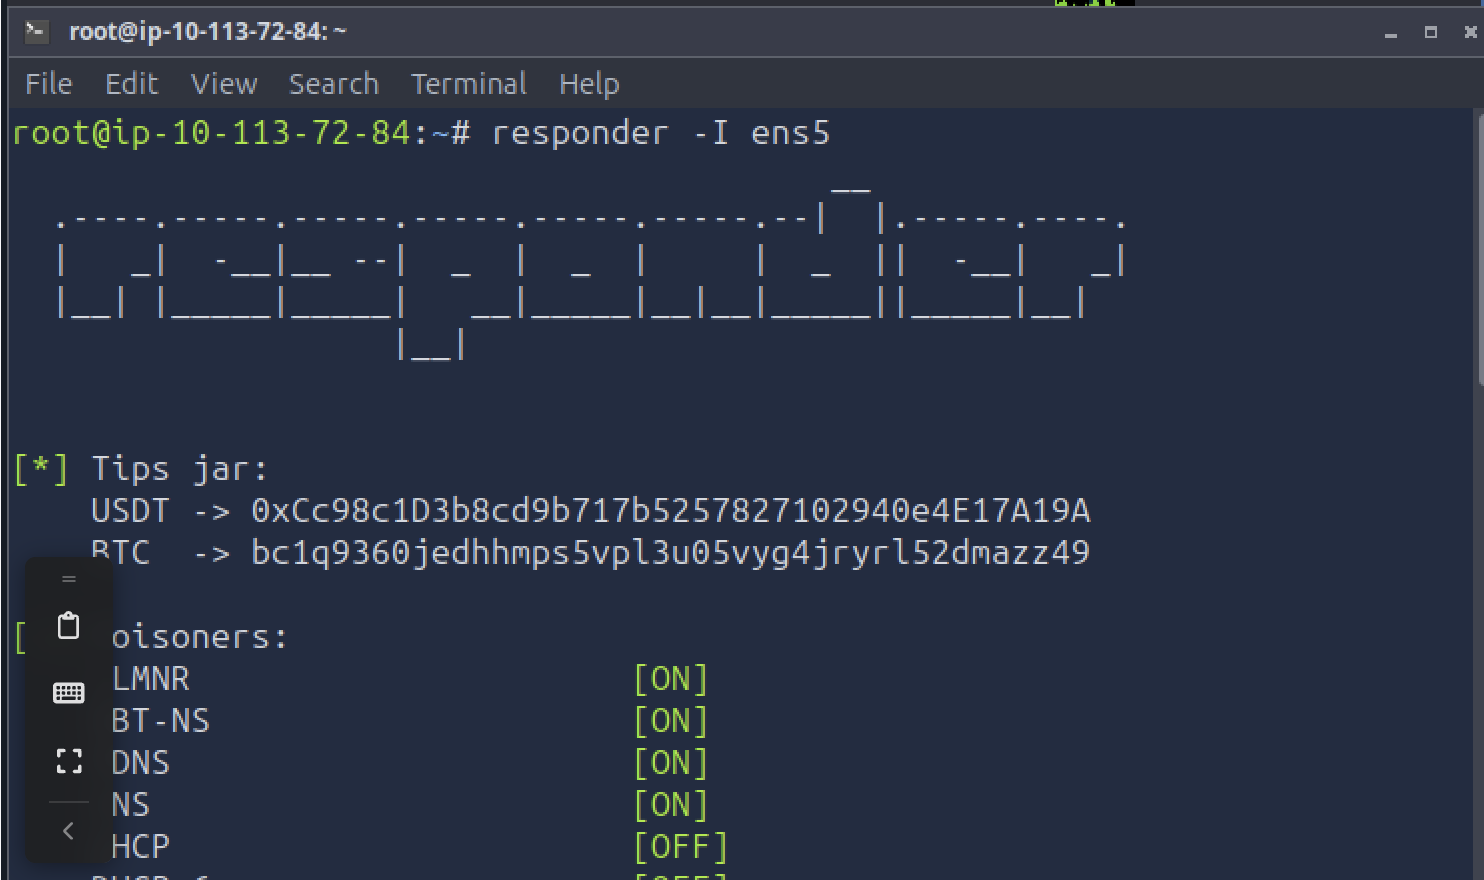
tryhackme-monikerlink-writeup
 omarmahmoud1024/tryhackme-monikerlink-writeup
TryHackMe Moniker Link (CVE-2024-21413) walkthrough: Outlook Protected View bypass leading to NTLMv2 hash capture via a crafted moniker link.
ctfeducationexploitation+4
omarmahmoud1024/tryhackme-monikerlink-writeupTryHackMe Moniker Link (CVE-2024-21413) walkthrough: Outlook Protected View bypass leading to NTLMv2 hash capture via a crafted moniker link.
 diegomjx/cve-2023-41425-wondercms-authenticated-rce
Xss injection, WonderCMS 3.2.0 -3.4.2
 exfil0/weaponizing-cve-2024-4367
CVE-2024-4367 is a critical vulnerability (CVSS 9.8) in PDF.js, allowing arbitrary JavaScript code execution due to insufficient type checks on the…
 chrxstxqn/cve-2025-6218-winrar-rce-poc
Comprehensive analysis and proof-of-concept for CVE-2025-6218 - WinRAR path traversal RCE vulnerability affecting versions 7.11 and earlier
 bhatbhupendra/moniker-link--cve-2024-21413-
Educational guide on CVE-2024-21413, the Outlook zero-click Moniker Link vulnerability, covering attack flow, NTLM credential capture, detection with…
 hantul/kotaemon-cve-2025-56526-56527-disclosure
Public disclosure for CVE-2025-56526 and CVE-2025-56527 — Stored XSS via unsanitized PDF content rendering and plaintext credential exposure in…
 elamani-drawing/cve-2024-4367-poc-pdfjs
PoC (Proof of Concept) de la CVE-2024-4367 - Vulnérabilité RCE dans libwebp. Démonstration complète incluant : création de payloads, scénarios…
 relichunt3r/swagger-ui
Swagger UI (CVE-2018-25031) POC, [HTMLi, XSS].
 reggyraider/cve-2023-21716
CVE-2023-21716 - Microsoft Word RTF fonttbl Heap Corruption RCE exploit with reverse shell payload
 xdavidhu/mitmap
📡 A python program to create a fake AP and sniff data.
 curi0usjack/luckystrike
A PowerShell based utility for the creation of malicious Office macro documents.