

Awesome-BEC
 randomaccess3/awesome-bec
Repository of attack and defensive information for Business Email Compromise investigations
cloud-securitycurated-resourcesdigital-forensics+7
randomaccess3/awesome-becRepository of attack and defensive information for Business Email Compromise investigations
 jenyraval/phishing-simulation
Phishing Simulation mainly aims to increase phishing awareness by providing an intuitive tutorial and customized assessment
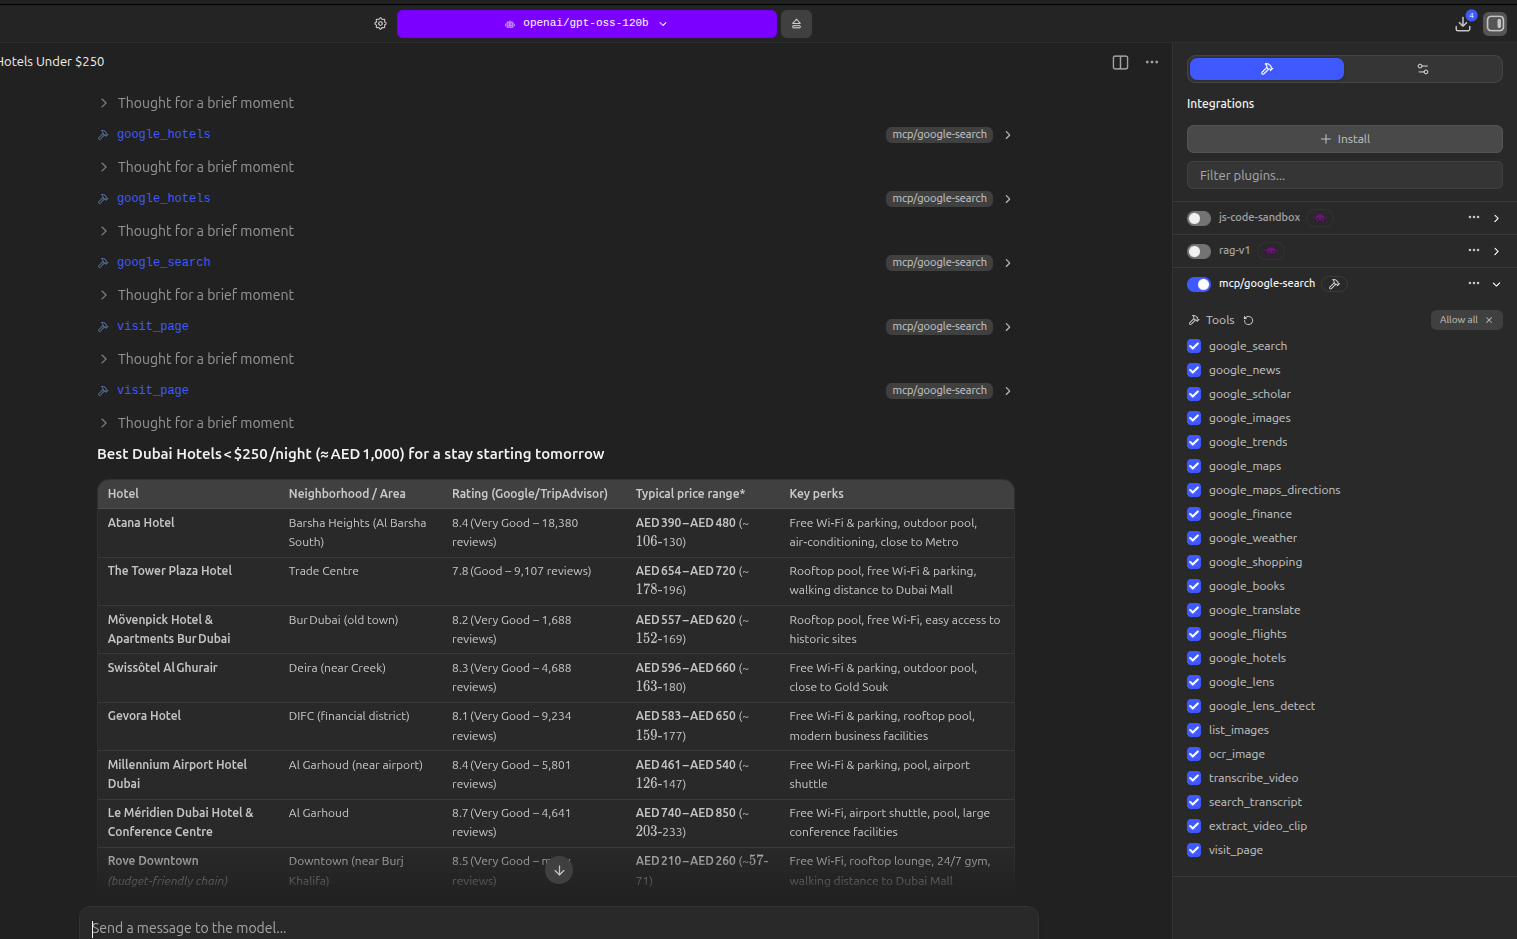 vincentkaufmann/noapi-google-search-mcp
MCP server for Google search and page fetching using headless Chromium
 duy-31/cve-2024-21413
Microsoft Outlook Information Disclosure Vulnerability (leak password hash) - Expect Script POC
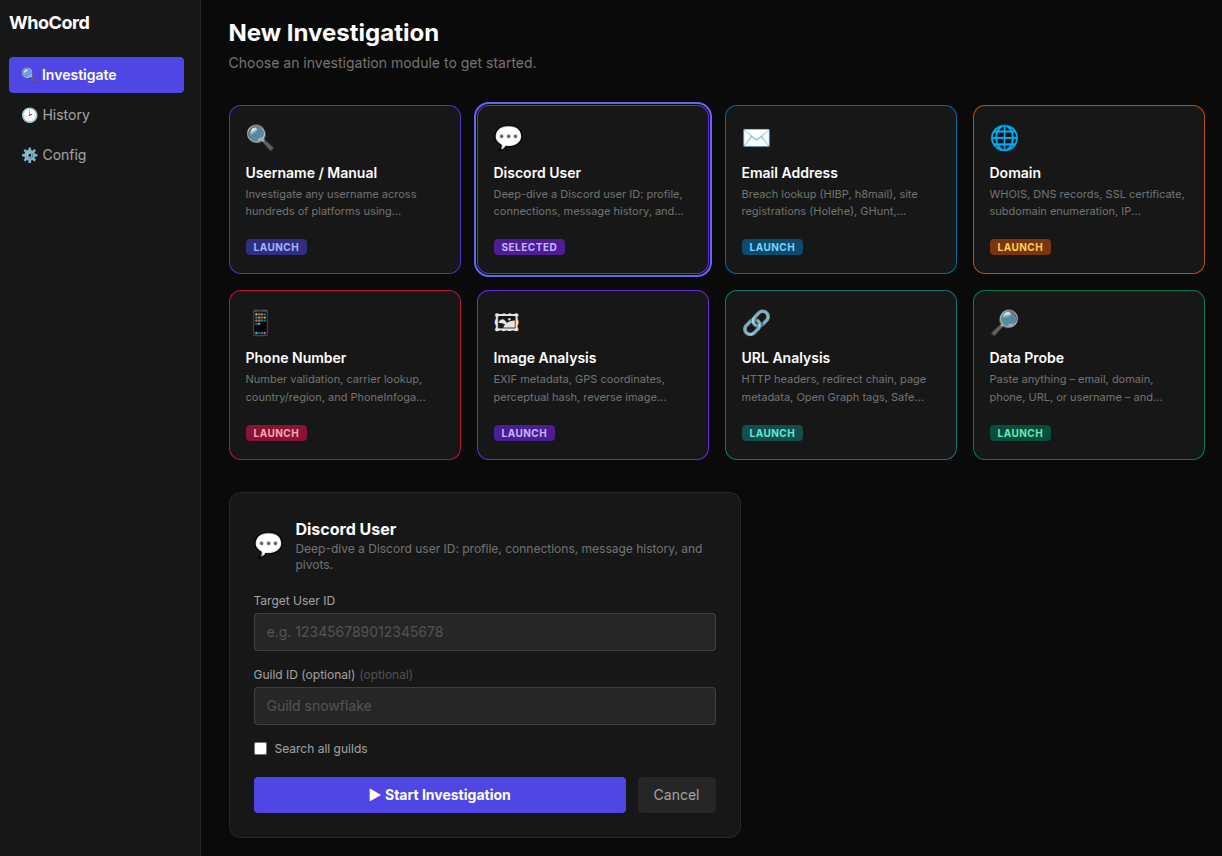 siv-nick/whocord
Scans Discord links across mutual guilds to extract profiles, cross‑references 700+ sites, searches usernames with 30+ tools, and generates an…
 trustedsec/reel
Phishing simulation and awareness framework for node-based campaigns, credential capture, SMTP delivery, CAPTCHA, and optional browser credential…
 g4lb1t/pstf2
Passive Security Tools Fingerprinting Framework
 jakabakos/cve-2023-36884-ms-office-html-rce
MS Office and Windows HTML RCE (CVE-2023-36884) - PoC and exploit
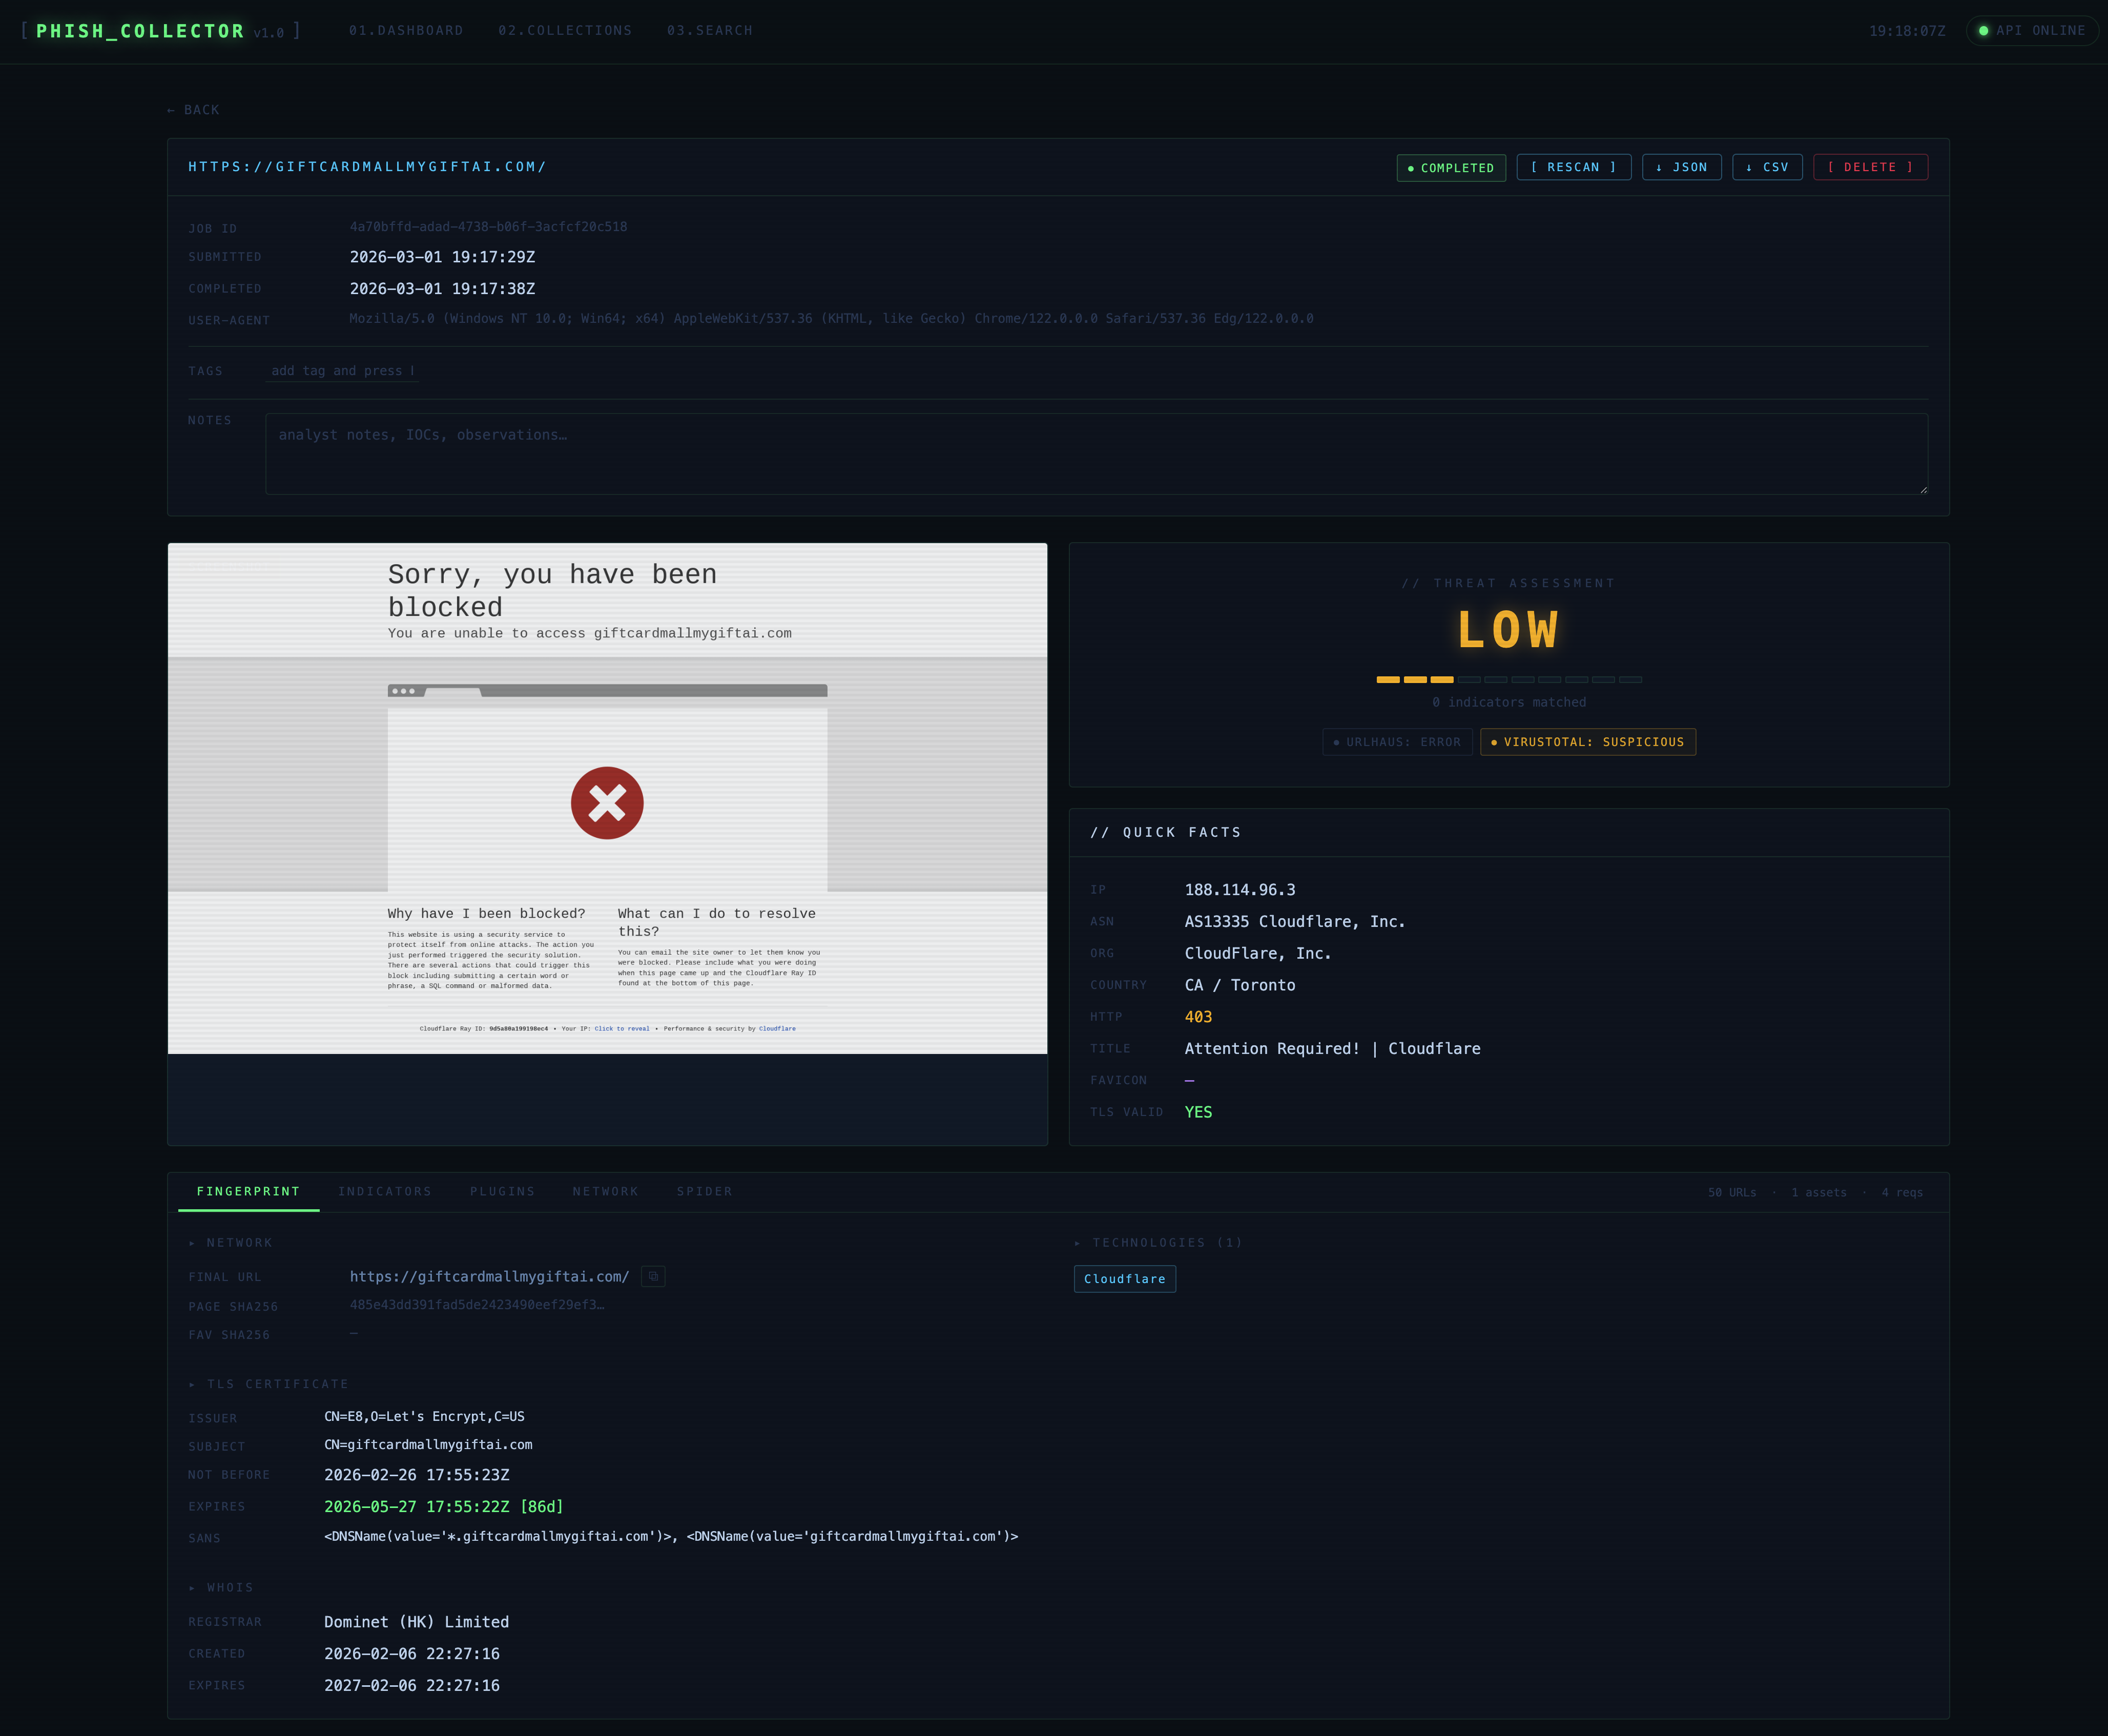 olizimmermann/phishcollector
PhishCollector is a research framework for collecting, analysing, and tracking phishing sites.
 alchemist3dot14/cve-2025-2783
Simulated PoC for CVE-2025-2783 — a sandbox escape vulnerability in Chrome's Mojo IPC. Includes phishing delivery, memory fuzzing, IPC simulation,…
 vighnesh91/severitas
Authorized social-engineering simulation framework with an isolated loopback lab, synthetic audience generation, pre-flight authorization checks, and…
 ahmetkarakayaoffical/cve-2024-21413-microsoft-outlook-remote-code-execution-vulnerability
Bu betik, Microsoft Outlook'ta keşfedilen ve CVSS değeri 9.8 olan önemli bir güvenlik açığı olan CVE-2024-21413 için bir kavram kanıtı (PoC)…
 unhackerencapital/pdfernetremotelo
PoC - Prueba de Concepto de CVE-2024-4367 en conjunto al CVE-2023-38831 en un solo Script
 hacky1997/cve-2020-8825
Proof-of-concept exploit for stored XSS vulnerability in VanillaForum 2.6.3, demonstrating arbitrary HTML/script injection via insufficient input…
 anupam2808/spy-masker
It is a simple Python Script to hide phishing URL under a normal looking URL (google.com or facebook.com). It can be integrated into Phishing tools…
 minhhk68/cve-2026-13156
CVE-2026-13156 Vulnerability Advisory & PoC — Discovered by Huynh Kien Minh (MinhHK).
 razureink/cve-2024-43451-ntlm_hash_disclosure_reproduction
CVE Reproduction: cve-2024-43451-ntlm_hash_disclosure_reproduction