
 wavvs/doctrack
Tool to manipulate and weaponize Office Open XML documents.
 chrismaddalena/cooper
A Python tool for ingesting HTML and producing HTML source suitable for phishing campaigns.
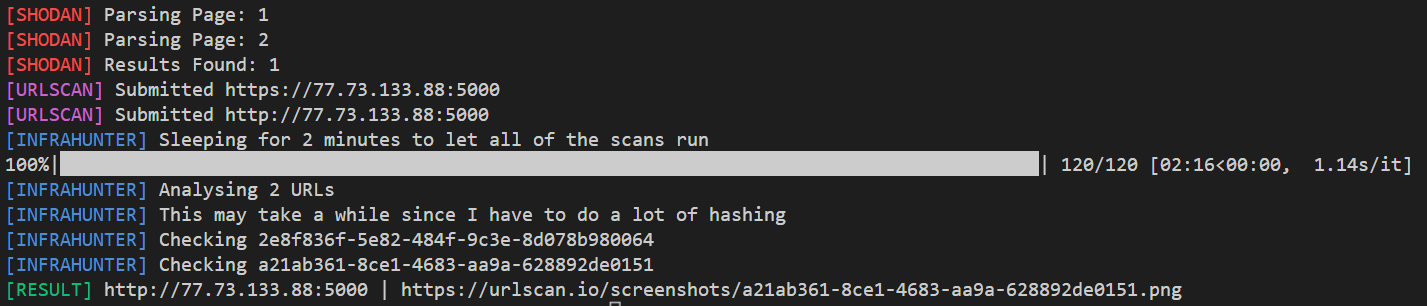 montysecurity/infrahunter
Actively hunt for attacker infrastructure by filtering Shodan results with URLScan data.
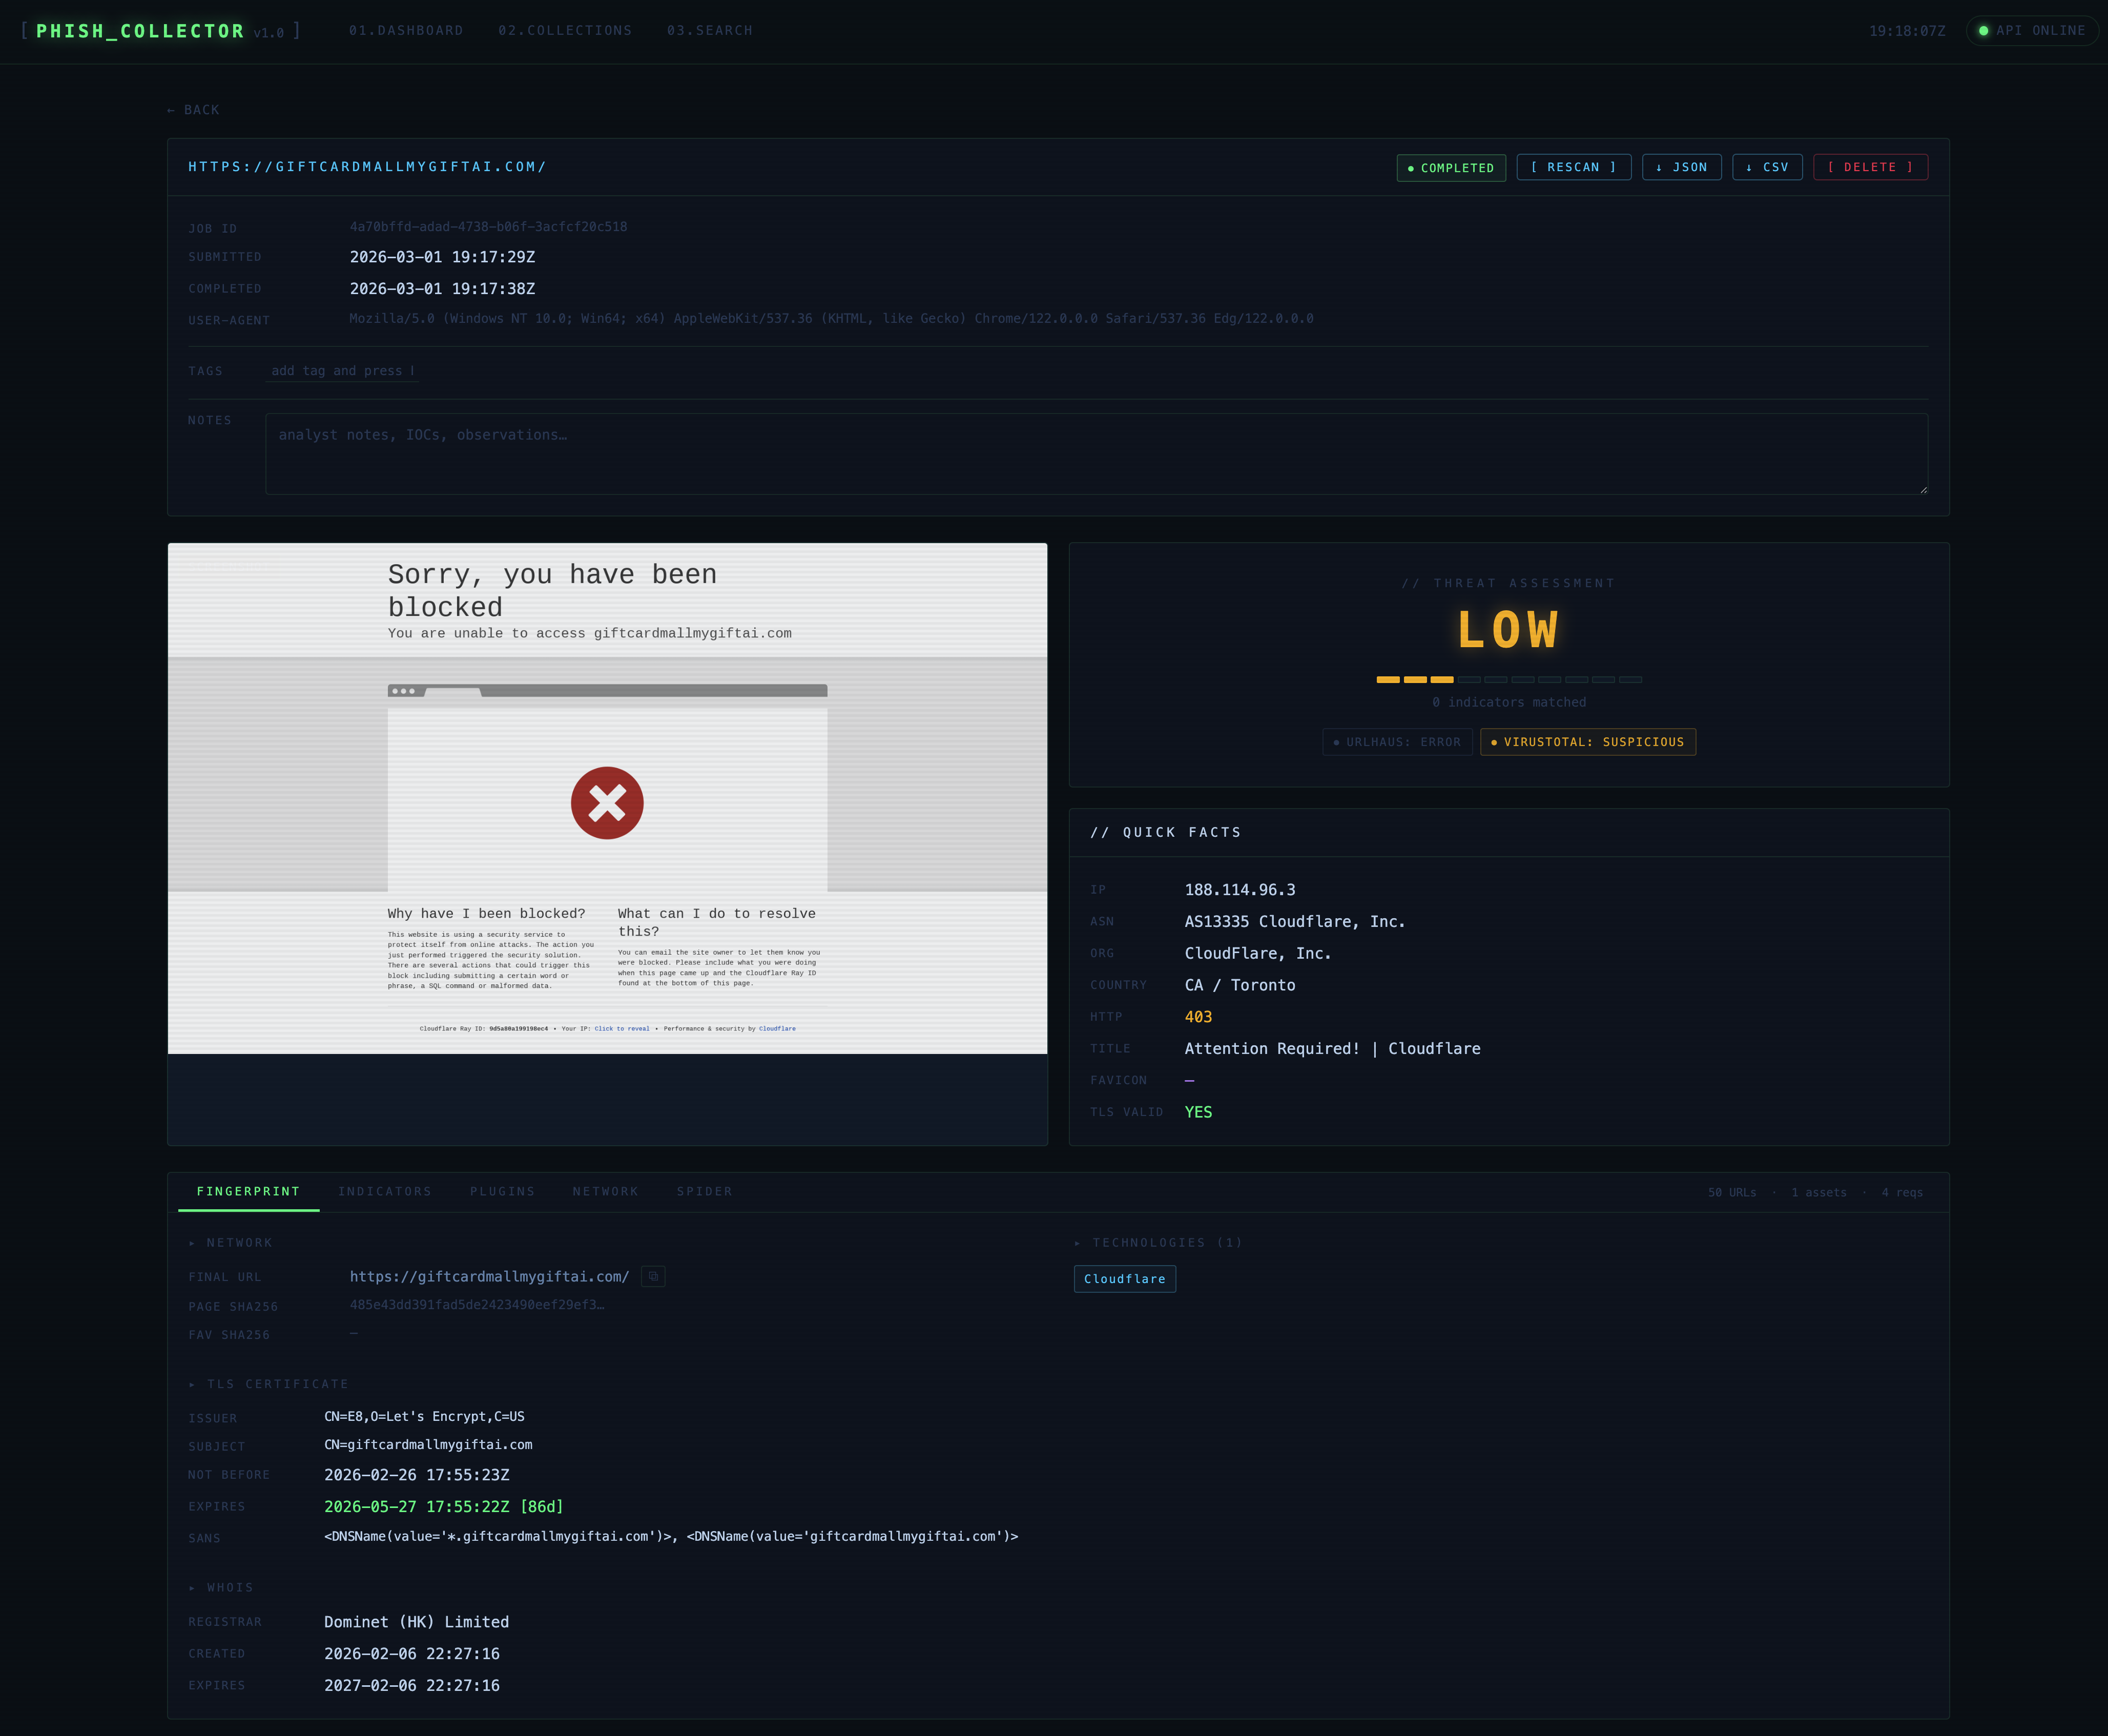 olizimmermann/phishcollector
PhishCollector is a research framework for collecting, analysing, and tracking phishing sites.
 elvira-alec/fracture
FragAttacks WiFi penetration framework — CVE-2020-24586/87/88
 bardlaudian/cve-2025-24071
Dependency-free Python PoC generator for CVE-2025-24071 that crafts a malicious .library-ms file in a ZIP to trigger Windows Explorer NTLM hash…
 frozenka/cve-2025-26318
POC CVE-2025-26318
 ronixxcybsec0101/cve-2025-25461
SeedDMS Stored Cross Site Scripting(XSS)
 cappricio-securities/socialengineering-templates
a SET framework templates
 samsayen/jqueryingu
Valid JQuery that profiles the system and returns info to the server in a fake analytics GET request
 spiralbl0ck/ios-safari-mallicous-extension-example
Example on how to injection(currently under work) of keylogger js through Safari Extension(that part done)
 urban4/cve-2022-3992
Cross Site Scripting on sanitization-management-system
 jaykali/lockphish
Lockphish it's the first tool (07/04/2020) for phishing attacks on the lock screen, designed to grab Windows credentials, Android PIN and iPhone…
 spiderlabs/responder
Responder is a LLMNR, NBT-NS and MDNS poisoner, with built-in HTTP/SMB/MSSQL/FTP/LDAP rogue authentication server supporting NTLMv1/NTLMv2/LMv2,…
 xdavidhu/mitmap
📡 A python program to create a fake AP and sniff data.
 life4/homoglyphs
Homoglyphs: get similar letters, convert to ASCII, detect possible languages and UTF-8 group.