
CVE-2026-32201-exploit
 b1tbit/cve-2026-32201-exploit
Python exploit for CVE-2026-32201, a reflected XSS in Microsoft SharePoint Server, enabling unauthenticated spoofing and data modification via…
exploitationpenetration-testingphishing-tools+3
1
b1tbit/cve-2026-32201-exploitPython exploit for CVE-2026-32201, a reflected XSS in Microsoft SharePoint Server, enabling unauthenticated spoofing and data modification via…
 ayato-shitomi/cve-2024-46278-teedy_1.11_account-takeover
【Teedy 1.11】Account Takeover via XSS
 cscli/cve-2017-5223
Proof-of-concept exploit for CVE-2017-5223 demonstrating arbitrary file read via PHPMailer's attachment and email content injection.
 minotauro2020/cve-2023-40869
Cross Site Scripting vulnerability in mooSocial mooSocial Software v.3.1.6 allows a remote attacker to execute arbitrary code via a crafted script to…
 mbanyamer/cve-2026-27579-collabplatform-appwrite-cors-misconfiguration
Exploit PoC for CVE-2026-27579, a CORS misconfiguration in Appwrite backend, demonstrating credentialed account data theft via malicious phishing…
 secsys-fdu/cve-2025-51863
Proof-of-concept for a Self-XSS vulnerability in ChatGPTUtil, demonstrating cookie theft and account hijacking via crafted SVG payloads pasted into…
 geozin/poc-cve-2018-25031
Proof-of-concept exploit for CVE-2018-25031 (Swagger UI XSS) that exfiltrates authorization codes via crafted configUrl/url parameters.
 mbadanoiu/cve-2020-13965
CVE-2020-13965: Cross-Site Scripting via Malicious XML Attachment in Roundcube Webmail
 leocottret/cve-2024-30956
(DOM-based XSS) HTML Injection vulnerability in TOWeb v.12.05 and before allows an attacker to inject HTML/JS code via the _message.html component.
 mandiant/reelphish
Real-time two-factor phishing tool that automates credential harvesting by intercepting credentials from a phishing site and submitting them to the…
 xdavidhu/langhost
👻 A LAN dropbox chatbot controllable via Telegram
 wireghoul/htshells
Self contained htaccess shells and attacks
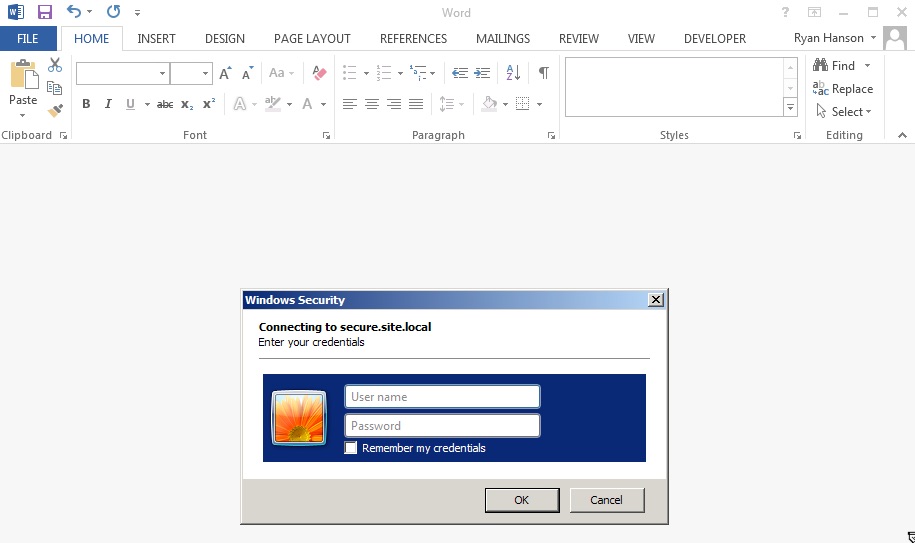 ryhanson/phishery
An SSL Enabled Basic Auth Credential Harvester with a Word Document Template URL Injector
 bronzebee/cve-2023-23397
Python script for sending e-mails with CVE-2023-23397 payload using SMTP
 kaihaochen04/monikerlinktest
cve-2024-21413
 urban4/cve-2022-3992
Cross Site Scripting on sanitization-management-system