
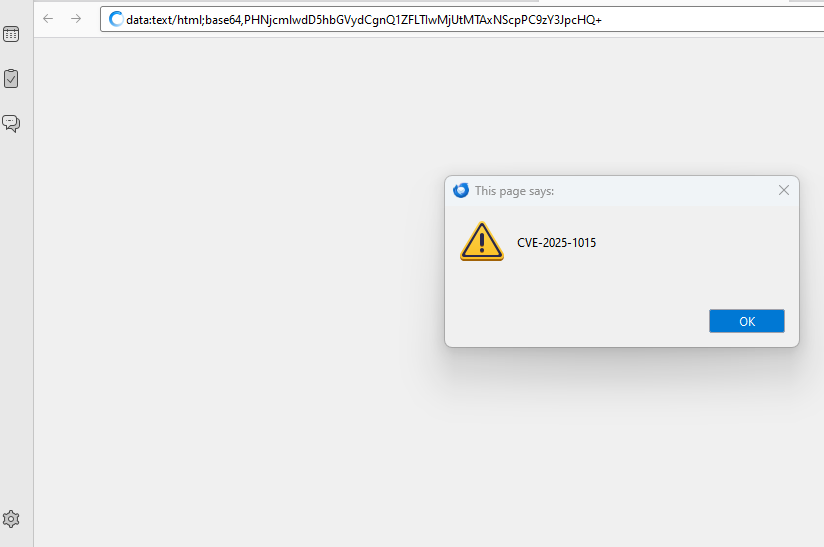
CVE-2025-1015
 r3m0t3nu11/cve-2025-1015
an attacker to create and export an address book containing a malicious payload in a field. For example, in the “Other” field of the Instant…
exploitationpayload-generationphishing-tools+3
3
r3m0t3nu11/cve-2025-1015an attacker to create and export an address book containing a malicious payload in a field. For example, in the “Other” field of the Instant…
 ash1996x/cve-2025-50154-aggressor-script
Cobalt Strike Aggressor script that weaponizes LNK and Library-MS files to trigger SMB NTLMv2 hash disclosure, including CVE-2025-24054 bypass, for…
 edu0x01/hack-tools
Project that brings together several pentest tools
 bhanunamikaze/cve-2024-42009
This Proof of Concept (PoC) demonstrates an exploit for CVE-2024-42009, leveraging a cross-site scripting (XSS) vulnerability to extract emails from…
 samsayen/jqueryingu
Valid JQuery that profiles the system and returns info to the server in a fake analytics GET request
 am0nt31r0/password-analysis
Script in Go that analyzes a list of passwords based on in its entropy and weak passwords from a dictionary. Useful for penetration tests and…
 geozin/poc-cve-2018-25031
Proof-of-concept exploit for CVE-2018-25031 (Swagger UI XSS) that exfiltrates authorization codes via crafted configUrl/url parameters.
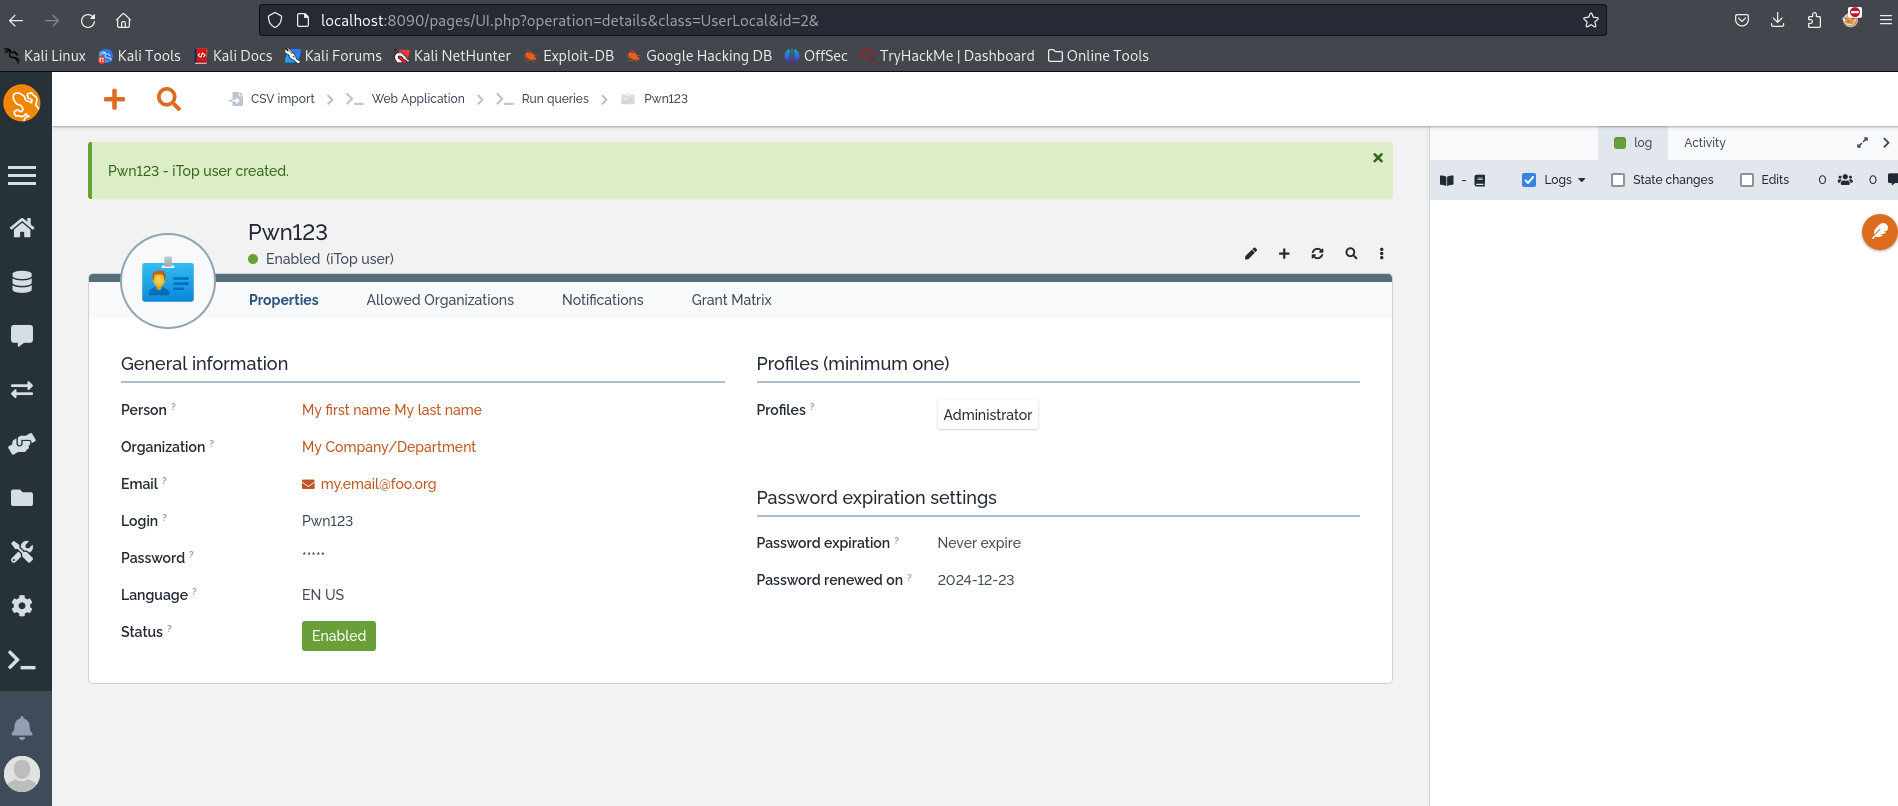 harshit-mashru/itop-cves-exploit
This repository contains exploits for iTOP CVE-2024-52002, 52000, 31998, 31448 that involve CSRF+XSS chaining to get RCE
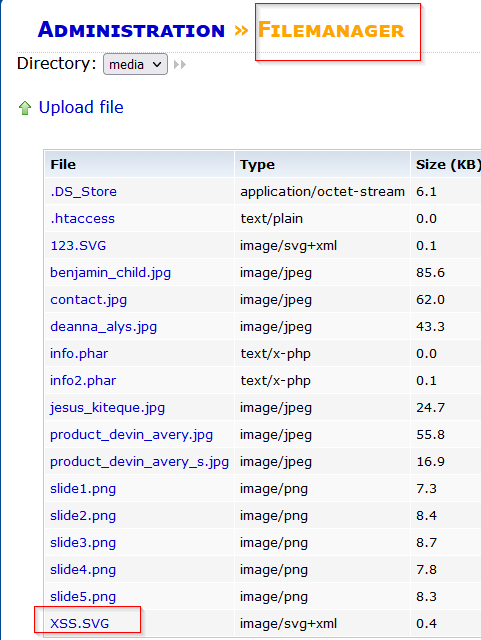 sromanhu/cve-2023-44767_ritecms-file-upload--xss---filemanager
RiteCMS 3.0 is affected by File Upload - XSS vulnerability that allows attackers to upload a PDF file with a hidden XSS that when executed will…
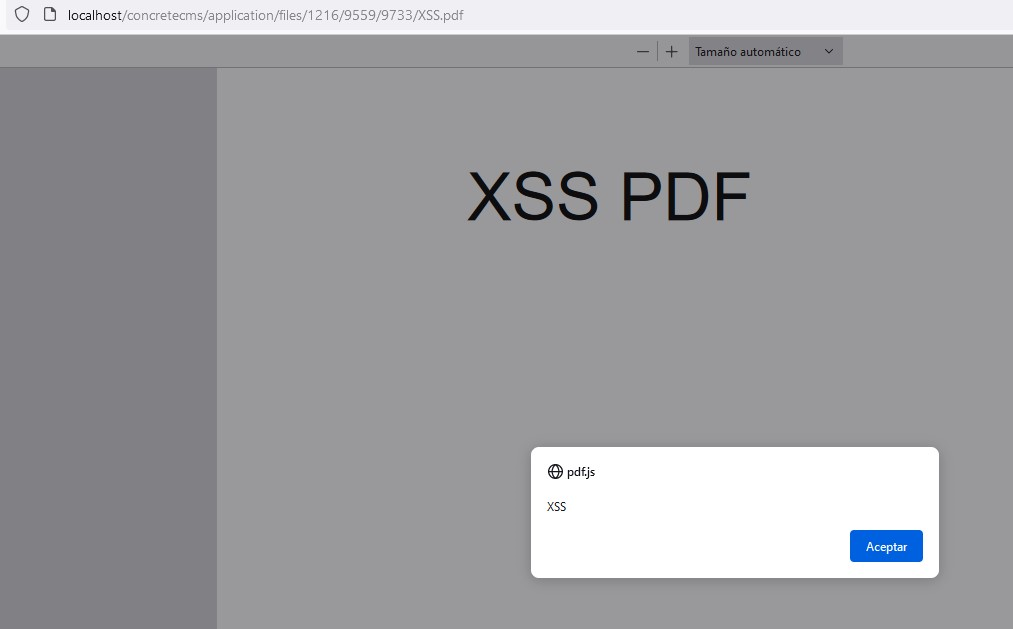 sromanhu/cve-2023-44763_concretecms-arbitrary-file-upload-thumbnail
ConcreteCMS v.9.2.1 is affected by Arbitrary File Upload vulnerability that allows Cross-Site Scriting (XSS) Stored.
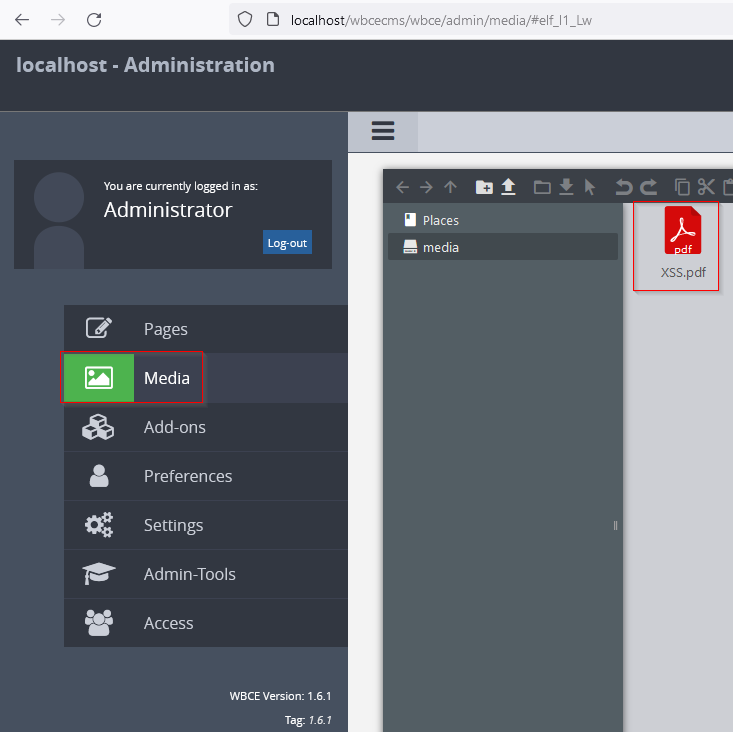 sromanhu/cve-2023-43871-wbce-arbitrary-file-upload--xss---media
WBCE 1.6.1 is affected by File Upload - XSS vulnerability that allows attackers to upload a PDF file with a hidden XSS that when executed will launch…
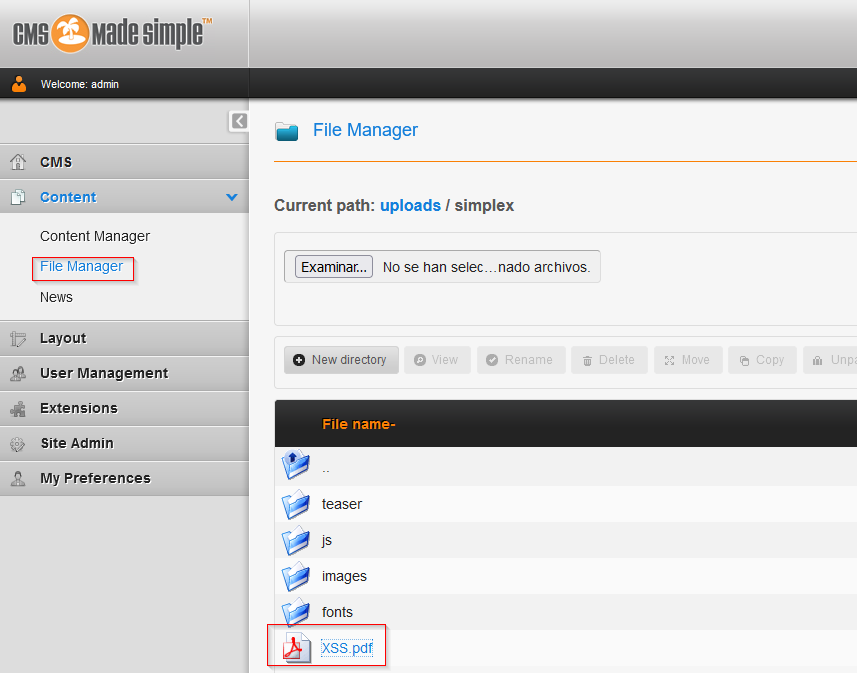 sromanhu/cve-2023-43872-cmsmadesimple-arbitrary-file-upload--xss---file-manager
CMSmadesimple 2.2.18 is affected by File Upload - XSS vulnerability that allows attackers to upload a PDF file with a hidden XSS that when executed…
 mandiant/reelphish
Real-time two-factor phishing tool that automates credential harvesting by intercepting credentials from a phishing site and submitting them to the…
 k4n3co/lab-rats-v1.6
Lab-RATS is a powerful and lightweight Android Remote Administration Tool full of features that enables remote monitoring, management and interaction…
 utkusen/socialhunter
crawls the website and finds broken social media links that can be hijacked
 drk1wi/modlishka
Modlishka. Reverse Proxy.
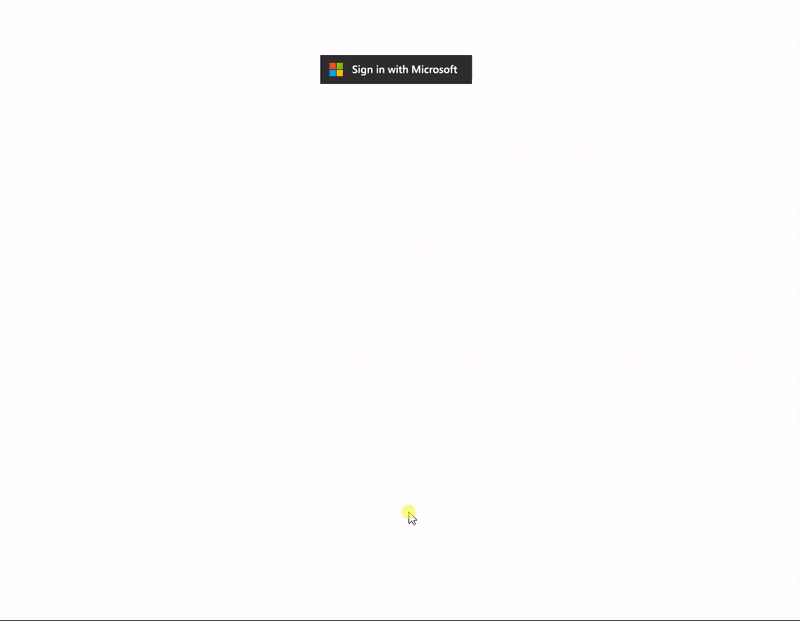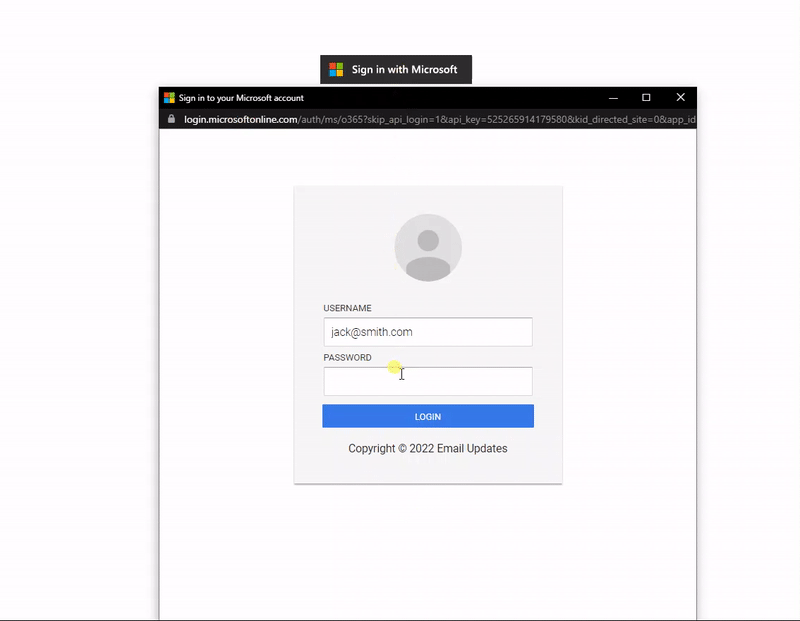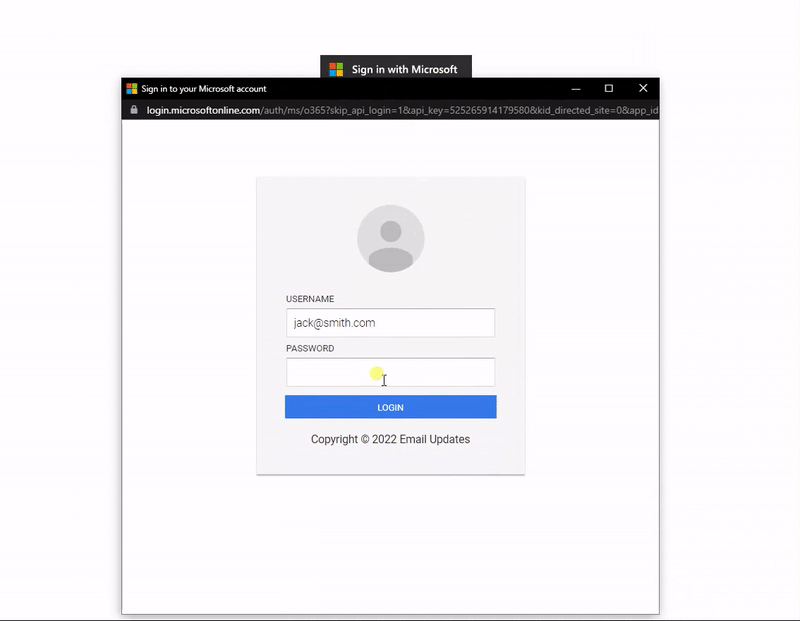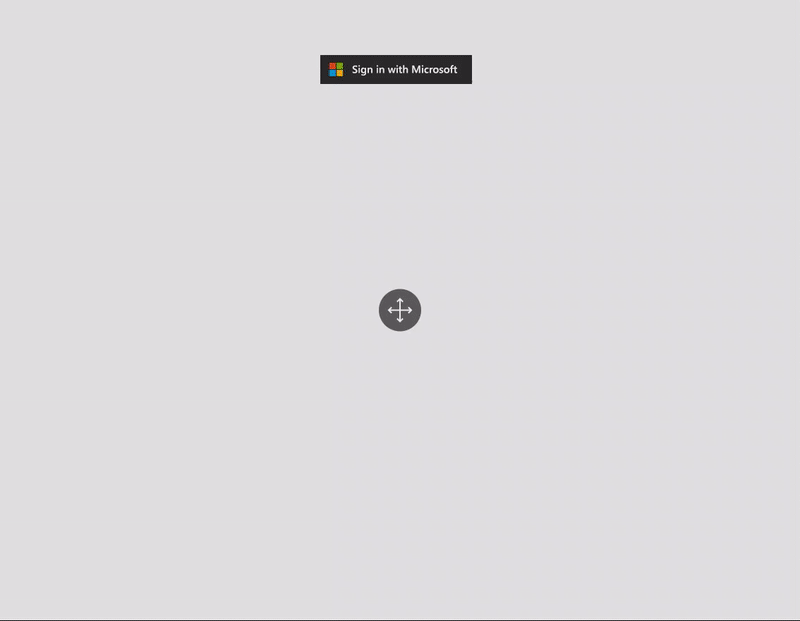 mrd0x/bitb
HTML/CSS/JS templates for Browser-In-The-Browser phishing attacks, embedding fake login windows with customizable titles, domains, and phishing links…
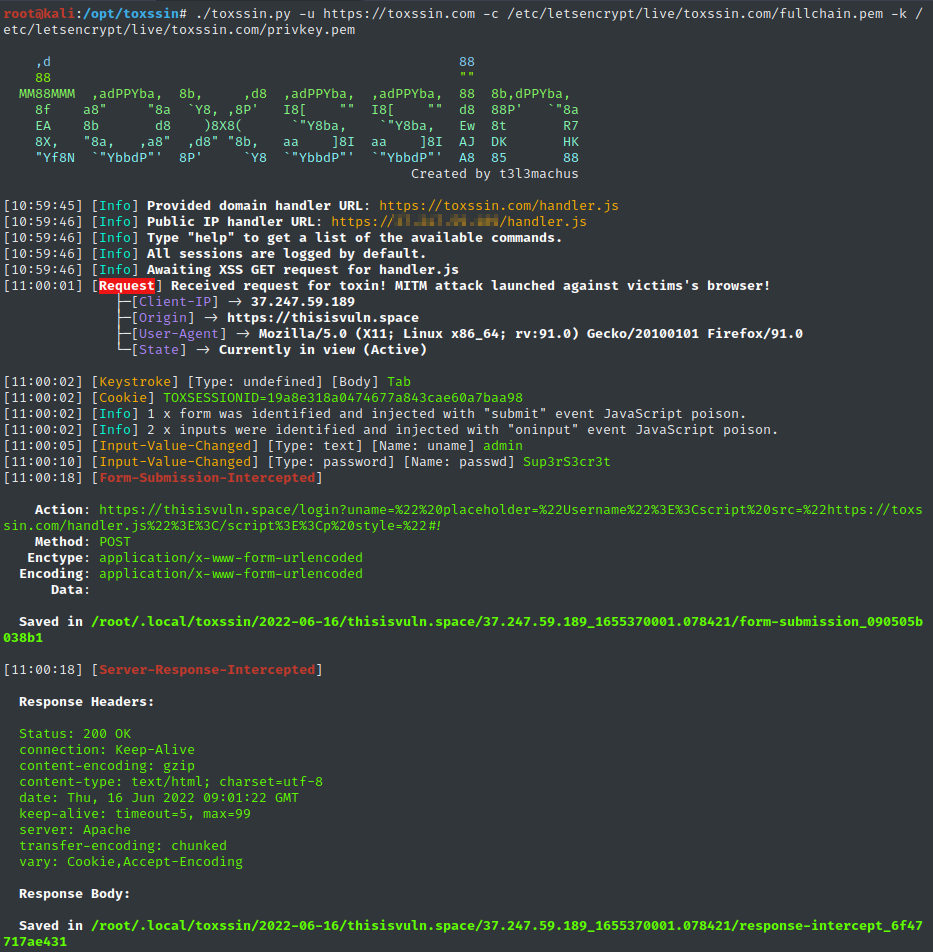 t3l3machus/toxssin
An XSS exploitation command-line interface and payload generator.