
SignHere
 retr0-code/signhere
SignHere is implementation of CVE-2017-11882. SignHere is builder of malicious rtf document and VBScript payloads.
command-and-controlexploitationpayload-generation+3
6
retr0-code/signhereSignHere is implementation of CVE-2017-11882. SignHere is builder of malicious rtf document and VBScript payloads.
 g33xter/cve-2021-28079
Proof-of-concept exploit for XSS vulnerability in Jamovi <=1.6.18. Demonstrates crafting malicious .omv documents with JavaScript payloads to achieve…
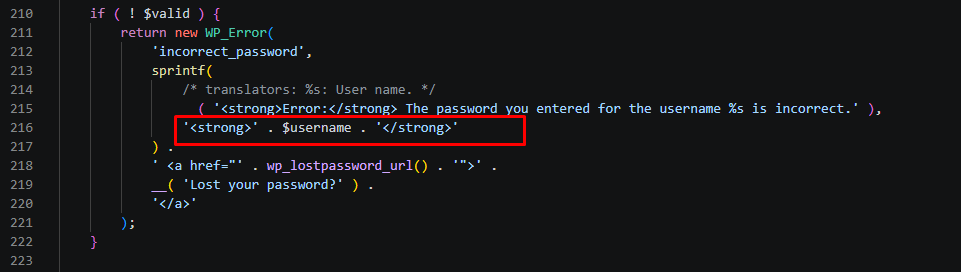 dungsocool/cve-2026-64638
Proof-of-concept exploit for CVE-2026-64638: reflected XSS in WordPress login chained with DOM clobbering to achieve admin account takeover and…
 mohwahyudi/poc-cve-2026-64638-
PoC exploit chain for WordPress pre-auth XSS to RCE via DOM clobbering, REST JSONP/SOME, and plugin upload, with Docker lab verification and…
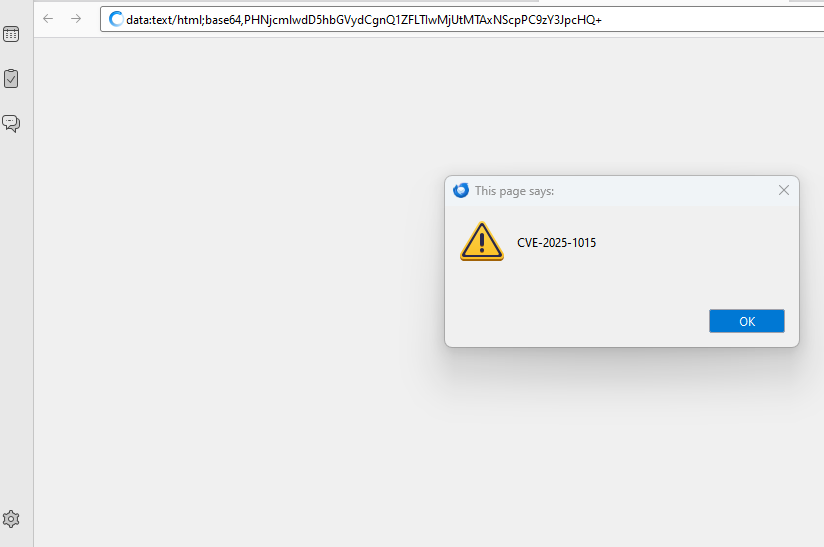 r3m0t3nu11/cve-2025-1015
an attacker to create and export an address book containing a malicious payload in a field. For example, in the “Other” field of the Instant…
 cesarbtakeda/7-zip-cve-2025-0411-poc
Proof-of-concept exploit for CVE-2025-0411, demonstrating Mark-of-the-Web bypass in 7-Zip to enable arbitrary code execution via crafted archives…

 jun2e0/cve-2025-26788
Proof-of-concept exploit for CVE-2025-26788 demonstrating WebAuthn credential ID manipulation via JavaScript hooking to bypass authentication in…
 s1lkys/cve-2021-24884
If an authenticated user who is able to edit Wordpress PHP code in any kind, clicks a malicious link, PHP code can be edited through XSS in…
 raffli-dev/cve-2023-41425
Exploit for Wonder CMS XSS to RCE (CVE-2023-41425) with theme upload and reverse shell payloads.
 zzn1nj4/cve-2025-22131-poc
PoC for CVE-2025-22131
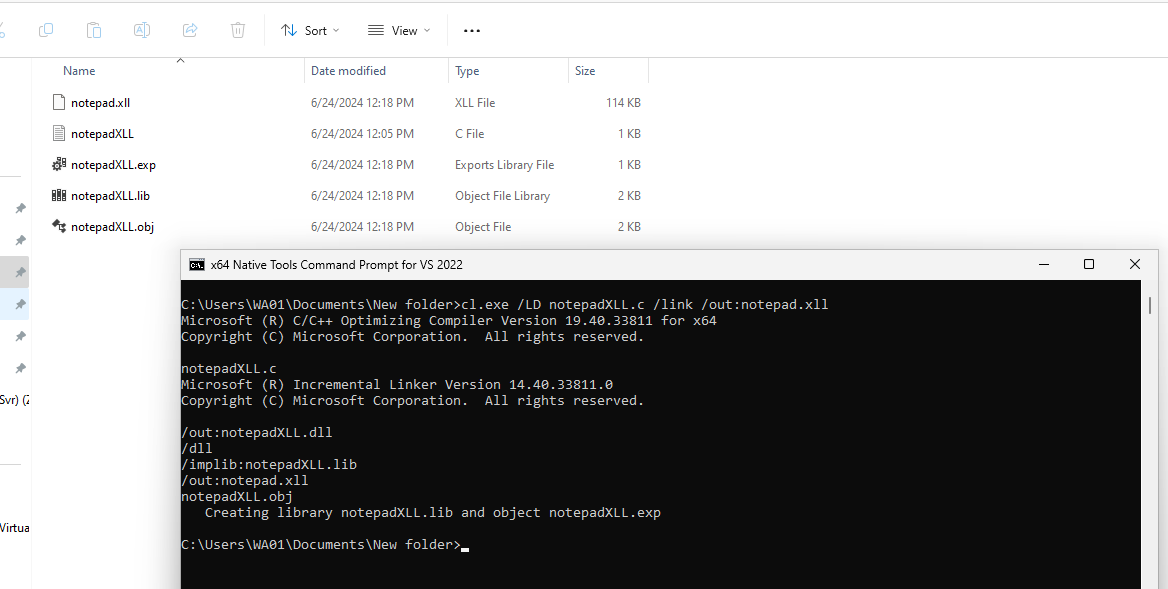 h3x0v3rl0rd/xll_windows_reverse_shell
xll windows reverse shell
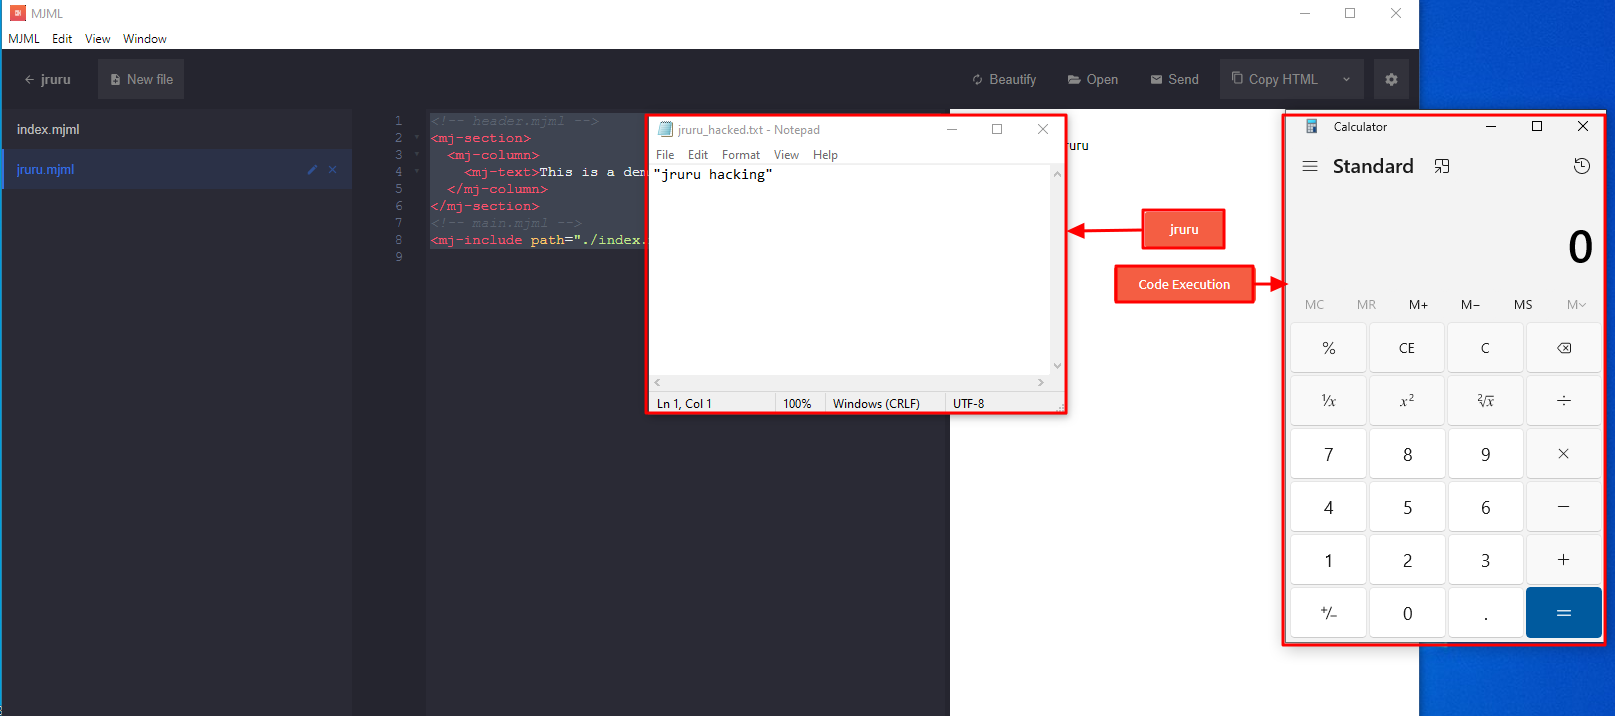 eqstlab/cve-2024-25293
mjml-app v3.0.4 & 3.1.0-beta RCE exploit
 sromanhu/cve-2023-44763_concretecms-arbitrary-file-upload-thumbnail
ConcreteCMS v.9.2.1 is affected by Arbitrary File Upload vulnerability that allows Cross-Site Scriting (XSS) Stored.
 shaheeryasirofficial/smugglemypayload
Generates HTML smuggling pages that embed and reconstruct files client-side via JavaScript, with payload encoding, chunking, obfuscation, and…