
CVE-2023-33977
 mnqazi/cve-2023-33977
Read more at Medium
exploitationphishing-toolsvulnerability-analysis+2
mnqazi/cve-2023-33977Read more at Medium
 sromanhu/cve-2023-44763_concretecms-arbitrary-file-upload-thumbnail
ConcreteCMS v.9.2.1 is affected by Arbitrary File Upload vulnerability that allows Cross-Site Scriting (XSS) Stored.
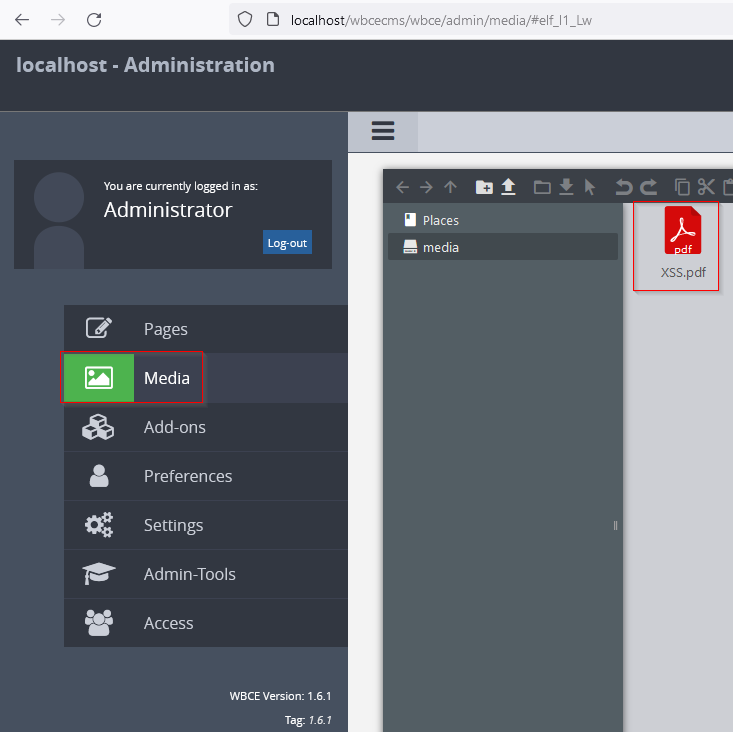 sromanhu/cve-2023-43871-wbce-arbitrary-file-upload--xss---media
WBCE 1.6.1 is affected by File Upload - XSS vulnerability that allows attackers to upload a PDF file with a hidden XSS that when executed will launch…
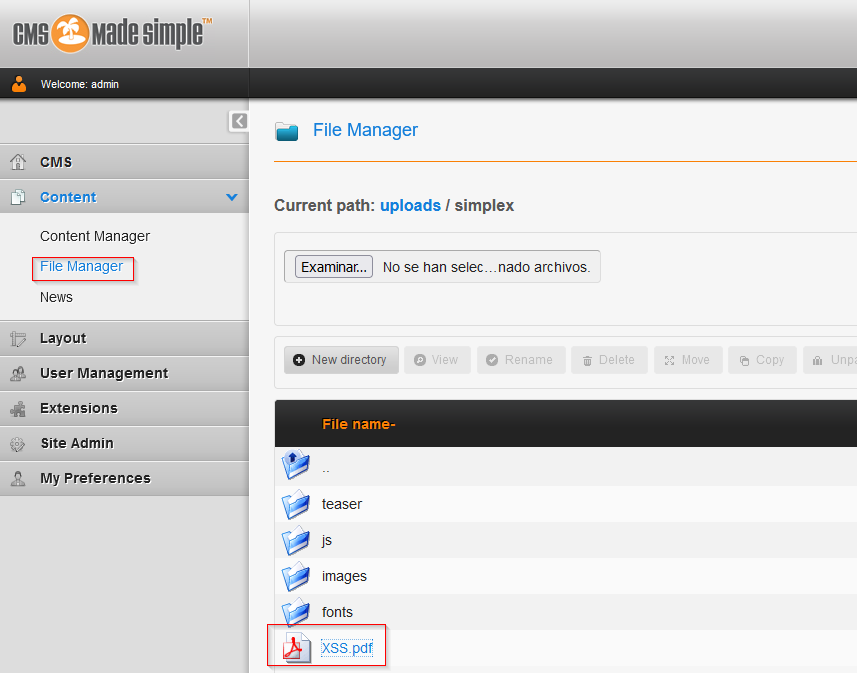 sromanhu/cve-2023-43872-cmsmadesimple-arbitrary-file-upload--xss---file-manager
CMSmadesimple 2.2.18 is affected by File Upload - XSS vulnerability that allows attackers to upload a PDF file with a hidden XSS that when executed…
 htr-tech/fake-mailer
Send Mail Anonymously with this Script
 byt3bl33d3r/spamchannel
Spoof emails from any of the +2 Million domains using MailChannels (DEFCON 31 Talk)
 warhorse/warhorse
Infrastructure Automation
 curi0usjack/luckystrike
A PowerShell based utility for the creation of malicious Office macro documents.
 mehulj94/radium
Python logger with multiple features.