

CVE-2021-40101
 s1lkys/cve-2021-40101
Survey XSS combined with CSRF leads to Admin Account Takeover in Concrete5 8.5.4
exploitationpenetration-testingphishing-tools+3
1
s1lkys/cve-2021-40101Survey XSS combined with CSRF leads to Admin Account Takeover in Concrete5 8.5.4
 zumiyumi/cve-2024-50677
This repository presents a proof-of-concept of CVE-2024-50677
 bhanunamikaze/cve-2024-42009
This Proof of Concept (PoC) demonstrates an exploit for CVE-2024-42009, leveraging a cross-site scripting (XSS) vulnerability to extract emails from…
 ayato-shitomi/cve-2024-46278-teedy_1.11_account-takeover
【Teedy 1.11】Account Takeover via XSS
 oscarakaelvis/cve-2018-8062
Persistent XSS on Comtrend AR-5387un router
 mexeck88/csrf-via-stored-xss-for-privesc
Chamilo-LMS (v2.0) CVE-2025-26153
 mbanyamer/cve-2026-27579-collabplatform-appwrite-cors-misconfiguration
Exploit PoC for CVE-2026-27579, a CORS misconfiguration in Appwrite backend, demonstrating credentialed account data theft via malicious phishing…
 relichunt3r/swagger-ui
Swagger UI (CVE-2018-25031) POC, [HTMLi, XSS].
 reggyraider/cve-2023-21716
CVE-2023-21716 - Microsoft Word RTF fonttbl Heap Corruption RCE exploit with reverse shell payload
 0pts/cve-2023-0214
Secure Web Gateway 10.2.11 - Cross-Site Scripting (XSS)
 sanupl/letterpress-1.2.1-open-redirection-via-html-injection-vulnerability
In LetterPress plugin <= 1.2.1 is vulnerable to Html Injection Vulnerability which can futher leads to Open Redirection Vulnerabilty.
 amirzargham/cve-2024-37383-exploit
Roundcube mail server exploit for CVE-2024-37383 (Stored XSS)
 geozin/poc-cve-2018-25031
Proof-of-concept exploit for CVE-2018-25031 (Swagger UI XSS) that exfiltrates authorization codes via crafted configUrl/url parameters.
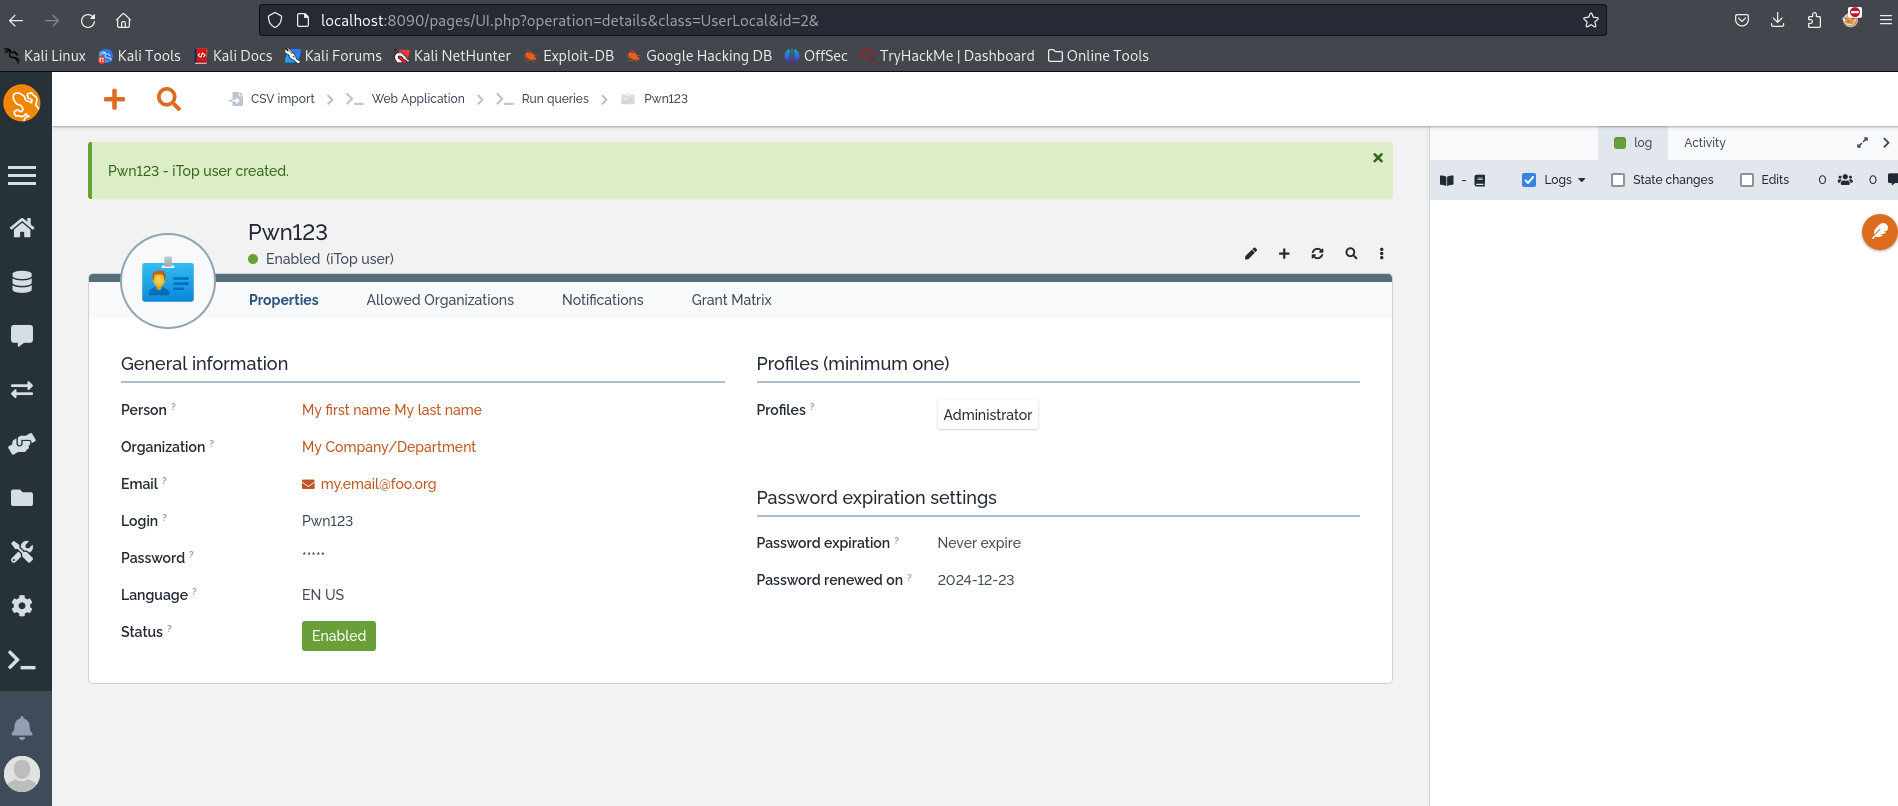 harshit-mashru/itop-cves-exploit
This repository contains exploits for iTOP CVE-2024-52002, 52000, 31998, 31448 that involve CSRF+XSS chaining to get RCE
 cyber-wo0dy/cve-2023-49052
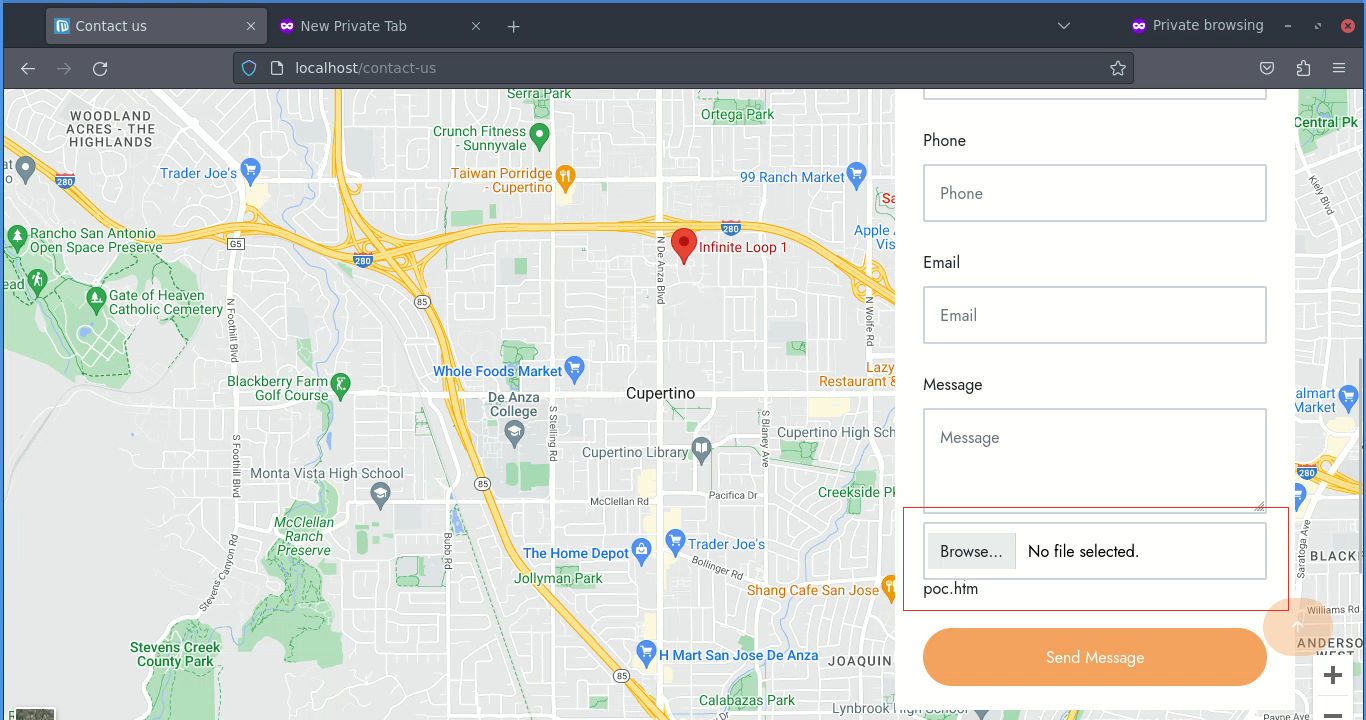
Microweber version 2.0.4 vulnerable to "Uploading Malicious Files"
 eqstlab/cve-2024-25293
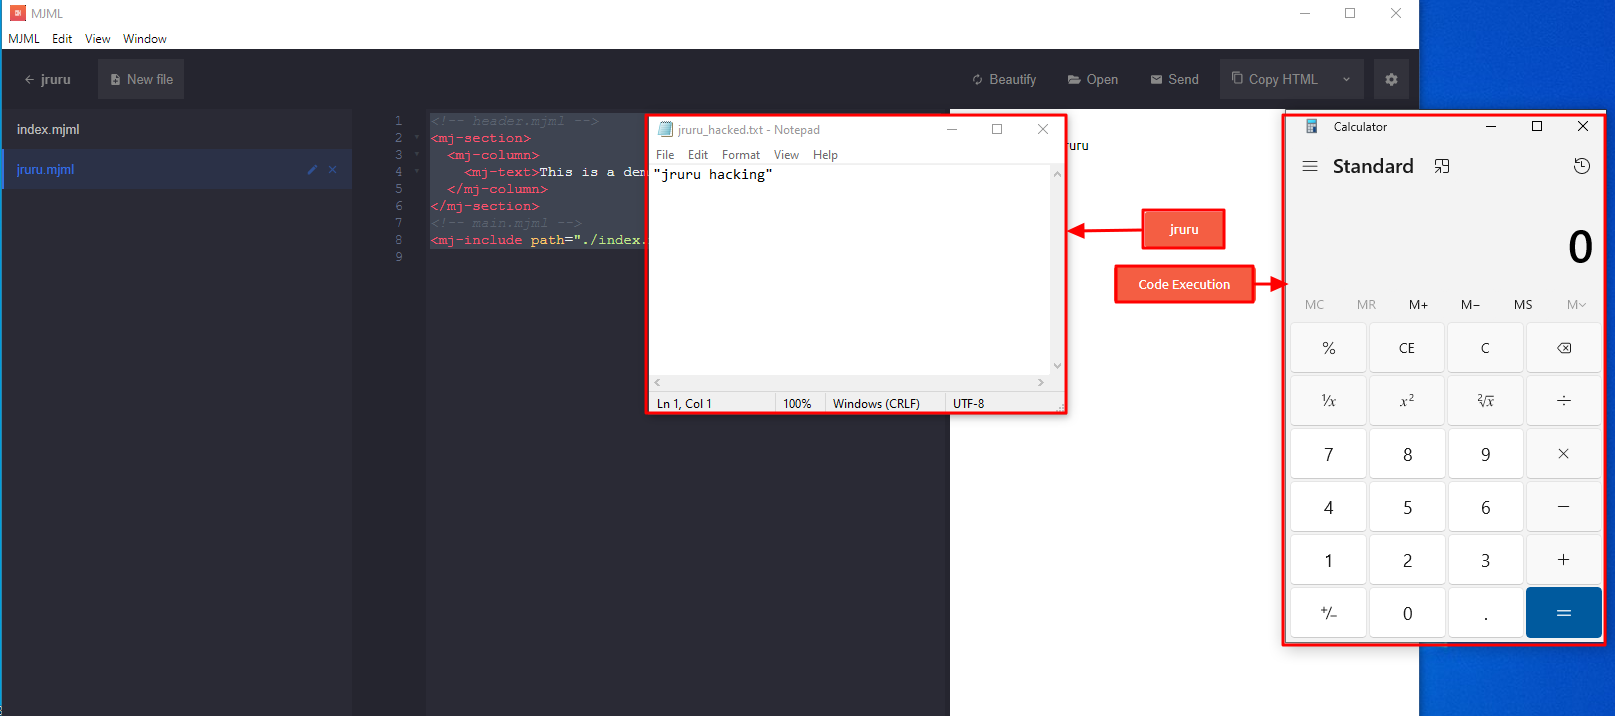
mjml-app v3.0.4 & 3.1.0-beta RCE exploit
 mnqazi/cve-2023-33977
Read more at Medium
 sromanhu/cve-2023-44763_concretecms-arbitrary-file-upload-thumbnail
ConcreteCMS v.9.2.1 is affected by Arbitrary File Upload vulnerability that allows Cross-Site Scriting (XSS) Stored.