
CVE-2024-30956
 leocottret/cve-2024-30956
(DOM-based XSS) HTML Injection vulnerability in TOWeb v.12.05 and before allows an attacker to inject HTML/JS code via the _message.html component.
exploitationphishing-toolssocial-engineering+2
leocottret/cve-2024-30956(DOM-based XSS) HTML Injection vulnerability in TOWeb v.12.05 and before allows an attacker to inject HTML/JS code via the _message.html component.
 urban4/cve-2022-3992
Cross Site Scripting on sanitization-management-system
 sromanhu/cve-2023-43872-cmsmadesimple-arbitrary-file-upload--xss---file-manager
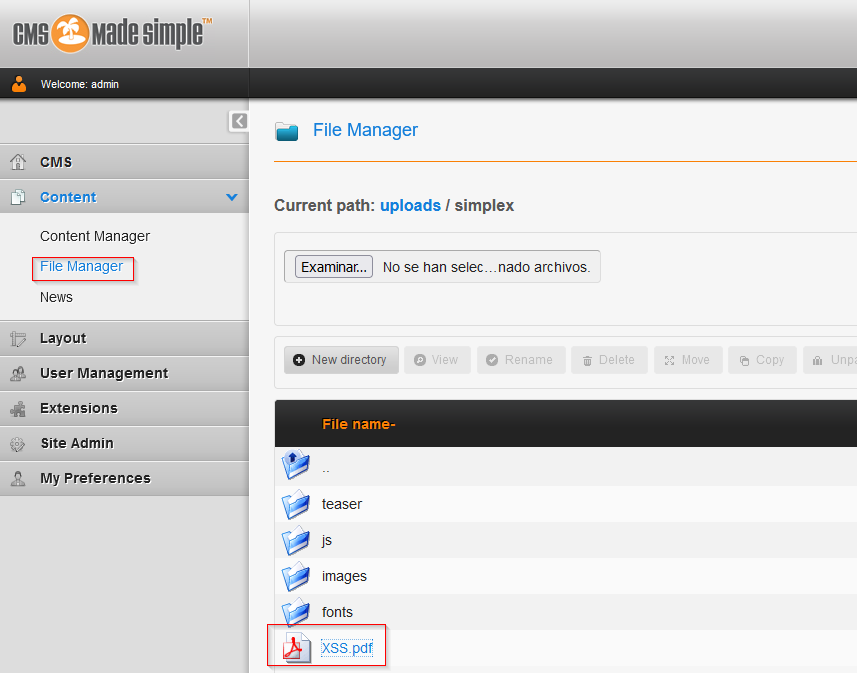
CMSmadesimple 2.2.18 is affected by File Upload - XSS vulnerability that allows attackers to upload a PDF file with a hidden XSS that when executed…
 jaykali/lockphish
Lockphish it's the first tool (07/04/2020) for phishing attacks on the lock screen, designed to grab Windows credentials, Android PIN and iPhone…
 arismelachroinos/lscript
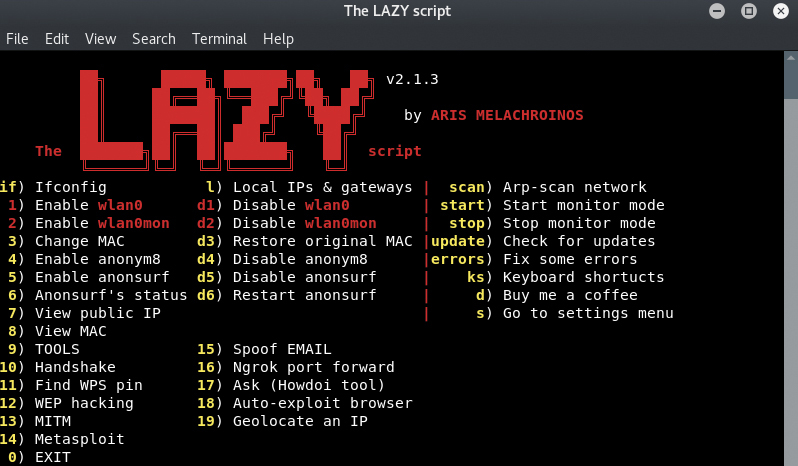
The LAZY script will make your life easier, and of course faster.
 th3unkn0n/telegram-scraper
telegram group scraper tool. fetch all information about group members