
CVE-2018-8062
 oscarakaelvis/cve-2018-8062
Persistent XSS on Comtrend AR-5387un router
exploitationpenetration-testingphishing-tools+3
12 years ago
oscarakaelvis/cve-2018-8062Persistent XSS on Comtrend AR-5387un router
 minotauro2020/cve-2023-40869
Cross Site Scripting vulnerability in mooSocial mooSocial Software v.3.1.6 allows a remote attacker to execute arbitrary code via a crafted script to…
 mexeck88/csrf-via-stored-xss-for-privesc
Chamilo-LMS (v2.0) CVE-2025-26153
 mbanyamer/cve-2026-27579-collabplatform-appwrite-cors-misconfiguration
Exploit PoC for CVE-2026-27579, a CORS misconfiguration in Appwrite backend, demonstrating credentialed account data theft via malicious phishing…
 zzn1nj4/cve-2025-22131-poc
PoC for CVE-2025-22131
 roj1py/cve-2024-47875-phpspreadsheet-xss-poc
This is a PoC/Exploit for the CVE-2024-47875 PhpSpreadsheet XSS Vuln
 reggyraider/cve-2023-21716
CVE-2023-21716 - Microsoft Word RTF fonttbl Heap Corruption RCE exploit with reverse shell payload
 shacode/olyx
🔗 Lightweight security orchestrator mobile application for URI vetting, providing a unified, multi-engine interface to aggregate and validate link…
 openxp-research/cve-2022-2546
All-in-One WP Migration < 7.63 - Unauthenticated Reflected XSS + CSRF
 secsys-fdu/cve-2025-51863
Proof-of-concept for a Self-XSS vulnerability in ChatGPTUtil, demonstrating cookie theft and account hijacking via crafted SVG payloads pasted into…
 samsayen/jqueryingu
Valid JQuery that profiles the system and returns info to the server in a fake analytics GET request
 gmh5225/fullscreenbrowserphishing
PoC of the phishing through setting browser in the fullscreen mode
 sanupl/letterpress-1.2.1-open-redirection-via-html-injection-vulnerability
In LetterPress plugin <= 1.2.1 is vulnerable to Html Injection Vulnerability which can futher leads to Open Redirection Vulnerabilty.
 amirzargham/cve-2024-37383-exploit
Roundcube mail server exploit for CVE-2024-37383 (Stored XSS)
 am0nt31r0/password-analysis
Script in Go that analyzes a list of passwords based on in its entropy and weak passwords from a dictionary. Useful for penetration tests and…
 geozin/poc-cve-2018-25031
Proof-of-concept exploit for CVE-2018-25031 (Swagger UI XSS) that exfiltrates authorization codes via crafted configUrl/url parameters.
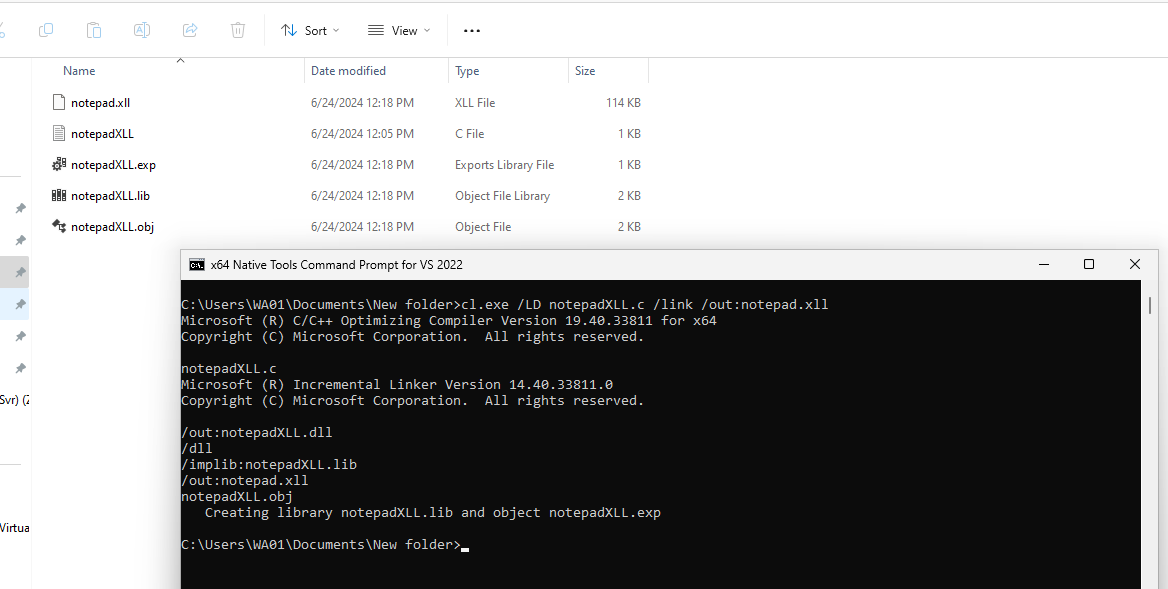 h3x0v3rl0rd/xll_windows_reverse_shell
xll windows reverse shell
 spiralbl0ck/ios-safari-mallicous-extension-example
Example on how to injection(currently under work) of keylogger js through Safari Extension(that part done)