
CVE-2024-37383-exploit
 amirzargham/cve-2024-37383-exploit
Roundcube mail server exploit for CVE-2024-37383 (Stored XSS)
data-exfiltrationemail-securityexploitation+3
amirzargham/cve-2024-37383-exploitRoundcube mail server exploit for CVE-2024-37383 (Stored XSS)
 undeadsec/socialfish
Modern dynamic phishing toolkit for authorized red team exercises. Clones login pages, captures credentials, cookies, and 2FA codes with a live…
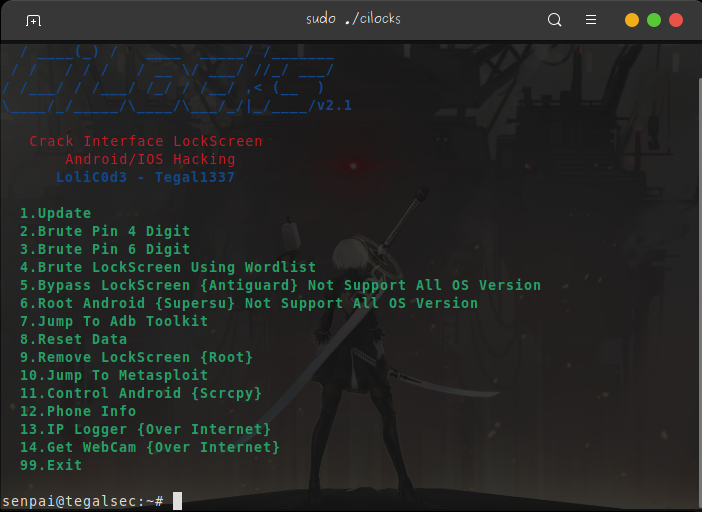 tegal1337/cilocks
Crack Interface lockscreen, Metasploit and More Android/IOS Hacking
 makdosx/mip22
Advanced phishing framework with 83 pre-built cloned websites, manual site cloning, URL masking, and real-time credential capture with audio…
 duy-31/cve-2024-21413
Microsoft Outlook Information Disclosure Vulnerability (leak password hash) - Expect Script POC
 trustedsec/reel
Phishing simulation and awareness framework for node-based campaigns, credential capture, SMTP delivery, CAPTCHA, and optional browser credential…
 jakabakos/cve-2023-36884-ms-office-html-rce
MS Office and Windows HTML RCE (CVE-2023-36884) - PoC and exploit
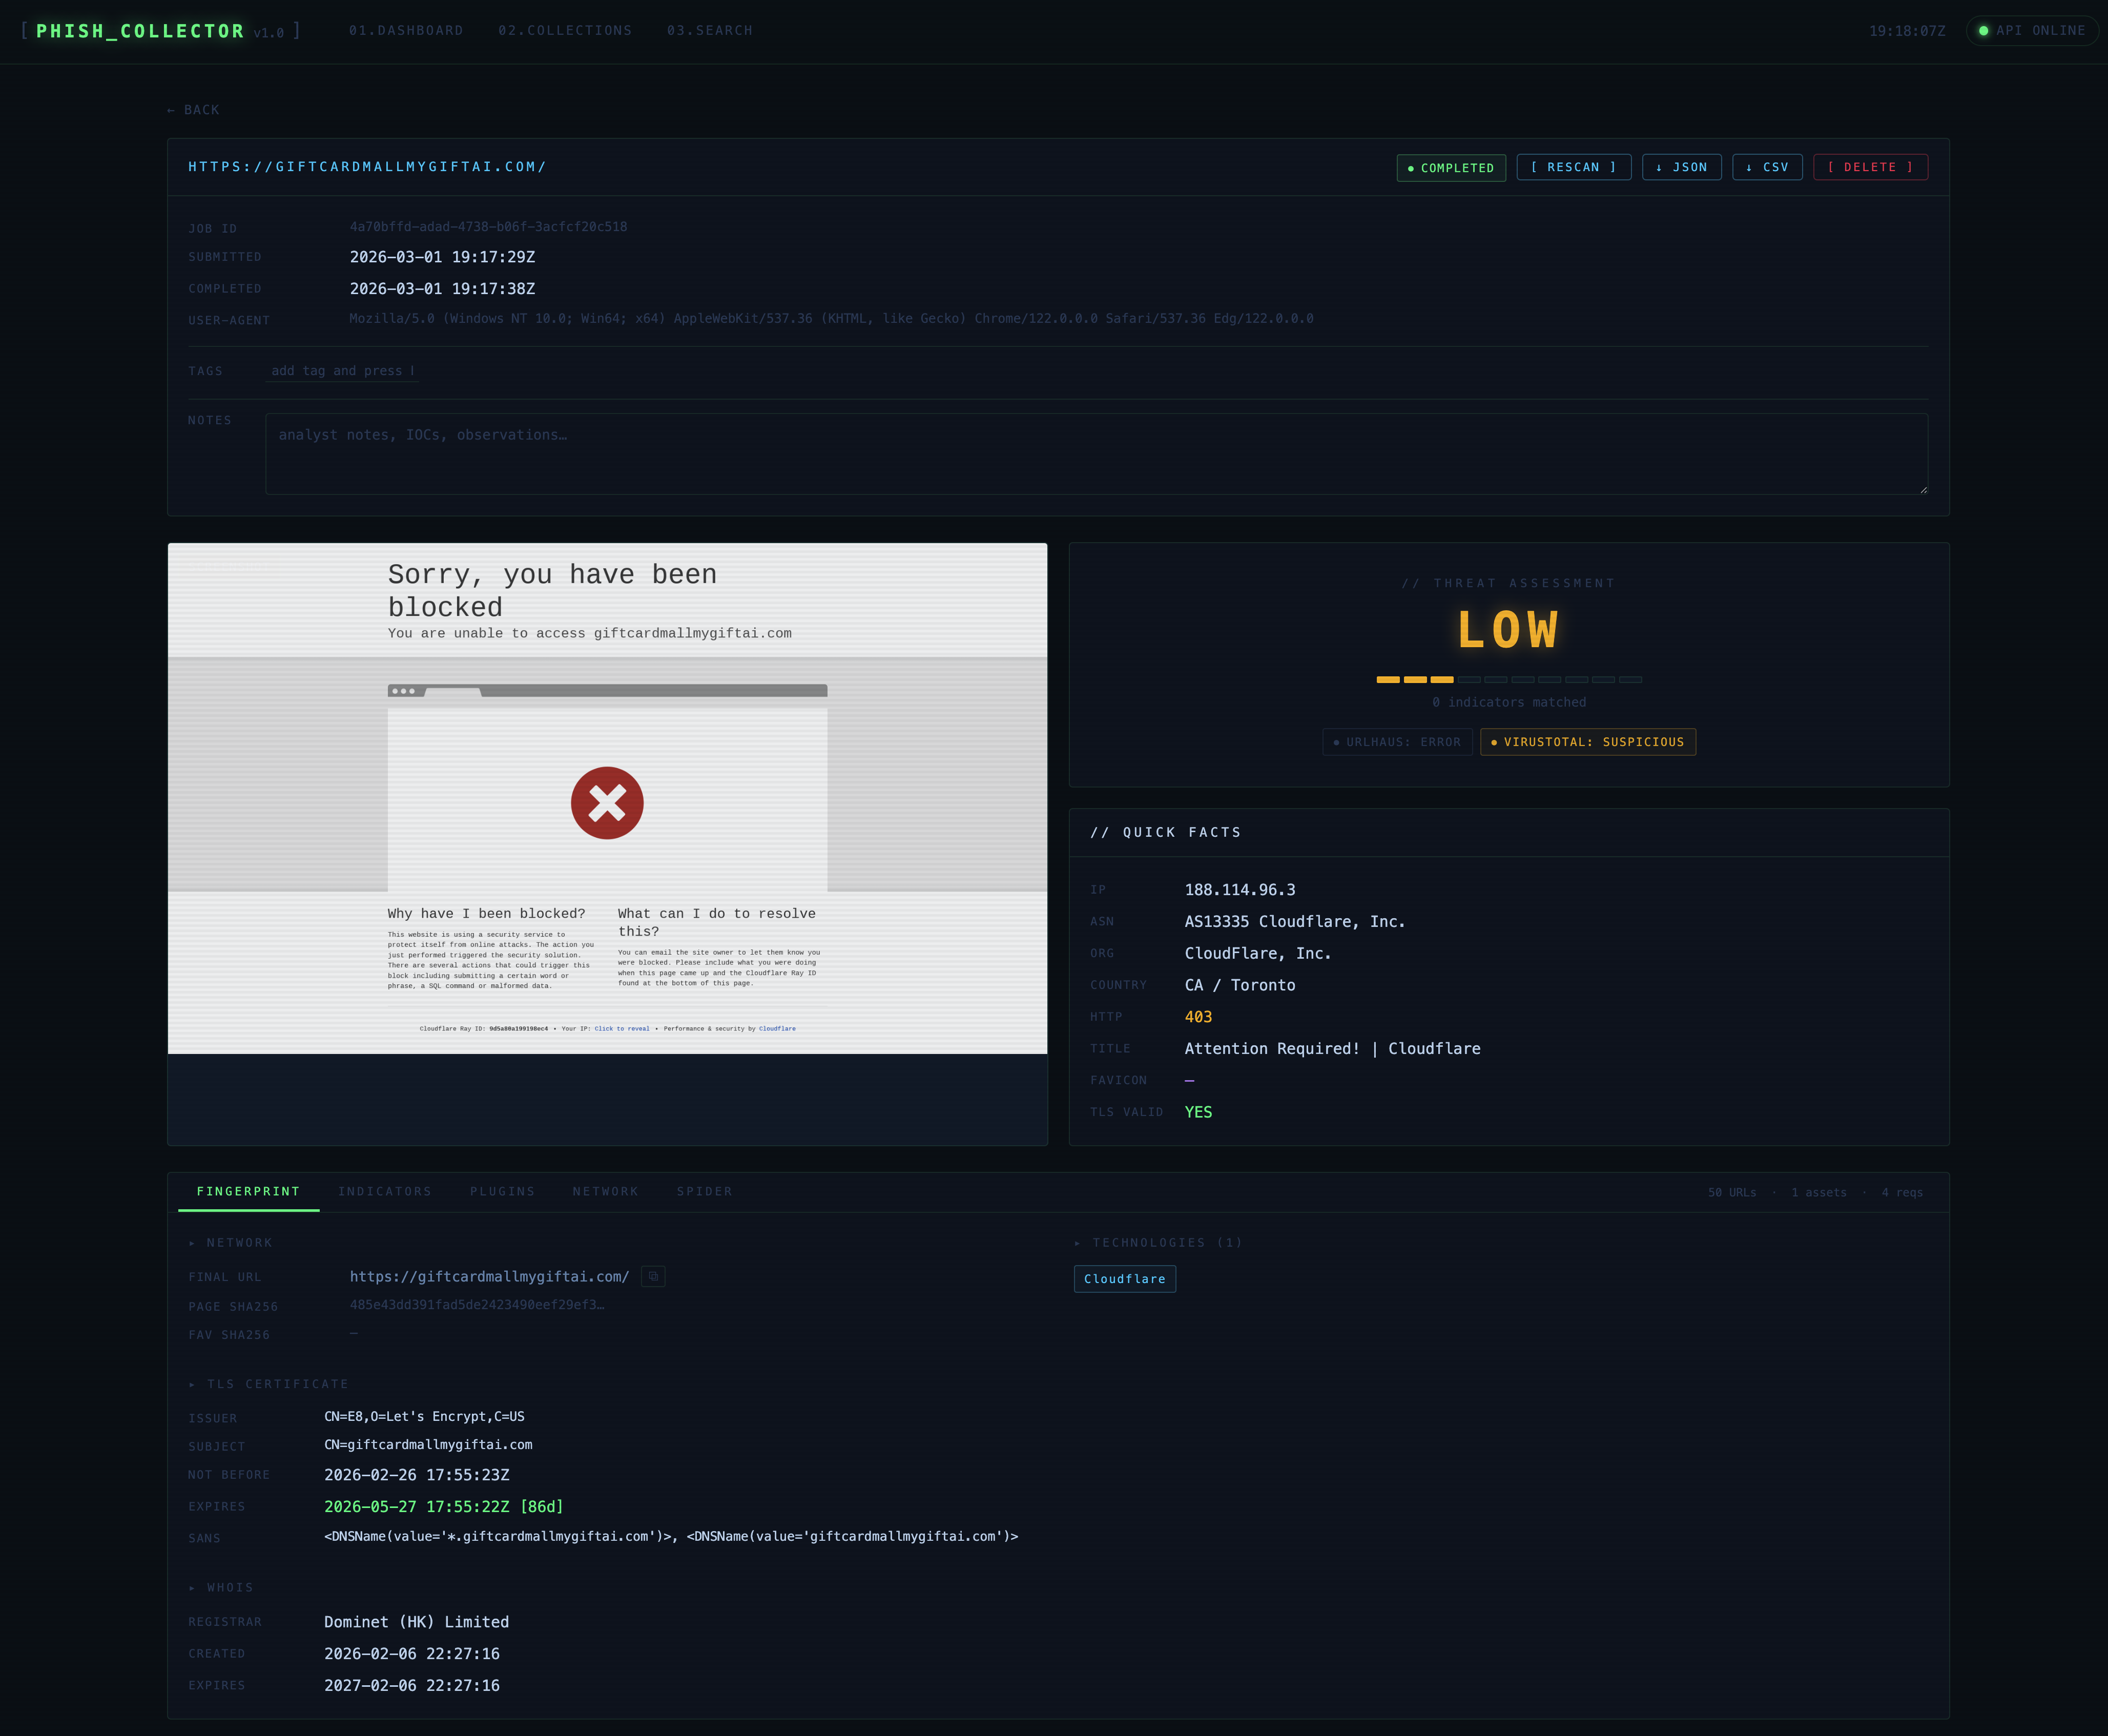 olizimmermann/phishcollector
PhishCollector is a research framework for collecting, analysing, and tracking phishing sites.
 alchemist3dot14/cve-2025-2783
Simulated PoC for CVE-2025-2783 — a sandbox escape vulnerability in Chrome's Mojo IPC. Includes phishing delivery, memory fuzzing, IPC simulation,…
 ahmetkarakayaoffical/cve-2024-21413-microsoft-outlook-remote-code-execution-vulnerability
Bu betik, Microsoft Outlook'ta keşfedilen ve CVSS değeri 9.8 olan önemli bir güvenlik açığı olan CVE-2024-21413 için bir kavram kanıtı (PoC)…
 unhackerencapital/pdfernetremotelo
PoC - Prueba de Concepto de CVE-2024-4367 en conjunto al CVE-2023-38831 en un solo Script
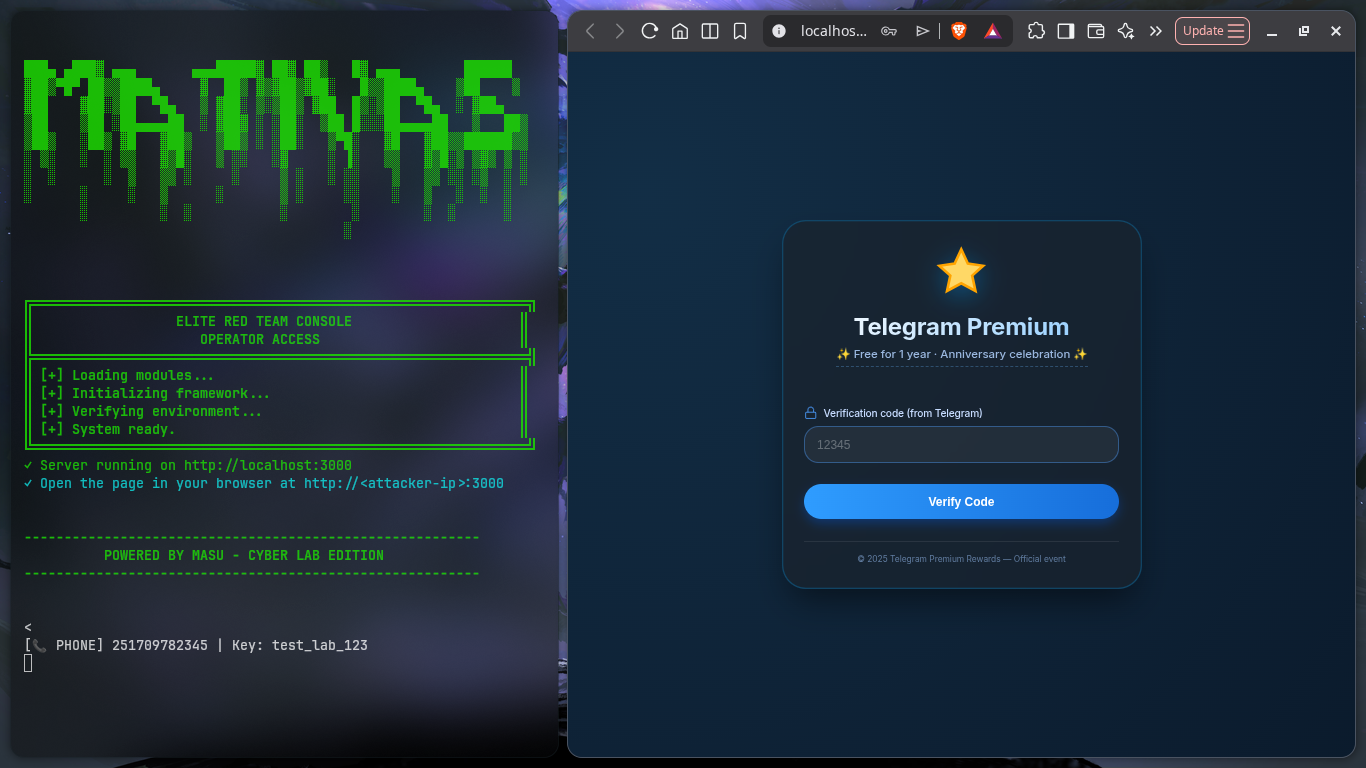 maty156/telegram-phish-simulator
Educational Telegram phishing simulation for cybersecurity training and awareness. Demonstrates credential harvesting via fake login pages in…
 razureink/cve-2024-43451-ntlm_hash_disclosure_reproduction
CVE Reproduction: cve-2024-43451-ntlm_hash_disclosure_reproduction
 lewis-ricardo/amaranth-project
CVE-2025-8088 exploitation chain + Quasar C2 multi-stage payload delivery
 segunakinsoyinu/cve-2024-42009-roundcube-xss
Stored XSS exploit for Roundcube Webmail ≤1.6.6 (CVE-2024-42009) with zero-click email exfiltration via CSS animation event handlers. Includes SMTP…
 chrxstxqn/cve-2025-6218-winrar-rce-poc
Comprehensive analysis and proof-of-concept for CVE-2025-6218 - WinRAR path traversal RCE vulnerability affecting versions 7.11 and earlier