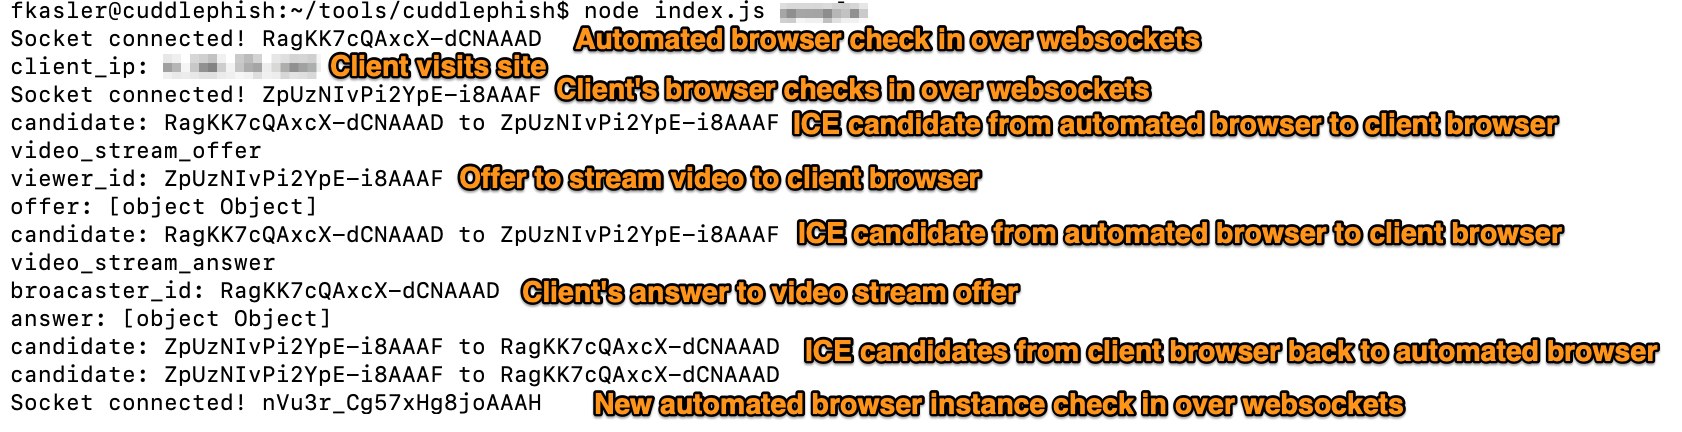
cuddlephish
 fkasler/cuddlephish
Weaponized Browser-in-the-Middle (BitM) for Penetration Testers
penetration-testingphishingphishing-tools+3
fkasler/cuddlephishWeaponized Browser-in-the-Middle (BitM) for Penetration Testers
 f-bader/tokentacticsv2
A fork of the great TokenTactics with support for CAE and token endpoint v2
 wh4l3x/cve-2026-xxxx-atlassian-email-enumeration
CVE-2026-XXXX: Atlassian GraphQL Email Enumeration Oracle (CWE-204, CVSS 5.3 MEDIUM)
 mexeck88/csrf-via-stored-xss-for-privesc
Chamilo-LMS (v2.0) CVE-2025-26153
 praetorian-inc/oauthseeker
A malicious OAuth application that can be leveraged for both internal and external phishing attacks targeting Microsoft Azure and Office365 users.
 trouble-1/vajra
Vajra is a UI-based tool with multiple techniques for attacking and enumerating in the target's Azure and AWS environment. It features an intuitive…
 r3m0t3nu11/cve-2025-1015
an attacker to create and export an address book containing a malicious payload in a field. For example, in the “Other” field of the Instant…
 4lbh4cker/alhacking
Albanian Hacking Tool!! Tools to help you with ethical hacking, Social media hack, phone info, Gmail attack, phone number attack, user discovery,…
 rvrsh3ll/tokentactics
Azure JWT Token Manipulation Toolset
 amirzargham/cve-2023-08-21-exploit
Axigen < 10.3.3.47, 10.2.3.12 - Reflected XSS
 ka7ana/cve-2023-23397
PowerShell proof-of-concept for CVE-2023-23397 that exploits Outlook's ReminderSoundFile property to intercept Net-NTLMv2 hashes via SMB or WebDAV…
 nccgroup/droppedconnection
Emulates a Cisco ASA Anyconnect VPN service for credential harvesting and VBS payload delivery in red team phishing operations.
 hacky1997/cve-2020-8825
Proof-of-concept exploit for stored XSS vulnerability in VanillaForum 2.6.3, demonstrating arbitrary HTML/script injection via insufficient input…
 chrismaddalena/goreport
A Python script to collect campaign data from Gophish and generate a report
 s1lkys/cve-2021-24884
If an authenticated user who is able to edit Wordpress PHP code in any kind, clicks a malicious link, PHP code can be edited through XSS in…
 viralmaniar/phirautee
A proof of concept crypto virus to spread user awareness about attacks and implications of ransomwares. Phirautee is written purely using PowerShell…
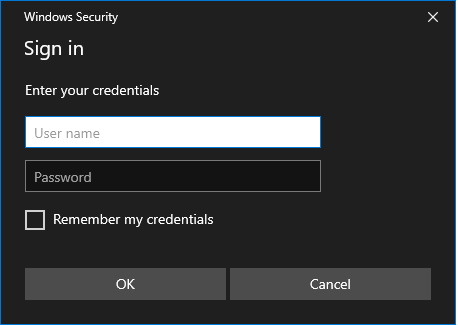 dviros/credsleaker
Credsleaker allows an attacker to craft a highly convincing credentials prompt using Windows Security, validate it against the DC and in turn leak it…