
CVE-2023-21716
 reggyraider/cve-2023-21716
CVE-2023-21716 - Microsoft Word RTF fonttbl Heap Corruption RCE exploit with reverse shell payload
binary-exploitationeducationexploitation+4
reggyraider/cve-2023-21716CVE-2023-21716 - Microsoft Word RTF fonttbl Heap Corruption RCE exploit with reverse shell payload
 nickvourd/rti-toolkit
PowerShell toolkit for remote template injection attacks and defense. Injects malicious links into Office Word documents for phishing, with…
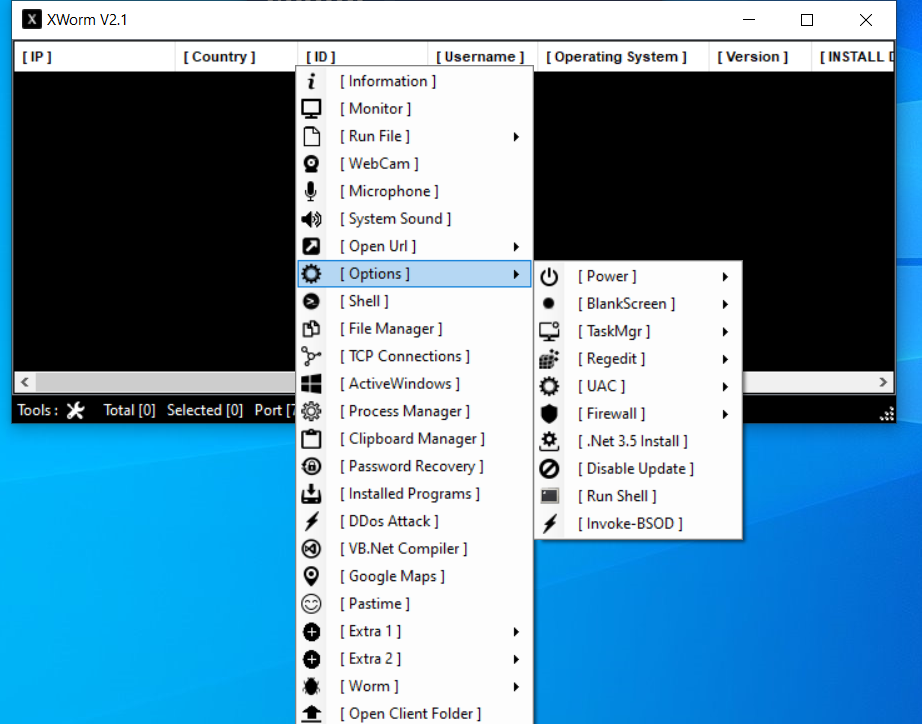
 manturever/xworm-rat
⭐️The famous XWorm RAT, version 2.1. Educational purposes only
 r00t-3xp10it/meterpeter
C2 Powershell Command & Control Framework with BuiltIn Commands
 spiralbl0ck/ios-safari-mallicous-extension-example
Example on how to injection(currently under work) of keylogger js through Safari Extension(that part done)
 jump-wang-111/amzword
An automated attack chain based on CVE-2022-30190, 163 email backdoor, and image steganography.
 v35hr4j/cve-2022-1597
The plugin, used as a companion for the Discy and Himer themes, does not sanitise and escape a parameter on its reset password form which makes it…
 r00t-3xp10it/backdoorppt
transform your payload.exe into one fake word doc (.ppt)
 xdavidhu/langhost
👻 A LAN dropbox chatbot controllable via Telegram
 ecstatic-nobel/osweep
Don't Just Search OSINT. Sweep It.
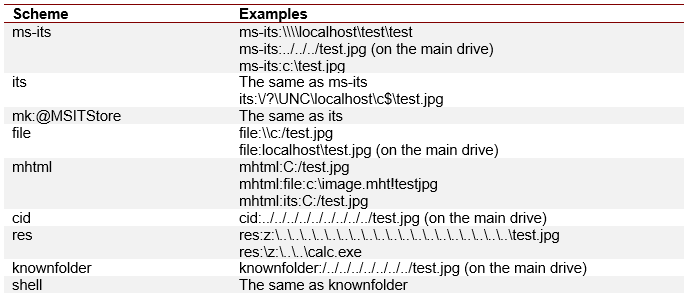 nccgroup/outlookleaktest
The Outlook HTML Leak Test Project
 mazenelzanaty/embomber
Python Script for Email Bombing which supports Gmail, Yahoo, Hotmail/Outlook
 ryhanson/phishery
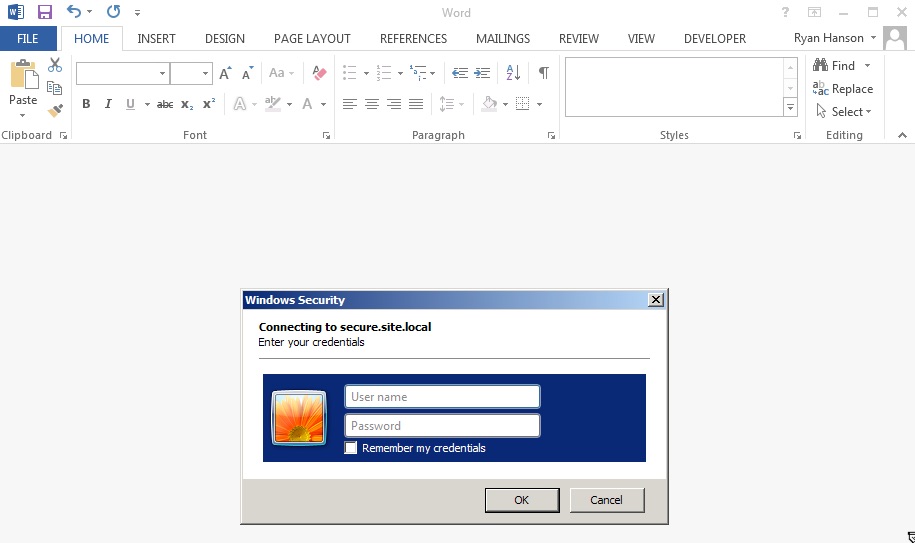
An SSL Enabled Basic Auth Credential Harvester with a Word Document Template URL Injector