
CVE-2026-32201-exploit
 b1tbit/cve-2026-32201-exploit
Python exploit for CVE-2026-32201, a reflected XSS in Microsoft SharePoint Server, enabling unauthenticated spoofing and data modification via…
exploitationpenetration-testingphishing-tools+3
1
b1tbit/cve-2026-32201-exploitPython exploit for CVE-2026-32201, a reflected XSS in Microsoft SharePoint Server, enabling unauthenticated spoofing and data modification via…
 0pts/cve-2023-0214
Secure Web Gateway 10.2.11 - Cross-Site Scripting (XSS)
 xepor/xepor
Flask-like routing framework for mitmproxy to intercept, modify, and spoof HTTP requests/responses. Enables rapid development of MITM scripts for…
 3v4si0n/http-revshell
Powershell reverse shell using HTTP/S protocol with AMSI bypass and Proxy Aware
 onvio/gophish
Gophish with Malicious Attachment and HTTP redirect support
 komomon/cve-2022-30190-follina-office-msdt-fixed
Modified CVE-2022-30190 exploit tool for MS-MSDT Office RCE with custom docx template support, binary/command execution modes, and embedded HTTP…
 qsecure-labs/overlord
Python-based CLI for automated red team infrastructure deployment on AWS and Digital Ocean, with modular support for C2, email servers, HTTP…
 dviros/credsleaker
Credsleaker allows an attacker to craft a highly convincing credentials prompt using Windows Security, validate it against the DC and in turn leak it…
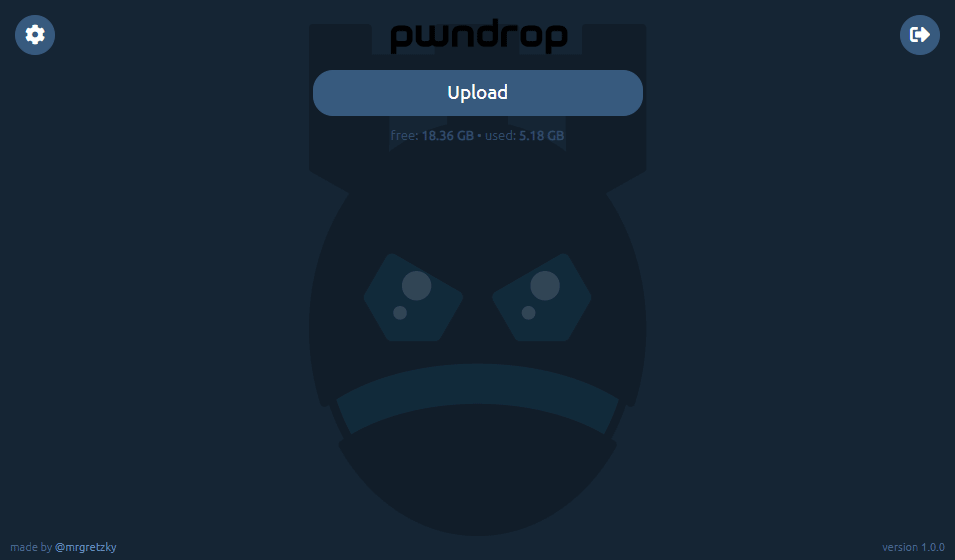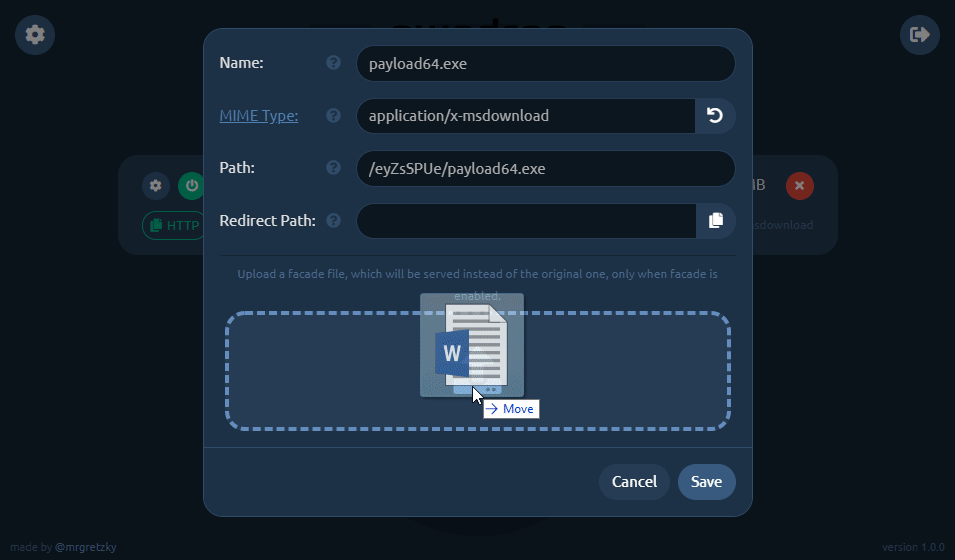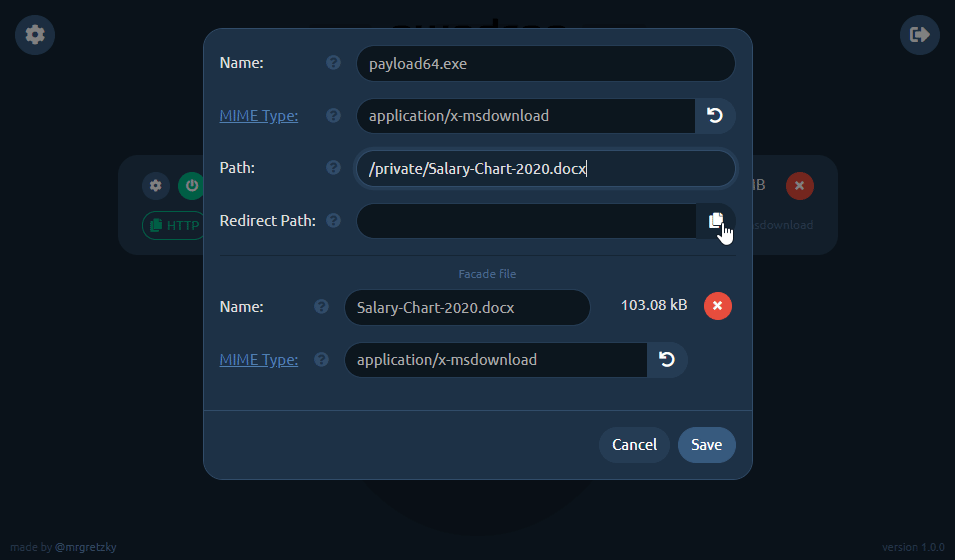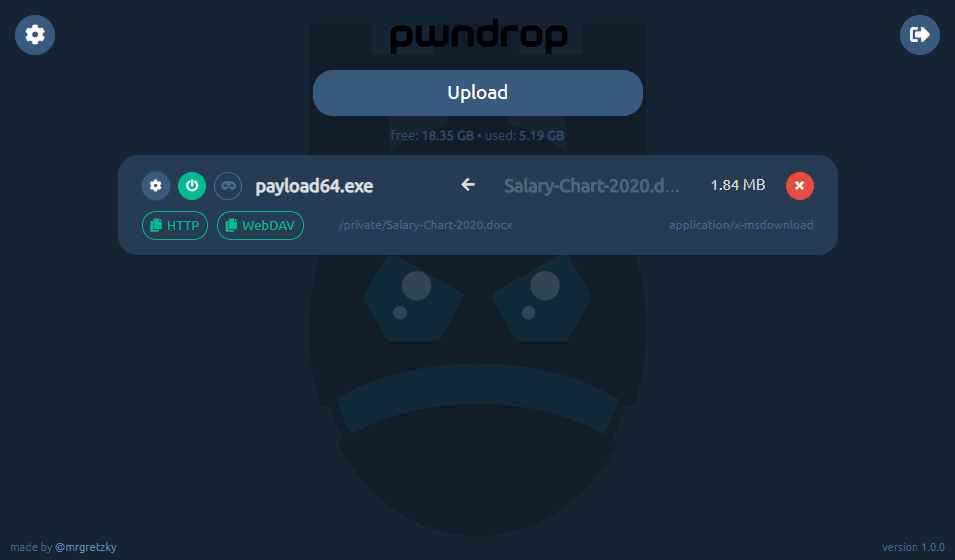 kgretzky/pwndrop
Self-deployable file hosting service for red teamers, allowing to easily upload and share payloads over HTTP and WebDAV.
 spiderlabs/responder
Responder is a LLMNR, NBT-NS and MDNS poisoner, with built-in HTTP/SMB/MSSQL/FTP/LDAP rogue authentication server supporting NTLMv1/NTLMv2/LMv2,…
 quickbreach/exchangerelayx
An NTLM relay tool to the EWS endpoint for on-premise exchange servers. Provides an OWA for hackers.
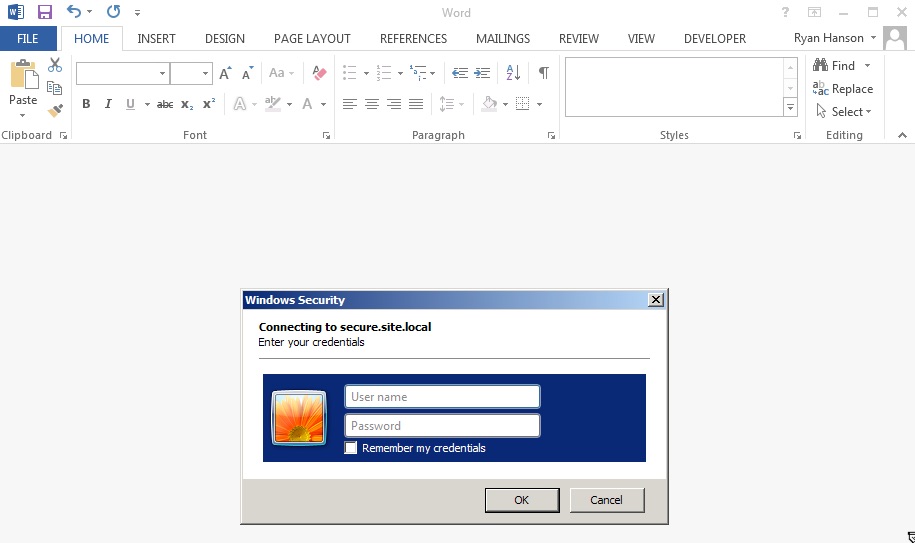 ryhanson/phishery
An SSL Enabled Basic Auth Credential Harvester with a Word Document Template URL Injector