

beef
 beefproject/beef
The Browser Exploitation Framework Project
command-and-controlexploitationexploit-frameworks+8
beefproject/beefThe Browser Exploitation Framework Project
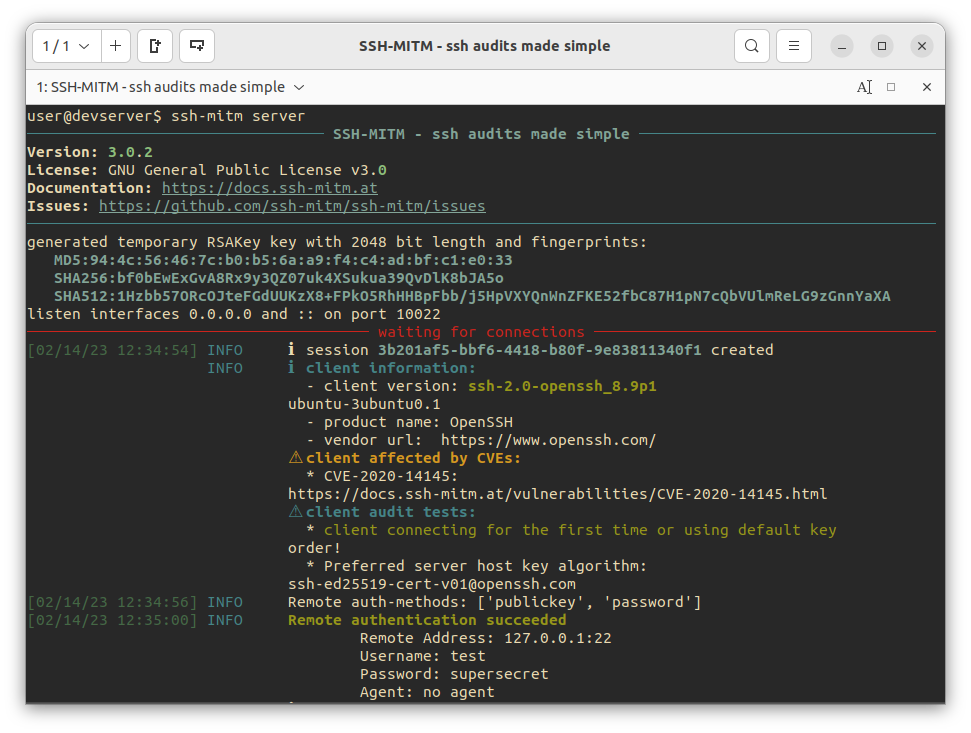 ssh-mitm/ssh-mitm
SSH-MITM - ssh audits made simple
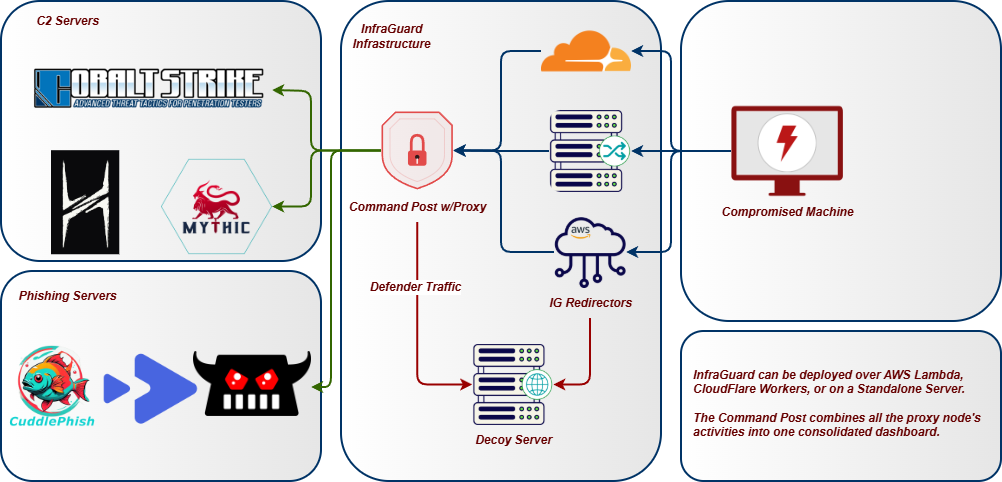 whispergate/infraguard
InfraGuard is a Command & Control Redirection Proxy and Manager which protects your Red Team Infrastructure against threat attribution
 goshs-labs/goshs
Feature-rich single-binary file server for red teamers and developers. HTTP/S · WebDAV · FTP/SFTP · SMB · LDAP/S · NTLM hash capture · DNS/SMTP…
 yuyudhn/blindxss-lite
A lightweight Blind XSS (Cross-Site Scripting) collector and payload server built with Flask
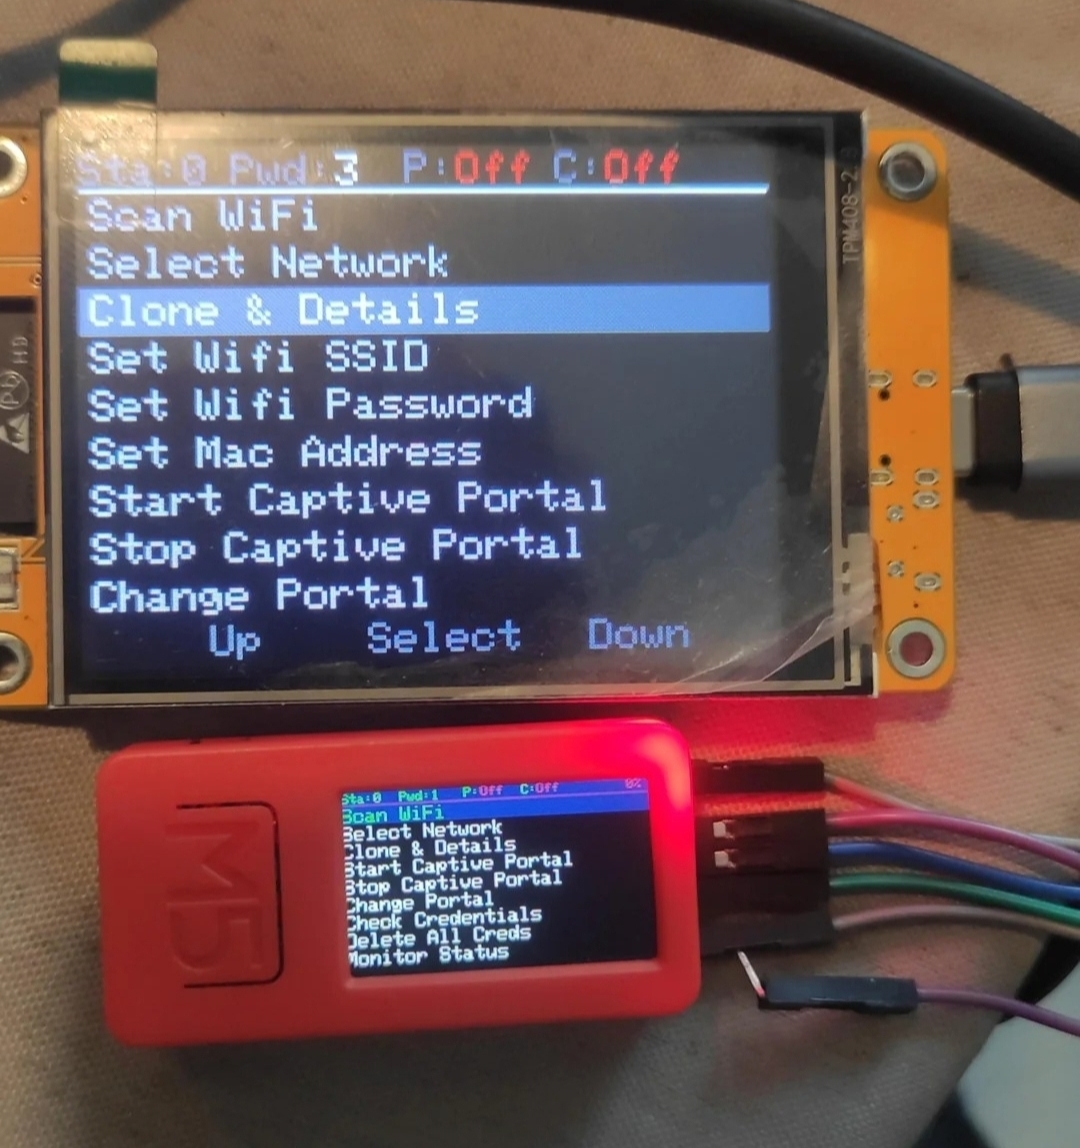 7h30th3r0n3/evil-m5project
Multi-purpose WiFi penetration testing toolkit for M5Stack devices. Performs network scanning, evil-twin attacks, deauthentication, captive portal…
 mr-un1k0d3r/azureredops
Azure RedOps is a offensive security toolkit for assessing the security posture of Microsoft Entra ID
 dedsec1121fk/dedsec
Educational Android (Termux) toolkit for learning penetration testing, OSINT, social engineering, and network security through hands-on scripts,…
 vighnesh91/severitas
Authorized social-engineering simulation framework with an isolated loopback lab, synthetic audience generation, pre-flight authorization checks, and…
 ultrafunkamsterdam/nodriver
Successor of Undetected-Chromedriver. Providing a blazing fast framework for web automation, webscraping, bots and any other creative ideas which are…
 sherlock-project/sherlock
Hunt down social media accounts by username across social networks
 bardlaudian/cve-2025-24071
Dependency-free Python PoC generator for CVE-2025-24071 that crafts a malicious .library-ms file in a ZIP to trigger Windows Explorer NTLM hash…
 trustedsec/unicorn
Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…
 mishakorzik/allhackingtools
All-in-One Hacking Tools For Hackers! And more hacking tools! For termux.
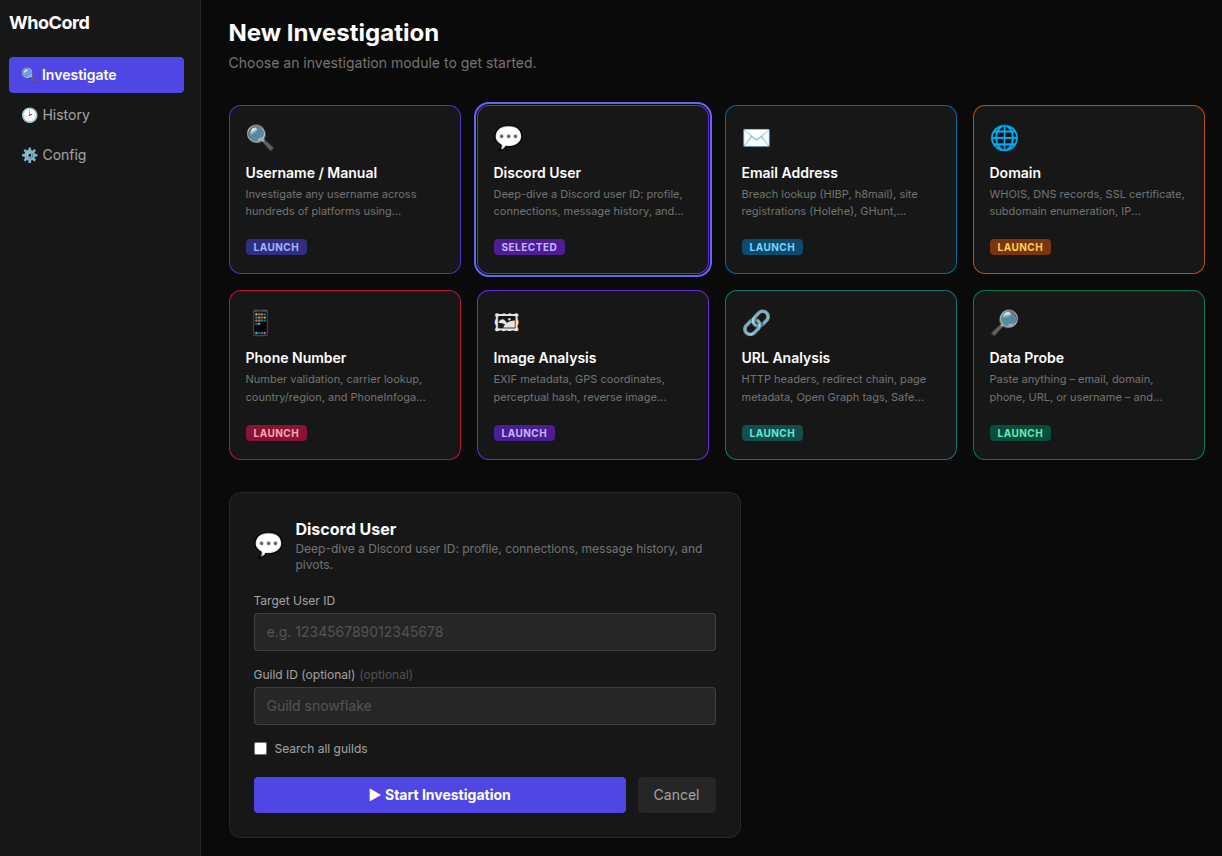 siv-nick/whocord
Scans Discord links across mutual guilds to extract profiles, cross‑references 700+ sites, searches usernames with 30+ tools, and generates an…
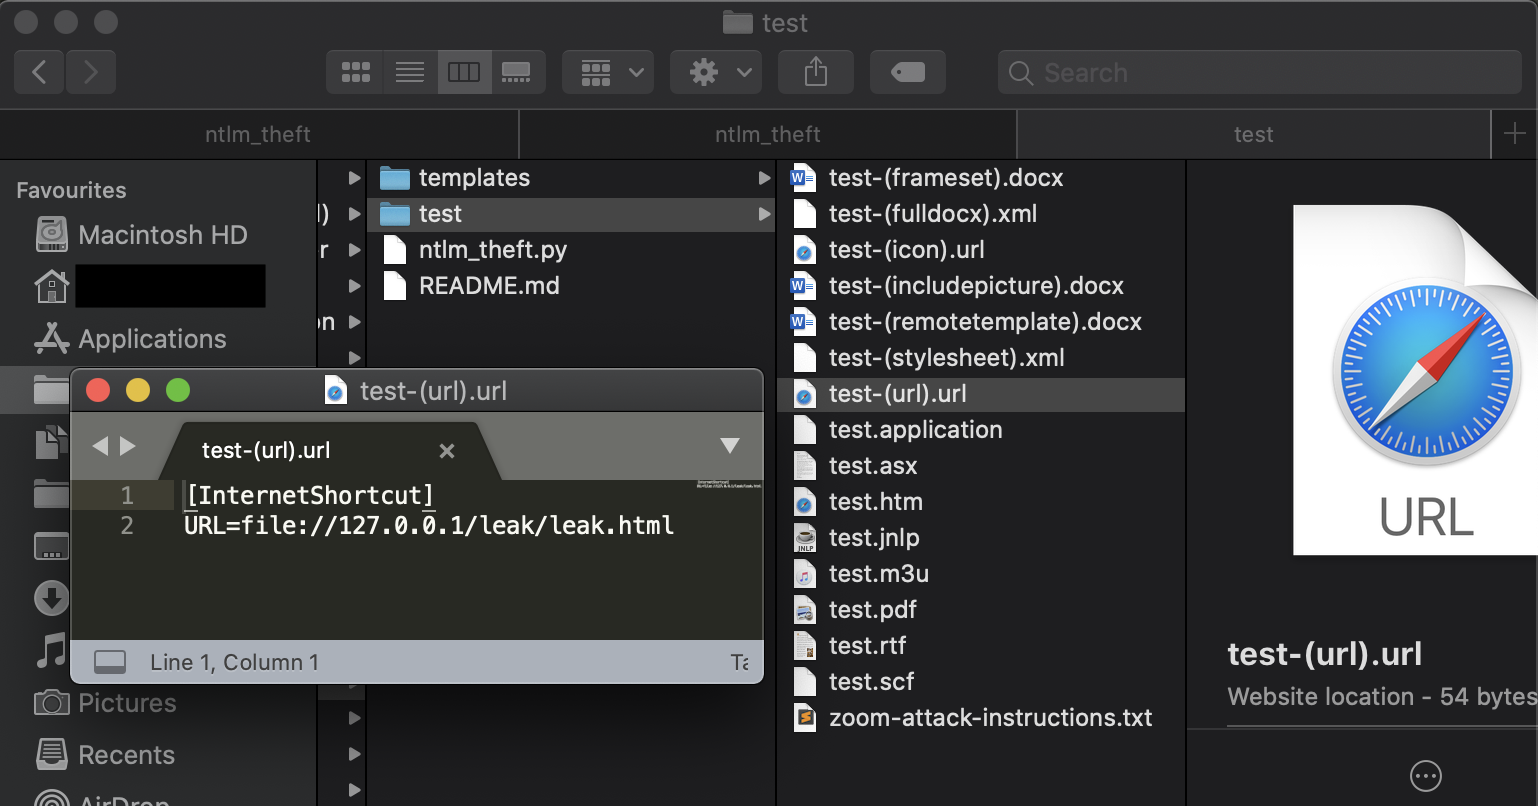 greenwolf/ntlm_theft
A tool for generating multiple types of NTLMv2 hash theft files by Jacob Wilkin (Greenwolf)
 redbyte1337/graphspy
Initial Access and Post-Exploitation Tool for Entra ID and M365 with a browser-based GUI
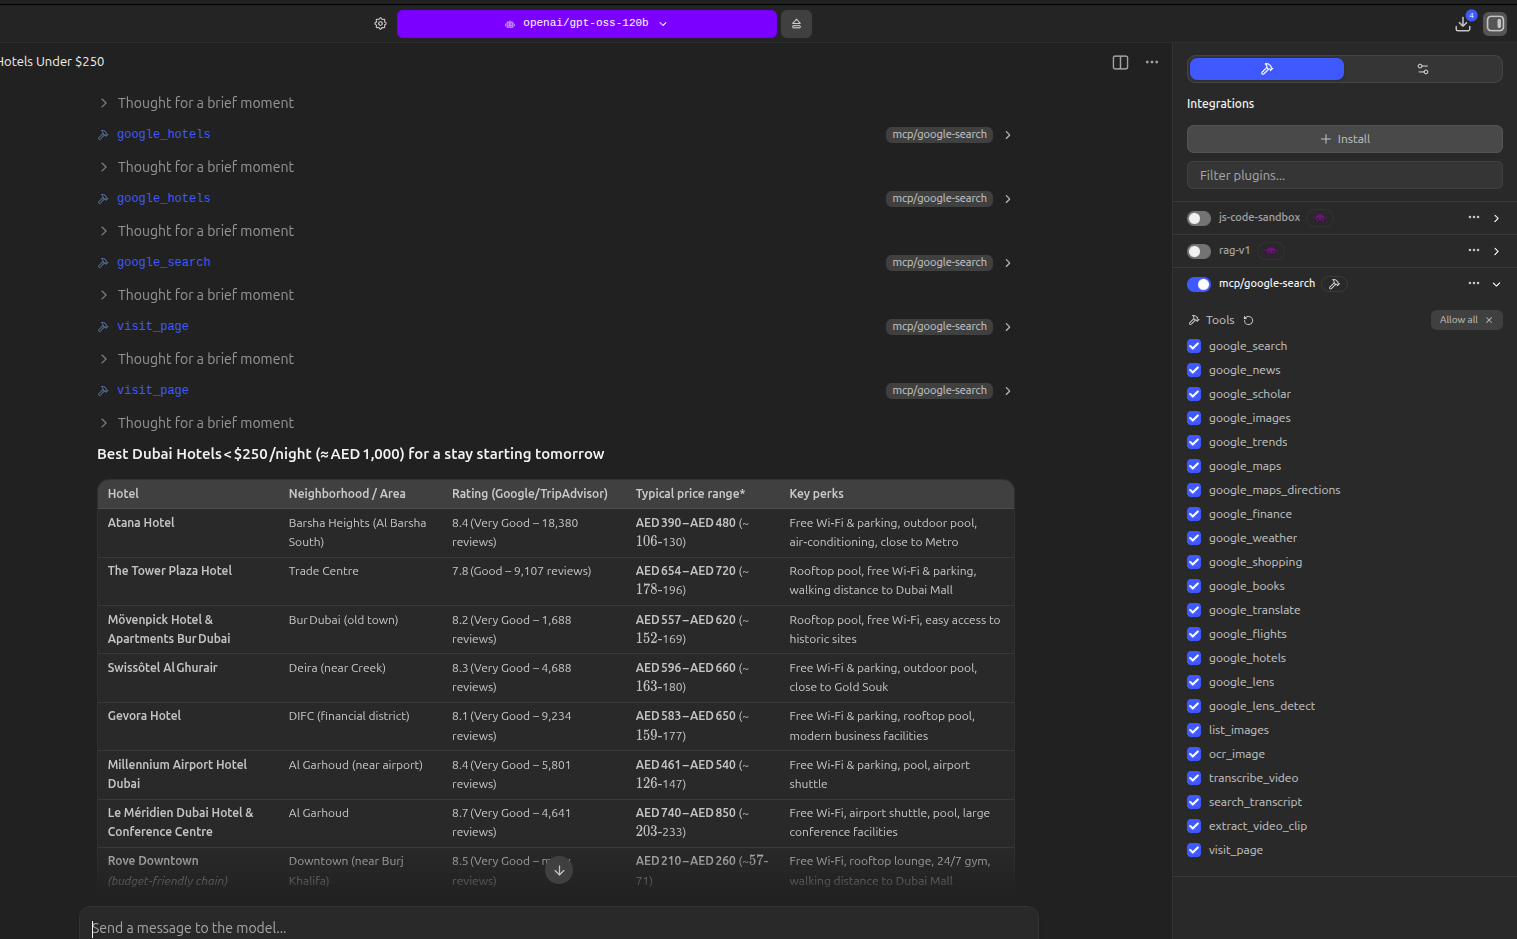 vincentkaufmann/noapi-google-search-mcp
MCP server for Google search and page fetching using headless Chromium