

zaproxy
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
android-securityapi-securityapi-security-testing+15
zaproxy/zaproxyOpen-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
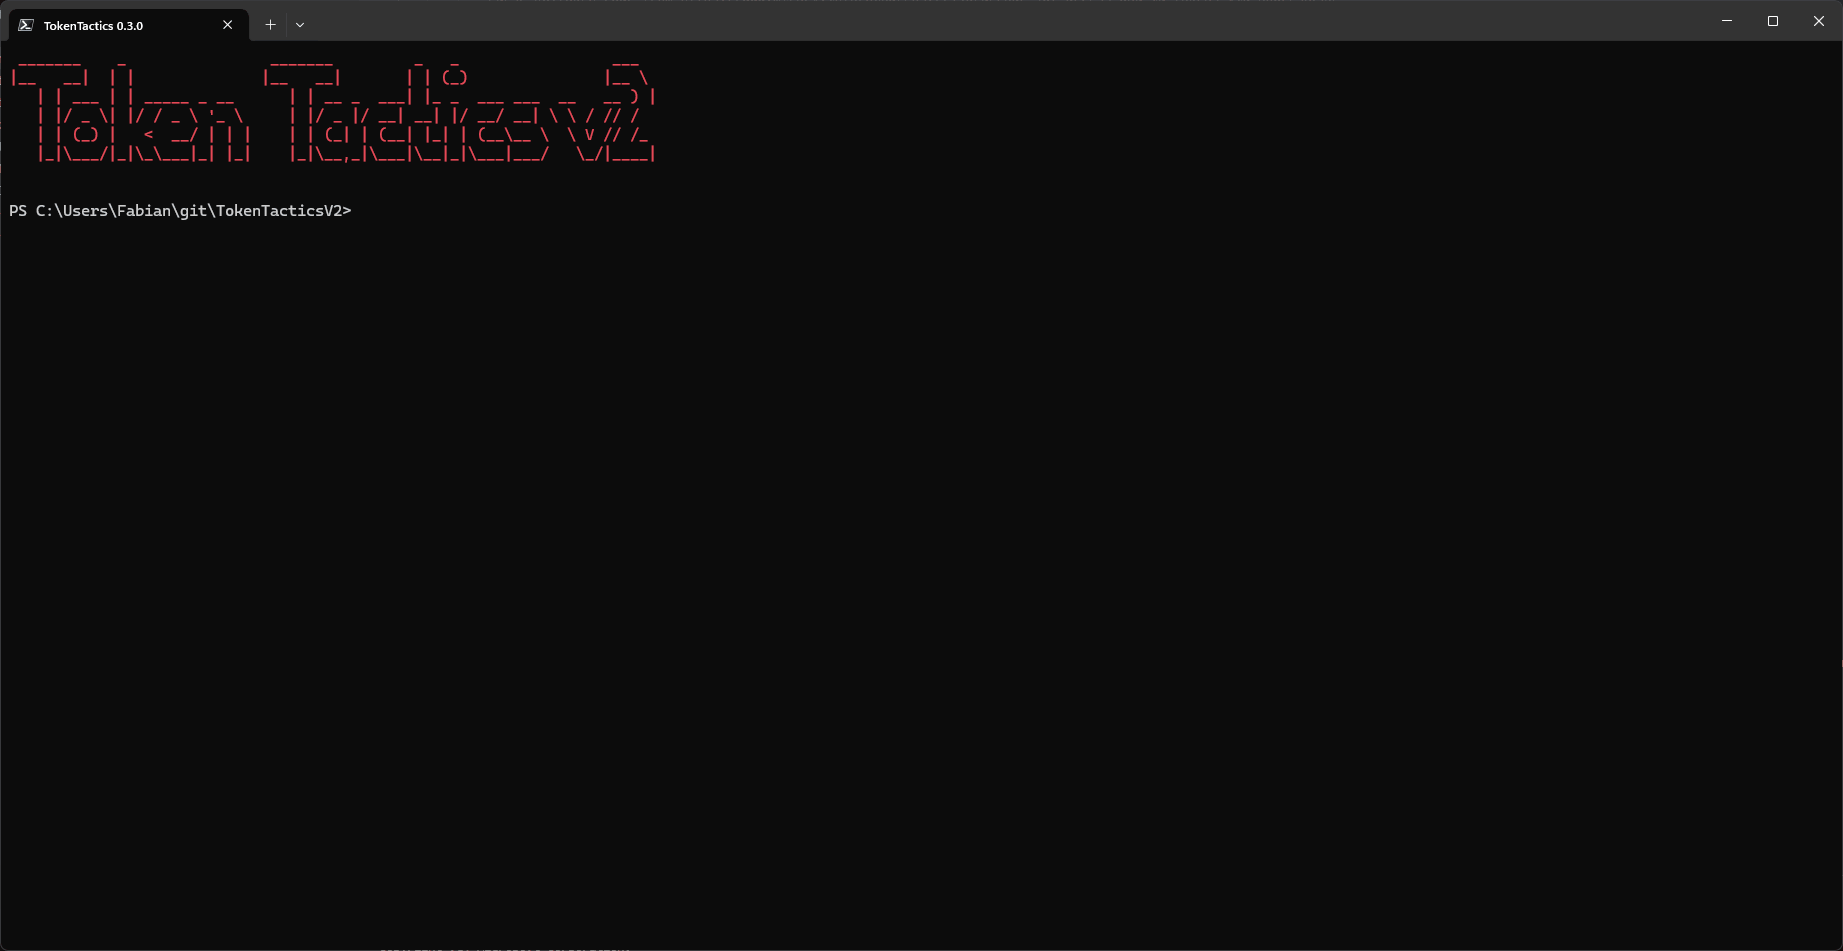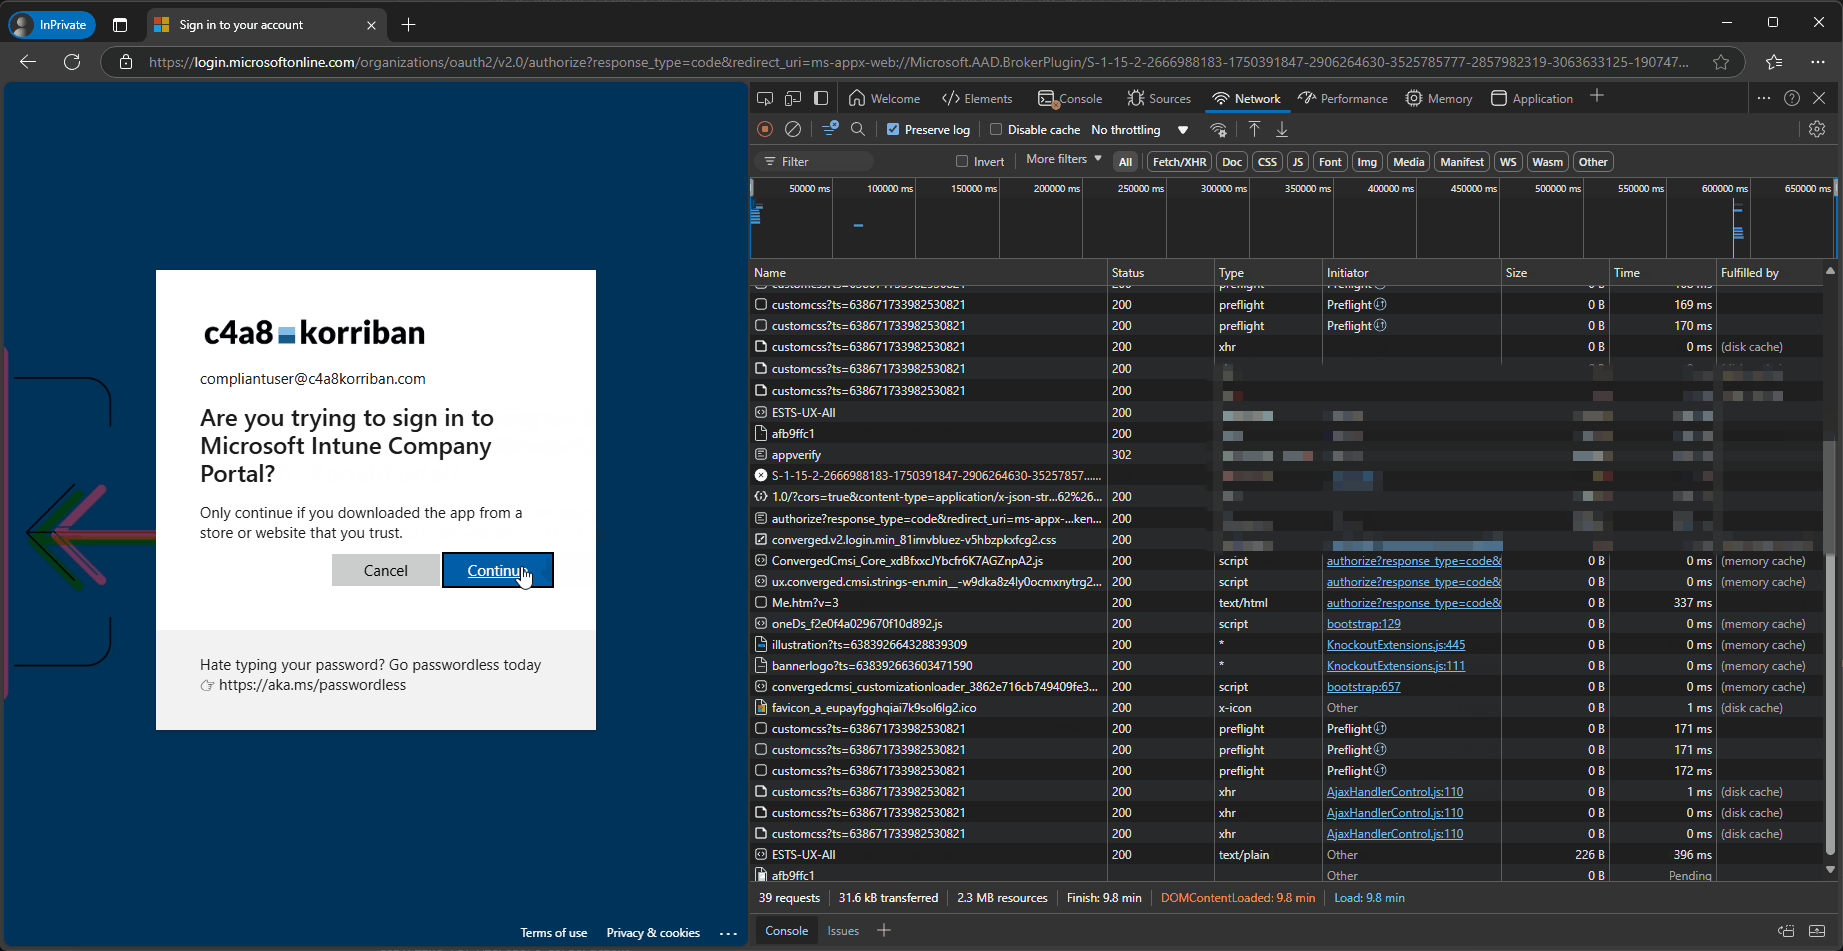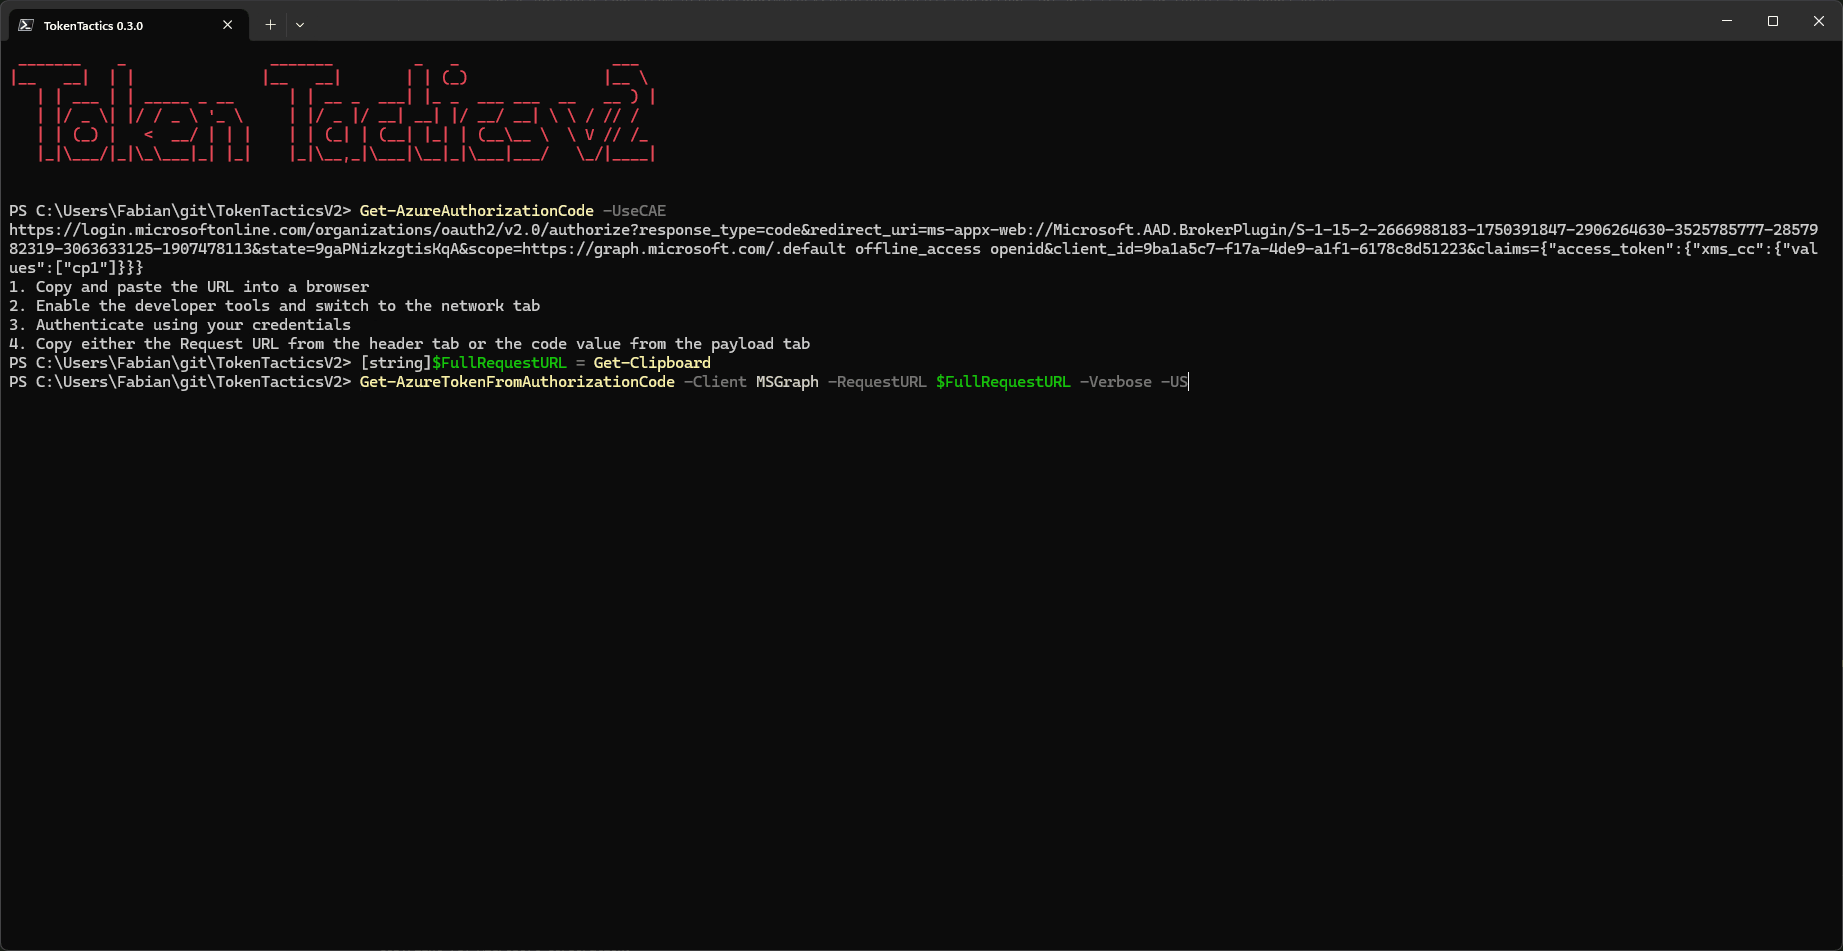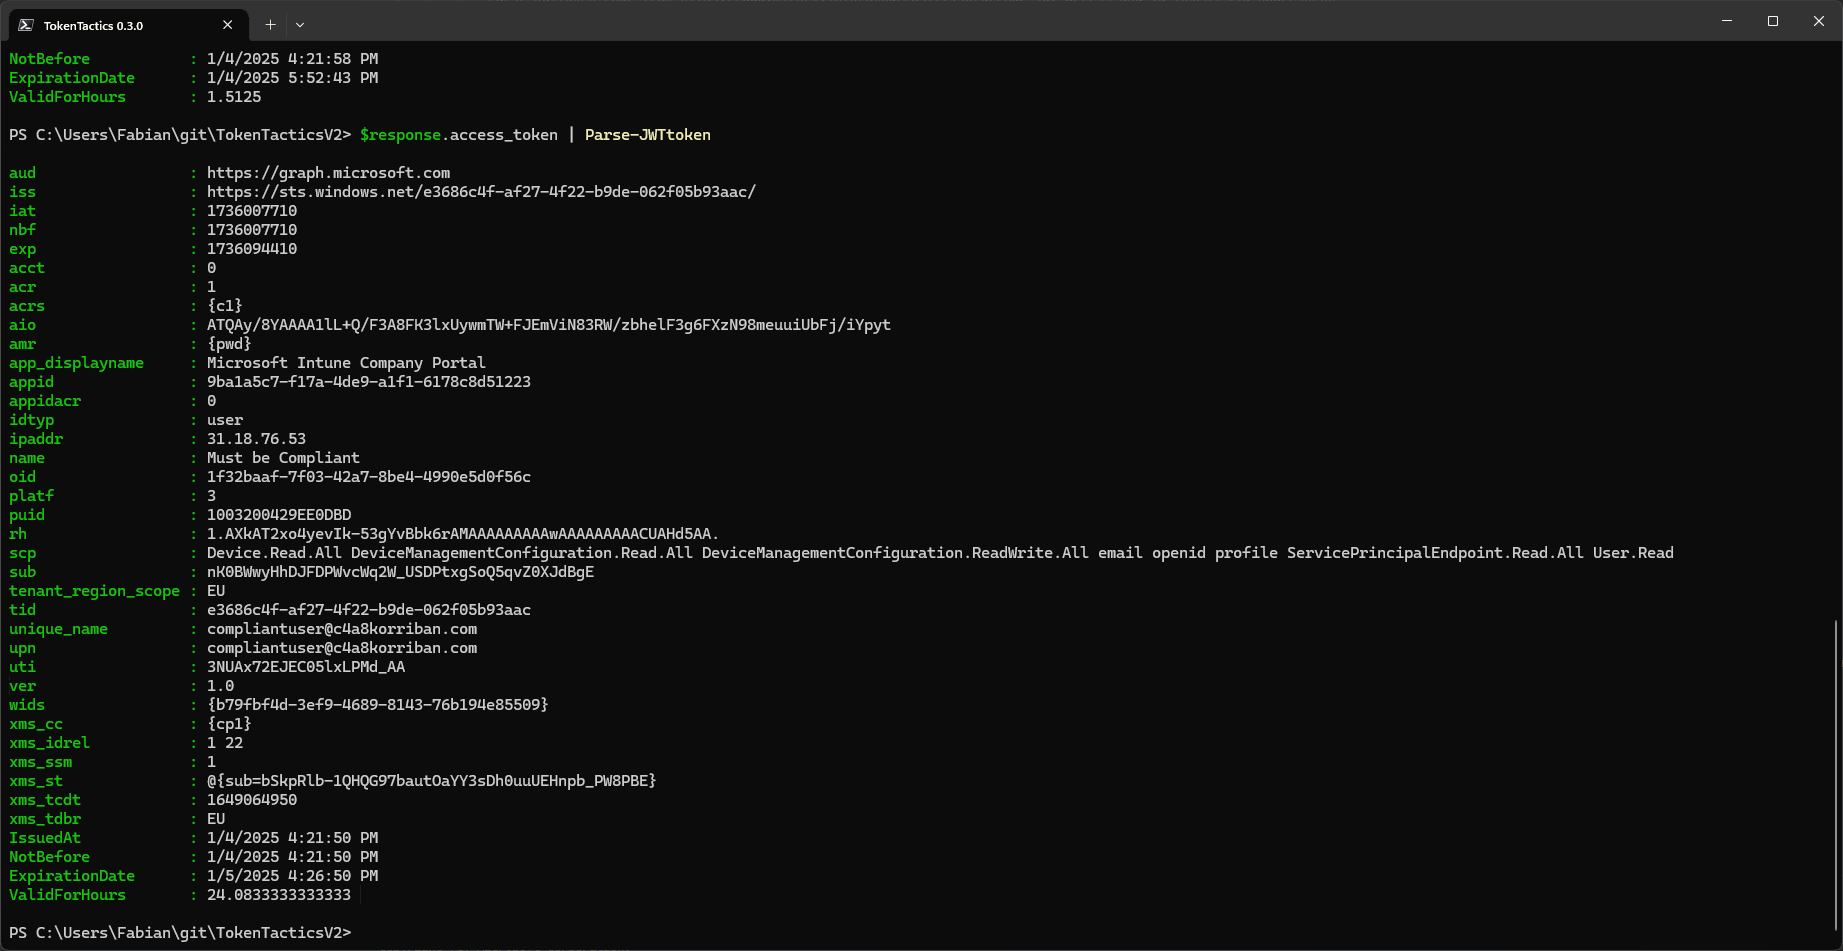 f-bader/tokentacticsv2
A fork of the great TokenTactics with support for CAE and token endpoint v2
 mishakorzik/allhackingtools
All-in-One Hacking Tools For Hackers! And more hacking tools! For termux.
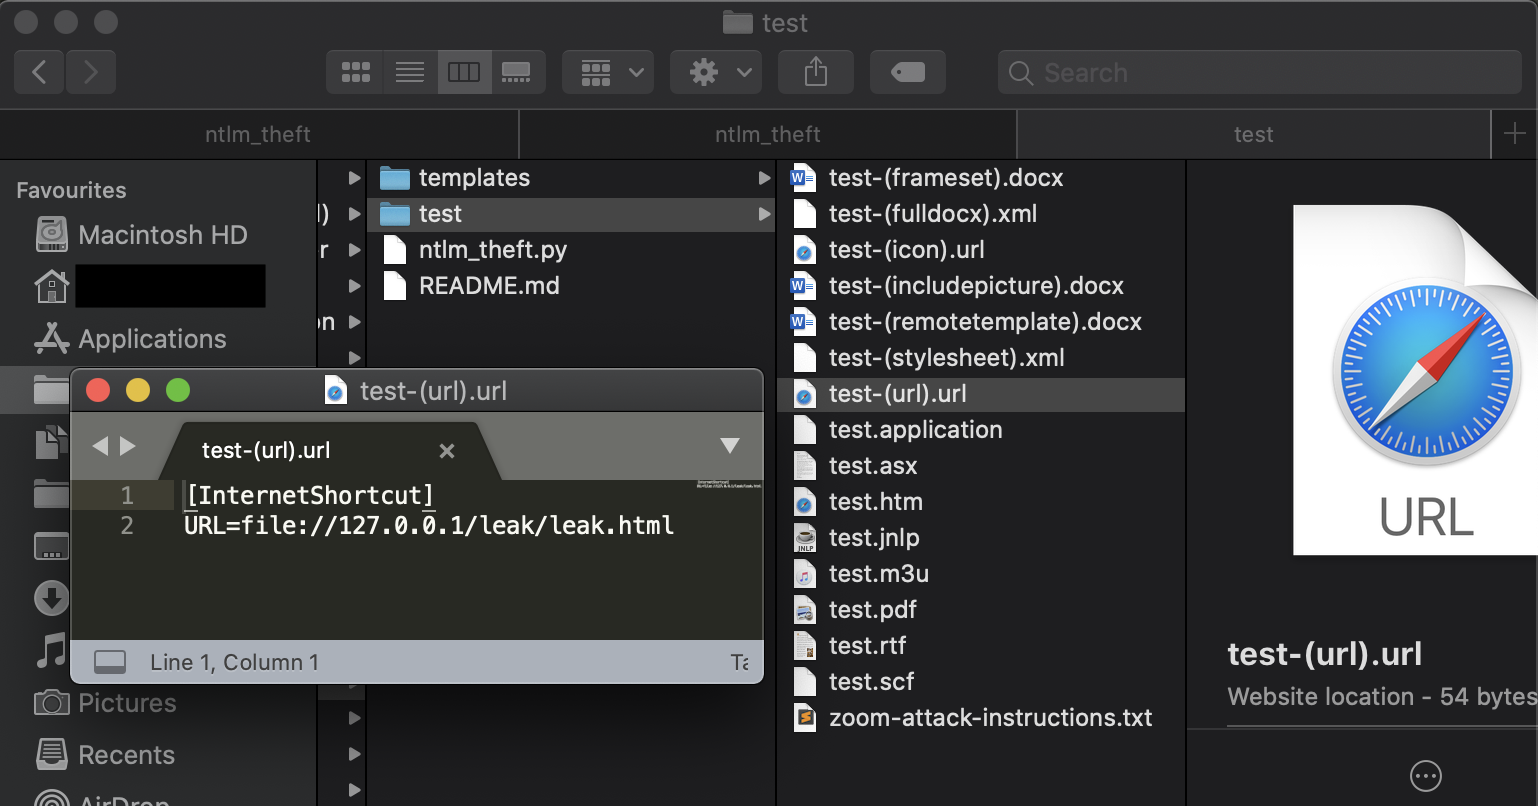 greenwolf/ntlm_theft
A tool for generating multiple types of NTLMv2 hash theft files by Jacob Wilkin (Greenwolf)
 dedsec1121fk/dedsec
Educational Android (Termux) toolkit for learning penetration testing, OSINT, social engineering, and network security through hands-on scripts,…
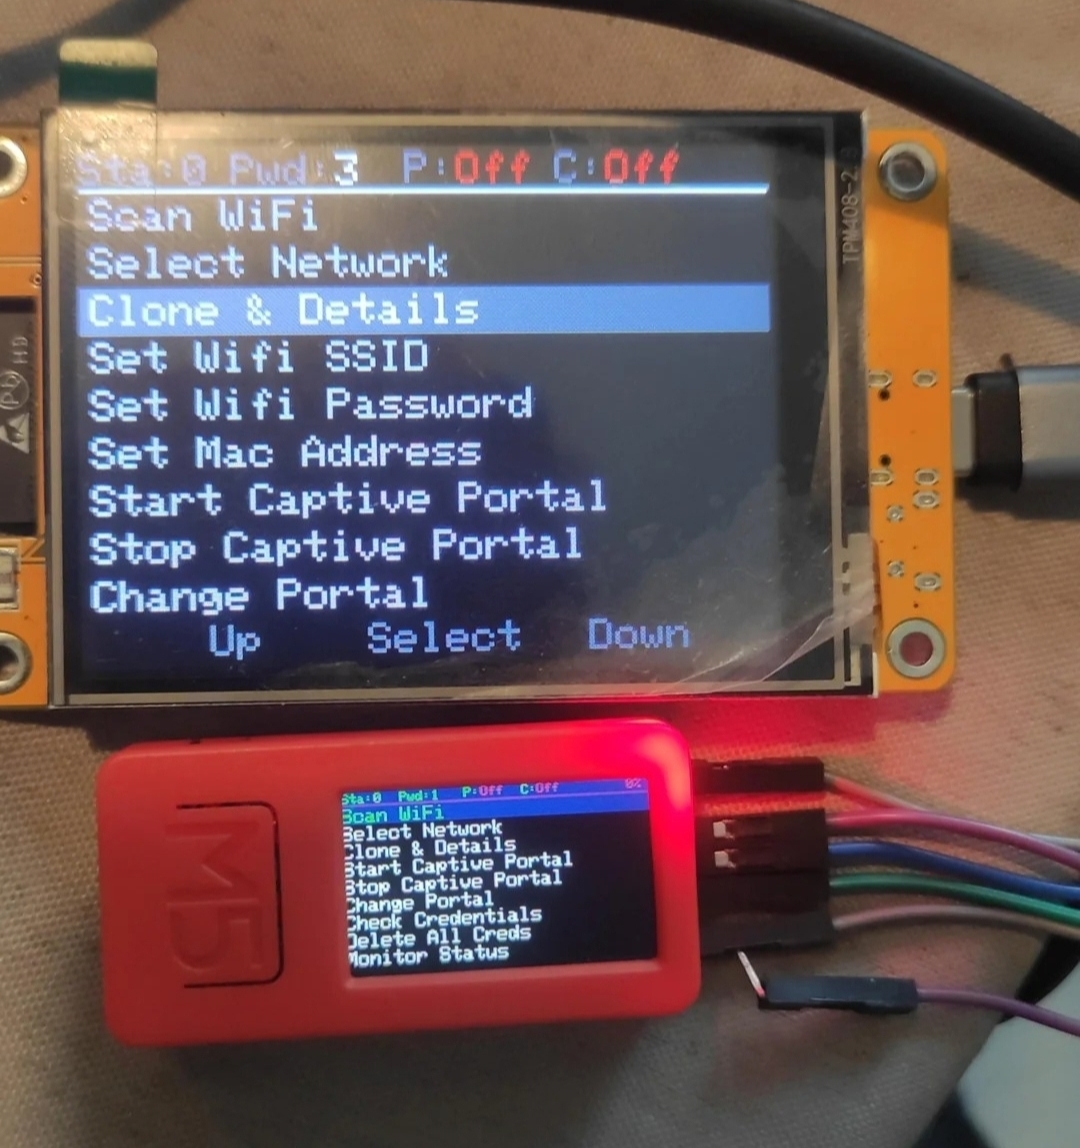 7h30th3r0n3/evil-m5project
Multi-purpose WiFi penetration testing toolkit for M5Stack devices. Performs network scanning, evil-twin attacks, deauthentication, captive portal…
 jonaslejon/malicious-pdf
Generate malicious PDF test files for penetration testing, bug bounty hunting, and red teaming. Tests SSRF, XSS, XXE, NTLM credential theft, and data…
 drk1wi/modlishka
Modlishka. Reverse Proxy.
 weswrench/cve-2026-36214
Stored Cross-Site Scripting (XSS) in osTicket via Vulnerable Bootstrap Tooltip Component
 trustedsec/social-engineer-toolkit
The Social-Engineer Toolkit (SET) repository from TrustedSec - All new versions of SET will be deployed here.
 dharmstm/cve-2026-30502-openkm-6.3.12-reflected-xss
Documentation and proof-of-concept for CVE-2026-30502, a reflected XSS vulnerability in OpenKM v6.3.12. Includes technical analysis, root cause,…
 nickvourd/rti-toolkit
PowerShell toolkit for remote template injection attacks and defense. Injects malicious links into Office Word documents for phishing, with…
 sanupl/letterpress-1.2.1-open-redirection-via-html-injection-vulnerability
In LetterPress plugin <= 1.2.1 is vulnerable to Html Injection Vulnerability which can futher leads to Open Redirection Vulnerabilty.
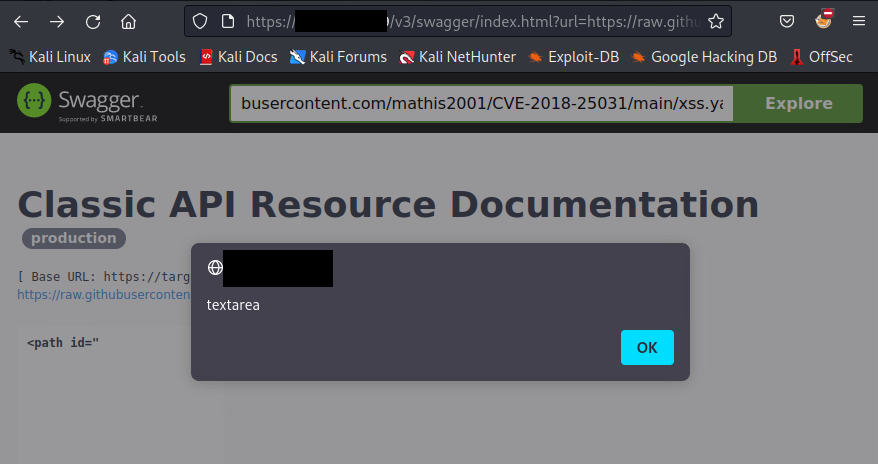 mathis2001/cve-2018-25031
CVE-2018-25031 tests
 crimsonforge-io/king-phisher
Simulate realistic phishing campaigns with credential harvesting, email tracking, and landing page cloning for security awareness training and…
 b1tbit/cve-2026-32201-exploit
Python exploit for CVE-2026-32201, a reflected XSS in Microsoft SharePoint Server, enabling unauthenticated spoofing and data modification via…
 elvira-alec/fracture
FragAttacks WiFi penetration framework — CVE-2020-24586/87/88
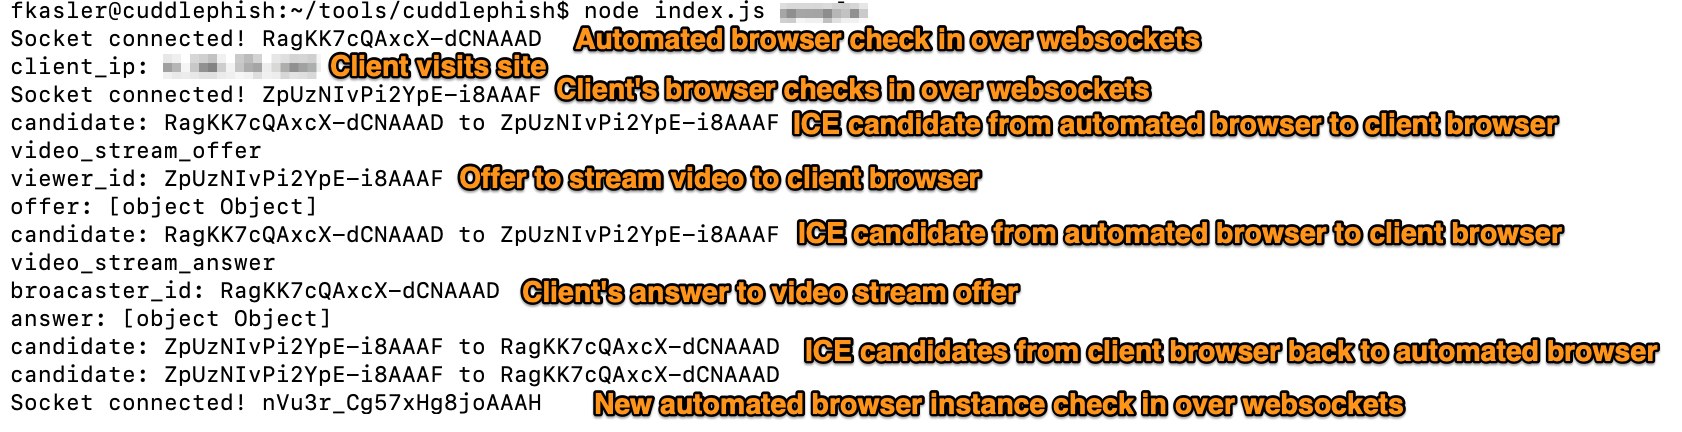 fkasler/cuddlephish
Weaponized Browser-in-the-Middle (BitM) for Penetration Testers