
FullscreenBrowserPhishing
 gmh5225/fullscreenbrowserphishing
PoC of the phishing through setting browser in the fullscreen mode
educationphishingphishing-tools+3
gmh5225/fullscreenbrowserphishingPoC of the phishing through setting browser in the fullscreen mode
 bardlaudian/cve-2025-24071
Dependency-free Python PoC generator for CVE-2025-24071 that crafts a malicious .library-ms file in a ZIP to trigger Windows Explorer NTLM hash…
 mr-un1k0d3r/redteamscripts
Collection of offensive red team scripts including process termination, SPF bypass for phishing, password spraying, and ColdFusion password…
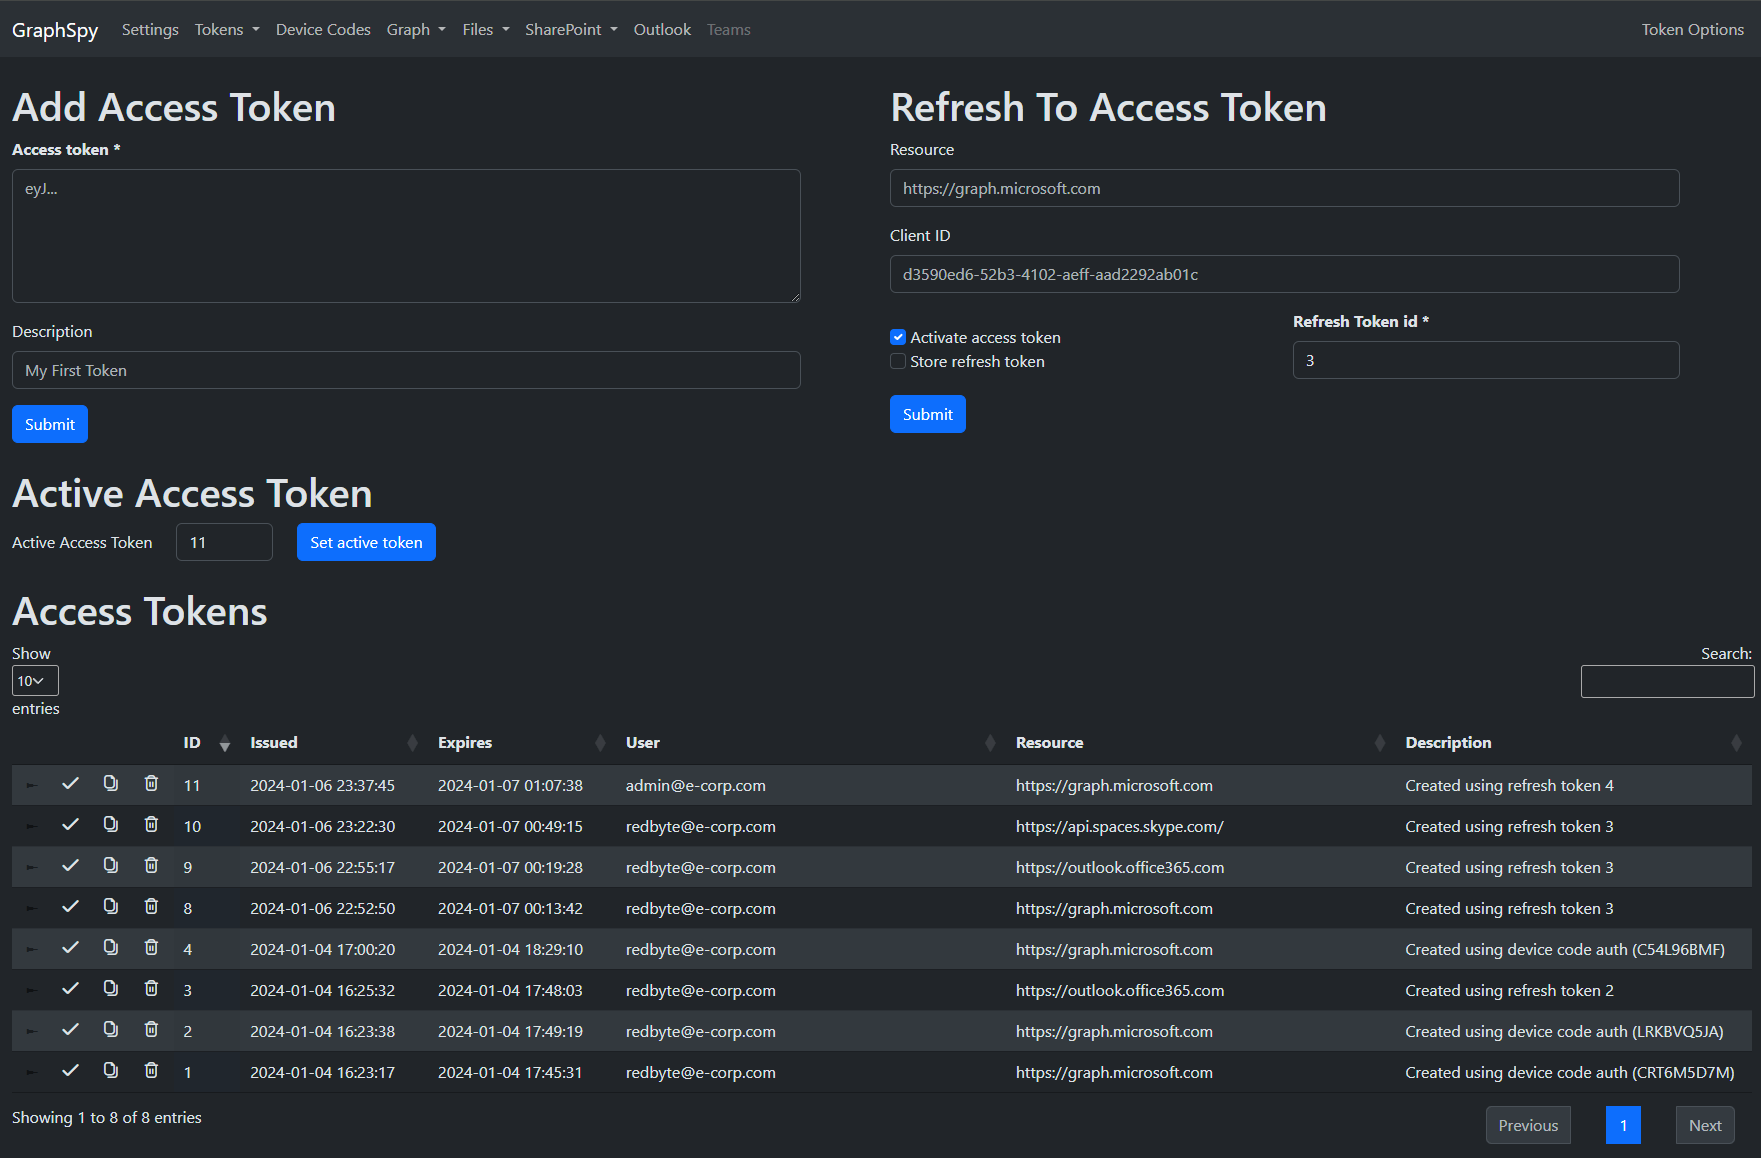 redbyte1337/graphspy
Initial Access and Post-Exploitation Tool for Entra ID and M365 with a browser-based GUI
 johnhammond/recaptcha-phish
Phishing with a fake reCAPTCHA
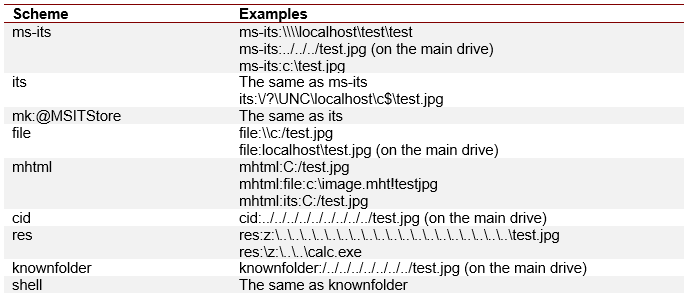 nccgroup/outlookleaktest
The Outlook HTML Leak Test Project
 h3x0v3rl0rd/xll_windows_reverse_shell
xll windows reverse shell
 cappricio-securities/camjacking
CamJacking is a tool designed for use in human penetration testing tool. It is intended to simulate potential security threats by testing the…

 nu11secur1ty/vulnerable-pdf
Educational PDF files demonstrating client-side exploitation techniques, including calculator execution and directory browsing, for security testing…
 dviros/rat-via-telegram
Windows Remote Post Breach Tool via Telegram
 operatorequals/smbrat
A Windows Remote Administration Tool in Visual Basic with UNC paths
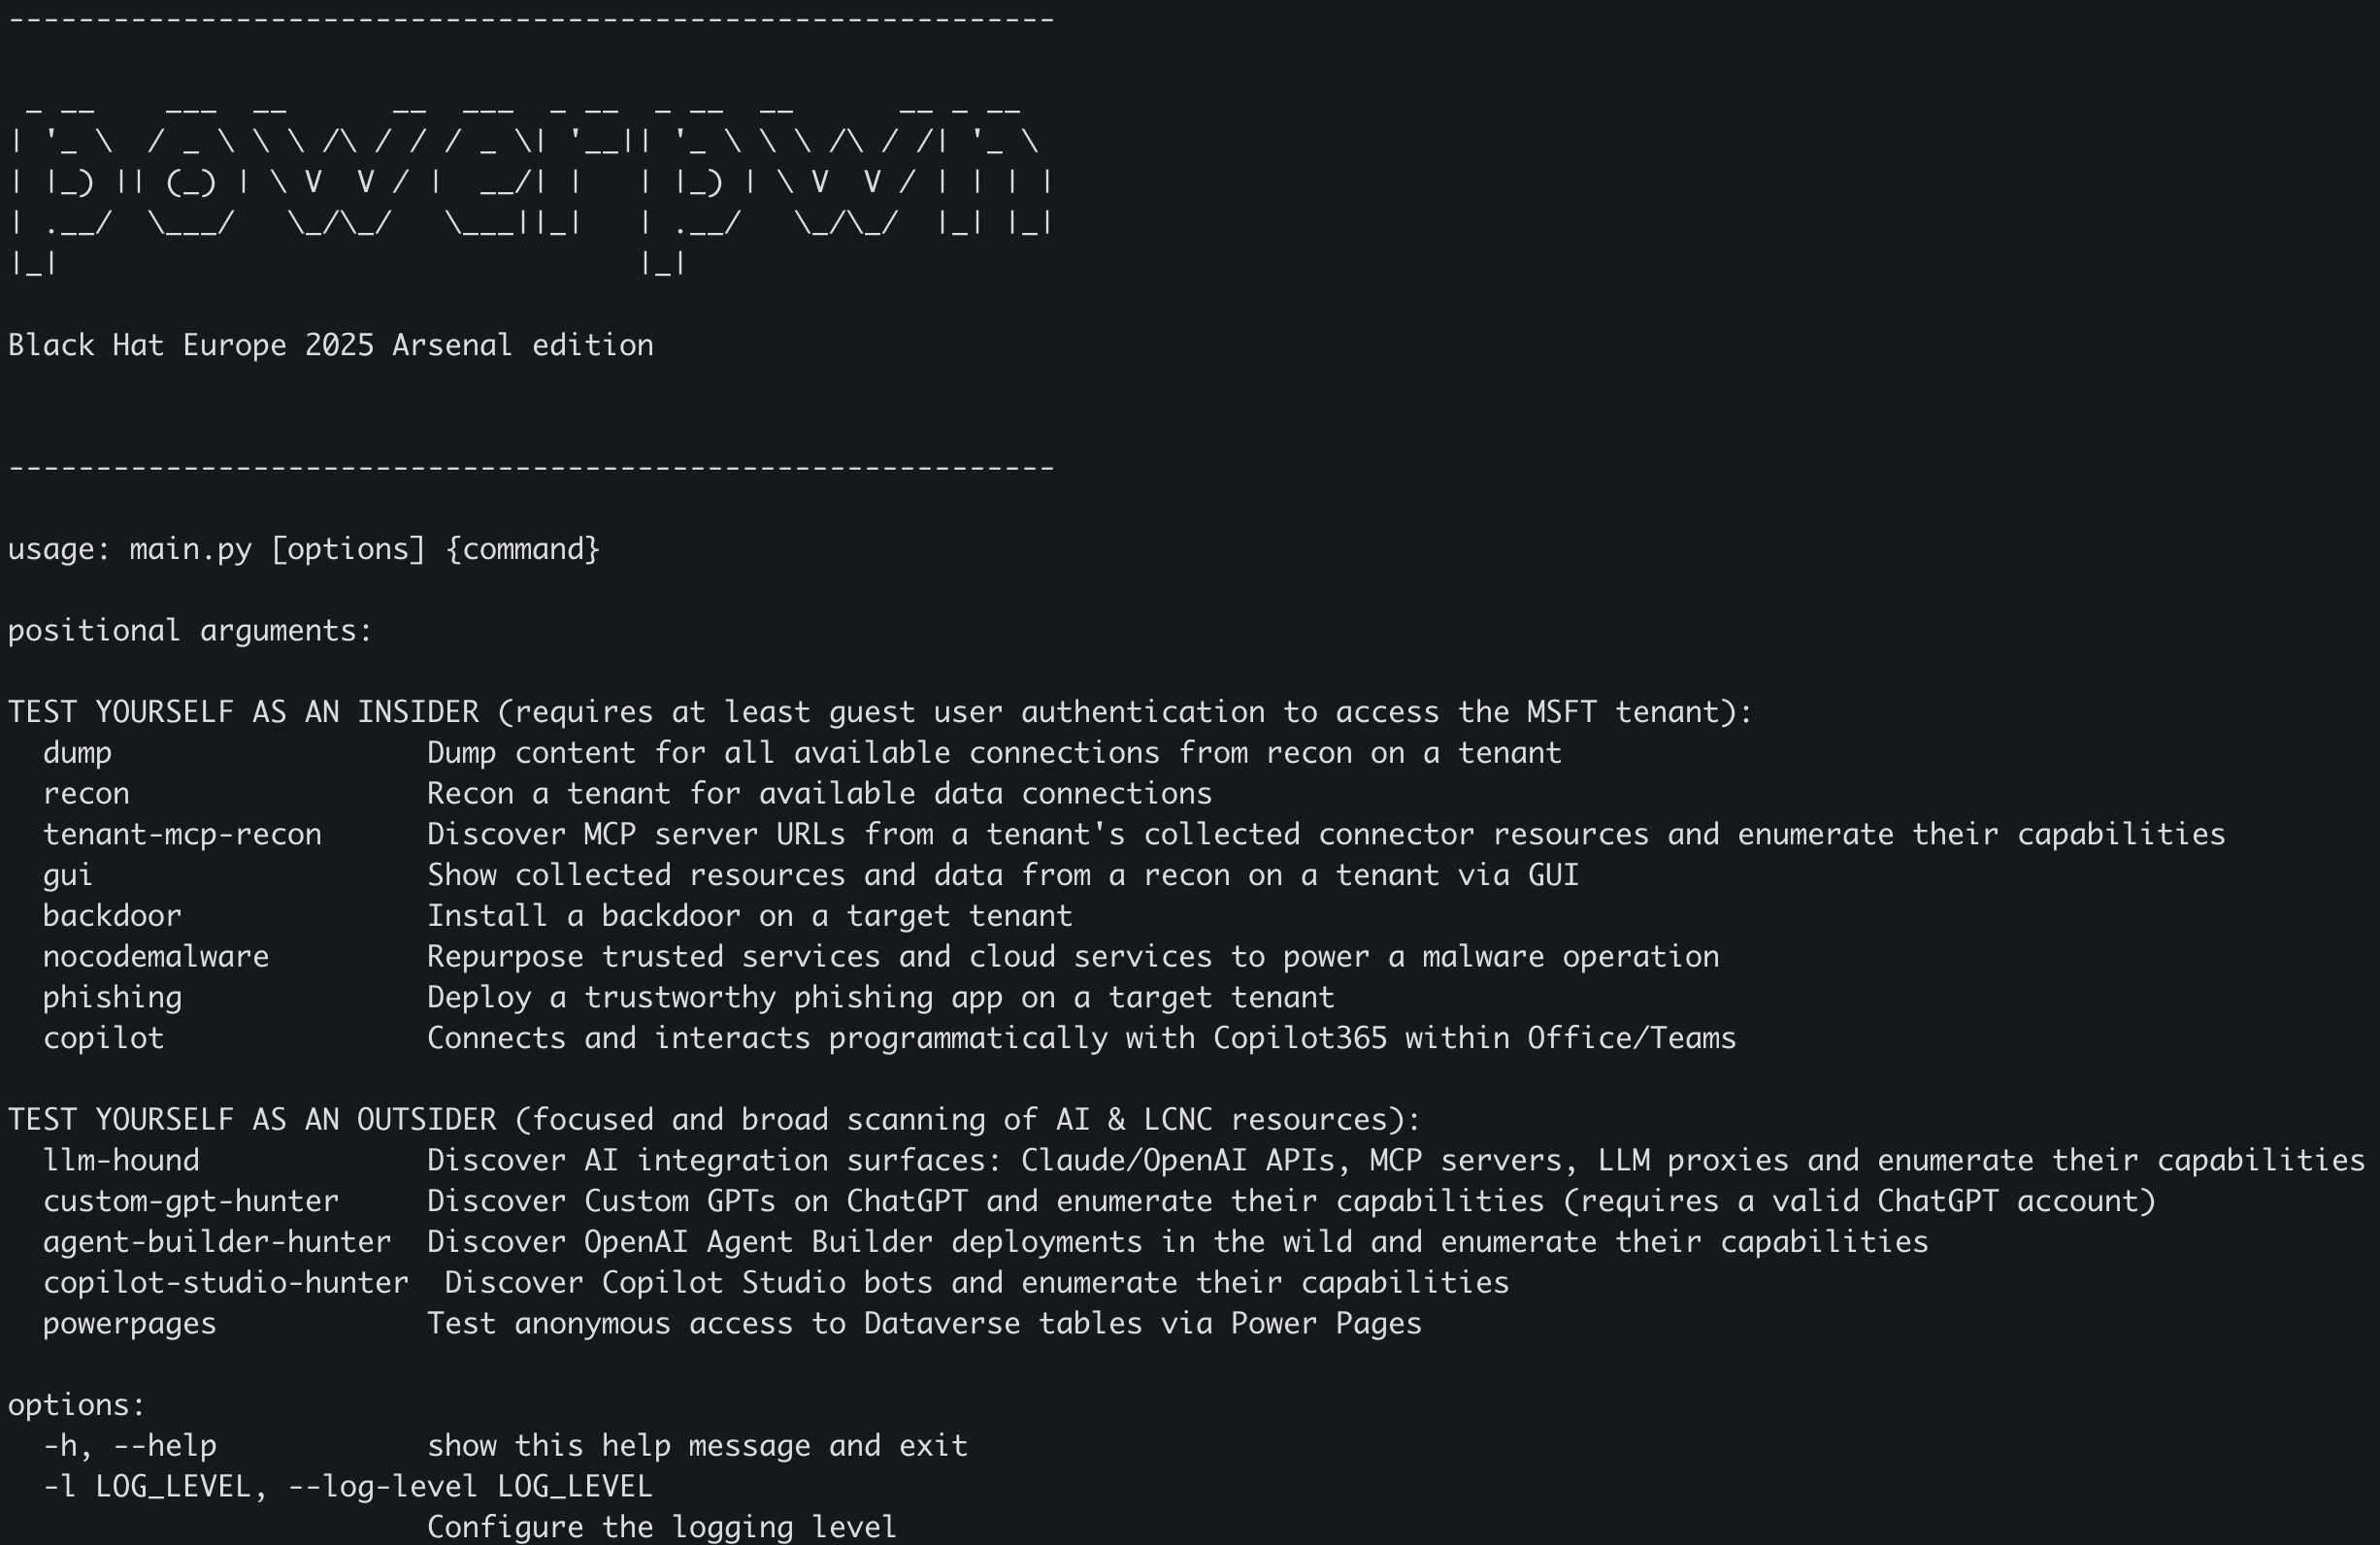 mbrg/power-pwn
An offensive/defense security toolset for discovery, recon and ethical assessment of AI Agents
 furqankhan1/cve-2019-13498
CVE-2019-13498
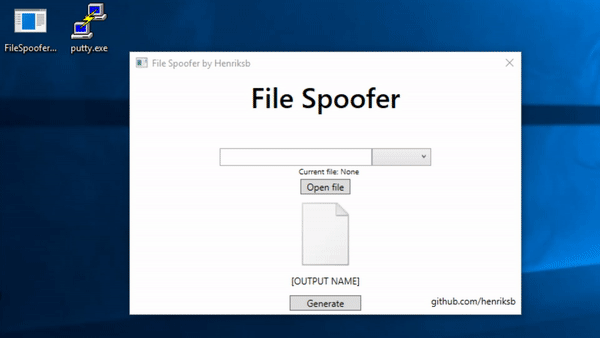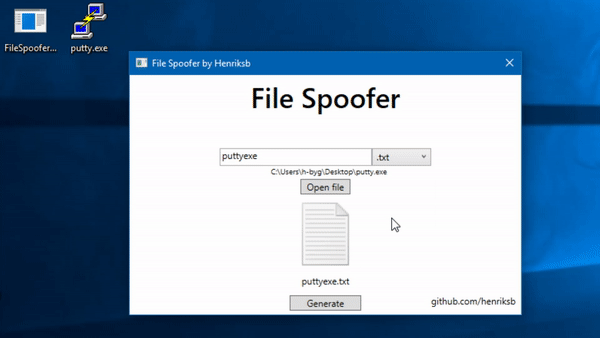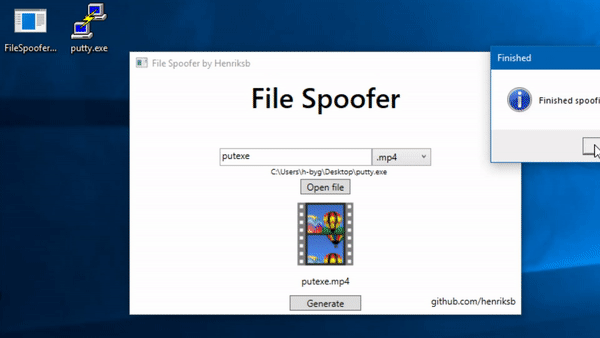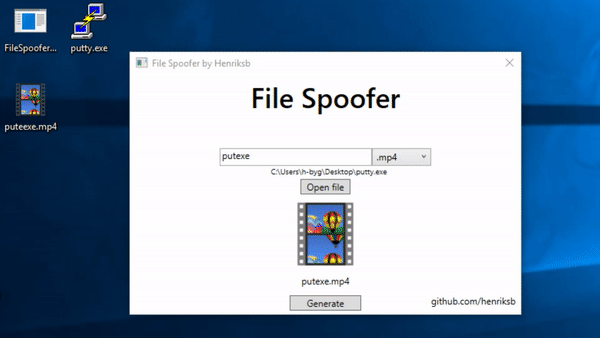 henriksb/extensionspoofer
Spoof file icons and extensions in Windows
 ka7ana/cve-2023-23397
PowerShell proof-of-concept for CVE-2023-23397 that exploits Outlook's ReminderSoundFile property to intercept Net-NTLMv2 hashes via SMB or WebDAV…
 j00sean/cve-2022-44666
Technical write-up and proof-of-concept for CVE-2022-44666, a Windows Contacts syslink control href attribute escape vulnerability enabling remote…
 helidem/cve-2025-24054_cve-2025-24071-poc
Proof of Concept for the NTLM Hash Leak via .library-ms CVE-2025-24054 / CVE-2025-24071