

blindxss-lite
 yuyudhn/blindxss-lite
A lightweight Blind XSS (Cross-Site Scripting) collector and payload server built with Flask
command-and-controldata-exfiltrationinformation-gathering+7
3
yuyudhn/blindxss-liteA lightweight Blind XSS (Cross-Site Scripting) collector and payload server built with Flask
 samsayen/jqueryingu
Valid JQuery that profiles the system and returns info to the server in a fake analytics GET request
 virtualsamuraii/flyphish
Deploy a phishing infrastructure on the fly.
 b1tbit/cve-2026-32201-exploit
Python exploit for CVE-2026-32201, a reflected XSS in Microsoft SharePoint Server, enabling unauthenticated spoofing and data modification via…
 muraenateam/muraena
Automates phishing and post-phishing activities with an almost-transparent reverse proxy that dynamically mirrors target web apps and interacts with…
 george0papasotiriou/cve-2026-22005-oauth-2.0-device-code-phishing-short-interval-
Proof-of-concept for CVE-2026-22005 showing OAuth 2.0 device code phishing via too-short polling interval, with vulnerable Flask server and exploit…
 diegomjx/cve-2023-41425-wondercms-authenticated-rce
Xss injection, WonderCMS 3.2.0 -3.4.2
 the-girl-who-lived/cve-2020-25498
Stored XSS via CSRF in Beetel 777VR1 Router
 komomon/cve-2022-30190-follina-office-msdt-fixed
Modified CVE-2022-30190 exploit tool for MS-MSDT Office RCE with custom docx template support, binary/command execution modes, and embedded HTTP…
 amirzargham/cve-2024-37383-exploit
Roundcube mail server exploit for CVE-2024-37383 (Stored XSS)
 vincentkaufmann/noapi-google-search-mcp
MCP server for Google search and page fetching using headless Chromium
 quinnbast/malicious-mcp
A Proof-of-concept repository showing how an untrusted MCP server can steal literally everything...
 goshs-labs/goshs
Feature-rich single-binary file server for red teamers and developers. HTTP/S · WebDAV · FTP/SFTP · SMB · LDAP/S · NTLM hash capture · DNS/SMTP…
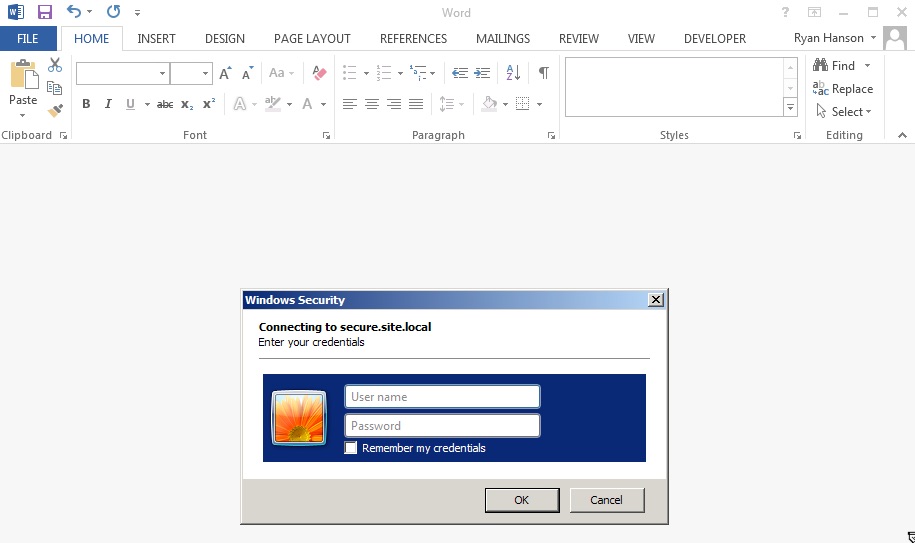 ryhanson/phishery
An SSL Enabled Basic Auth Credential Harvester with a Word Document Template URL Injector
 quickbreach/exchangerelayx
An NTLM relay tool to the EWS endpoint for on-premise exchange servers. Provides an OWA for hackers.
 arjunindia/fb-phisher-python
A python server tool based on flask , this tool can phish some Facebook credentials!
 mdsecactivebreach/farmer
Harvests NetNTLM hashes in Windows domains via a local WebDAV server, with LNK file poisoning and Office document field code injection for lateral…
 cryst4linqq/turkorat
Fully undetected grabber (grabs wallets, passwords, cookies, modifies discord client etc.)