
Evilginx3-Phishlets
This repository provides penetration testers and red teams with an extensive collection of dynamic phishing templates designed specifically for use…

This repository provides penetration testers and red teams with an extensive collection of dynamic phishing templates designed specifically for use…

Authorized social-engineering simulation framework with an isolated loopback lab, synthetic audience generation, pre-flight authorization checks, and…

PoC of the phishing through setting browser in the fullscreen mode

Contains evilginx phislets, gophish templates, burp suite extensions etc.

CVE-2024-4367 is a critical vulnerability (CVSS 9.8) in PDF.js, allowing arbitrary JavaScript code execution due to insufficient type checks on the…

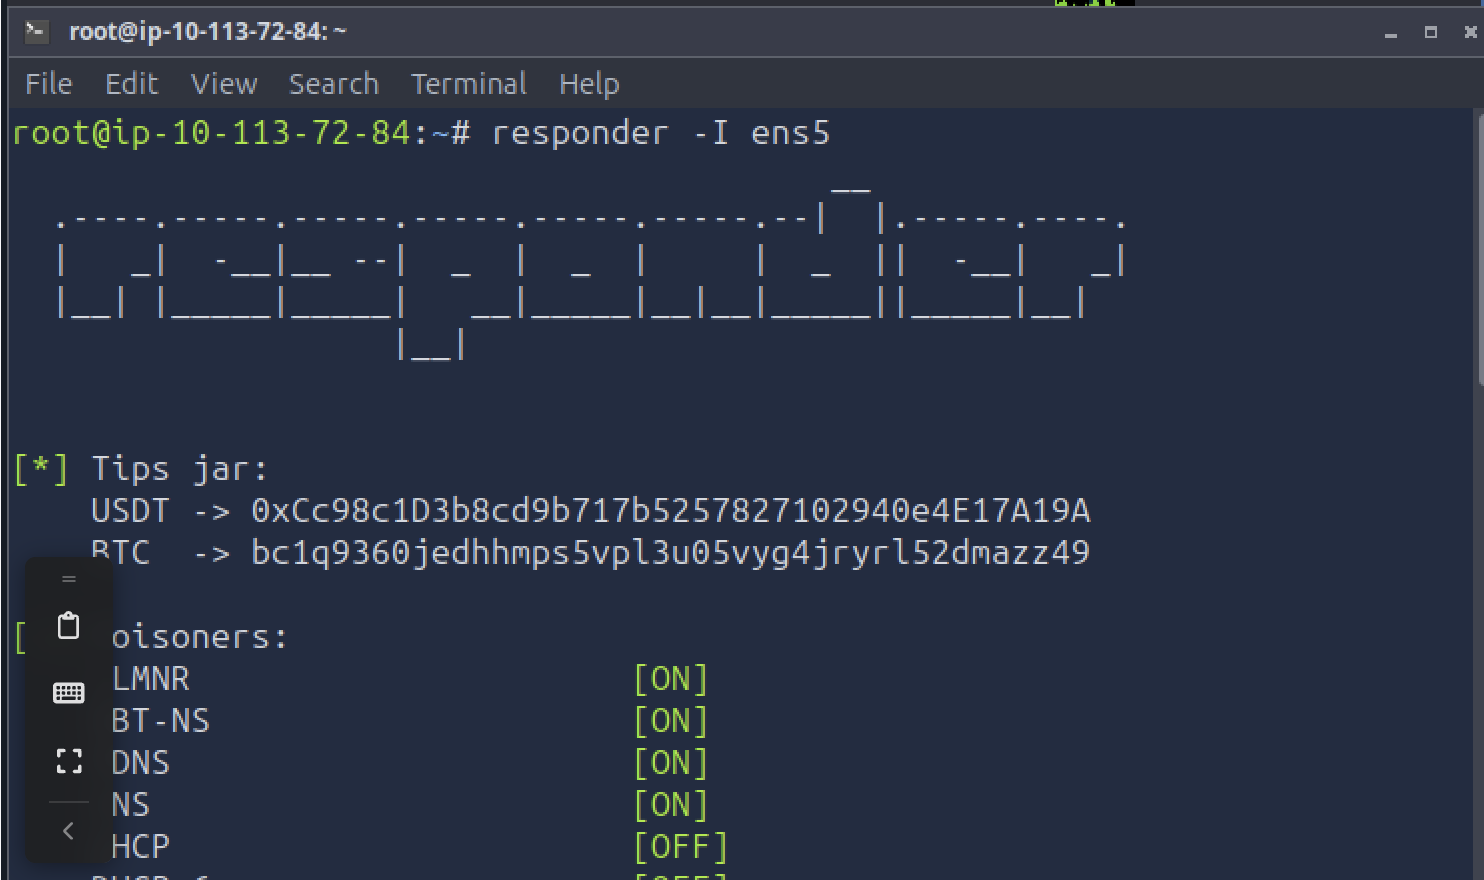
Documentation of my hands-on lab Moniker Link (CVE-2024-21413) completed on TryHackMe.

C# Tool to interact with MS Exchange based on MS docs

Repository of attack and defensive information for Business Email Compromise investigations

TryHackMe Moniker Link (CVE-2024-21413) walkthrough: Outlook Protected View bypass leading to NTLMv2 hash capture via a crafted moniker link.

Phishing simulation and awareness framework for node-based campaigns, credential capture, SMTP delivery, CAPTCHA, and optional browser credential…

CamJacking is a tool designed for use in human penetration testing tool. It is intended to simulate potential security threats by testing the…

CVE-2026-13156 Vulnerability Advisory & PoC — Discovered by Huynh Kien Minh (MinhHK).

CVE Reproduction: cve-2024-43451-ntlm_hash_disclosure_reproduction

Educational PDF files demonstrating client-side exploitation techniques, including calculator execution and directory browsing, for security testing…

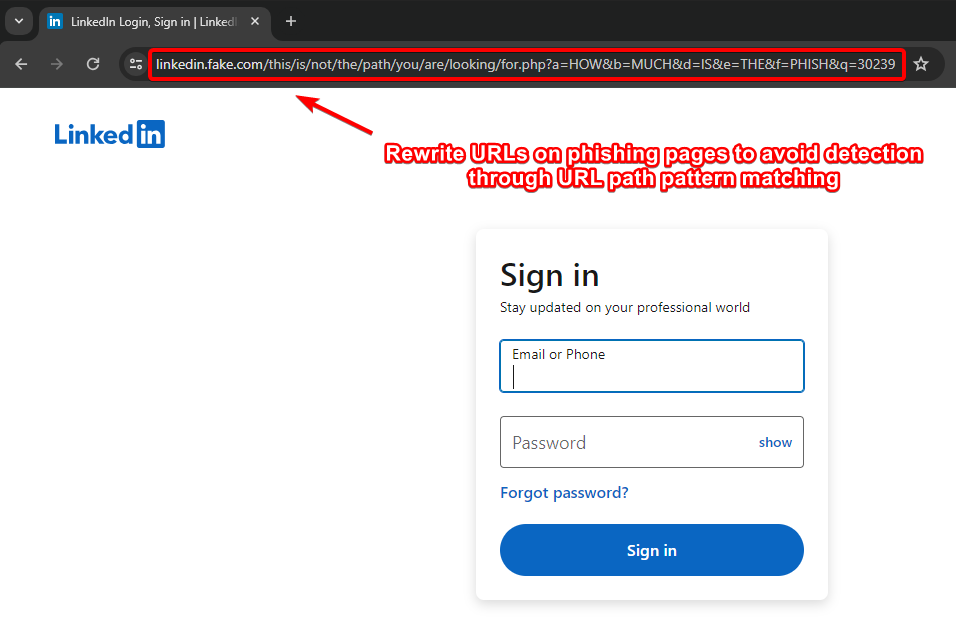
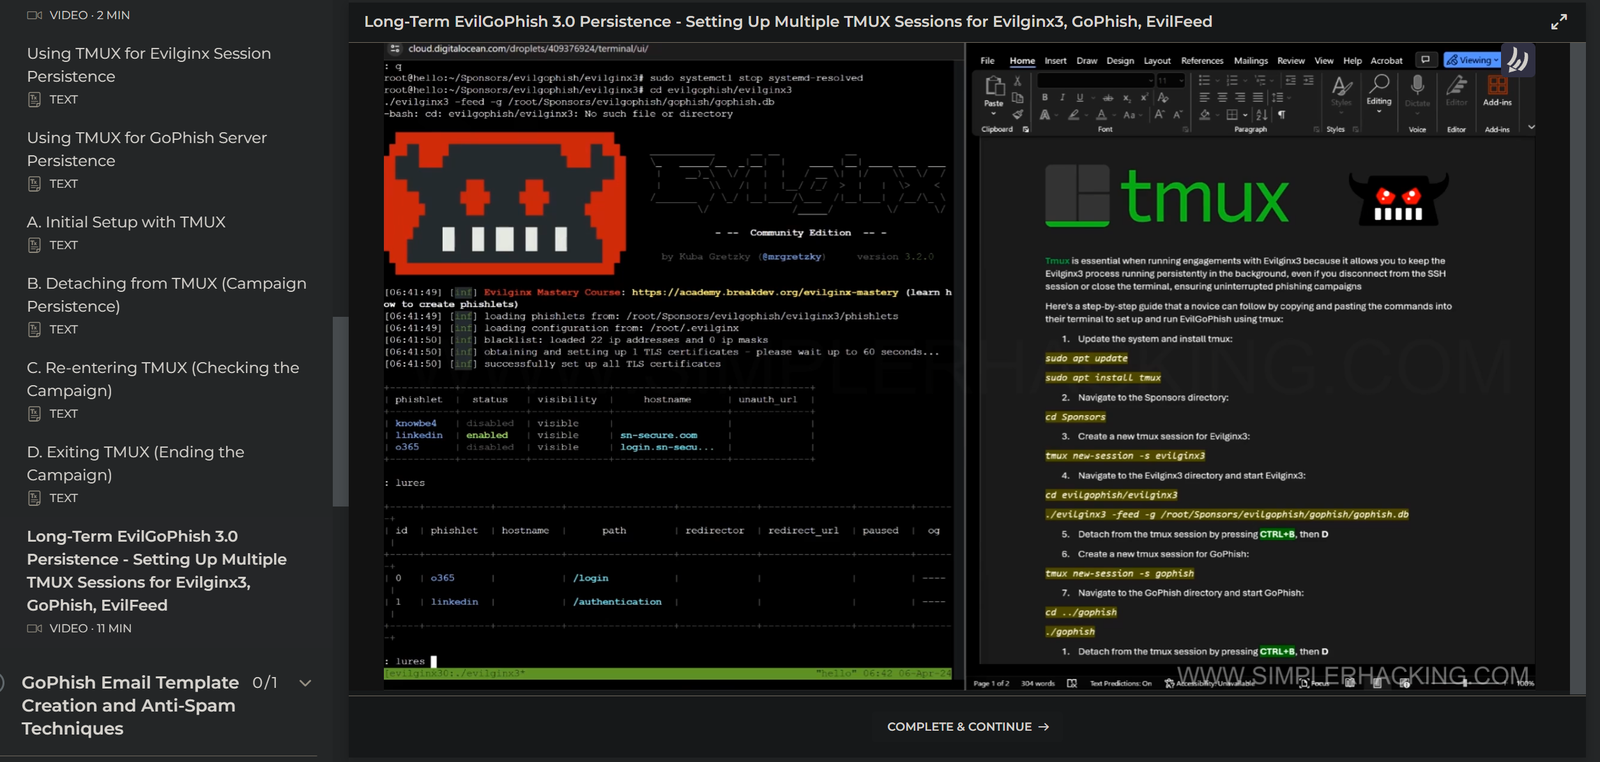
Evilginx Phishing Infrastructure Setup Guide - Securing Evilginx and Gophish Infrastructure, Removing IOCs, Phishing TTPs

This demonstration video shows how we can control the victim's device by sending the innocent-looking PDF file to the target which actually consists…

Potential malicious code execution via CHM hijacking (CVE-2019-9896)

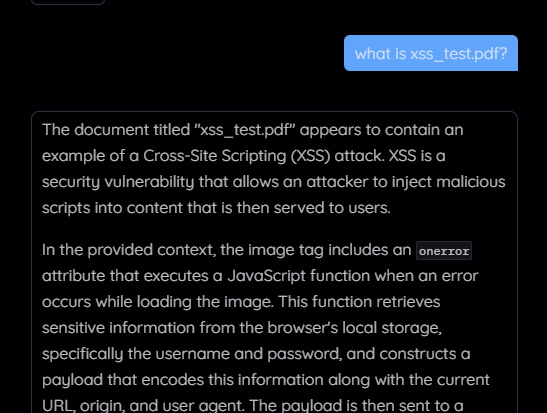
Public disclosure for CVE-2025-56526 and CVE-2025-56527 — Stored XSS via unsanitized PDF content rendering and plaintext credential exposure in…