SmuggleMyPayload
Generates HTML smuggling pages that embed and reconstruct files client-side via JavaScript, with payload encoding, chunking, obfuscation, and…

Generates HTML smuggling pages that embed and reconstruct files client-side via JavaScript, with payload encoding, chunking, obfuscation, and…

Dependency-free Python PoC generator for CVE-2025-24071 that crafts a malicious .library-ms file in a ZIP to trigger Windows Explorer NTLM hash…

Collection of offensive red team scripts including process termination, SPF bypass for phishing, password spraying, and ColdFusion password…

Exploit PoC for CVE-2026-27579, a CORS misconfiguration in Appwrite backend, demonstrating credentialed account data theft via malicious phishing…

Python exploit for CVE-2026-32201, a reflected XSS in Microsoft SharePoint Server, enabling unauthenticated spoofing and data modification via…

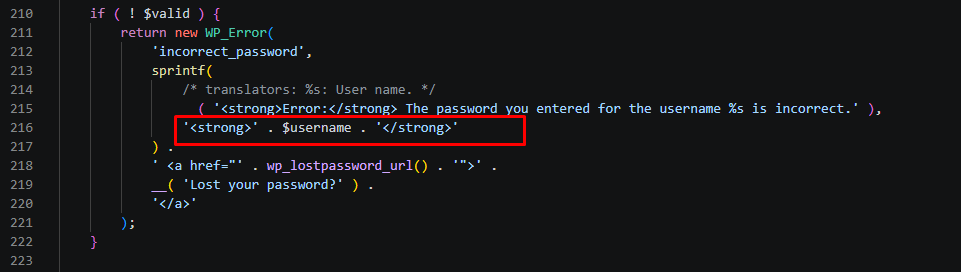
Proof-of-concept exploit for CVE-2026-64638: reflected XSS in WordPress login chained with DOM clobbering to achieve admin account takeover and…

PoC exploit chain for WordPress pre-auth XSS to RCE via DOM clobbering, REST JSONP/SOME, and plugin upload, with Docker lab verification and…

macOS Initial Access Payload Generator

Example on how to injection(currently under work) of keylogger js through Safari Extension(that part done)

xll windows reverse shell

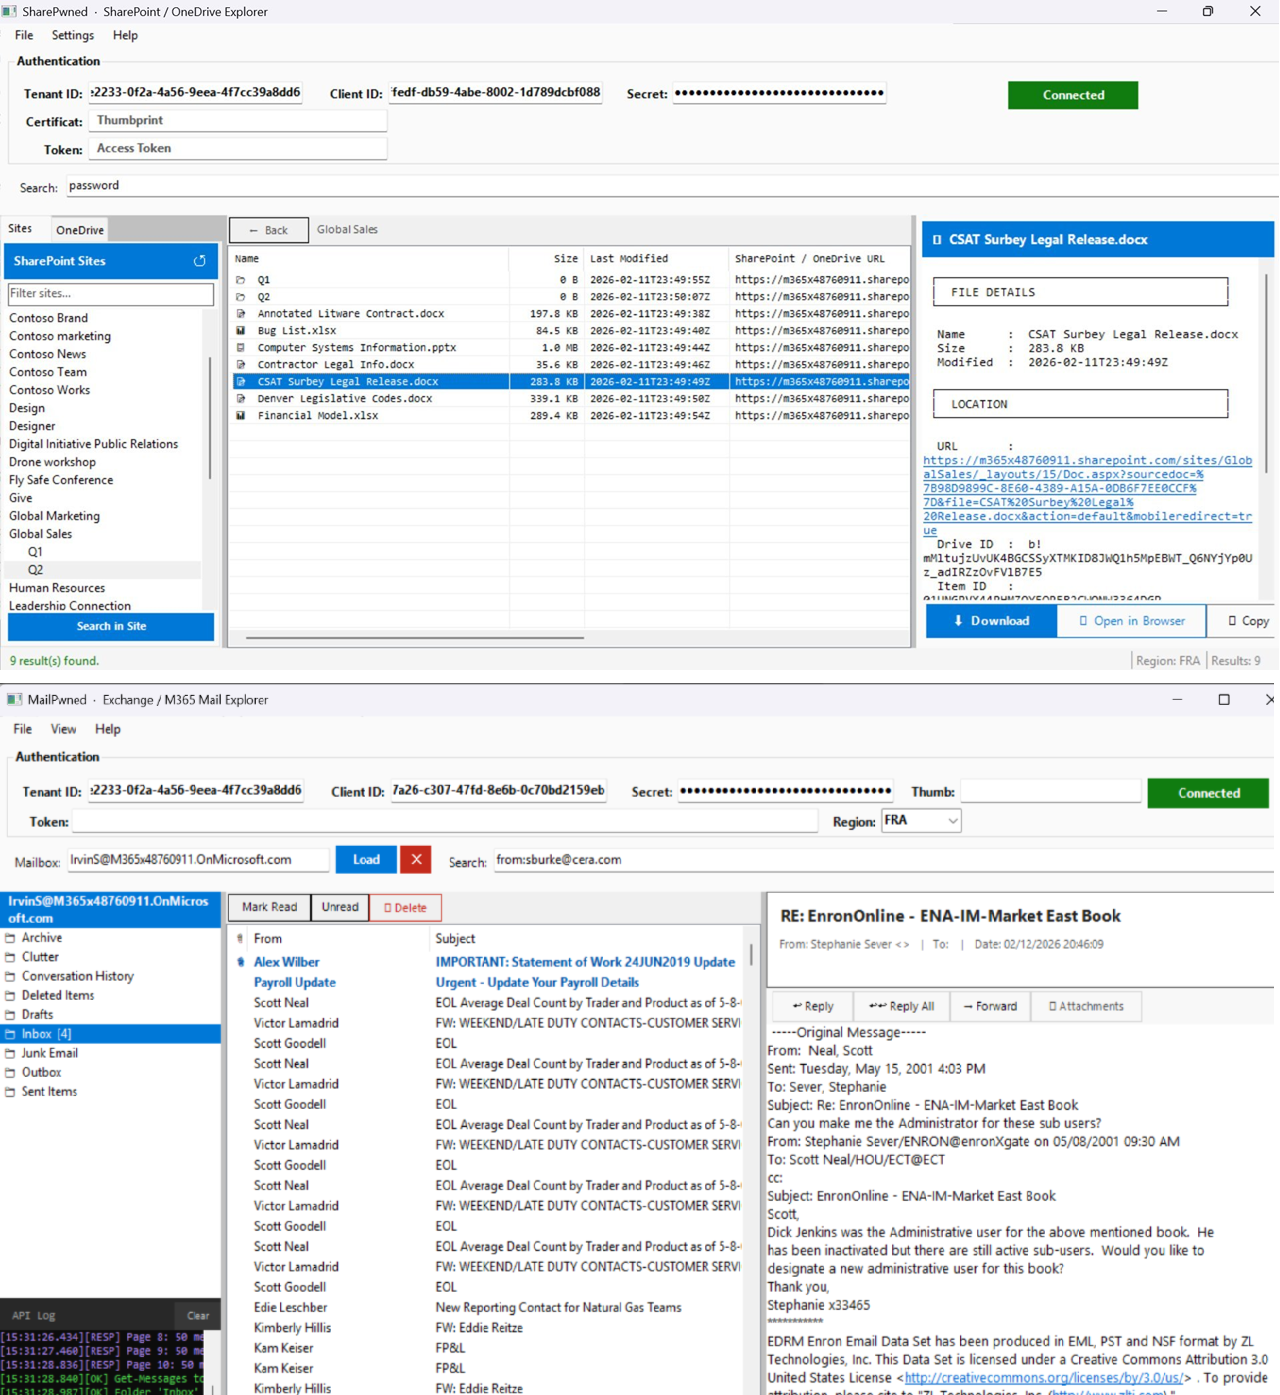
Two WinForms GUI tools for enumerating, searching, and exfiltrating data from M365 environments using application-level OAuth tokens


Self contained htaccess shells and attacks

Educational PDF files demonstrating client-side exploitation techniques, including calculator execution and directory browsing, for security testing…

A Windows Remote Administration Tool in Visual Basic with UNC paths

Bella is a pure python post-exploitation data mining tool & remote administration tool for macOS. 🍎💻

Read more at Medium