

Lab-RATS-v1.6
 k4n3co/lab-rats-v1.6
Lab-RATS is a powerful and lightweight Android Remote Administration Tool full of features that enables remote monitoring, management and interaction…
android-securitycommand-and-controldata-exfiltration+8
80
k4n3co/lab-rats-v1.6Lab-RATS is a powerful and lightweight Android Remote Administration Tool full of features that enables remote monitoring, management and interaction…
 shaheeryasirofficial/smugglemypayload
Generates HTML smuggling pages that embed and reconstruct files client-side via JavaScript, with payload encoding, chunking, obfuscation, and…
 gmh5225/fullscreenbrowserphishing
PoC of the phishing through setting browser in the fullscreen mode
 bardlaudian/cve-2025-24071
Dependency-free Python PoC generator for CVE-2025-24071 that crafts a malicious .library-ms file in a ZIP to trigger Windows Explorer NTLM hash…
 mr-un1k0d3r/redteamscripts
Collection of offensive red team scripts including process termination, SPF bypass for phishing, password spraying, and ColdFusion password…
 samsayen/jqueryingu
Valid JQuery that profiles the system and returns info to the server in a fake analytics GET request
 muraenateam/muraena
Automates phishing and post-phishing activities with an almost-transparent reverse proxy that dynamically mirrors target web apps and interacts with…
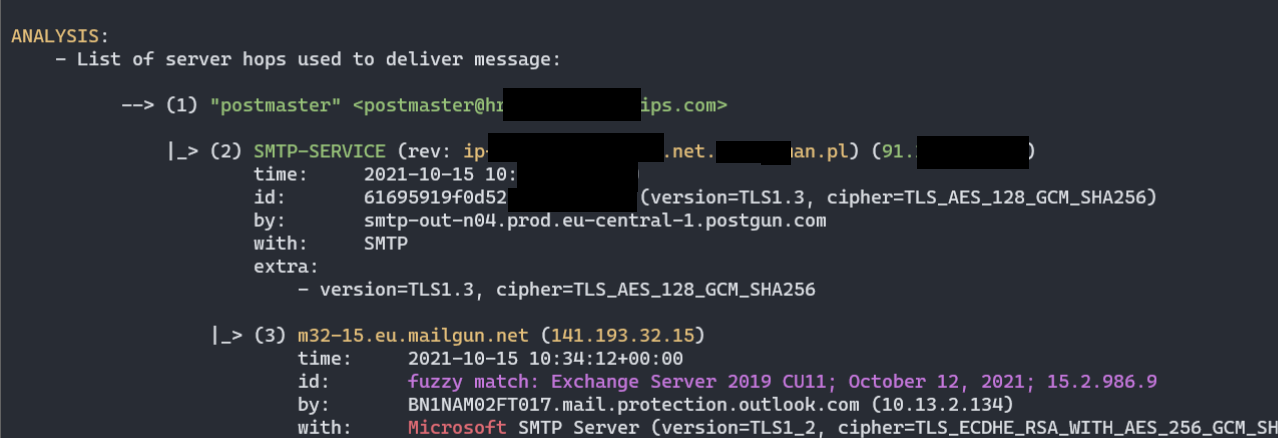 mgeeky/decode-spam-headers
A script that helps you understand why your E-Mail ended up in Spam
 ceramicskate0/sharpexchange
C# Tool to interact with MS Exchange based on MS docs
 nccgroup/droppedconnection
Emulates a Cisco ASA Anyconnect VPN service for credential harvesting and VBS payload delivery in red team phishing operations.
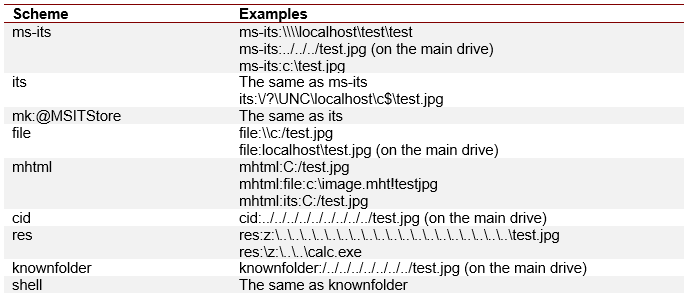 nccgroup/outlookleaktest
The Outlook HTML Leak Test Project
 cappricio-securities/socialengineering
SEt framework
 praetorian-inc/oauthseeker
A malicious OAuth application that can be leveraged for both internal and external phishing attacks targeting Microsoft Azure and Office365 users.
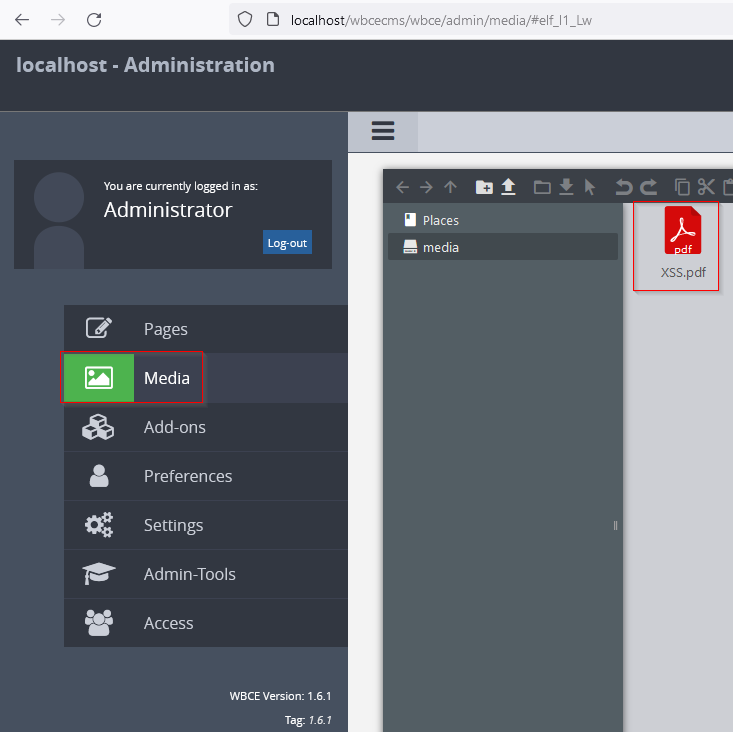 sromanhu/cve-2023-43871-wbce-arbitrary-file-upload--xss---media
WBCE 1.6.1 is affected by File Upload - XSS vulnerability that allows attackers to upload a PDF file with a hidden XSS that when executed will launch…
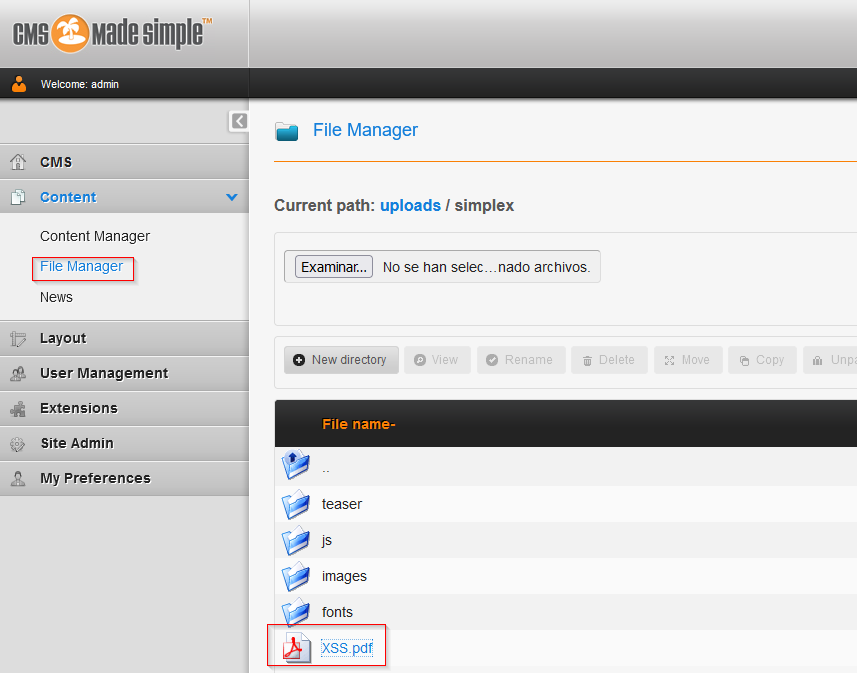 sromanhu/cve-2023-43872-cmsmadesimple-arbitrary-file-upload--xss---file-manager
CMSmadesimple 2.2.18 is affected by File Upload - XSS vulnerability that allows attackers to upload a PDF file with a hidden XSS that when executed…
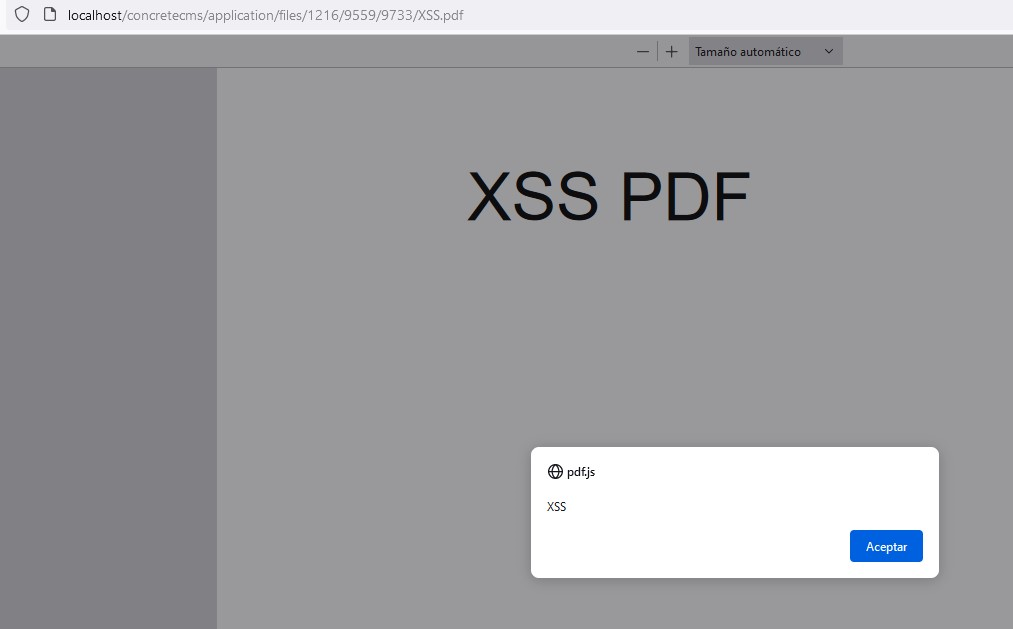 sromanhu/cve-2023-44763_concretecms-arbitrary-file-upload-thumbnail
ConcreteCMS v.9.2.1 is affected by Arbitrary File Upload vulnerability that allows Cross-Site Scriting (XSS) Stored.
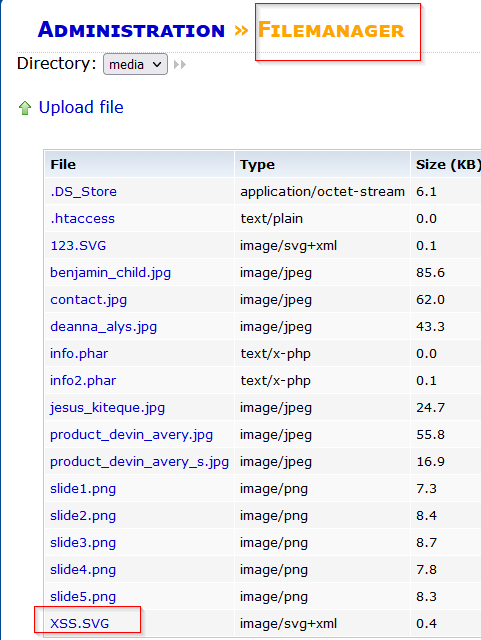 sromanhu/cve-2023-44767_ritecms-file-upload--xss---filemanager
RiteCMS 3.0 is affected by File Upload - XSS vulnerability that allows attackers to upload a PDF file with a hidden XSS that when executed will…
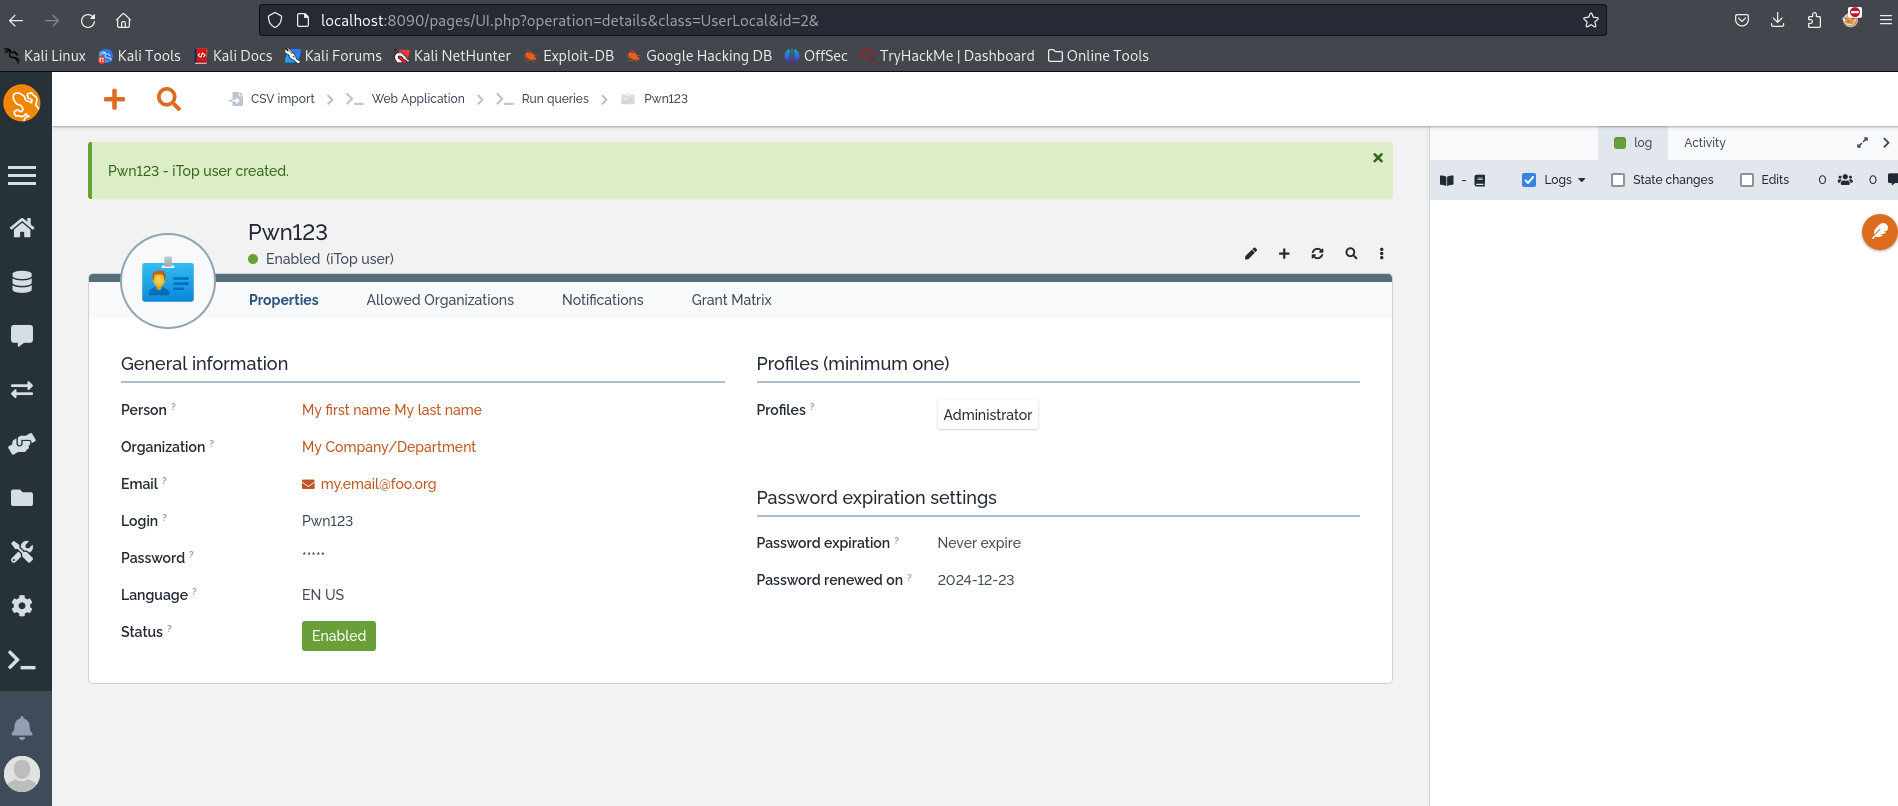 harshit-mashru/itop-cves-exploit
This repository contains exploits for iTOP CVE-2024-52002, 52000, 31998, 31448 that involve CSRF+XSS chaining to get RCE