
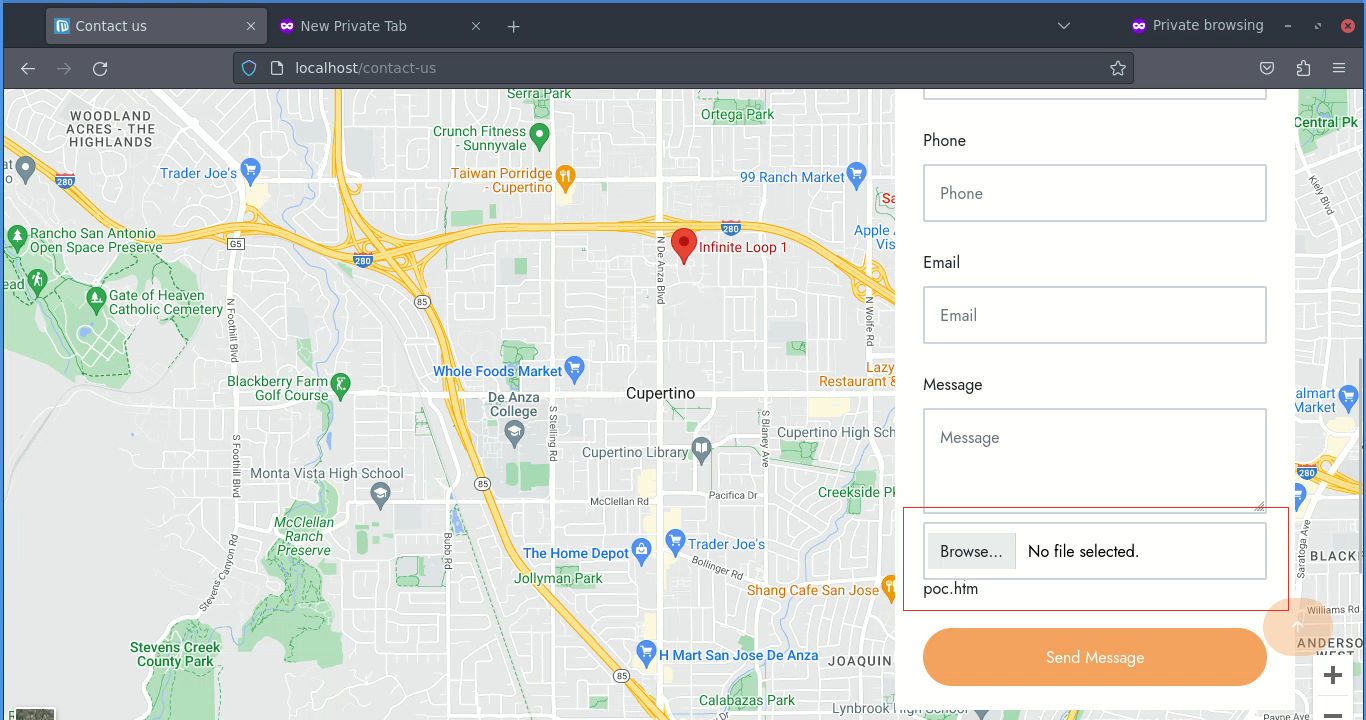
CVE-2023-49052
 cyber-wo0dy/cve-2023-49052
Microweber version 2.0.4 vulnerable to "Uploading Malicious Files"
exploitationmalware-analysisphishing-tools+2
cyber-wo0dy/cve-2023-49052Microweber version 2.0.4 vulnerable to "Uploading Malicious Files"
 mdsecactivebreach/farmer
Harvests NetNTLM hashes in Windows domains via a local WebDAV server, with LNK file poisoning and Office document field code injection for lateral…
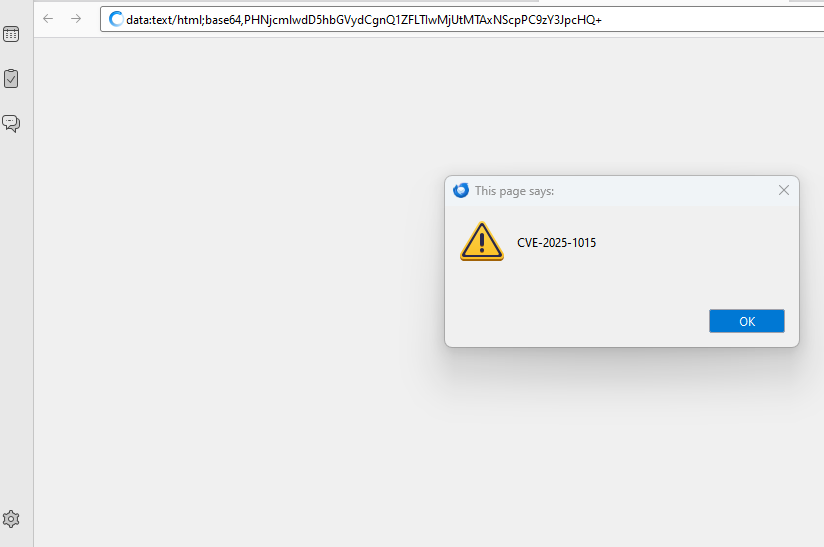 r3m0t3nu11/cve-2025-1015
an attacker to create and export an address book containing a malicious payload in a field. For example, in the “Other” field of the Instant…