

zaproxy
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
android-securityapi-securityapi-security-testing+15
15.9k
zaproxy/zaproxyOpen-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 undeadsec/socialfish
Modern dynamic phishing toolkit for authorized red team exercises. Clones login pages, captures credentials, cookies, and 2FA codes with a live…
 kleiton0x00/xsscope
XSScope is one of the most powerful and advanced GUI Framework for Modern Browser exploitation via XSS.
 mrd0x/webview2-cookie-stealer
Injects JavaScript keylogger into WebView2 pages to capture keystrokes and exfiltrate cookies from Microsoft authentication sessions via HTTP GET…
 sobri3195/pegasus-neo
PEGASUS-NEO is a comprehensive penetration testing framework designed for security professionals and ethical hackers. It combines multiple security…
 corvralabs/evilneko
Automated container orchestration tool for Browser-in-the-Browser (BITB) phishing attacks, enabling red teams to scale multi-target infrastructure…
 romain-deperne/cve-2026-33715
Unauthenticated SSRF and open email relay in Chamilo LMS — CVE-2026-33715 / CVSS 7.2
 charlesgargasson/cve-2023-41425
XSS-to-RCE exploit for Wonder CMS 3.2.0–3.4.2 with automated payload delivery, reverse shell, and cookie theft via malicious theme installation.
 d7x/cve-2020-12432
Proof-of-concept exploit for stored XSS and insecure permissions in Collabora CODE <= 4.2.2 via the Vereign WOPI API, enabling account hijacking and…
 security-avs/cve-2020-16270
Proof-of-concept for CVE-2020-16270, an XSS vulnerability in OLIMPOKS under 3.3.39, demonstrating remote injection of malicious JavaScript to steal…
 mbadanoiu/cve-2021-46366
CVE-2021-46366: Credential Bruteforce Attack via CSRF + Open Redirect in Magnolia CMS
 trustedsec/social-engineer-toolkit
The Social-Engineer Toolkit (SET) repository from TrustedSec - All new versions of SET will be deployed here.
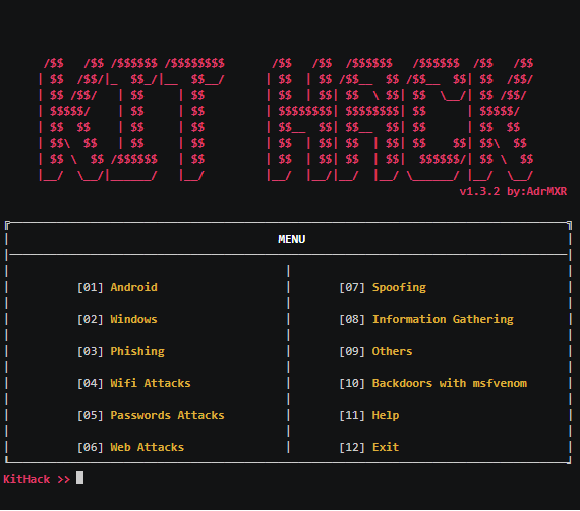 adrmxr/kithack
Hacking tools pack & backdoors generator.
 x3omdax/penbox
PenBox - A Penetration Testing Framework - The Tool With All The Tools , The Hacker's Repo
 dionach/phemail
PhEmail is a python open source phishing email tool that automates the process of sending phishing emails as part of a social engineering test
 zadewg/rius
CVE-2020-20093; 20094; 20095; 20096, 2022-28345 RTLO Injection URI Spoofing
 wifiphisher/wifiphisher
Rogue Access Point framework for red team engagements and Wi-Fi security testing. Performs Evil Twin, KARMA, and Known Beacons attacks to achieve…
 mrd0x/bitb
HTML/CSS/JS templates for Browser-In-The-Browser phishing attacks, embedding fake login windows with customizable titles, domains, and phishing links…