

wifipumpkin3
 p0cl4bs/wifipumpkin3
Powerful framework for rogue access point attack.
captcha-bypassdns-analysisphishing+5
p0cl4bs/wifipumpkin3Powerful framework for rogue access point attack.
 silverfoxx/pwnstar
PwnSTAR (Pwn SofT-Ap scRipt) - for all your fake-AP needs!
 sanupl/cve-2024-34568
In LetterPress plugin <= 1.2.1 is vulnerable to Cookie Stealing Vulnerability. An attacker can able to steal the cookies by injecting the JavaScript…
 filipegaudard/cve-2026-33149-poc
Proof-of-concept exploit for CVE-2026-33149, a Host header injection in Tandoor Recipes that enables invite link poisoning and cache poisoning.…
 ajansha/cve-2025-55903
Proof of concept for CVE-2025-55903, a stored HTML injection in PerfexCRM allowing authenticated users to inject malicious HTML into invoices and…
 polling-repo-continua/cve-2022-25257
Proof-of-concept exploit for CVE-2022-25257: CSRF parameter injection in SAS Logon 9.4 enabling warning-message spoofing for phishing attacks.
 echo-devim/cve-2022-48429_poc
Proof-of-concept exploit for CVE-2022-48429, a stored cross-site scripting vulnerability in JetBrains YouTrack dashboards enabling low-privileged…
 e1tex/cve-2023-48104
Proof-of-concept exploit demonstrating HTML injection in SOGo Web Client before 5.9.1, enabling phishing attacks via malicious forms in email bodies.
 mlniumm/cve-2025-28073
Proof-of-concept for a reflected XSS vulnerability in phpList 3.6.15 via the /lists/dl.php endpoint, enabling session hijacking and arbitrary…
 mbadanoiu/cve-2020-12625
CVE-2020-12625: Cross-Site Scripting via Malicious HTML Attachment in Roundcube Webmail
 abdurahmon3236/cve-2024-6529
Proof-of-concept scripts demonstrating reflected XSS in the Ultimate Classified Listings WordPress plugin and admin cookie theft via crafted payloads…
 s3cur3th1ssh1t/offensivevba
This repo covers some code execution and AV Evasion methods for Macros in Office documents
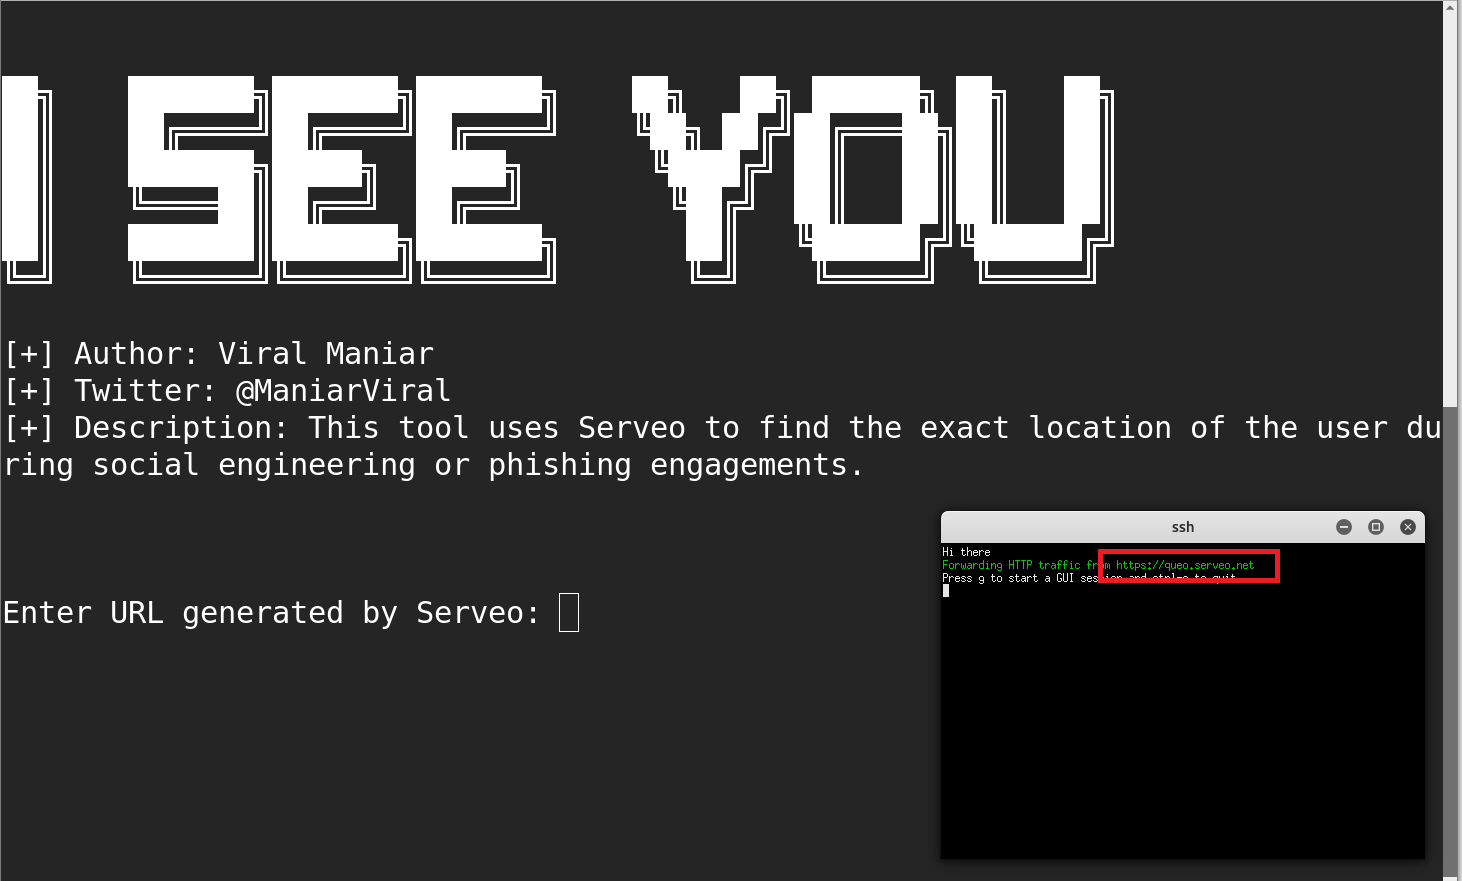 viralmaniar/i-see-you
ISeeYou is a Bash and Javascript tool to find the exact location of the users during social engineering or phishing engagements. Using exact location…
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 m4cs/babysploit
👶 BabySploit Beginner Pentesting Toolkit/Framework Written in Python 🐍
 d4rks3c-group/hiddeneyereborn
HiddenEye Reborn in better shape than ever, rewritten from scratch and adapted to modern world
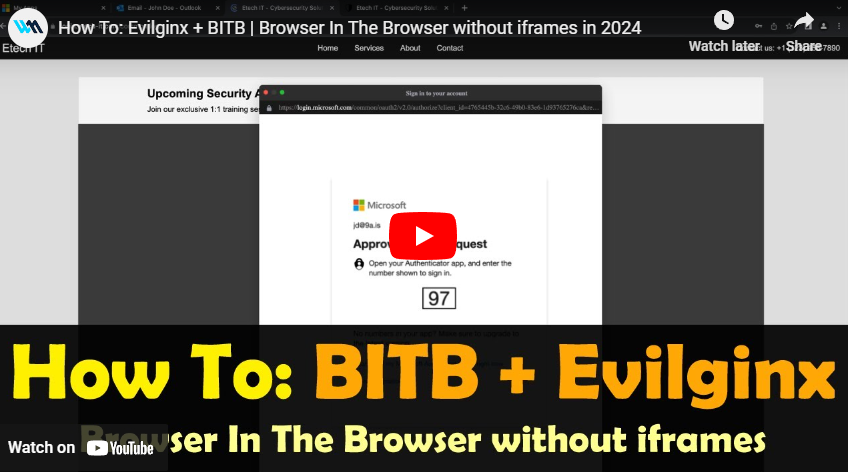 waelmas/frameless-bitb
A new approach to Browser In The Browser (BITB) without the use of iframes, allowing the bypass of traditional framebusters implemented by login…
 kgretzky/evilqr
Proof-of-concept to demonstrate dynamic QR swap phishing attacks in practice.