wordpress-rce-vapt-cve-2020-25213

Educational cybersecurity project demonstrating exploitation and mitigation of CVE-2020-25213 (WordPress File Manager Plugin RCE). Includes malware…

Educational cybersecurity project demonstrating exploitation and mitigation of CVE-2020-25213 (WordPress File Manager Plugin RCE). Includes malware…

Educational lab demonstrating CVE-2024-21413 exploitation in Outlook to leak NTLM hashes via malicious UNC links, with custom SMTP/POP3…

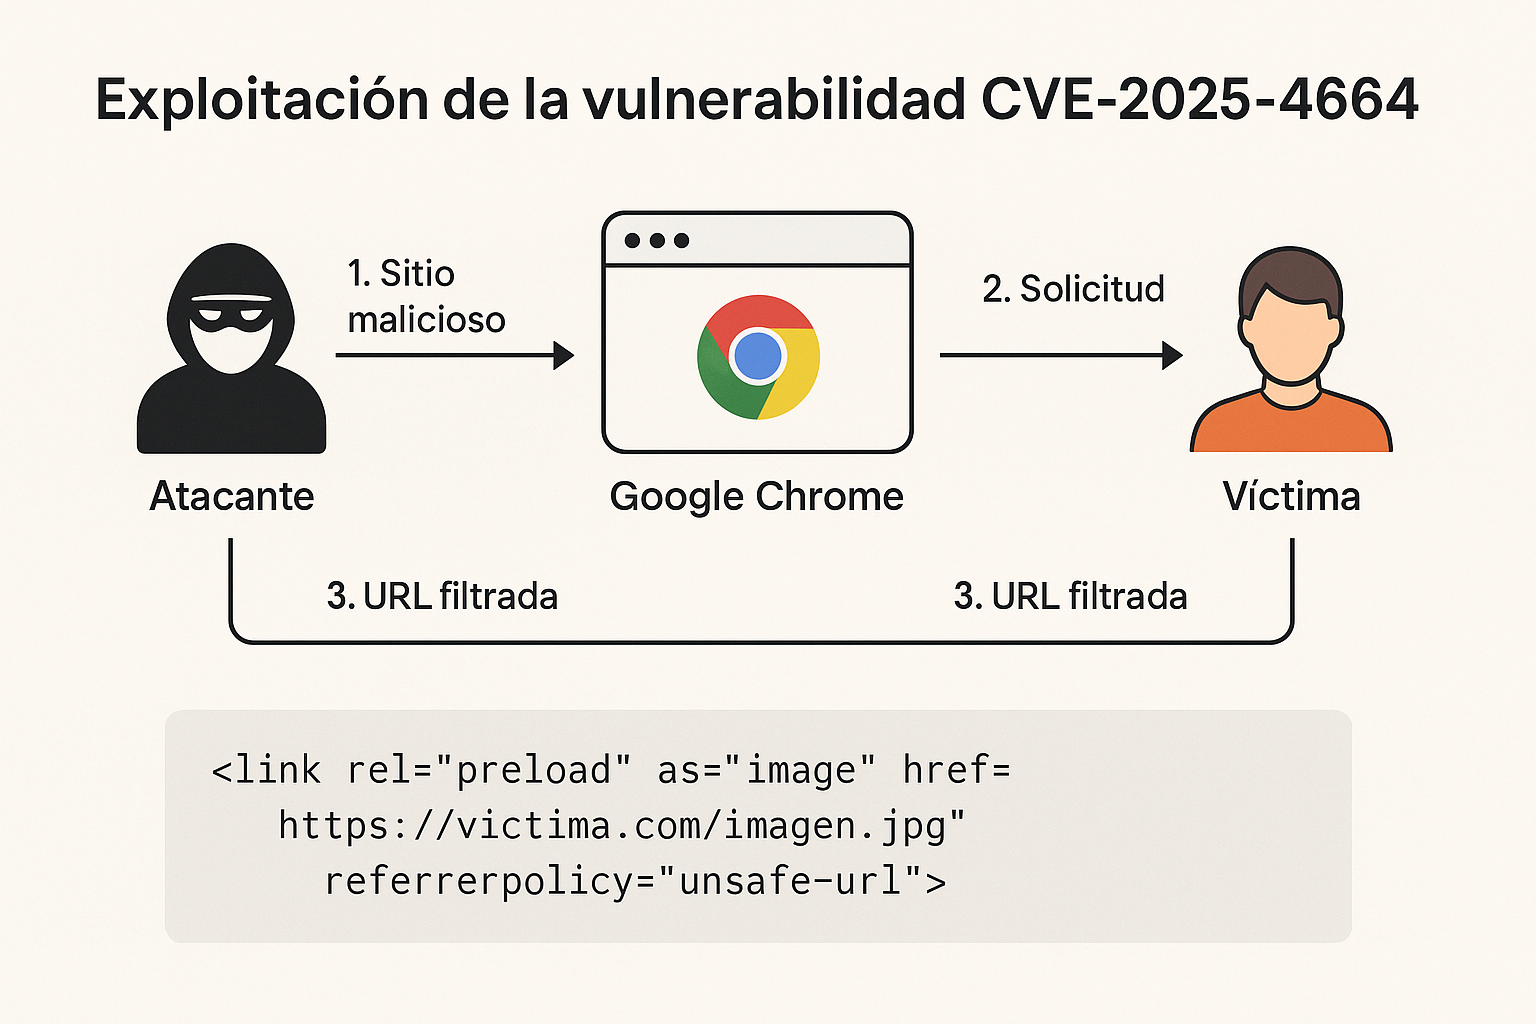
Educational demo of CVE-2025-4664, a Chrome Loader vulnerability enabling cross-origin data leakage via referrer-policy manipulation. Includes a…

A Proof of Concept for the CVE-2021-46398 flaw exploitation

Purple team project exploiting CVE-2023-23397 Outlook NTLM leak with phishing delivery, plus Sigma/Wazuh detections mapped to MITRE ATT&CK for the…

TryHackMe room walkthrough of CVE-2024-21413, covering the Outlook Moniker Link Protected View bypass, NTLM hash leaking, and credential capture with…

Educational Proof-of-Concept for the CVE-2022-30190 (Follina) vulnerability.

Social Engineering Tool


Generates HTML smuggling pages that embed and reconstruct files client-side via JavaScript, with payload encoding, chunking, obfuscation, and…

Addressbar spoofing through blob URL (Firefox browser). An attack can use a blob URL and script to spoof an arbitrary addressbar URL prefaced by…

Detailed proof-of-concept and technical analysis for CVE-2026-2441, a Chrome CSS use-after-free vulnerability enabling sandboxed renderer RCE via…

CloudSchool v3.0.1 is vulnerable to Cross Site Scripting (XSS). A normal user can steal session cookies of the admin users through notification…