
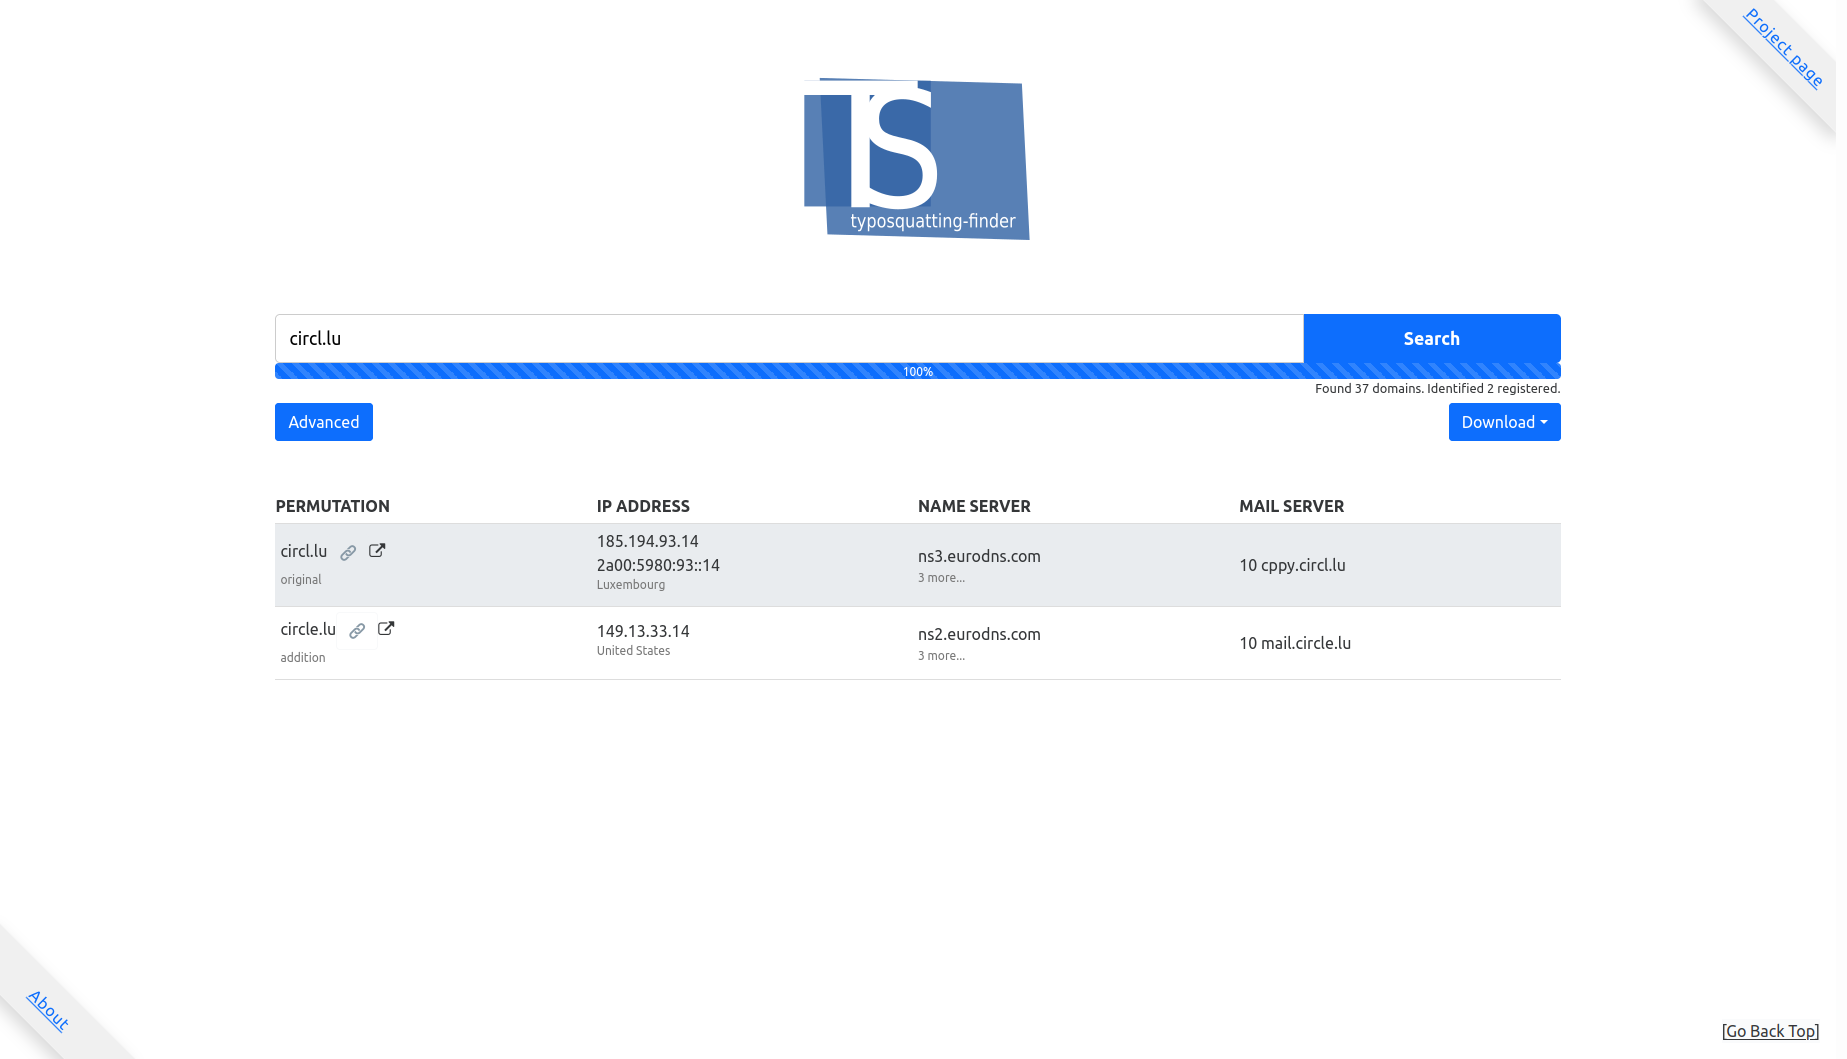
ail-typo-website
 typosquatter/ail-typo-website
Website for ail-typo-squatting library
dns-analysisinformation-gatheringosint+2
768 months ago
typosquatter/ail-typo-websiteWebsite for ail-typo-squatting library
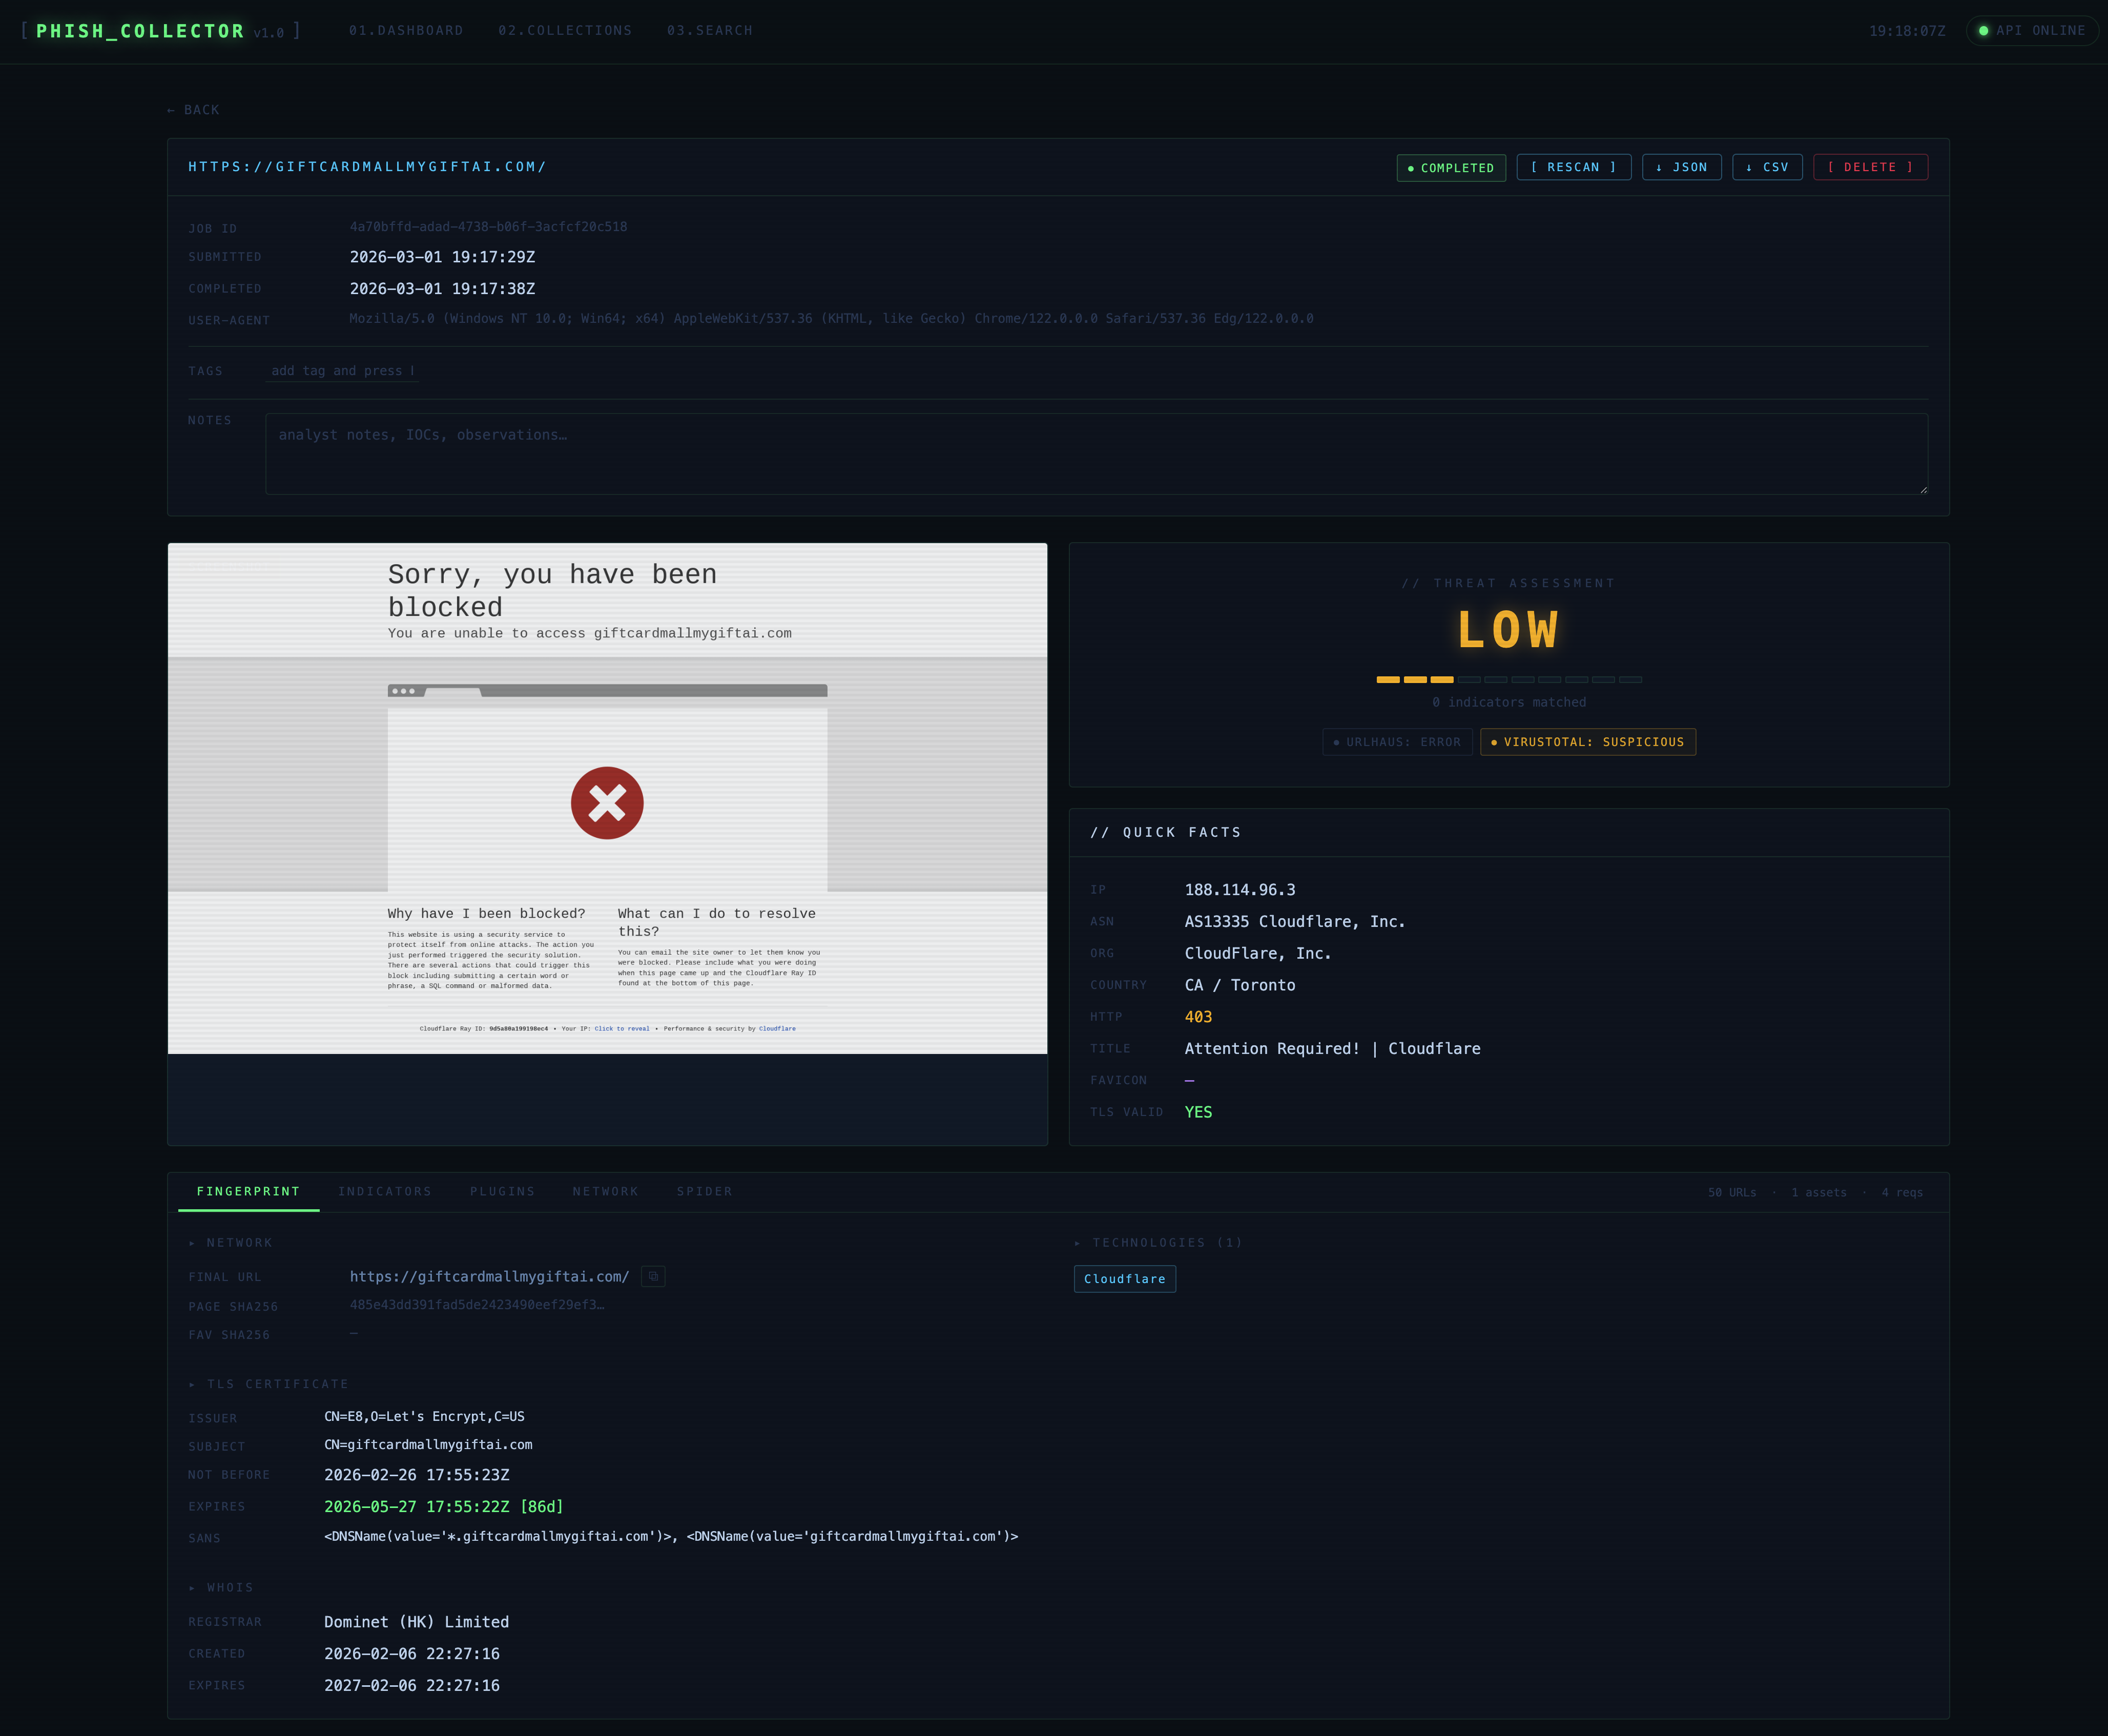 olizimmermann/phishcollector
PhishCollector is a research framework for collecting, analysing, and tracking phishing sites.
 hydradragonantivirus/hydradragonav-mobile
Android Antivirus which doesn't require root, adb, ca install and cloud with many features and ways to detect more zero-day malware
 ilianazz/young-domain-guard
Browser extension that warns users about recently registered domains to prevent phishing attacks. Queries RDAP to check domain age and displays…
 szzxli/soc-home-lab
Hands-on SOC lab: AWS mini-SOC with CloudTrail/GuardDuty, a Python CloudTrail IOC analyzer, phishing header forensics, ELF binary triage, and agent…
 narimangharib/irgc-whatsapp-phishkit
Analysis of state-sponsored WhatsApp phishing infrastructure with real-time QR hijacking and device surveillance
 scottalt/ai-email-threat-research
A cybersecurity research game measuring how humans detect AI-generated phishing emails. Built as a retro terminal experience.
 dshabani96/cve-2024-21413
Proof-of-concept exploit for Microsoft Outlook RCE (CVE-2024-21413) with SMTP email delivery, malicious RTF attachment generation, and optional…
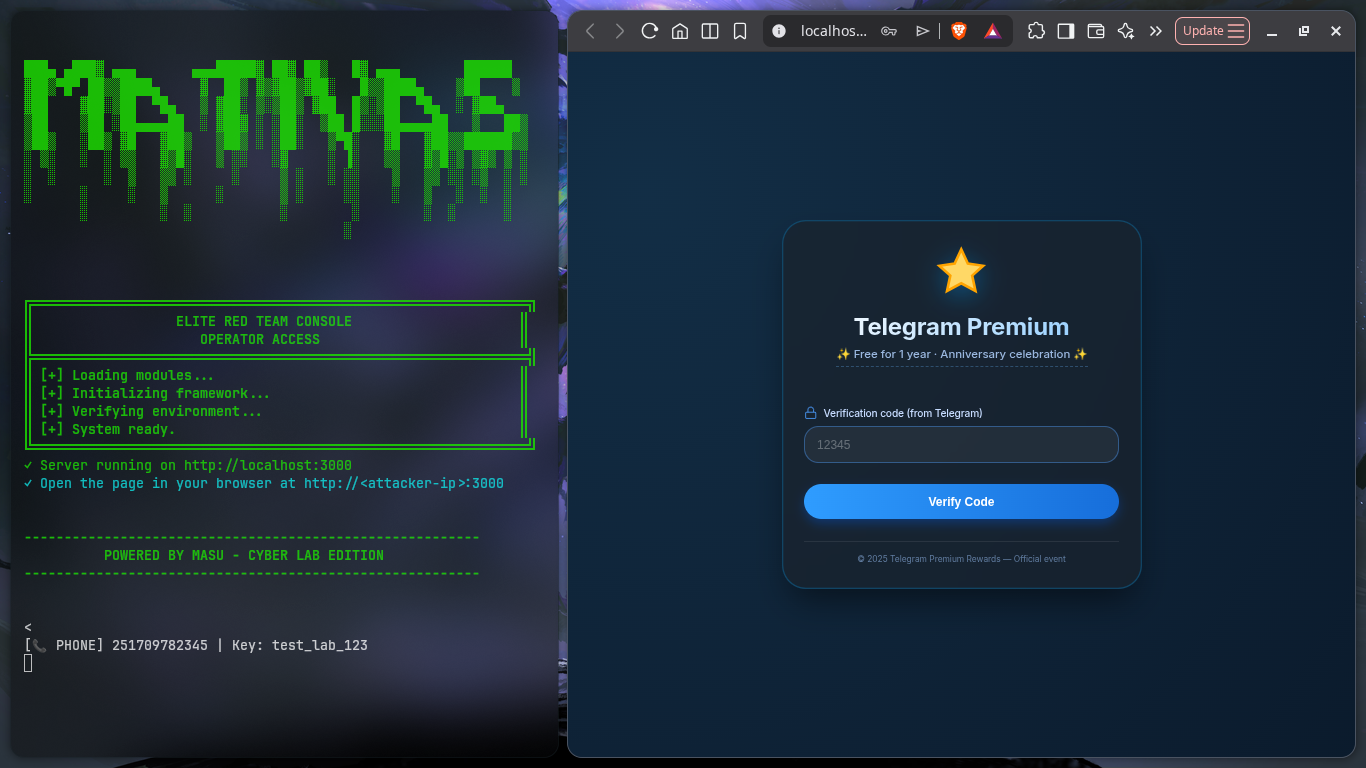 maty156/telegram-phish-simulator
Educational Telegram phishing simulation for cybersecurity training and awareness. Demonstrates credential harvesting via fake login pages in…
 romain-deperne/cve-2026-33715
Proof-of-concept exploit for unauthenticated SSRF and open email relay in Chamilo LMS via install.ajax.php, allowing internal network probing and…
 toxy4ny/bl00dym4ry
Educational trojan simulator for cybersecurity training, simulating phishing attacks with social engineering, system reconnaissance, anti-sandbox…
 brodsbytes/cyberpup
A free, open-source cybersecurity app for non techy people.
 fdzdev/cve-2024-50964
Documentation of CVE-2024-50964: critical DMARC policy bypass in DonWeb MX server allowing email spoofing, with low attack complexity and no required…
 gregory-chatelier/huntglyph
Detect visually similar characters (homoglyphs) and hidden data in text to protect against deceptive attacks
 dionissh/cve-2024-21413
Proof-of-concept exploit for Microsoft Outlook RCE (CVE-2024-21413) with SMTP-based phishing email delivery, malicious RTF attachment generation, and…
 themursalin/htb-mailing-a-complete-walkthrough
If you've been grinding through HackTheBox machines, Mailing is one of those boxes that genuinely teaches you something. It's rated Easy, runs on…
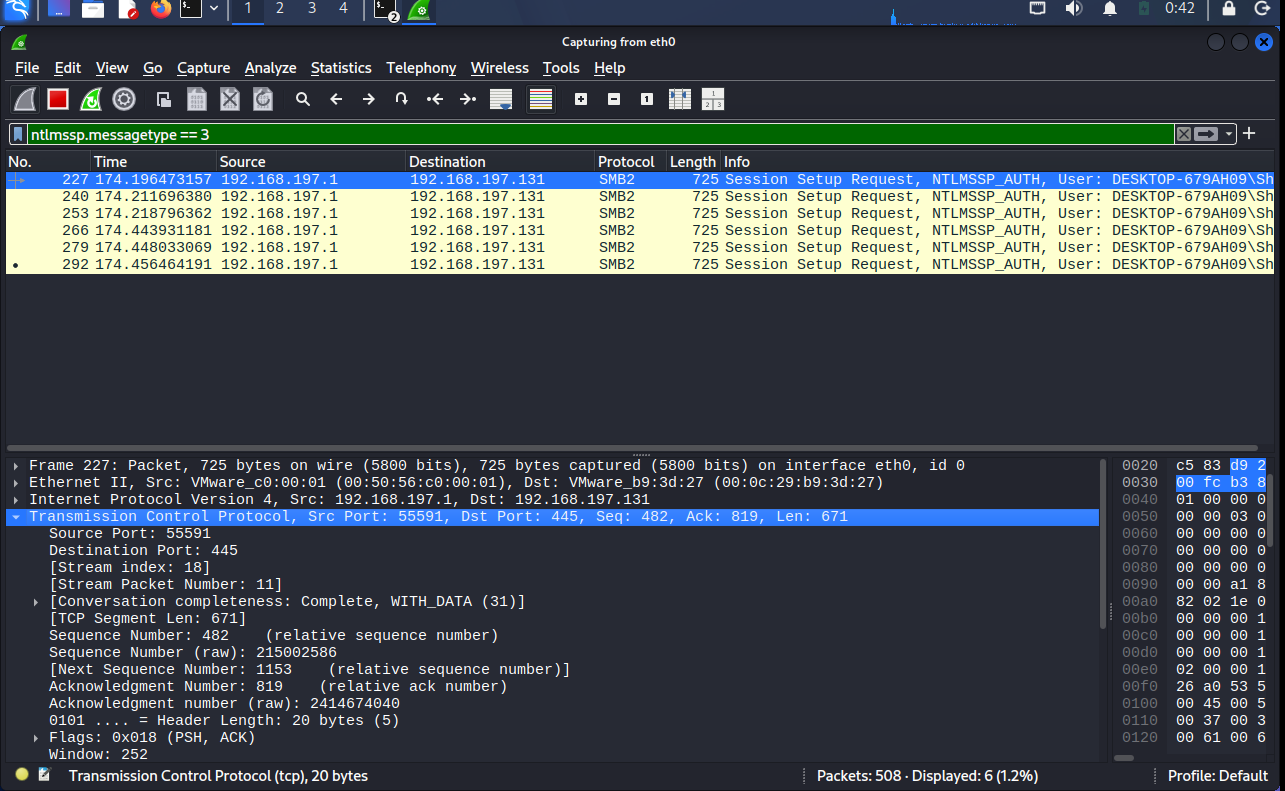 rahultb-sec/cve-2026-33829-writeup
Vulnerability Case Study: CVE-2026-33829 (Windows Snipping Tool NTLM Coercion)
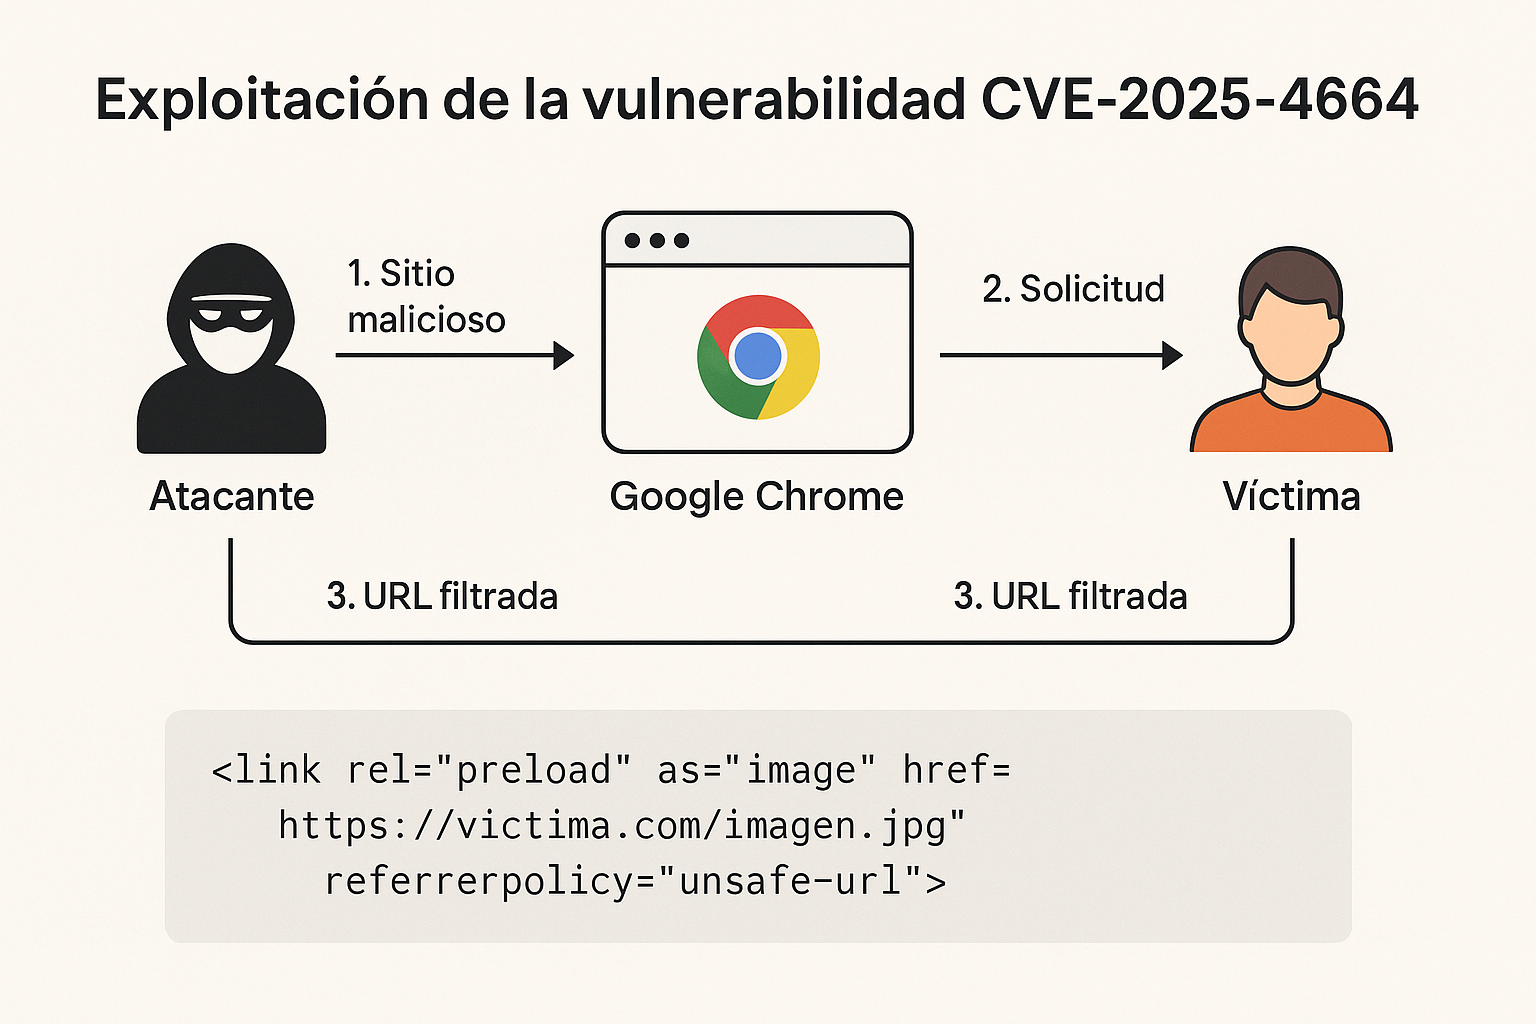 speinador/cve-2025-4664
Educational demo of CVE-2025-4664, a Chrome Loader vulnerability enabling cross-origin data leakage via referrer-policy manipulation. Includes a…