
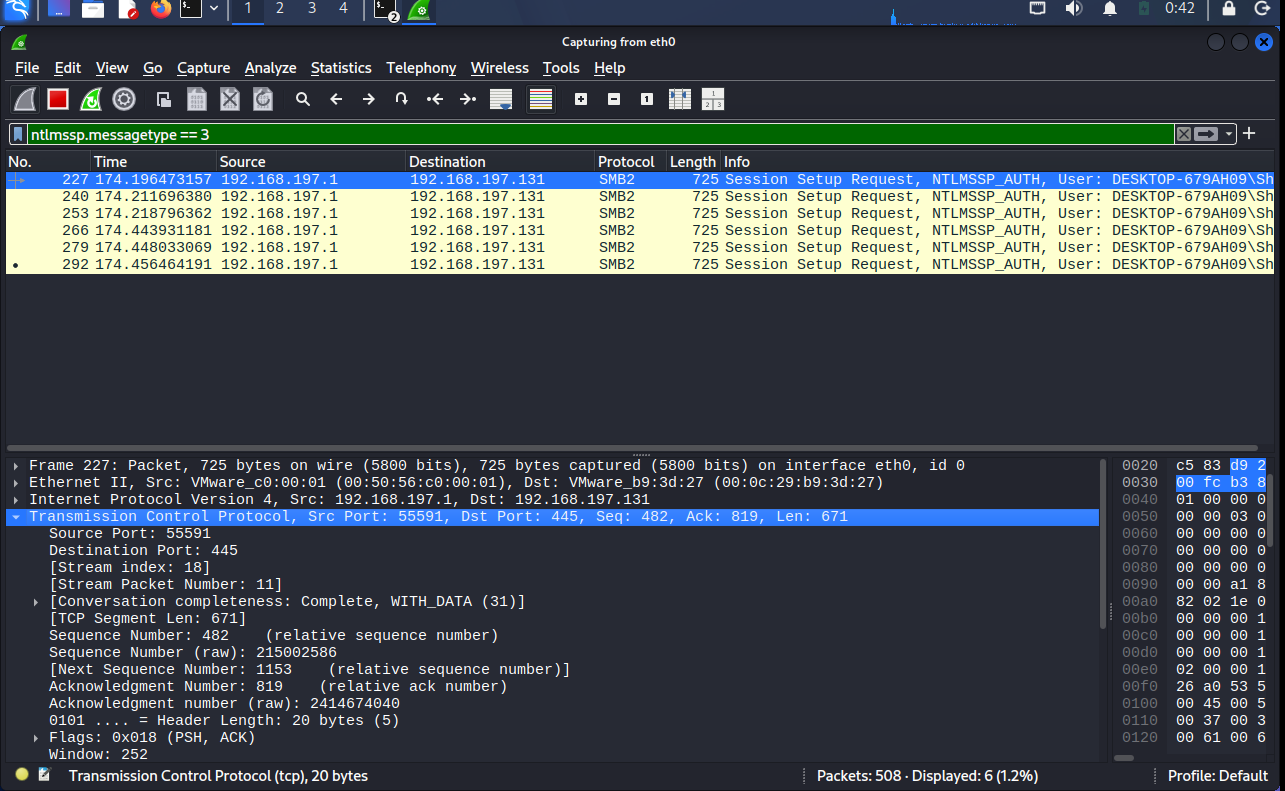
CVE-2026-33829-Writeup
 rahultb-sec/cve-2026-33829-writeup
Vulnerability Case Study: CVE-2026-33829 (Windows Snipping Tool NTLM Coercion)
educationexploitationinformation-gathering+3
rahultb-sec/cve-2026-33829-writeupVulnerability Case Study: CVE-2026-33829 (Windows Snipping Tool NTLM Coercion)
 utkusen/jeopardize
a low(zero) cost threat intelligence&response tool against phishing domains
 jaykali/lockphish
Lockphish it's the first tool (07/04/2020) for phishing attacks on the lock screen, designed to grab Windows credentials, Android PIN and iPhone…
 hlldz/pickl3
Windows active user credential phishing tool
 spiderlabs/firework
Firework is a proof of concept tool to interact with Microsoft Workplaces creating valid files required for the provisioning process.
 wavestone-cdt/abaddon
Red team operations management platform automating infrastructure deployment, C2 setup, phishing campaigns, and reconnaissance with integrated tool…
 alteredsecurity/365-stealer
Automates Illicit Consent Grant attacks against Azure/O365 tenants to steal refresh tokens, exfiltrate emails/OneDrive data, and create malicious…
 d4rks3c-group/hiddeneyereborn
HiddenEye Reborn in better shape than ever, rewritten from scratch and adapted to modern world
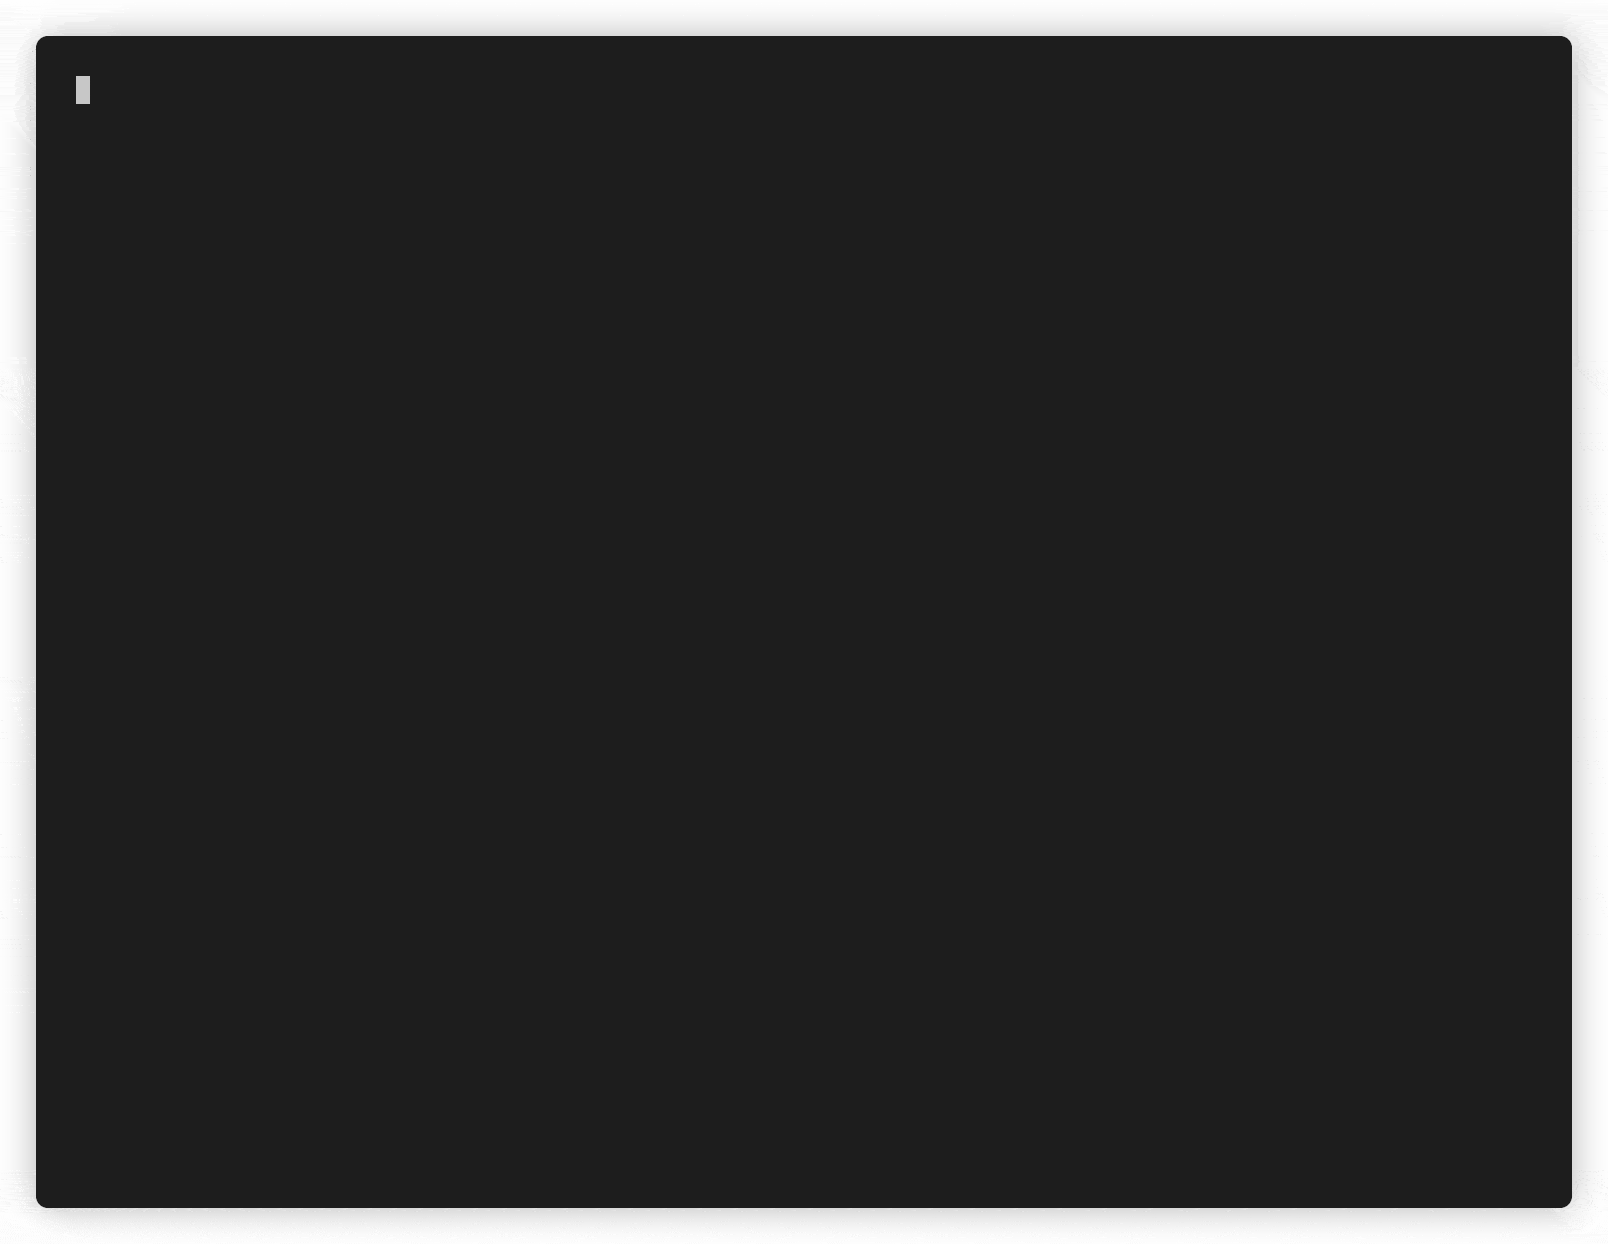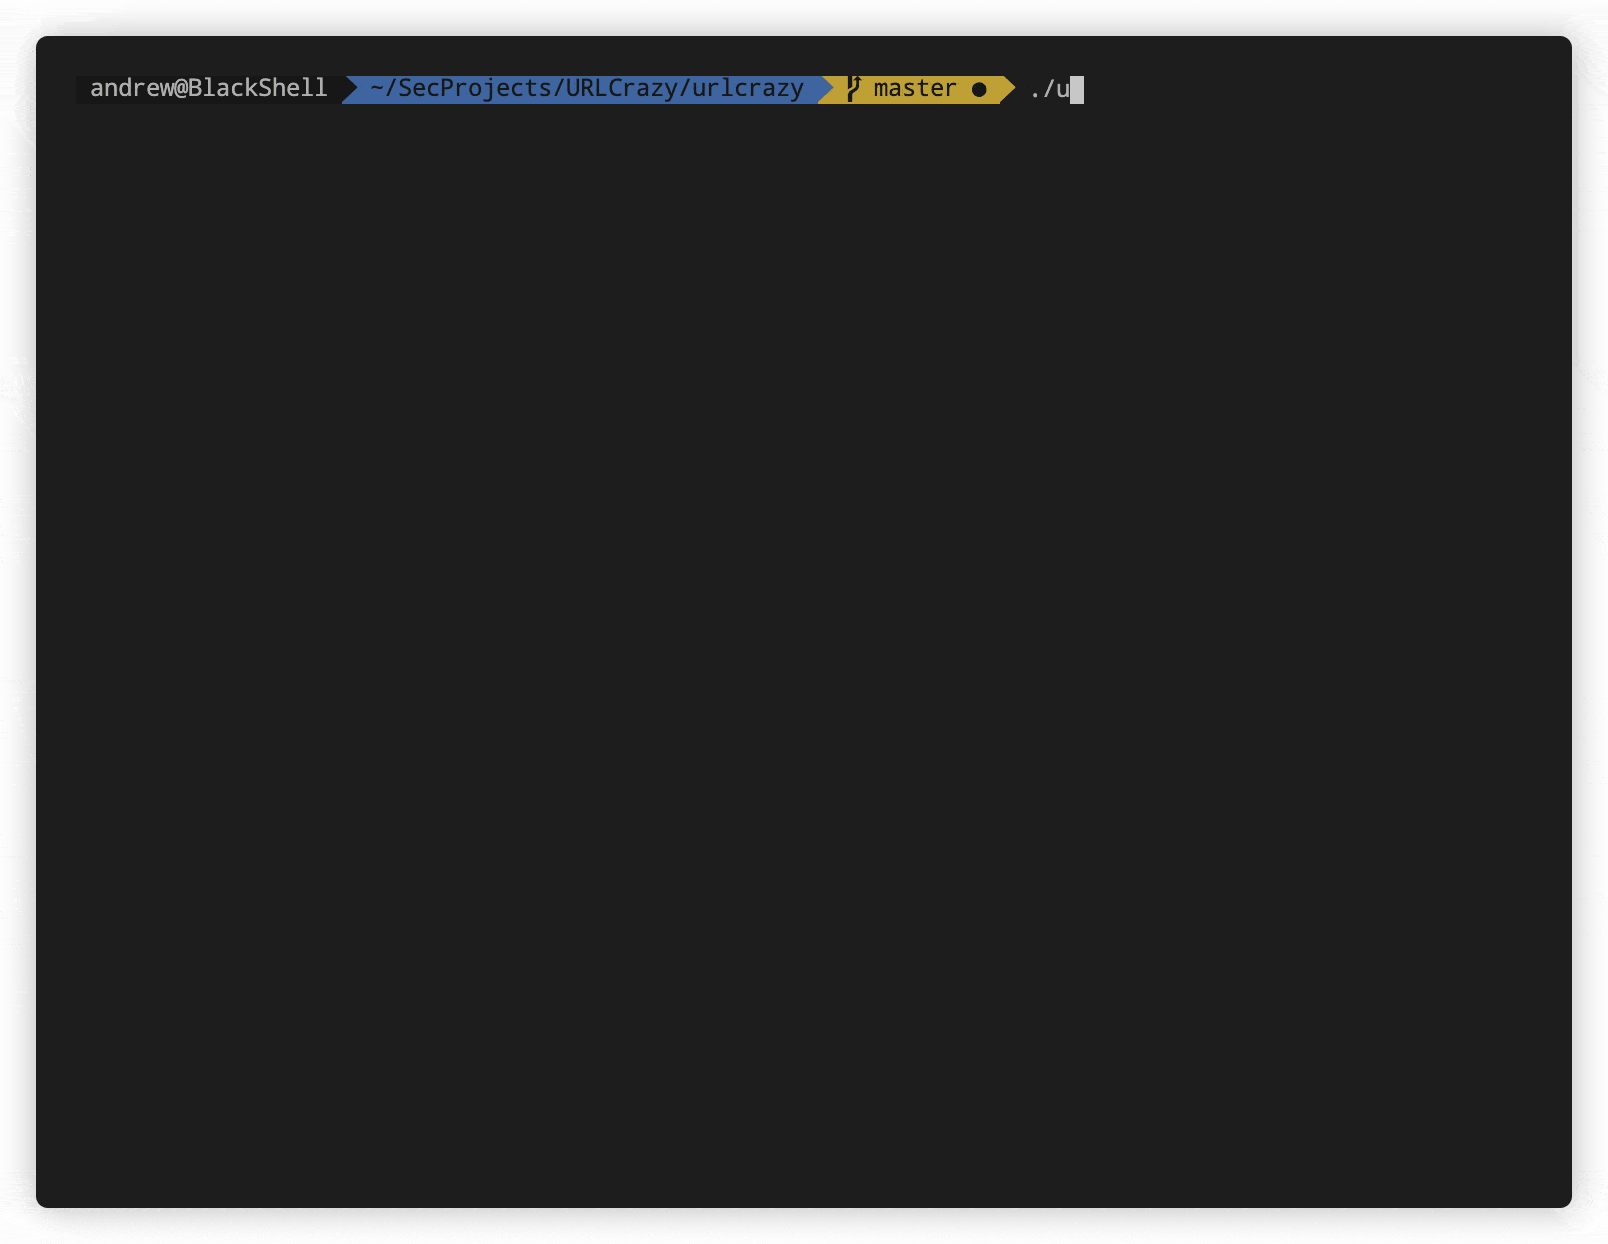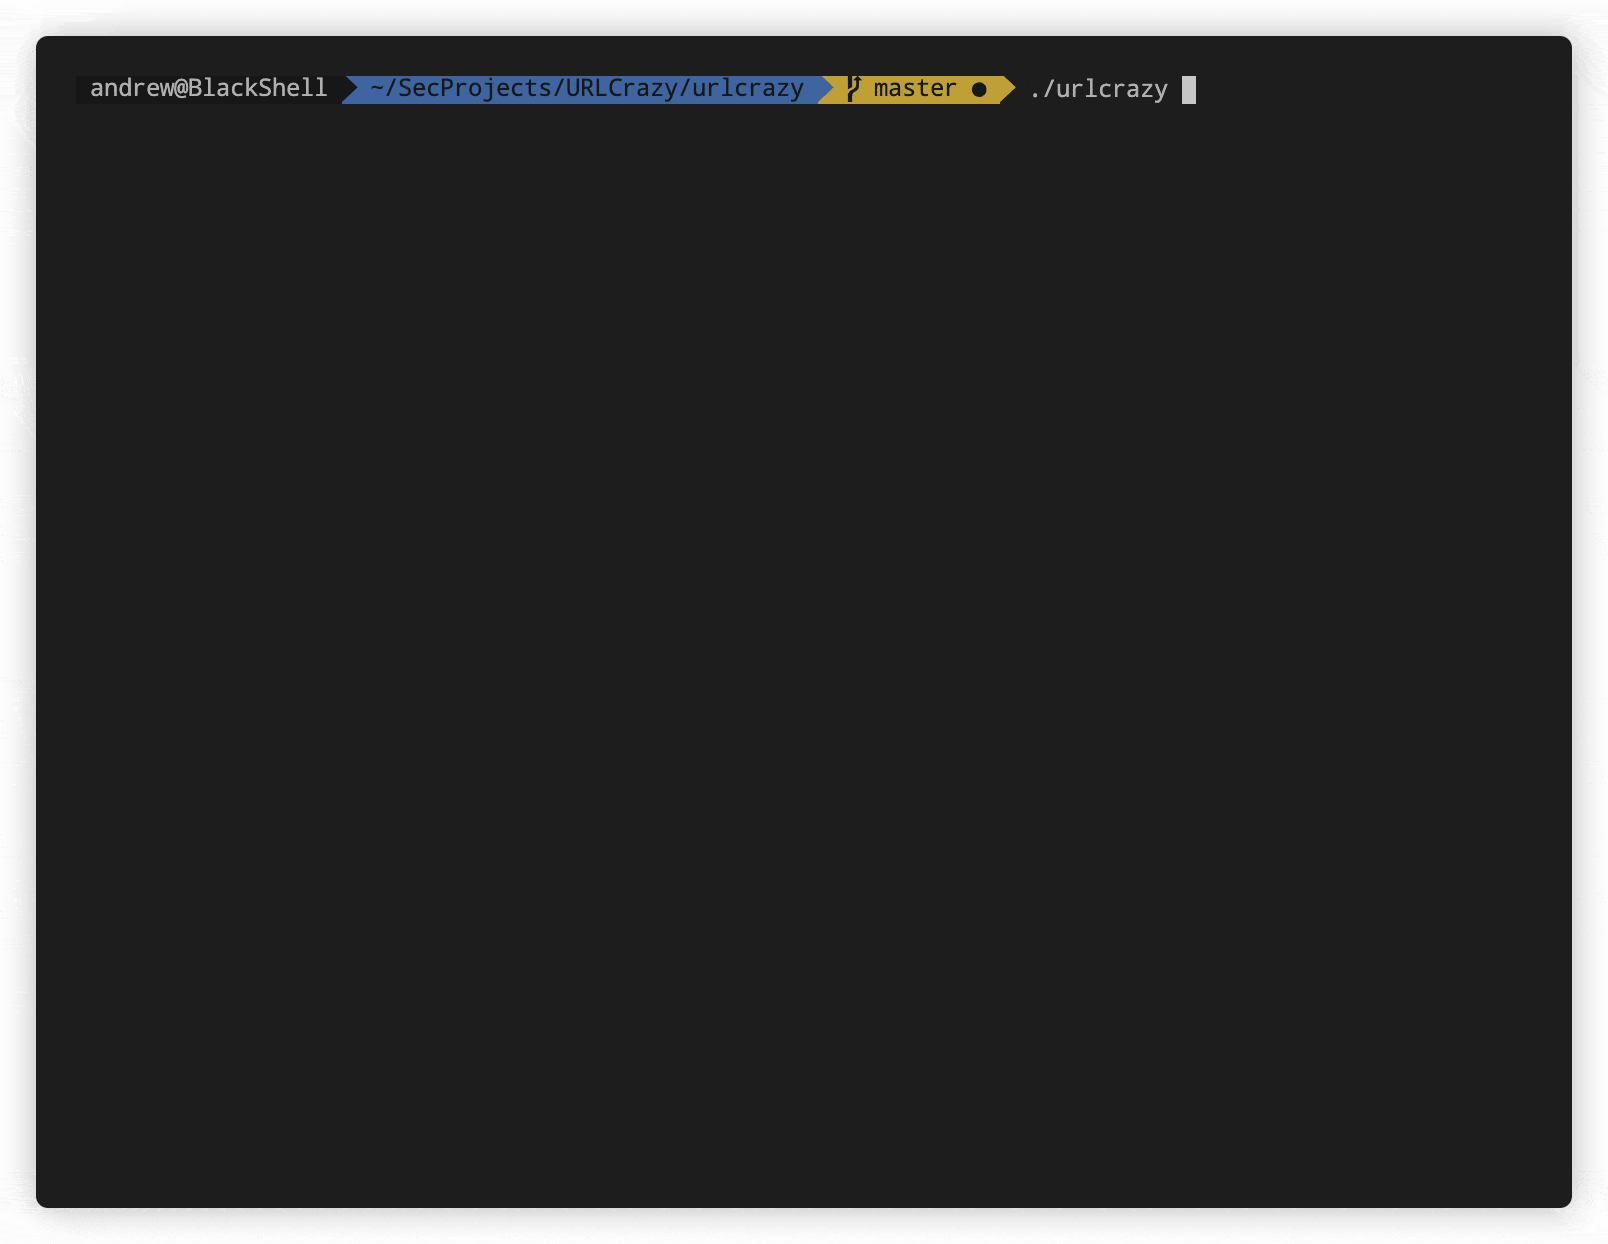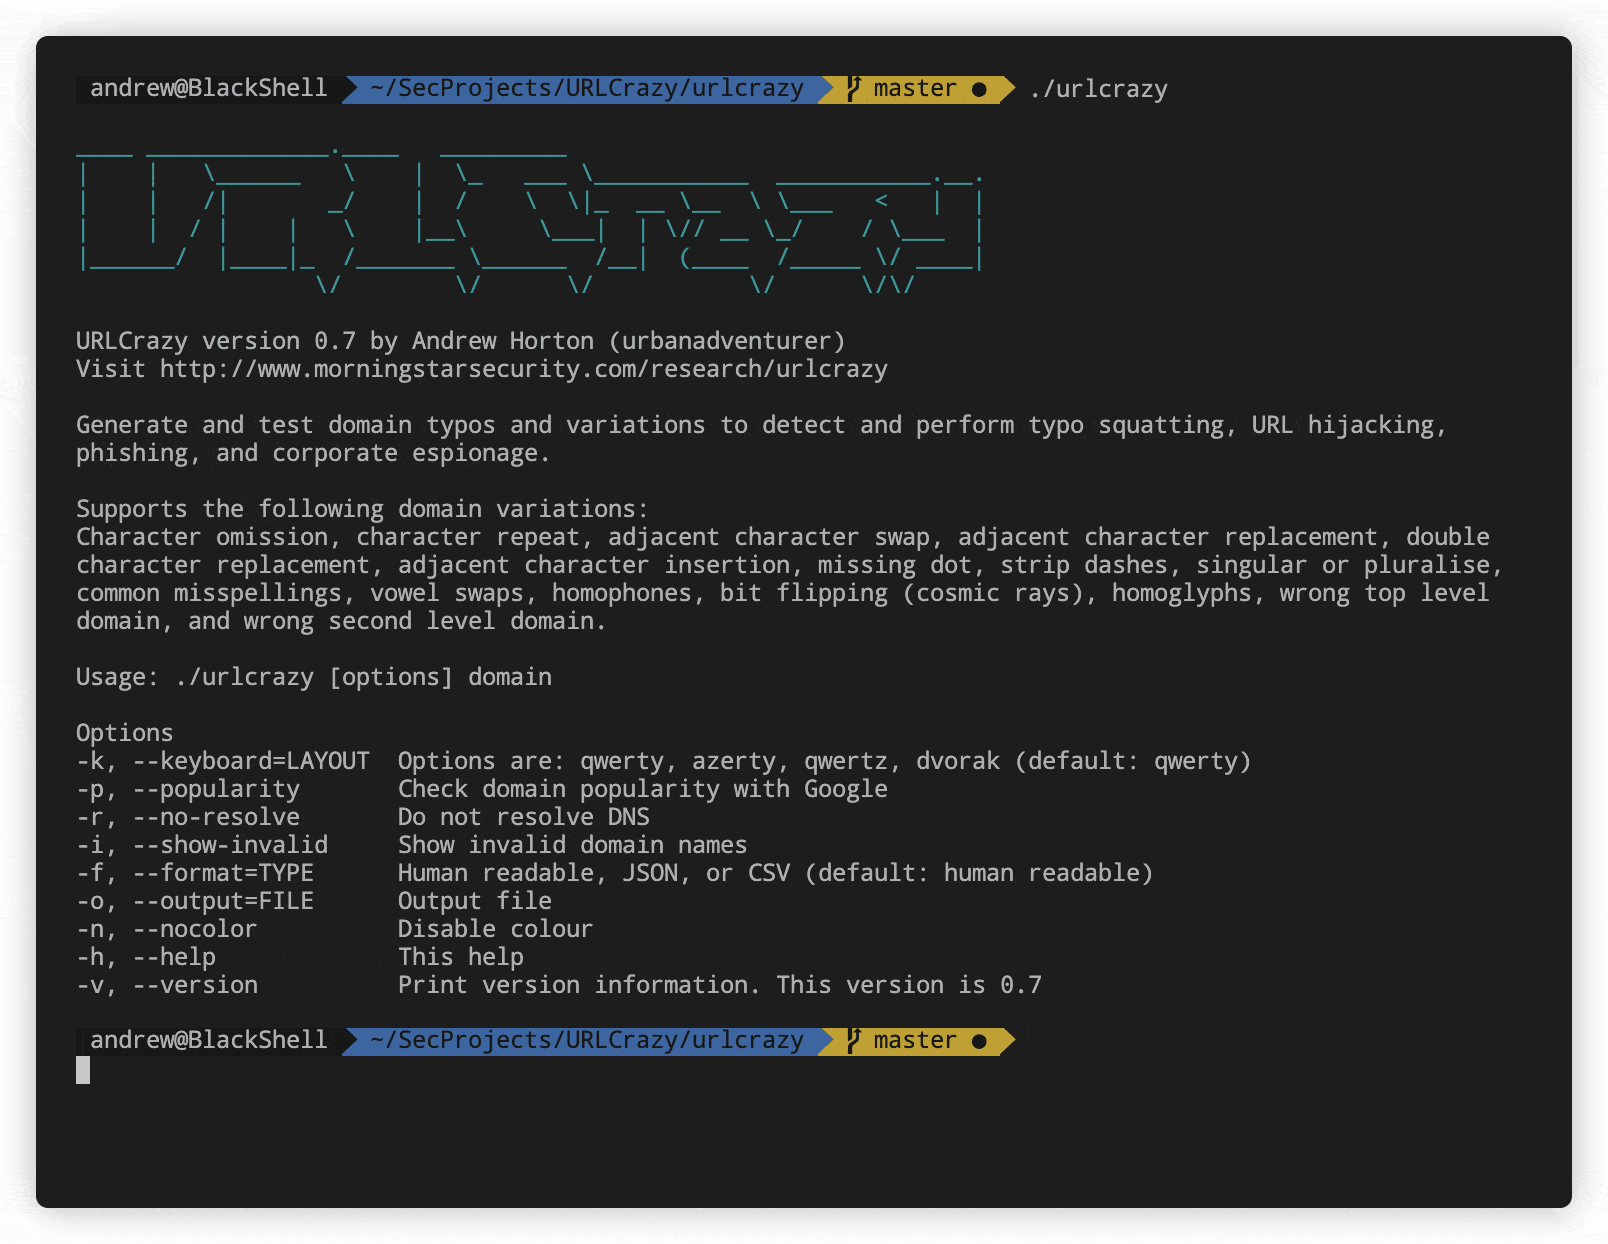 urbanadventurer/urlcrazy
Generate and test domain typos and variations to detect and perform typo squatting, URL hijacking, phishing, and corporate espionage.
 thomastjdev/wmd
Python framework for IT security tools
 rxwx/chlonium
Clone and import Chromium cookies and passwords across browsers with offline DPAPI state key decryption, supporting AES-256 GCM encrypted databases…
 initstring/evil-ssdp
Spoof SSDP replies and create fake UPnP devices to phish for credentials and NetNTLM challenge/response.

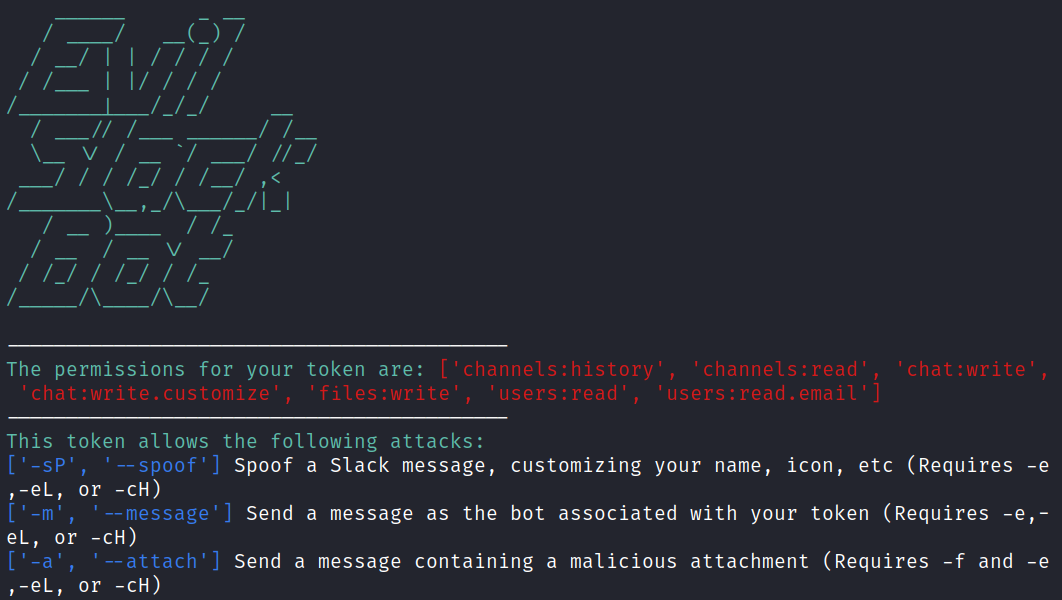 drew-sec/evilslackbot
A Slack bot phishing framework for Red Teaming exercises
 telefonicatc2tech/typodetect
Detects active domain mutations to prevent phishing and smishing. Uses IANA TLDs, blockchain DNS validation, and DoH malware reports. Outputs JSON or…
 jh00nbr/phishruffus
Intelligent threat hunter and phishing servers