
365-Stealer
 alteredsecurity/365-stealer
Automates Illicit Consent Grant attacks against Azure/O365 tenants to steal refresh tokens, exfiltrate emails/OneDrive data, and create malicious…
cloud-securitypenetration-testingphishing+1
588
alteredsecurity/365-stealerAutomates Illicit Consent Grant attacks against Azure/O365 tenants to steal refresh tokens, exfiltrate emails/OneDrive data, and create malicious…
 spyboy-productions/facad1ng
Open-source URL masking & analysis tool for security research, phishing awareness, and defensive testing. Demonstrates adversary techniques used to…
 ransomleak/training-security-awareness
Open-source interactive security awareness training library with 130+ SCORM exercises covering phishing, vishing, BEC, MFA fatigue, and OWASP AI/LLM…
 thomastjdev/wmd
Python framework for IT security tools
 micro-joan/zphisher-gui-back_office
Real-time phishing campaign back-office plugin for Zphisher, capturing credentials, checking account exposure via haveibeenpwned, and evaluating…
 pericena/ciclopeclic
Security awareness training tool for authorized phishing simulations and internal IT audits
 kimstars/ashwesker-cve-2026-21509
Proof-of-concept exploit for Microsoft Office security feature bypass (CVE-2026-21509). Generates malicious DOCX files with embedded OLE objects to…
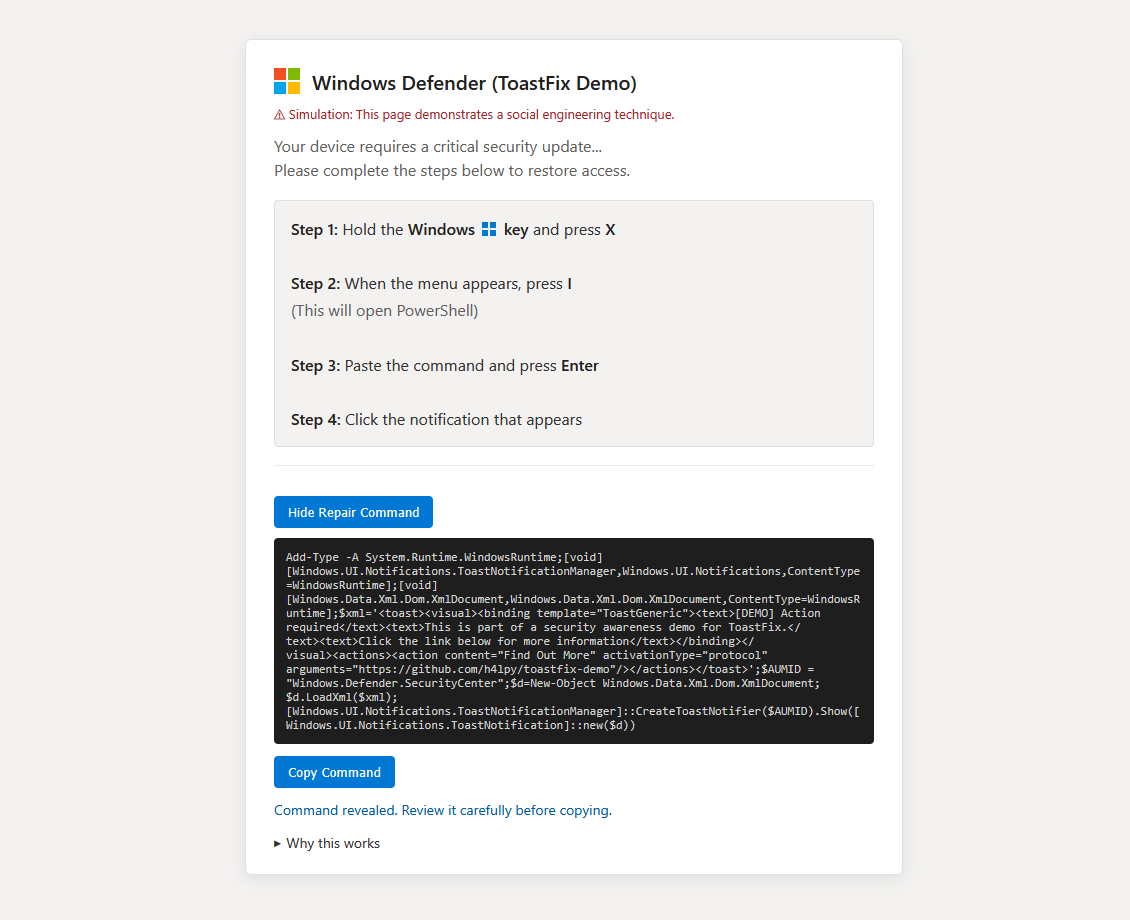 h4lpy/toastfix-demo
Proof-of-concept security demo illustrating how PowerShell can create trusted-looking Windows toast notifications chained together with…
 qyvora/qyvora-toha3ee
Go-based network exploitation and MITM framework for authorized penetration testing, network reconnaissance, traffic interception, wireless security…
 nehkark/cve-2025-40778
Proof-of-concept demonstrating DNS cache poisoning via additional record injection in BIND 9, with tools to validate and exploit CVE-2025-40778 for…
 razielx64/cve-2025-69606-gsvoip-xss
Proof-of-concept for a reflected XSS vulnerability (CVE-2025-69606) in GSVoIP Web Panel v2.0.90, demonstrating unauthenticated arbitrary JavaScript…
 alessandrobertoldi/research
Published security research repository featuring academic papers on domain hijacking, 2FA bypass, and large-scale spoofing techniques, authored by…
 cmadhushanka/wordpress-rce-vapt-cve-2020-25213
Educational cybersecurity project demonstrating exploitation and mitigation of CVE-2020-25213 (WordPress File Manager Plugin RCE). Includes malware…
 k9-modz/cve-2023-38873-g1
Proof-of-concept demonstrating a Clickjacking vulnerability on the G1 website, with a malicious iframe overlay and social engineering popup for…
 shellkraft/cve-2025-3568
A security vulnerability has been identified in Krayin CRM <=2.1.0 that allows a low-privileged user to escalate privileges by tricking an admin into…
 e1tex/cve-2023-48104
Proof-of-concept exploit demonstrating HTML injection in SOGo Web Client before 5.9.1, enabling phishing attacks via malicious forms in email bodies.
 fluxionnetwork/fluxion
Automated WPA/WPA2 phishing tool that captures handshakes, spawns a rogue access point, and lures users to a captive portal to harvest credentials…
 thalesgroup-cert/watcher
AI-powered threat intelligence platform for automated CVE/ransomware monitoring, domain surveillance, data leak detection, and incident response with…