
CVE-2025-3568
 shellkraft/cve-2025-3568
A security vulnerability has been identified in Krayin CRM <=2.1.0 that allows a low-privileged user to escalate privileges by tricking an admin into…
exploitationphishingprivilege-escalation+3
shellkraft/cve-2025-3568A security vulnerability has been identified in Krayin CRM <=2.1.0 that allows a low-privileged user to escalate privileges by tricking an admin into…
 ajansha/cve-2025-55903
Proof of concept for CVE-2025-55903, a stored HTML injection in PerfexCRM allowing authenticated users to inject malicious HTML into invoices and…
 ajansha/cve-2025-60378
Proof of concept for stored HTML injection in RISE CRM, demonstrating how authenticated users can inject malicious HTML into invoices and messages,…
 naimkowshik/lbfh
About All in one tool for Information Gathering, Vulnerability Scanning and Crawling. A must have tool for all penetration testers
 sybelle03/cve-2021-43617
This is a reproduction of PHP Laravel 8.70.1 - Cross Site Scripting (XSS) to Cross Site Request Forgery (CSRF) vulnerability
 mbadanoiu/cve-2021-46366
CVE-2021-46366: Credential Bruteforce Attack via CSRF + Open Redirect in Magnolia CMS
 sanupl/cve-2024-34568
In LetterPress plugin <= 1.2.1 is vulnerable to Cookie Stealing Vulnerability. An attacker can able to steal the cookies by injecting the JavaScript…
 elenichristopoulou/poc-cve-2026-20841
Proof-of-concept exploit for CVE-2026-20841, a Windows Notepad remote code execution vulnerability, using a crafted .md file and social engineering…
 filipegaudard/cve-2026-33149-poc
Proof-of-concept exploit for CVE-2026-33149, a Host header injection in Tandoor Recipes that enables invite link poisoning and cache poisoning.…
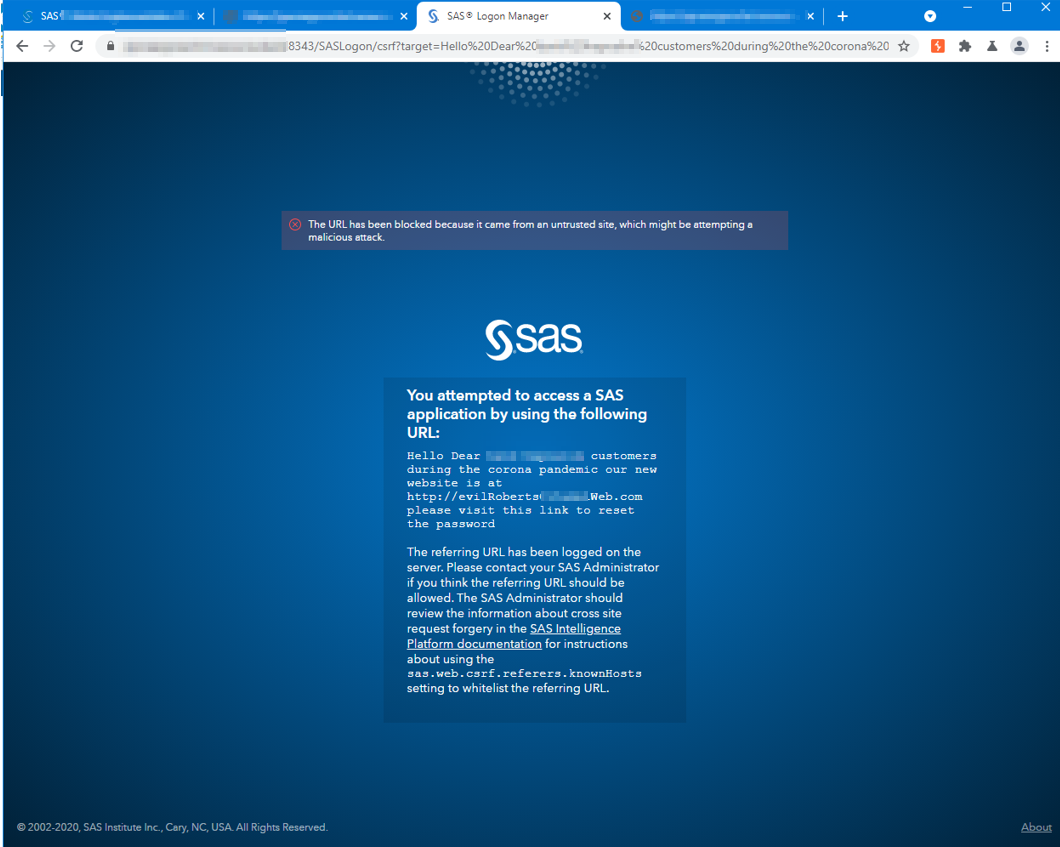 polling-repo-continua/cve-2022-25257
Proof-of-concept exploit for CVE-2022-25257: CSRF parameter injection in SAS Logon 9.4 enabling warning-message spoofing for phishing attacks.
 g37sys73m/cve-2022-46087
CloudSchool v3.0.1 is vulnerable to Cross Site Scripting (XSS). A normal user can steal session cookies of the admin users through notification…
 e1tex/cve-2023-48104
Proof-of-concept exploit demonstrating HTML injection in SOGo Web Client before 5.9.1, enabling phishing attacks via malicious forms in email bodies.
 dhmosfunk/7-zip-cve-2025-0411-poc
This repository contains POC scenarios as part of CVE-2025-0411 MotW bypass.
 tarantula-team/cve-2019-12949
CVE-2019-12949
 bokanrb/cve-2021-27404
HostHeaderInjection-Askey
 dead1nfluence/leantime-poc
CVE-2024-27474, CVE-2024-27476, CVE-2024-27477
 alkimcoskun/yordam-kutuphane-otomasyonunda-coklu-html-enjeksiyonu
CVE-2026-77818 - Yordam Kütüphane Otomasyon Sistemi - Üç ayrı noktada yansıtılmış HTML enjeksiyonu, form action ele geçirme ve kimlik bilgisi…
 v35hr4j/cve-2021-24563
The plugin does not prevent HTML files from being uploaded via its form, allowing unauthenticated user to upload a malicious HTML file containing…