
CVE-2026-33715
 romain-deperne/cve-2026-33715
Unauthenticated SSRF and open email relay in Chamilo LMS — CVE-2026-33715 / CVSS 7.2
exploitationphishingreconnaissance+2
romain-deperne/cve-2026-33715Unauthenticated SSRF and open email relay in Chamilo LMS — CVE-2026-33715 / CVSS 7.2
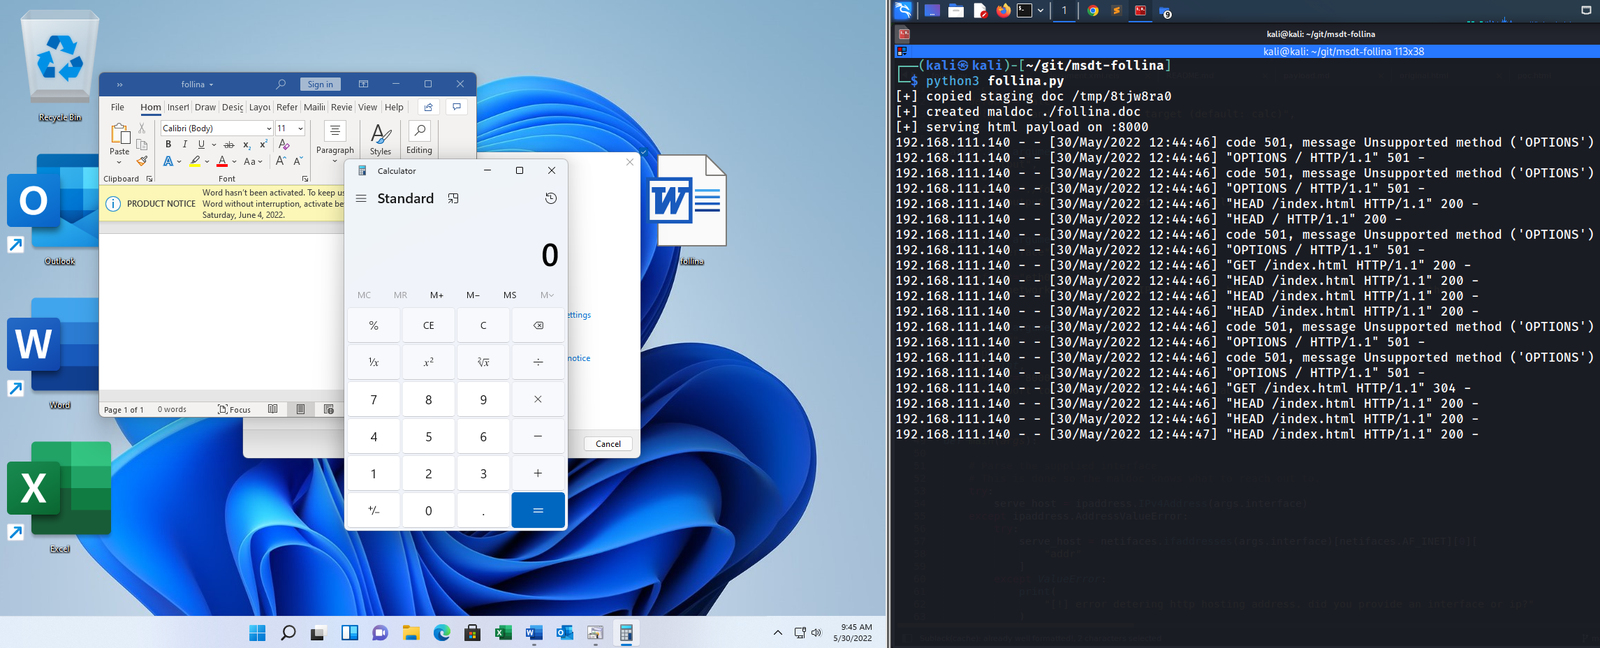 johnhammond/msdt-follina
Generates a malicious Microsoft Word document exploiting the MS-MSDT 'Follina' vulnerability to execute arbitrary commands or stage payloads via an…
 kgretzky/evilginx
PLEASE USE NEW VERSION: https://github.com/kgretzky/evilginx2
 kgretzky/evilqr
Proof-of-concept to demonstrate dynamic QR swap phishing attacks in practice.
 qyvora/qyvora-toha3ee
Go-based network exploitation and MITM framework for authorized penetration testing, network reconnaissance, traffic interception, wireless security…
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 jiep/offensive-ai-compilation
A curated list of useful resources that cover Offensive AI.
 secdev02/easytokens
Kali365 - EvilTokens Replica
 soufianetahiri/teamsntlmleak
Leak NTLM via Website tab in teams via MS Office
 viniciusfariasdev/cve-2024-21413-outlook-monikerlink-lab
Educational lab and PoC demonstrating CVE-2024-21413 Outlook Moniker Link attack to leak netNTLMv2 hashes via crafted HTML email.
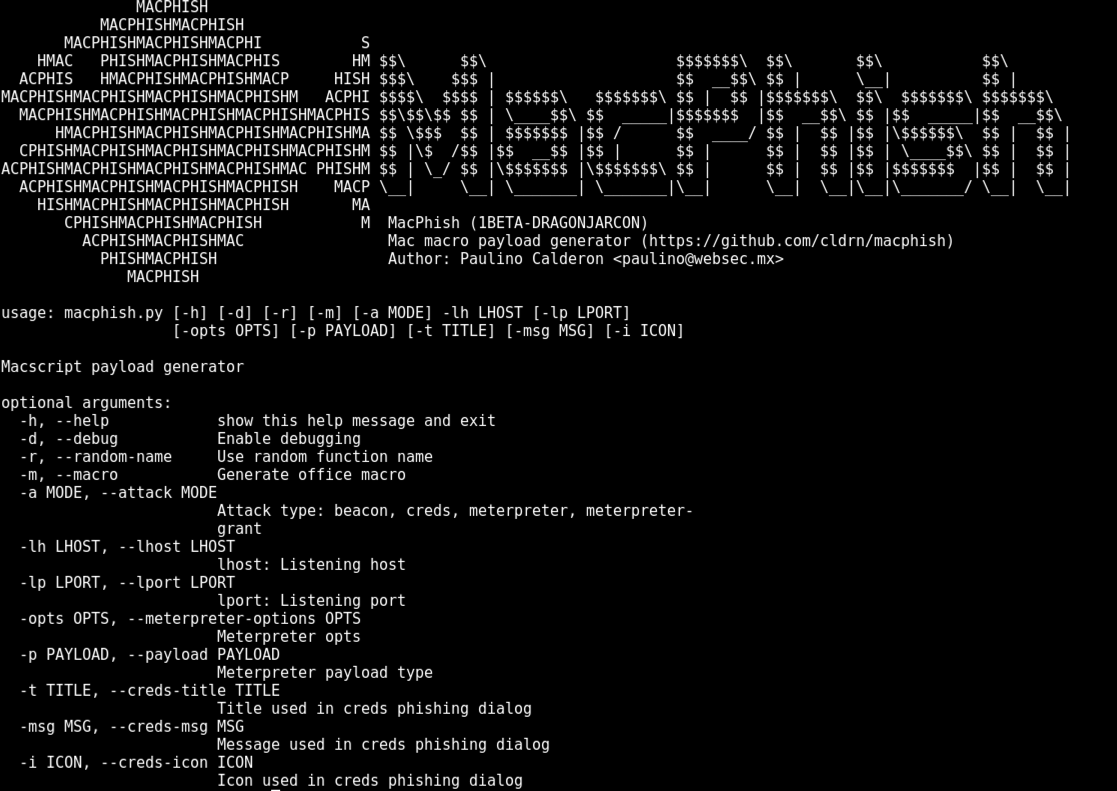 cldrn/macphish
Generates malicious Office for Mac macros with beacon, credential harvesting, and meterpreter payloads for phishing and exploitation testing on macOS.
 strangerealintel/cyberthreatintel
Analysis of malware and Cyber Threat Intel of APT and cybercriminals groups
 0xsu3ks/cve-2024-34328
Proof-of-concept for open redirection via Host header manipulation in Sielox AnyWare 2.1.2 (CVE-2024-34328), with exploit steps, impact, and…
 mbadanoiu/cve-2021-46366
CVE-2021-46366: Credential Bruteforce Attack via CSRF + Open Redirect in Magnolia CMS
 wifiphisher/wifiphisher
Rogue Access Point framework for red team engagements and Wi-Fi security testing. Performs Evil Twin, KARMA, and Known Beacons attacks to achieve…
 kgretzky/evilginx2
Standalone man-in-the-middle attack framework used for phishing login credentials along with session cookies, allowing for the bypass of 2-factor…
 mdsecactivebreach/o365-attack-toolkit
A toolkit to attack Office365