
CVE-2021-43617
 sybelle03/cve-2021-43617
This is a reproduction of PHP Laravel 8.70.1 - Cross Site Scripting (XSS) to Cross Site Request Forgery (CSRF) vulnerability
exploitationpenetration-testingphishing+3
1
sybelle03/cve-2021-43617This is a reproduction of PHP Laravel 8.70.1 - Cross Site Scripting (XSS) to Cross Site Request Forgery (CSRF) vulnerability
 sanupl/cve-2024-34568
In LetterPress plugin <= 1.2.1 is vulnerable to Cookie Stealing Vulnerability. An attacker can able to steal the cookies by injecting the JavaScript…
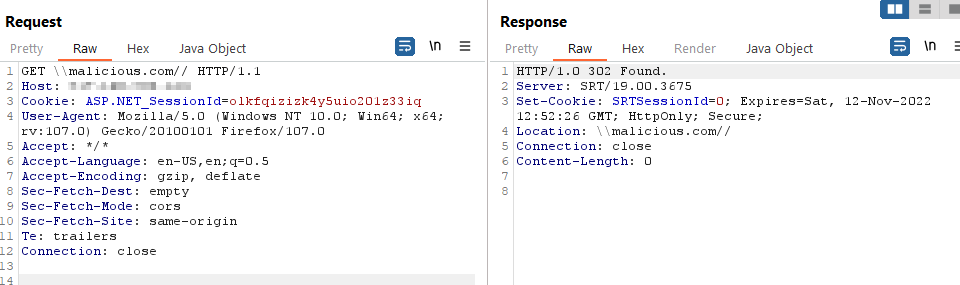 jbalanza/cve-2022-44215
Public disclosure of TitanFTP 19.X Open Redirection vulnerability
 gregory-chatelier/huntglyph
Detect visually similar characters (homoglyphs) and hidden data in text to protect against deceptive attacks
 arkha-corvus/letsdefend-soc173-follina-0-day-detected
We are presented with a security alert indicating the detection of the Follina (CVE-2022-30190) vulnerability. A malicious Word document triggered…
 millad7/sogo_web_mail-vulnerability-cve-2025-50340
Insecure Direct Object Reference (IDOR vulnerability) in SOGo Webmail Allows a user to send emails on behalf of another user.
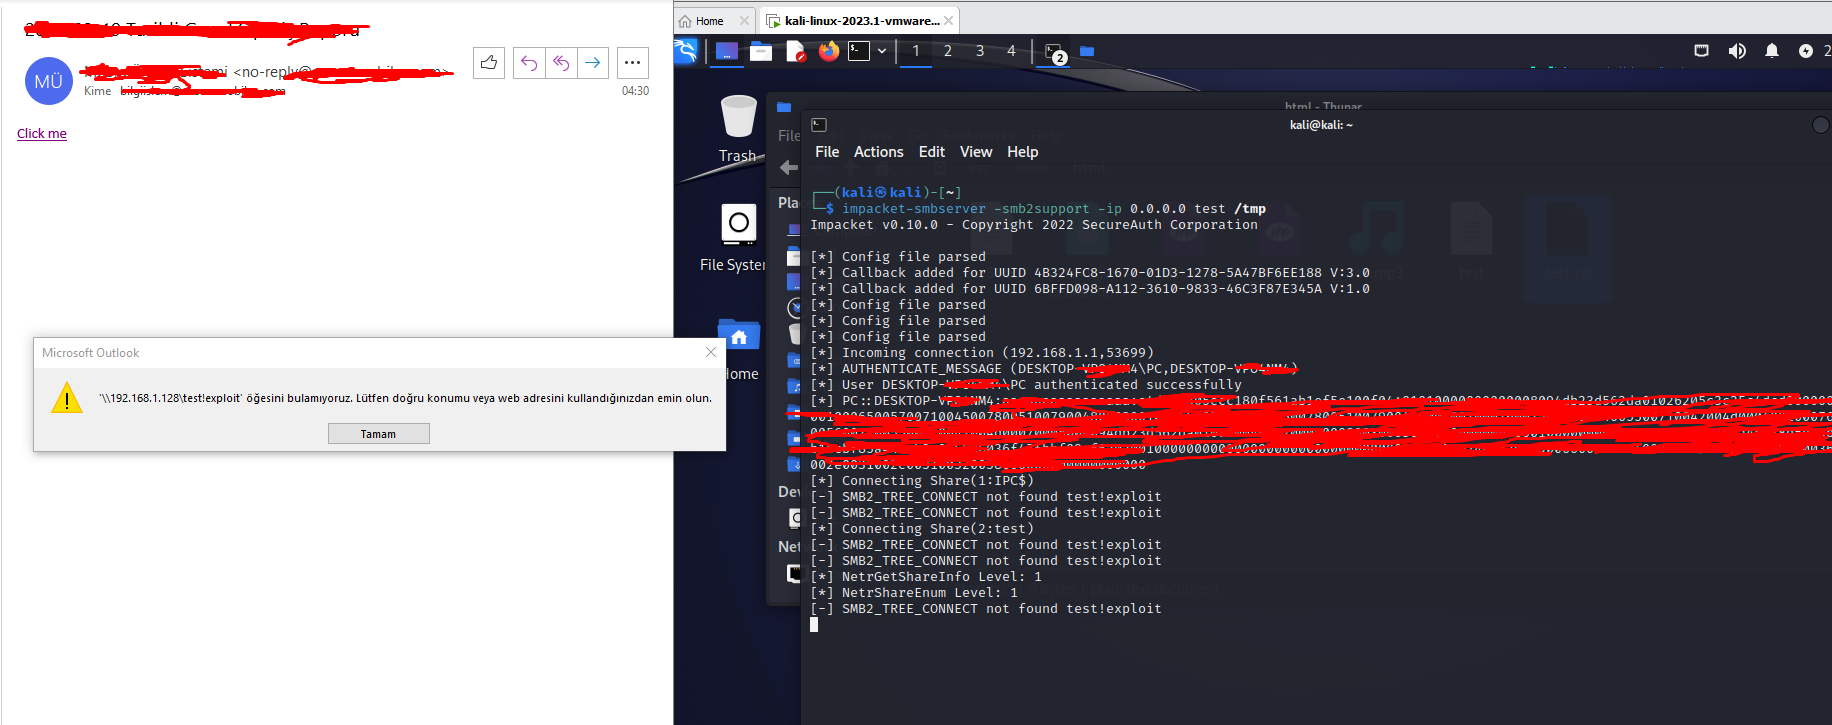 mseymend/cve-2024-21413
CVE-2024-21413 Açığını Kullanarak Giriş Bilgilerini Alma
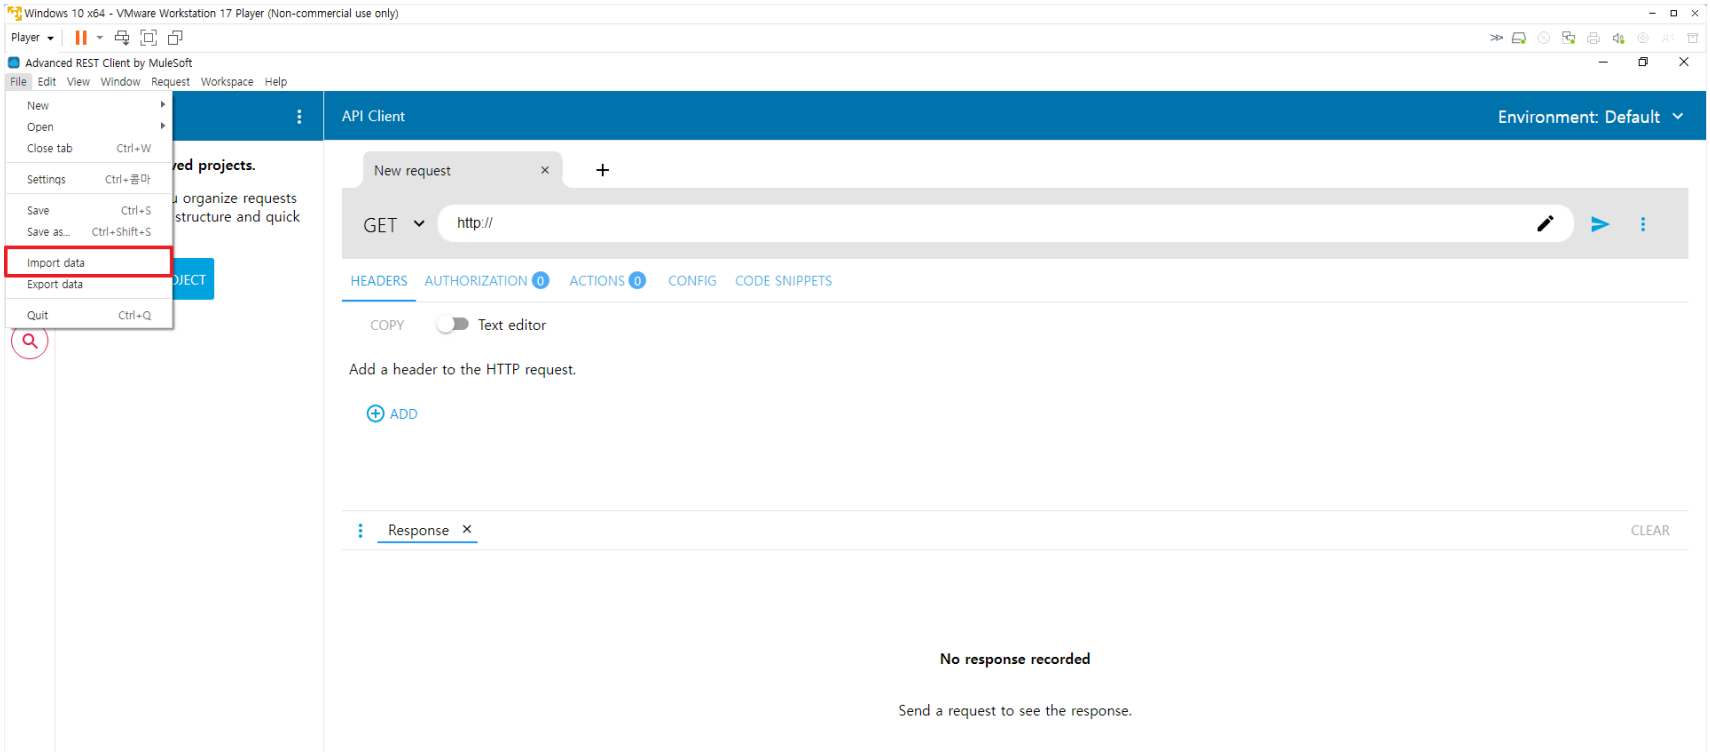 eqstlab/cve-2024-25503
Cross-Site Scripting vulnerability in Advanced REST Client v.17.0.9 exploit
 dead1nfluence/leantime-poc
CVE-2024-27474, CVE-2024-27476, CVE-2024-27477
 shellkraft/cve-2025-3568
A security vulnerability has been identified in Krayin CRM <=2.1.0 that allows a low-privileged user to escalate privileges by tricking an admin into…
 e1tex/cve-2023-48104
Proof-of-concept exploit demonstrating HTML injection in SOGo Web Client before 5.9.1, enabling phishing attacks via malicious forms in email bodies.
 mbadanoiu/cve-2021-46366
CVE-2021-46366: Credential Bruteforce Attack via CSRF + Open Redirect in Magnolia CMS
 mbadanoiu/cve-2020-12625
CVE-2020-12625: Cross-Site Scripting via Malicious HTML Attachment in Roundcube Webmail
 g37sys73m/cve-2022-46087
CloudSchool v3.0.1 is vulnerable to Cross Site Scripting (XSS). A normal user can steal session cookies of the admin users through notification…
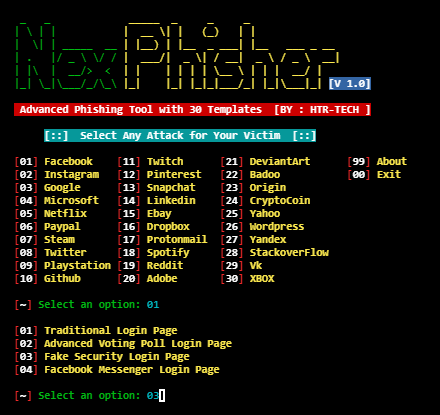 htr-tech/nexphisher
Advanced Phishing tool
 hlldz/pickl3
Windows active user credential phishing tool
 p0cl4bs/wifi-pumpkin-deprecated
DEPRECATED, wifipumpkin3 -> https://github.com/P0cL4bs/wifipumpkin3
 utkusen/jeopardize
a low(zero) cost threat intelligence&response tool against phishing domains