

sublime-rules
 sublime-security/sublime-rules
Sublime rules for email attack detection, prevention, and threat hunting.
defensive-toolsemail-securityphishing+1
376
sublime-security/sublime-rulesSublime rules for email attack detection, prevention, and threat hunting.
 rderaison/bromure
Proper sandboxing for agentic coding and web browsing
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 beefproject/beef
The Browser Exploitation Framework Project
 julioliraup/antiphishing
Advanced Phishing Protection: Suricata rulesets open and free
 boredchilada/clickfix-simulator-2025
A lightweight, self-hosted simulation tool for "ClickFix" (ClearFake) social engineering training. Safely simulates clipboard-injection attacks with…
 grisuno/lazyown
Red team framework and multi-operator C2 platform with AI agents, malleable implants, rootkits, phishing engine, and 741 CLI commands covering the…
 rspamd/rspamd
Spam filtering and email processing framework with regex rules, statistical analysis, custom Lua plugins, and external blocklists for MTA integration.
 criticalpathsecurity/zeek-intelligence-feeds
Aggregated Zeek-format threat intelligence feeds with combined indicators from public and curated sources for continuous IDS and network threat…
 cyb3rmik3/prompt-injection-email-samples
Open .eml test set for evaluating how email security controls and AI mailbox assistants handle indirect prompt injection across disclosure,…
 thalesgroup-cert/watcher
AI-powered threat intelligence platform for automated CVE/ransomware monitoring, domain surveillance, data leak detection, and incident response with…
 qyvora/qyvora-toha3ee
Go-based network exploitation and MITM framework for authorized penetration testing, network reconnaissance, traffic interception, wireless security…
 redbyte1337/credspy
Entra ID user enumeration and auth method discovery via the public GetCredentialType API
 ilianazz/young-domain-guard
Browser extension that warns users about recently registered domains to prevent phishing attacks. Queries RDAP to check domain age and displays…
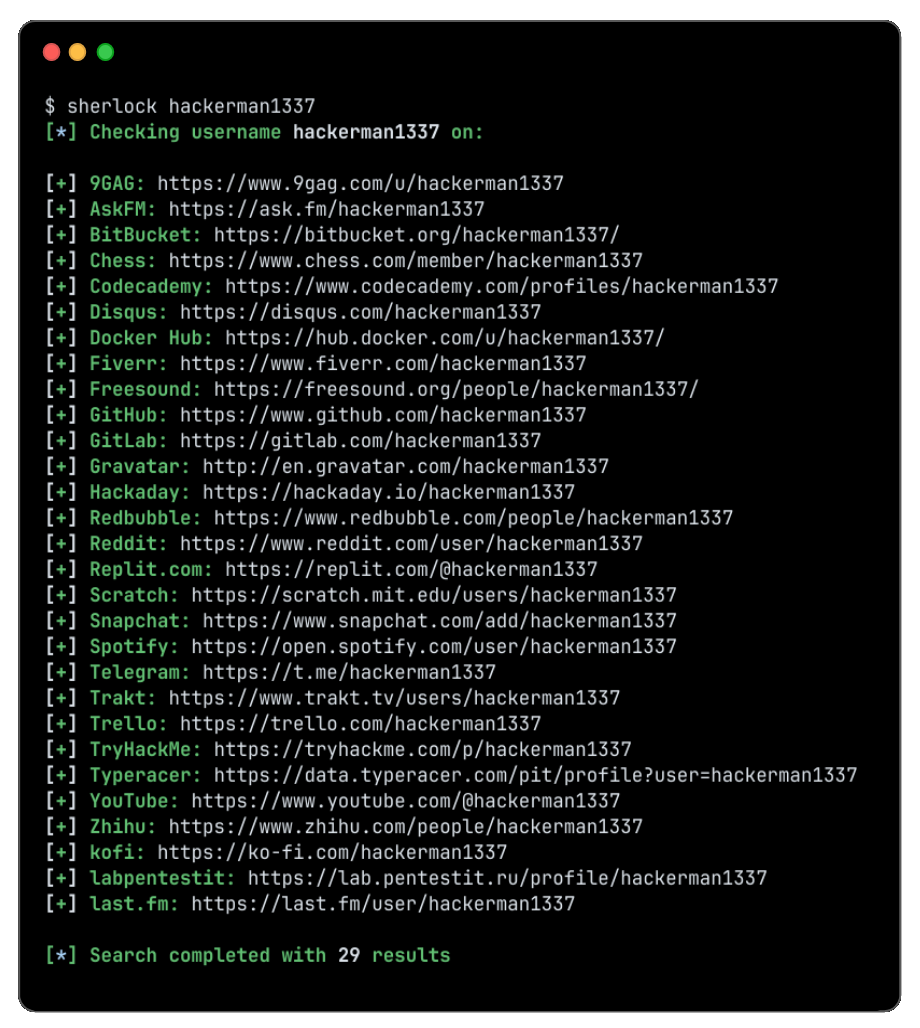 sherlock-project/sherlock
Hunt down social media accounts by username across social networks
 specterops/skills
Reusable offensive security skills and plugins for AI agents, covering reconnaissance, exploitation, C2, payload development, and reporting across…
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 hac01/azure-pentesting-suite
Go toolkit for authorized Azure security assessments: enumerates subscriptions and resources, audits misconfigurations, and attacks public Blob…