

sublime-rules
 sublime-security/sublime-rules
Sublime rules for email attack detection, prevention, and threat hunting.
defensive-toolsemail-securityphishing+1
373
sublime-security/sublime-rulesSublime rules for email attack detection, prevention, and threat hunting.
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 rspamd/rspamd
Spam filtering and email processing framework with regex rules, statistical analysis, custom Lua plugins, and external blocklists for MTA integration.
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 fluxionnetwork/fluxion
Automated WPA/WPA2 phishing tool that captures handshakes, spawns a rogue access point, and lures users to a captive portal to harvest credentials…
 qyvora/qyvora-toha3ee
Go-based network exploitation and MITM framework for authorized penetration testing, network reconnaissance, traffic interception, wireless security…
 romain-deperne/cve-2026-33715
Unauthenticated SSRF and open email relay in Chamilo LMS — CVE-2026-33715 / CVSS 7.2
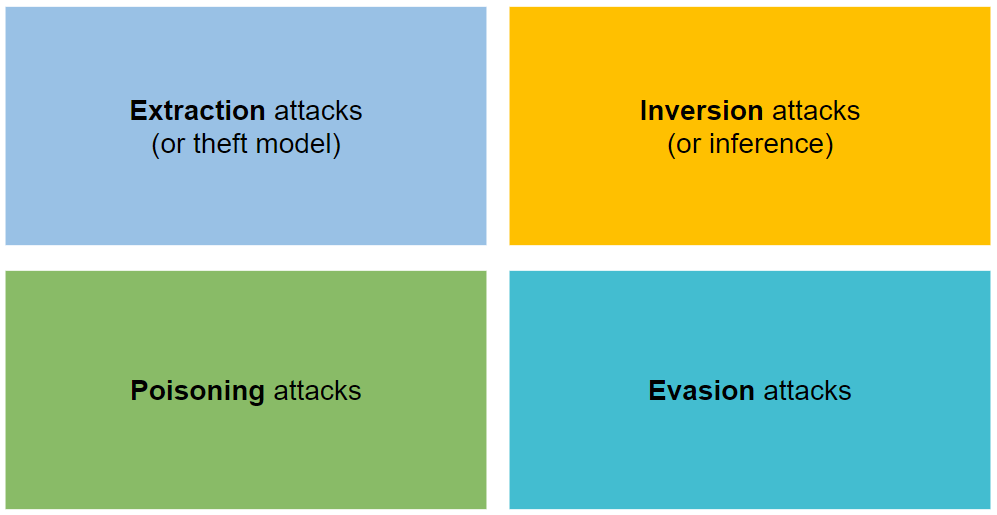 jiep/offensive-ai-compilation
A curated list of useful resources that cover Offensive AI.
 praneethnaidu1910-cmd/cve-2023-23397-purple-team
Purple team project exploiting CVE-2023-23397 Outlook NTLM leak with phishing delivery, plus Sigma/Wazuh detections mapped to MITRE ATT&CK for the…
 yoguicr/cve-2024-21413-outlook-assessment
Detailed vulnerability assessment and exploitation report for CVE-2024-21413 (Moniker Link) in Microsoft Outlook, including attack path, NetNTLMv2…
 secdev02/easytokens
Kali365 - EvilTokens Replica
 kgretzky/evilginx2
Standalone man-in-the-middle attack framework used for phishing login credentials along with session cookies, allowing for the bypass of 2-factor…
 nickvourd/rti-toolkit
PowerShell toolkit for remote template injection attacks and defense. Injects malicious links into Office Word documents for phishing, with…
 wifiphisher/wifiphisher
Rogue Access Point framework for red team engagements and Wi-Fi security testing. Performs Evil Twin, KARMA, and Known Beacons attacks to achieve…
 undeadsec/evilurl
Generate unicode domains for IDN Homograph Attack and detect them.
 pushsecurity/browser-identity-attacks-matrix
Offensive security drives defensive security. We're sharing a collection of SaaS attack techniques to help defenders understand the threats they…
 dionissh/cve-2024-21413
Proof-of-concept exploit for Microsoft Outlook RCE (CVE-2024-21413) with SMTP-based phishing email delivery, malicious RTF attachment generation, and…
 viniciusfariasdev/cve-2024-21413-outlook-monikerlink-lab
Educational lab and PoC demonstrating CVE-2024-21413 Outlook Moniker Link attack to leak netNTLMv2 hashes via crafted HTML email.